Judge-Jury-and-Executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

A tool to listen on a KNX bus via TPUART and the Calimero Project suite and to dump the data from the packets into a Wireshark-Compatible file hex…

WhatsApp Forensic Tool

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.

X-Ways Acropalypse extension detects CVE-2023-21036 in common images

Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal


IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

privacy-first, open-source and free idevice management tool written in Rust and Qt

OS X Auditor is a free Mac OS X computer forensics tool

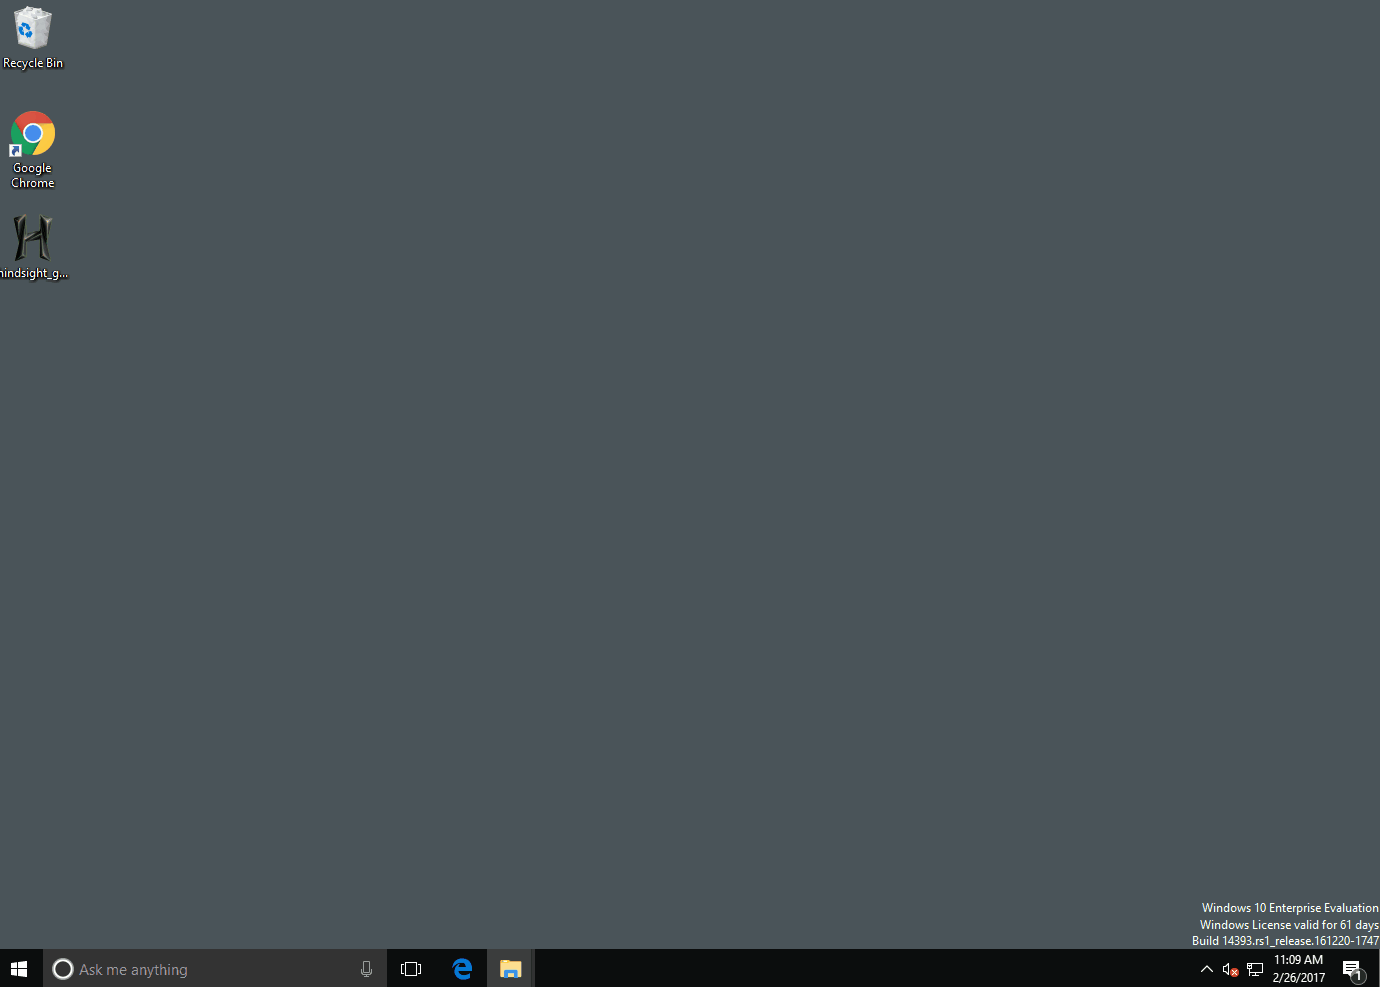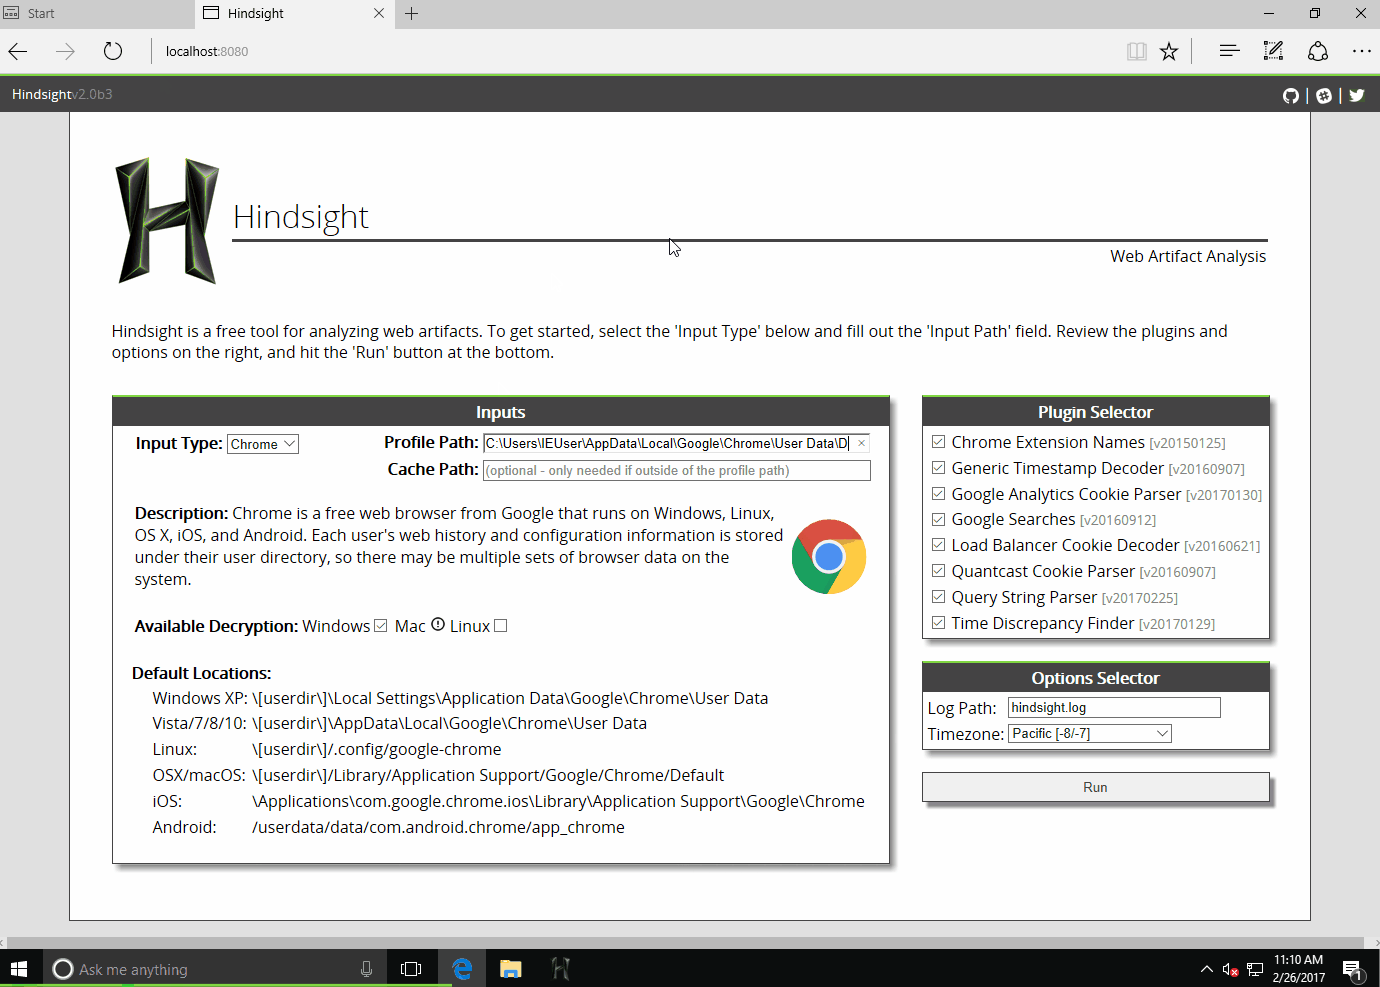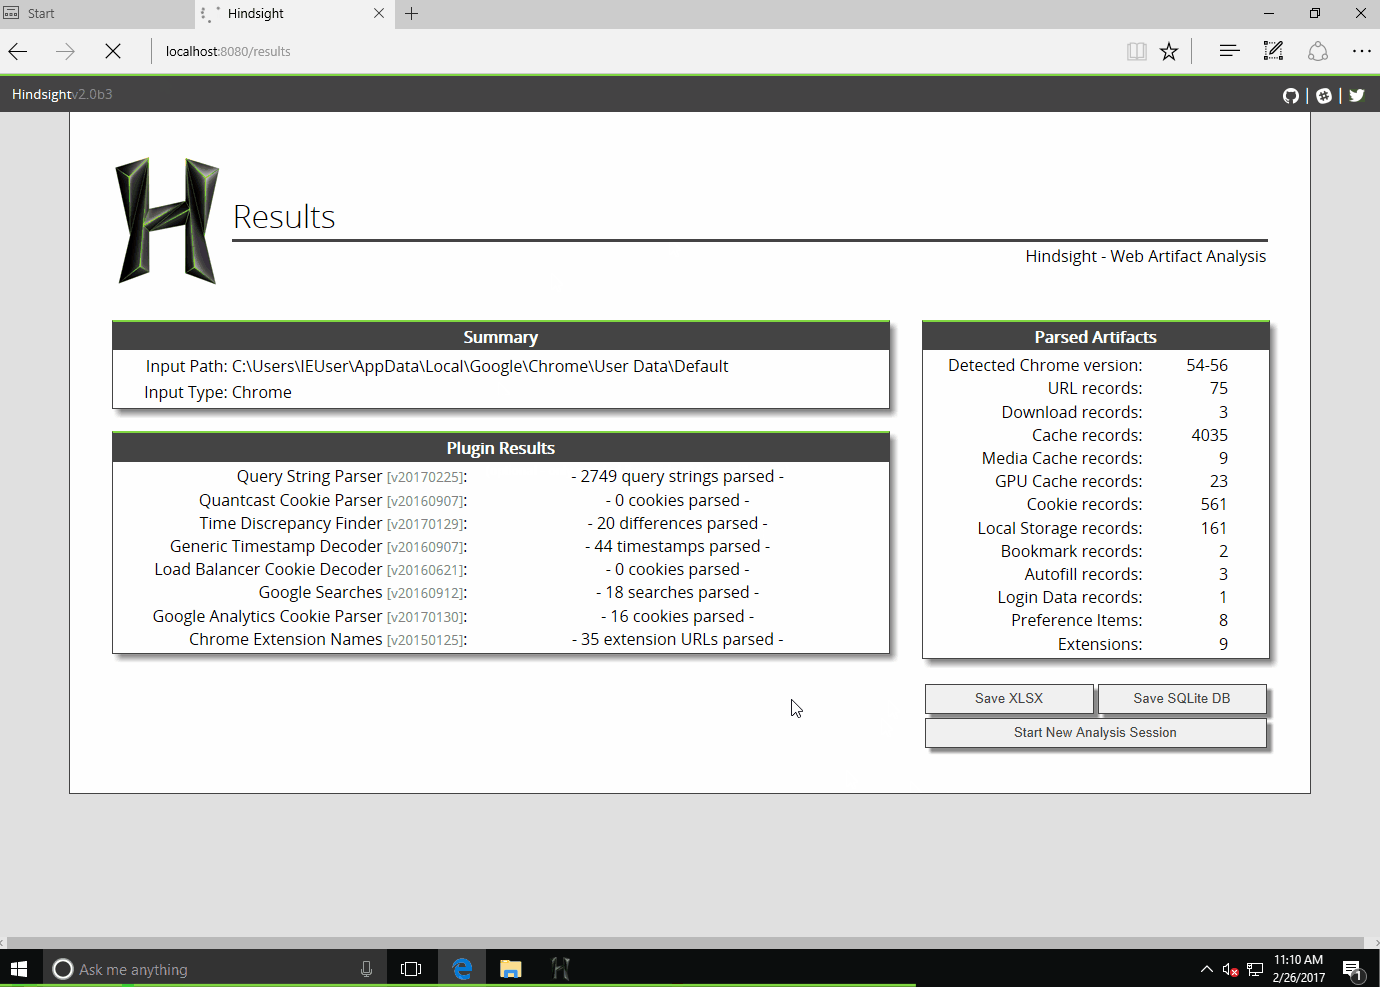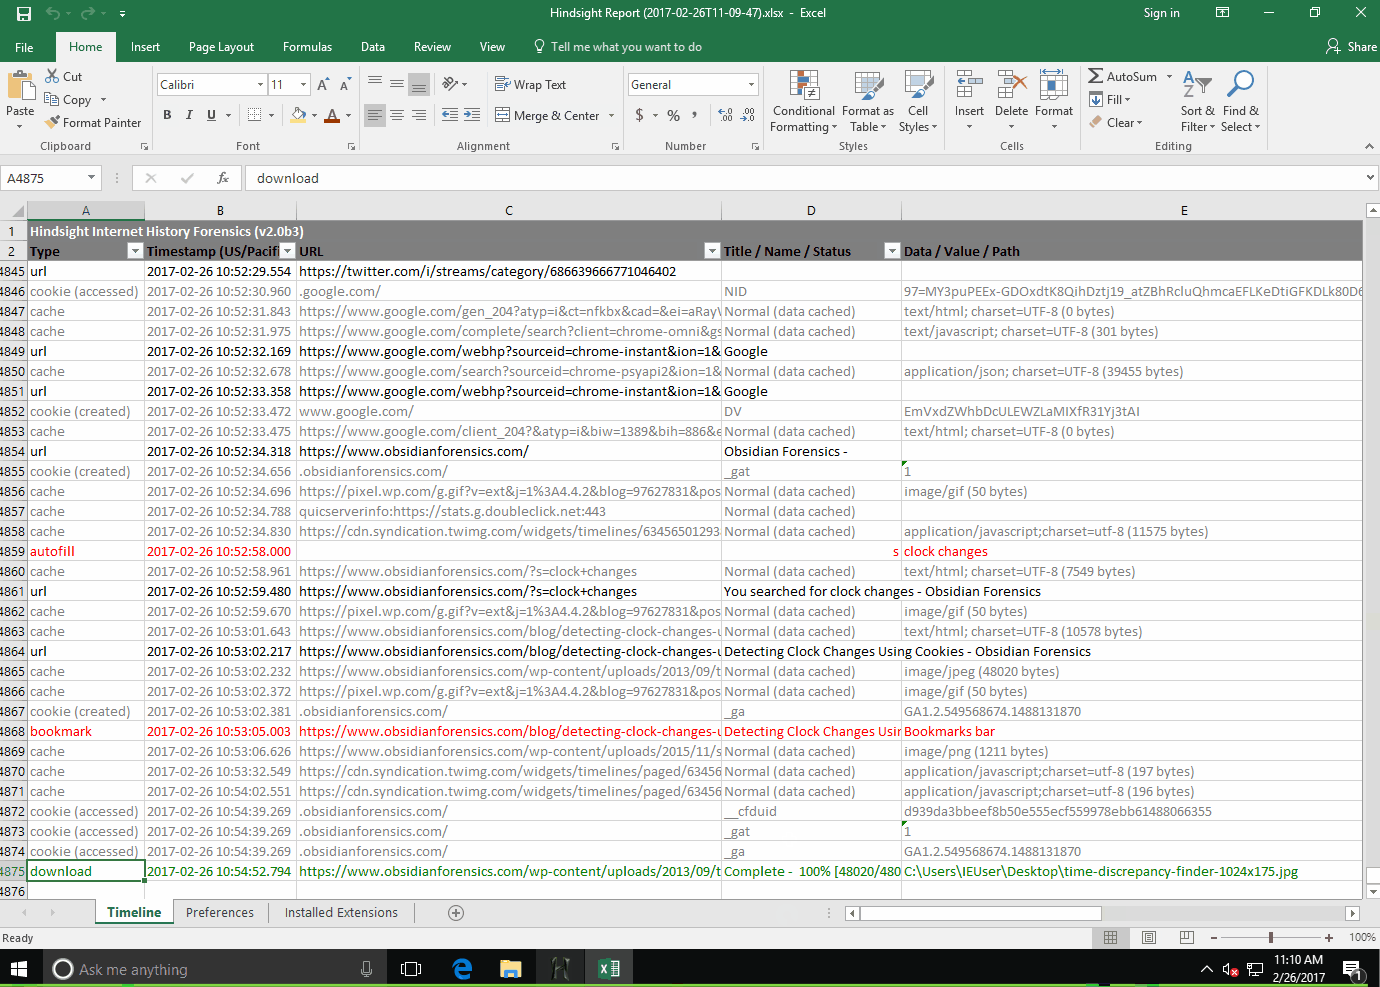
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox

Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…

OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

Loot and decrypt Windows DPAPI secrets remotely or offline, including masterkeys, credentials, vaults, certificates, browser data, and cached Azure…

A tool for forensic file system reconstruction.

Forensics tool for NTFS (parser, mft, bitlocker, deleted files)

Tool and framework for securely reading untrusted USB mass storage devices.