
oletools
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
code-analysisdigital-forensicsforensics+3
3.4k
decalage2/oletoolsPython toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 volatilityfoundation/community
Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
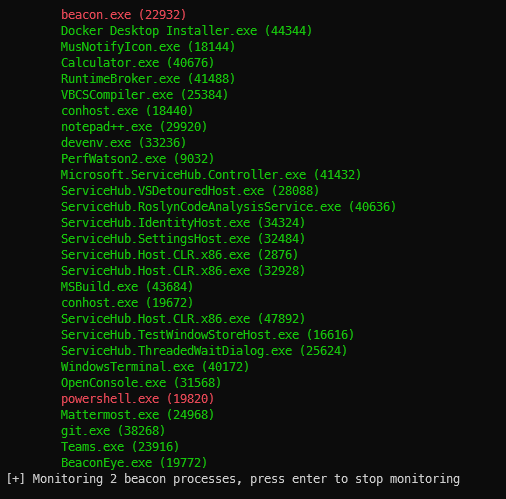 ccob/beaconeye
Hunts out CobaltStrike beacons and logs operator command output
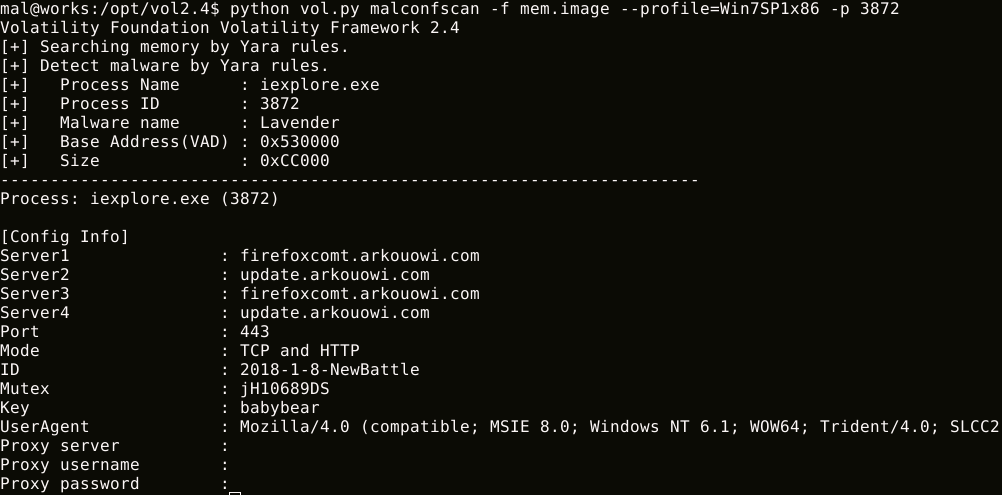 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
 pandare9x/configuration_extractors
Configuration Extractors for Malware
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
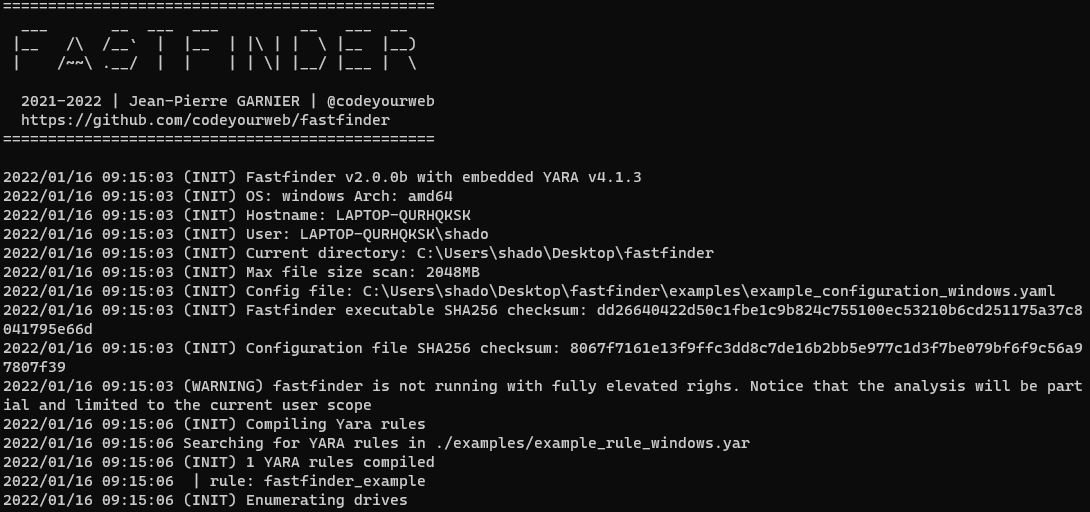 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder
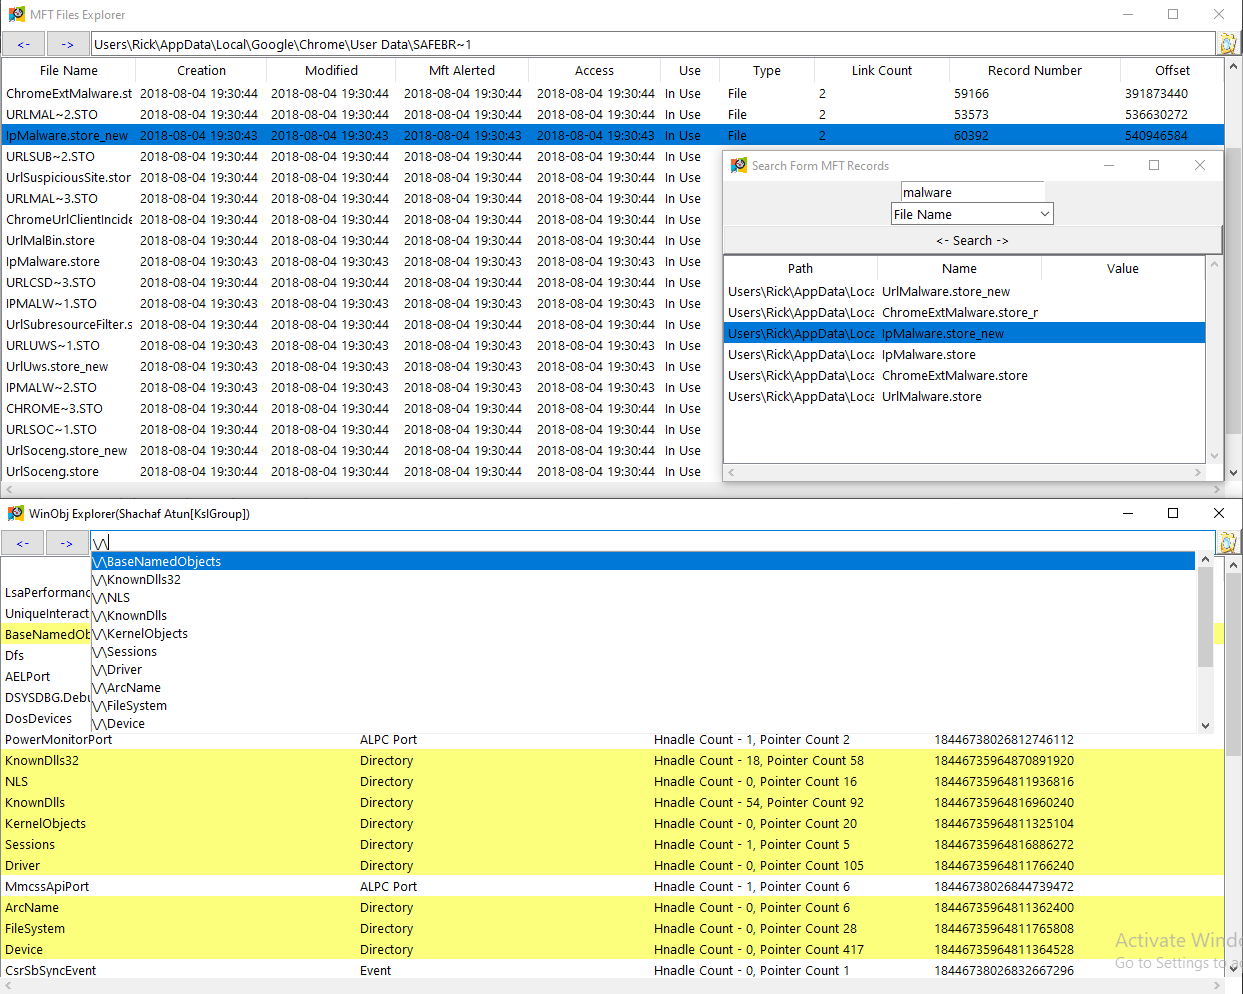 memoryforensics1/volexp
volatility explorer (volatility 2)
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 forensicxlab/vision-procmon
A ProcessMonitor visualization application written in rust.
 opensourcesec/cirtkit
Tools for the Computer Incident Response Team :computer:
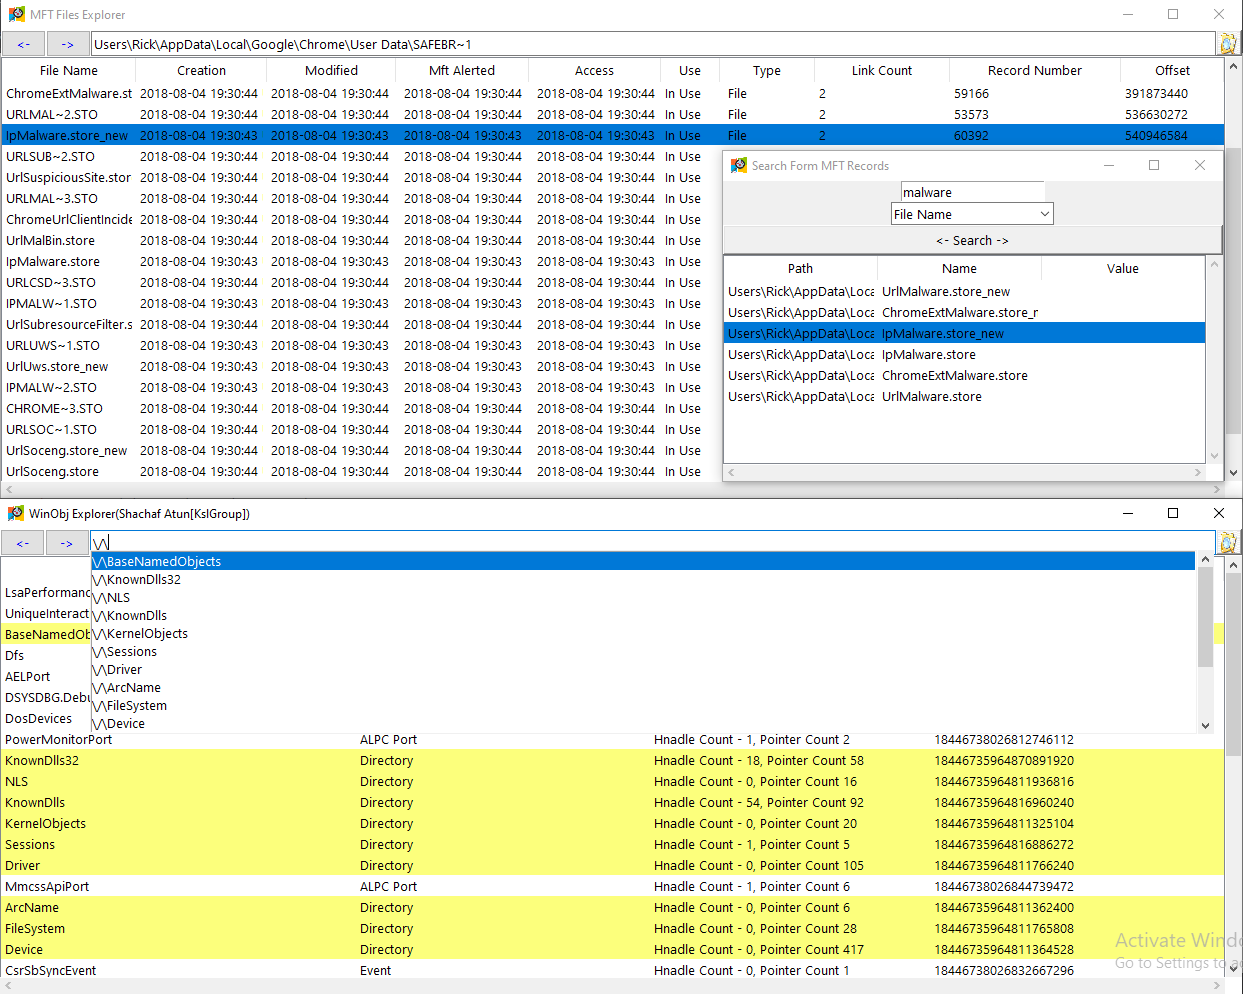 memoryforensics1/vol3xp
Volatility Explorer Suit (volatility 3)
 mayhamad/memtracer
Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
 crowdstrike/xwf-yara-scanner
Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…