

mongobleed-detector
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
database-securitydigital-forensicsforensics+5
81
neo23x0/mongobleed-detectorDetection Script for MongoBleed Exploitation
 m0n1x90/exif-gps-tracer
A python script which allows you to parse GeoLocation data from your Image files stored in a dataset.It also produces output in CSV file and also in…
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 0xcomposure/fftstegpic
A python script for digital image steganography using Fast Fourier Transform.
 hexastrike/ivanti-connect-secure-logs-parser
A Python script for examining Ivanti Secure Connect (ICS) event logs, designed to support investigations into vulnerabilities CVE-2025-0282,…
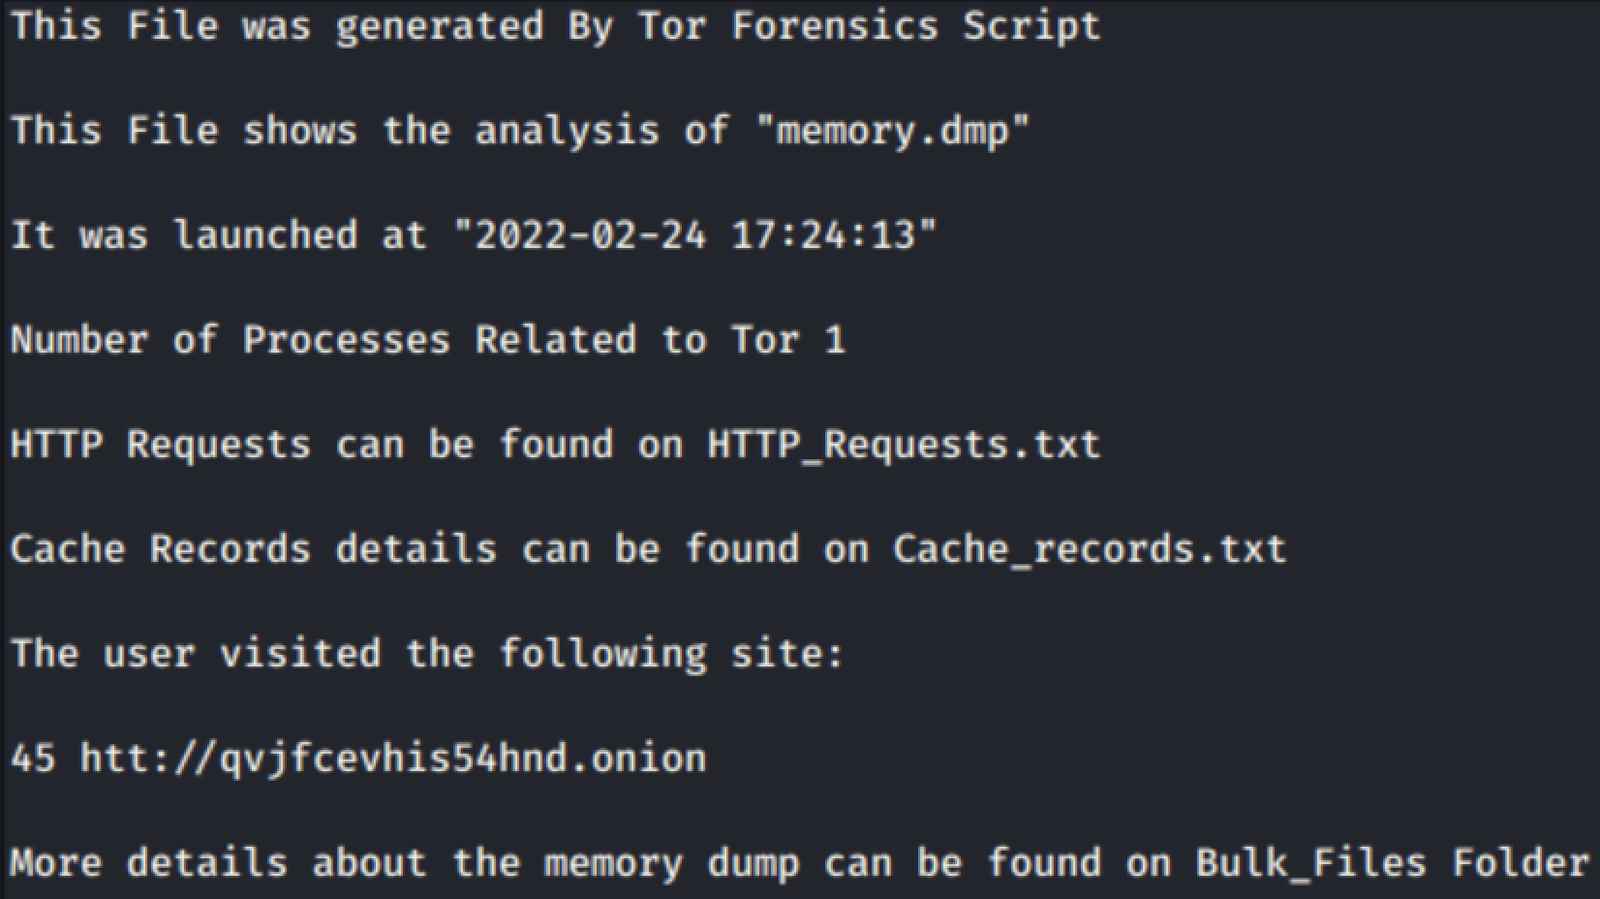 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781
 danielwep/cve-netscalerfilesystemcheck
This script checks the Citrix Netscaler if it has been compromised by CVE-2019-19781 attacks and collects all file system information
 w116tjb/plex2shell-windows-hunt
Plex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 busindre/mozcache
Simple shell script to perform forensic analysis of the Mozilla-Browsers cache (Firefox, Iceweasel and Seamonkey).
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 terminaljunki3/cve-2024-3400-checker
Check to see if your Palo Alto firewall has been compromised by running script againt support bundle.