
LockBit-Ransomware-Analysis
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
data-exfiltrationdigital-forensicseducation+8
vignesh-hp/lockbit-ransomware-analysisThreat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
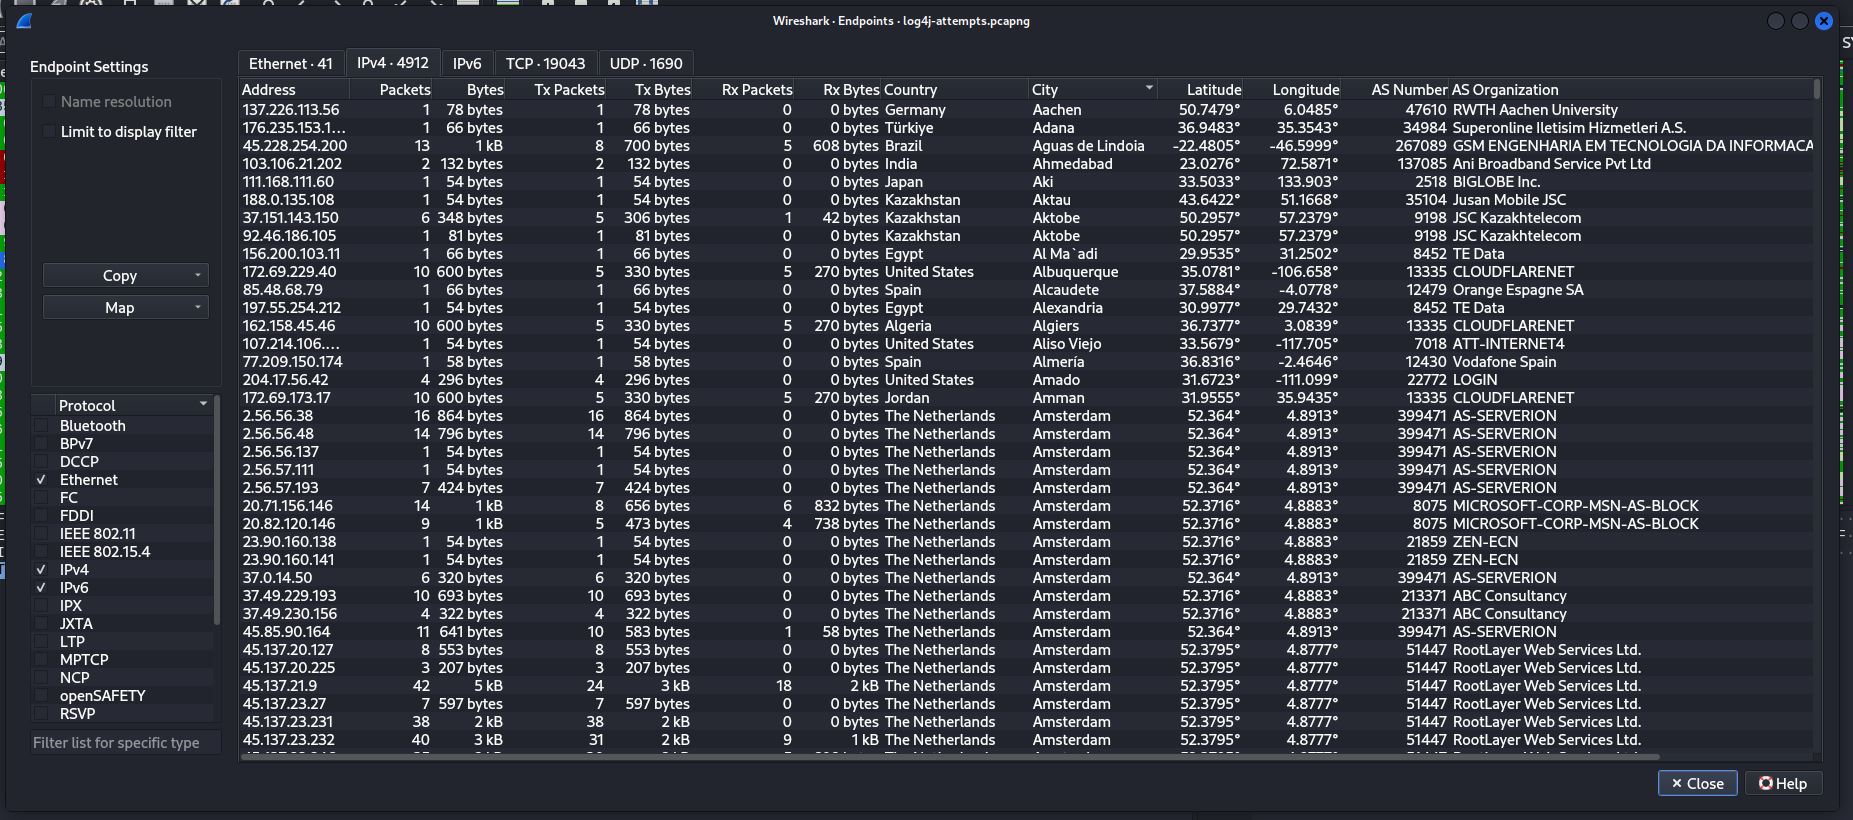 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 strangerealintel/cyberthreatintel
Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 mkorman90/regipy
Regipy is an os independent python library for parsing offline registry hives
 bontchev/whodunit
Recognizing the most likely APT groups responsible for an incident
 themittenmac/truetree
A command line tool for pstree-like output on macOS with additional pid capturing capabilities
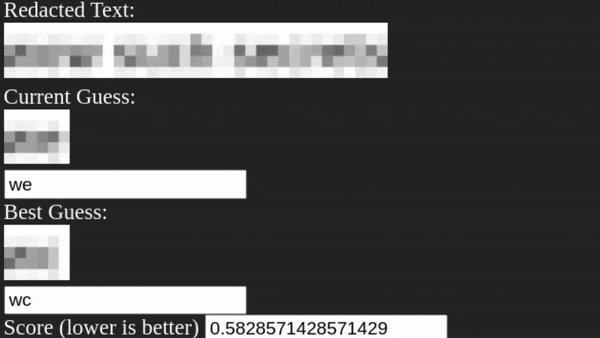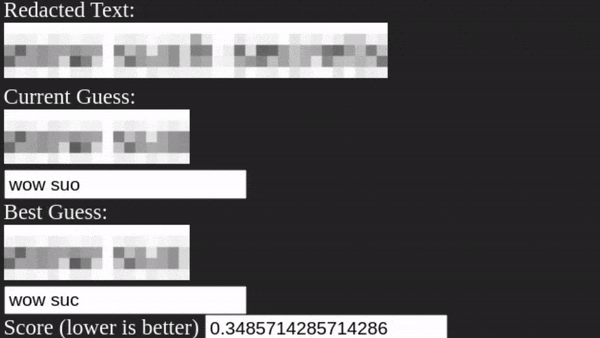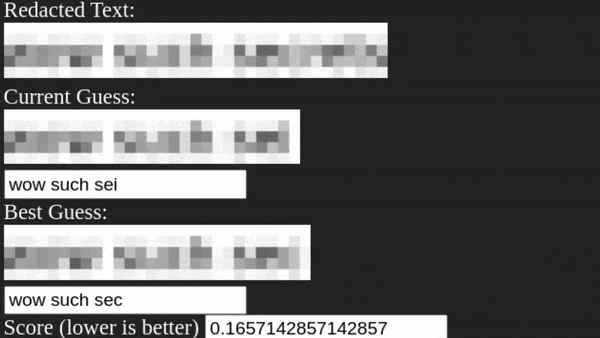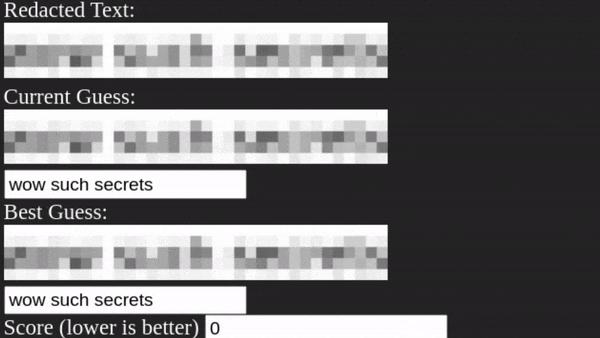 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 cyprianatsyor/cve-2024-24919-incident-report.md
Detailed incident report analyzing CVE-2024-24919 arbitrary file read exploit on Check Point Security Gateway, including technical analysis, response…
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)