Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
338 results
Chrome-Forensic_CVE-2024-0044 preview

Chrome-Forensic_CVE-2024-0044

GitHubjacktekno/chrome-forensic_cve-2024-0044

A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
android-securitydata-recoverydigital-forensics+6
8 months ago
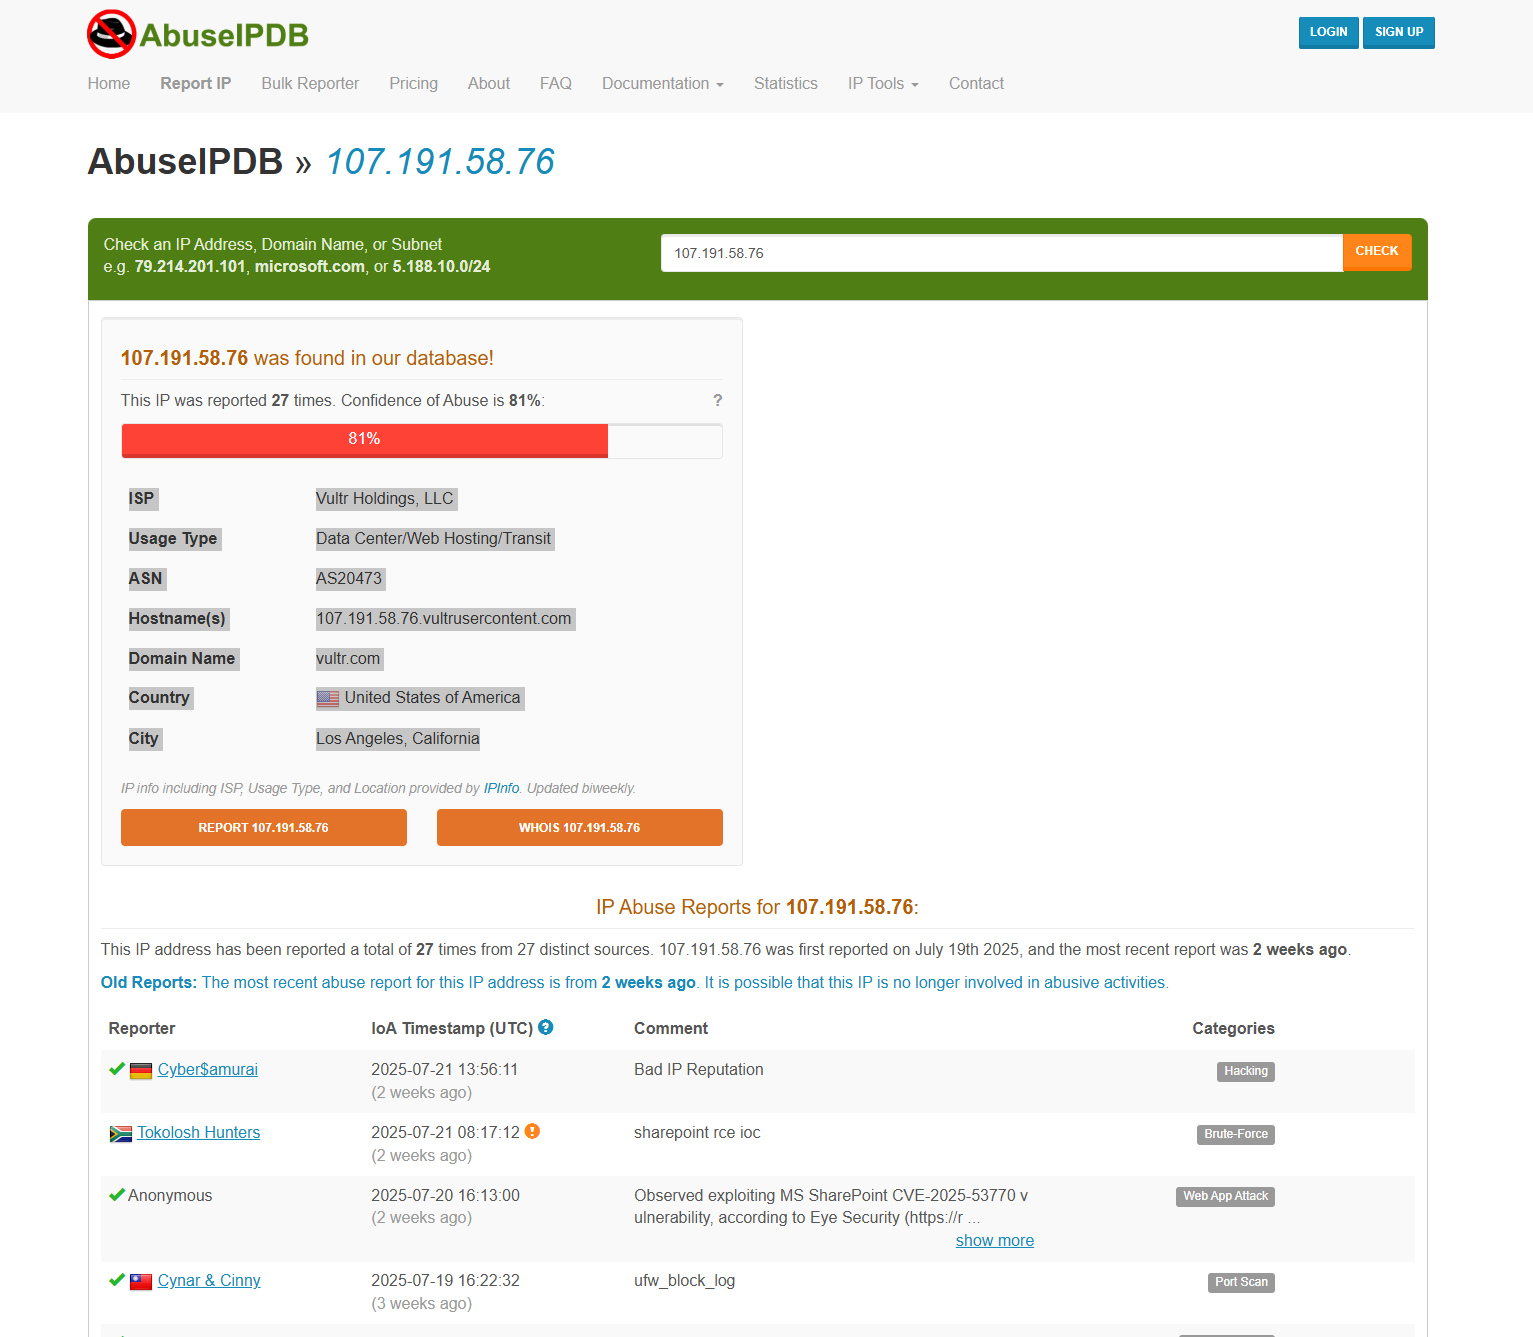
ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend preview

ToolShell-CVE-2025-53770-SharePoint-Exploit-Lab-LetsDefend

GitHubcyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend

Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
command-and-controlctfdigital-forensics+9
1 year ago
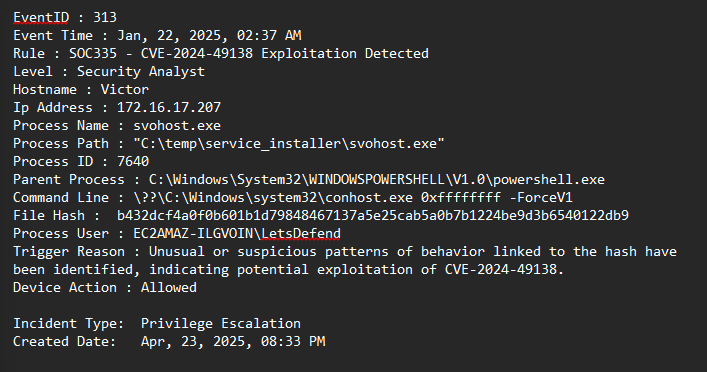
letsdefend-cve-2024-49138-investigation preview

letsdefend-cve-2024-49138-investigation

GitHubcyprianatsyor/letsdefend-cve-2024-49138-investigation

Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.

binary-exploitationdigital-forensicseducation+7
1 year ago
how_to_become_a_malware_analyst preview

how_to_become_a_malware_analyst

GitHubpinksawtooth/how_to_become_a_malware_analyst

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…

binary-analysisctfcurated-resources+7
2797 days ago
keyfinder preview
Archived

keyfinder

GitHubcertcc/keyfinder

A tool for finding and analyzing private (and public) key files, including support for Android APK files.
android-securitycryptographydigital-forensics+4
2783 years ago
sleuthkit preview

sleuthkit

GitHubsleuthkit/sleuthkit

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

data-recoverydigital-forensicsdisk-forensics+3
3.1k1 day ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8113 months ago
community preview

community

GitHubvolatilityfoundation/community

Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…

digital-forensicsmalware-analysismemory-forensics
3775 years ago
keepass-password-dumper preview

keepass-password-dumper

GitHubvdohney/keepass-password-dumper

Original PoC for CVE-2023-32784
digital-forensicsexploitationforensics+3
6523 years ago
CryKeX preview

CryKeX

GitHubcryptolok/crykex

Linux Memory Cryptographic Keys Extractor
cryptographydigital-forensicsencryption-decryption-tools+2
2423 years ago
pockint preview

pockint

GitHubedoardogerosa/pockint

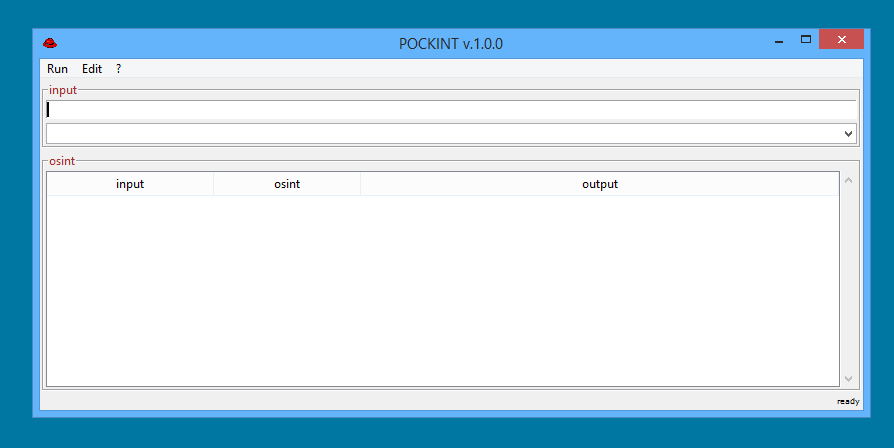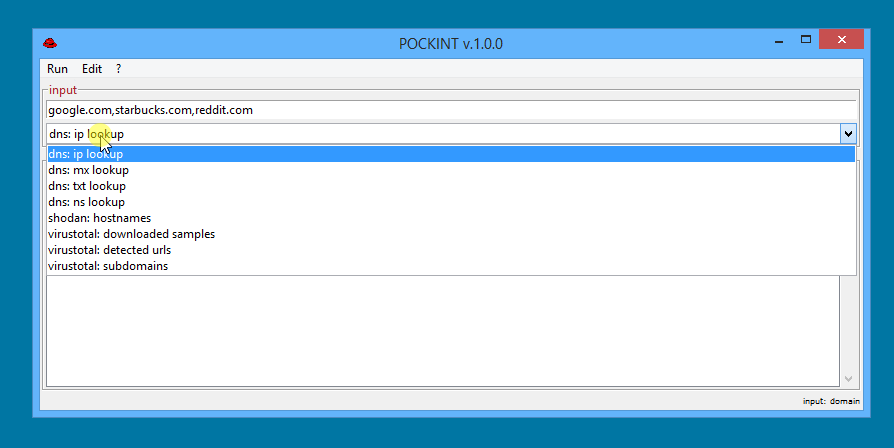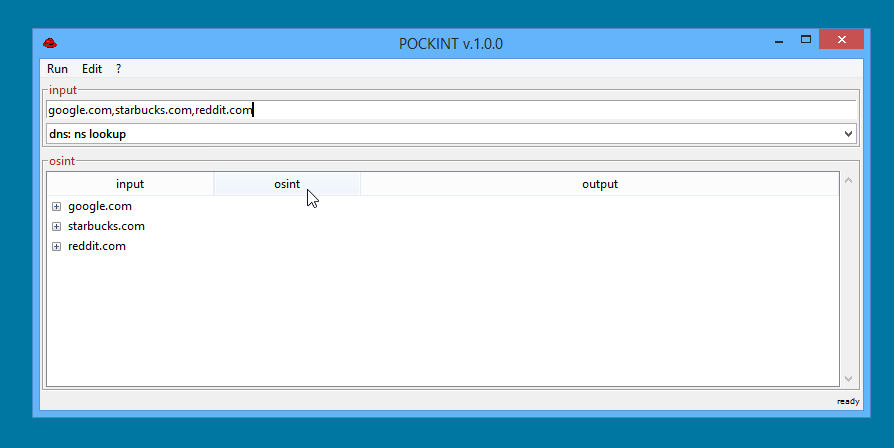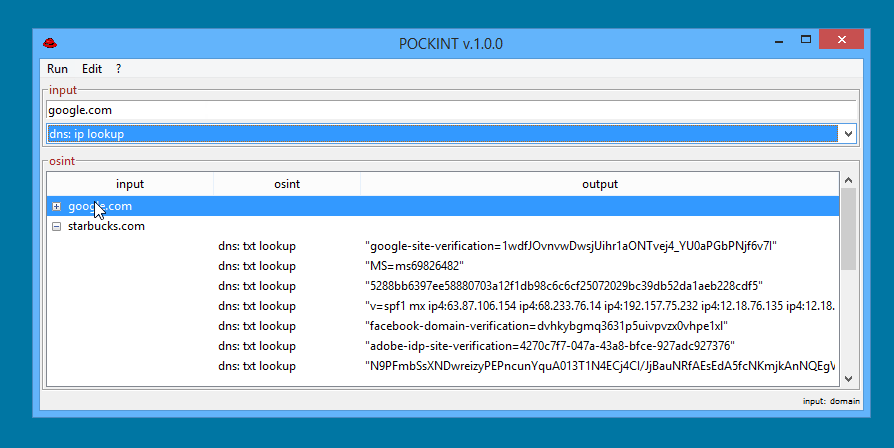
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️
digital-forensicsdns-analysisincident-response+5
2853 years ago
Labtainers preview

Labtainers

GitHubmfthomps/labtainers

Labtainers: A Docker-based cyber lab framework
binary-exploitationcryptographyctf+9
3154 days ago
distro preview

distro

GitHubremnux/distro

Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
digital-forensicsdynamic-analysis-sandboxingforensics+5
11728 days ago
python-haystack preview

python-haystack

GitHubtrolldbois/python-haystack

Process heap analysis framework - Windows/Linux - record type inference and forensics
binary-analysisdigital-forensicsforensics+2
959 years ago
SessionView preview

SessionView

GitHublsecqt/sessionview

A portable C# utility for enumerating local and remote windows sessions

digital-forensicsforensicsincident-response+3
578 months ago
SharkMCP preview

SharkMCP

GitHubweirdmachine64/sharkmcp

A swiss-knife MCP server for analysing PCAP files
ctfdigital-forensicseducation+6
754 months ago
adwind-decryptor preview

adwind-decryptor

GitHubmhelwig/adwind-decryptor

Simple decrypter for Java AdWind, jRAT, jBifrost trojan
binary-analysisdigital-forensicsencryption-decryption-tools+3
179 years ago
sorry-ransomware-analysis preview

sorry-ransomware-analysis

GitHubhabibkaratas/sorry-ransomware-analysis

Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign

cryptographydigital-forensicsforensics+4
54 months ago
Previous1…141516…19Next