
Umbrella_android
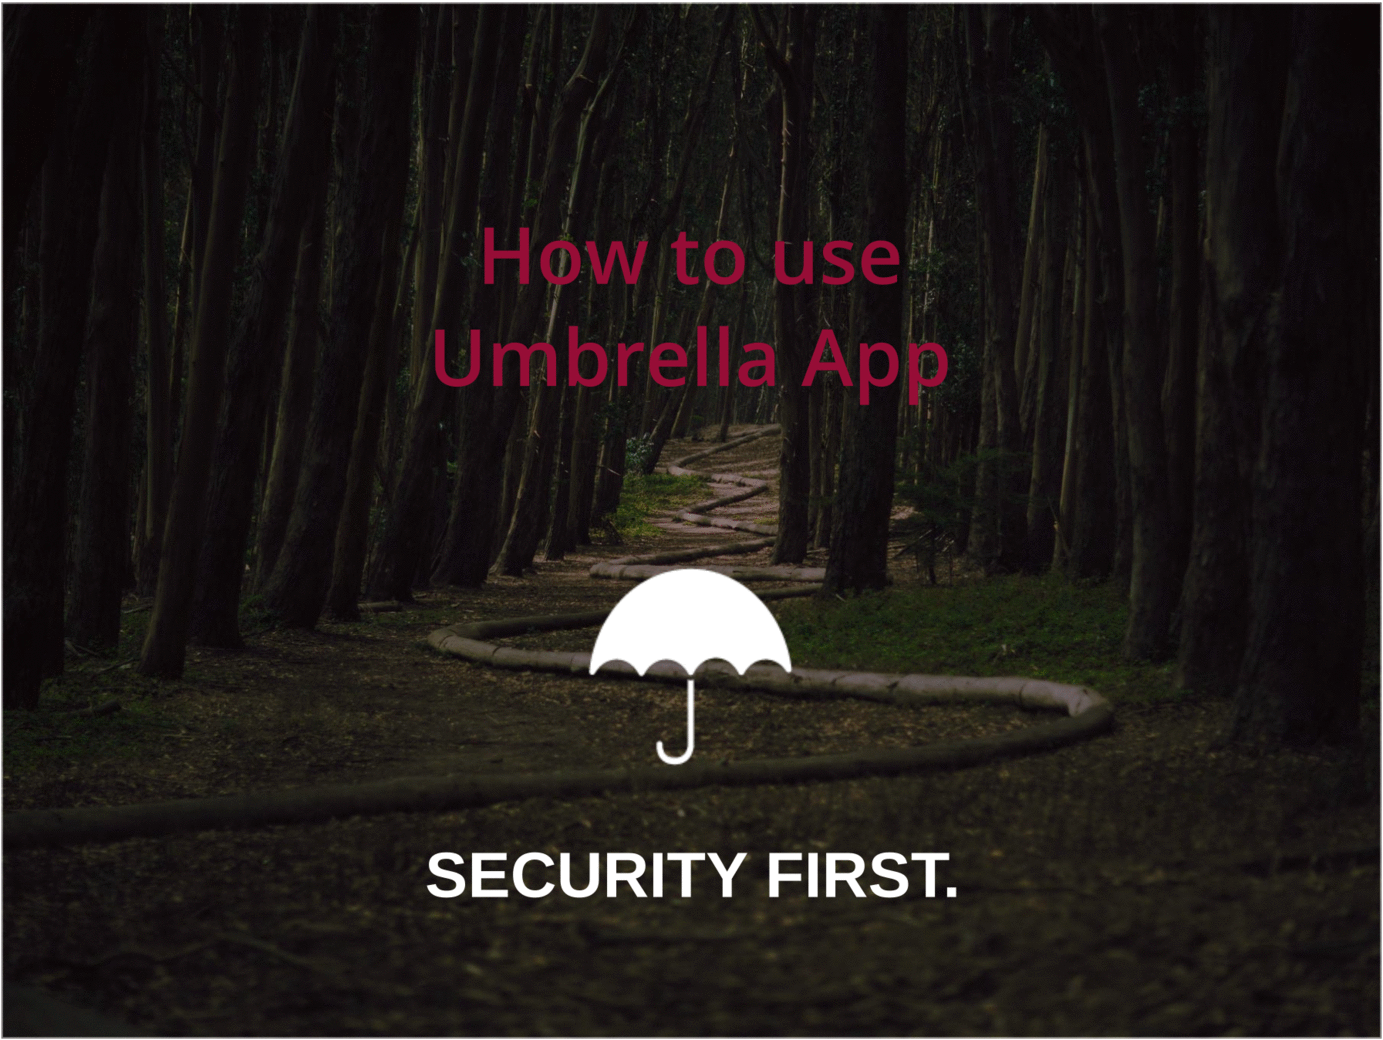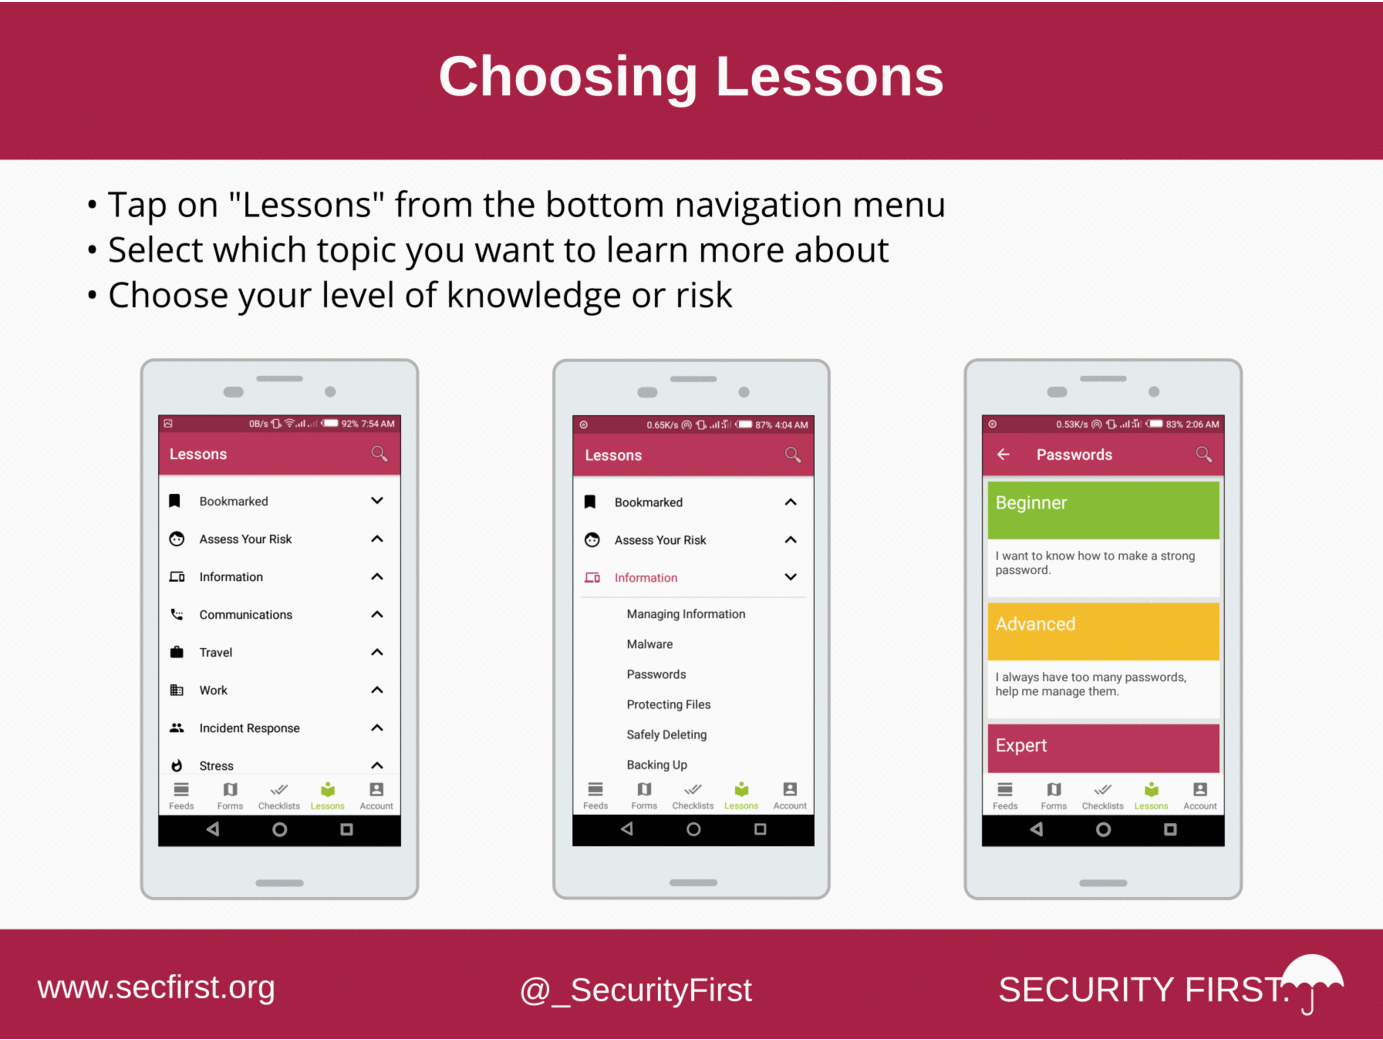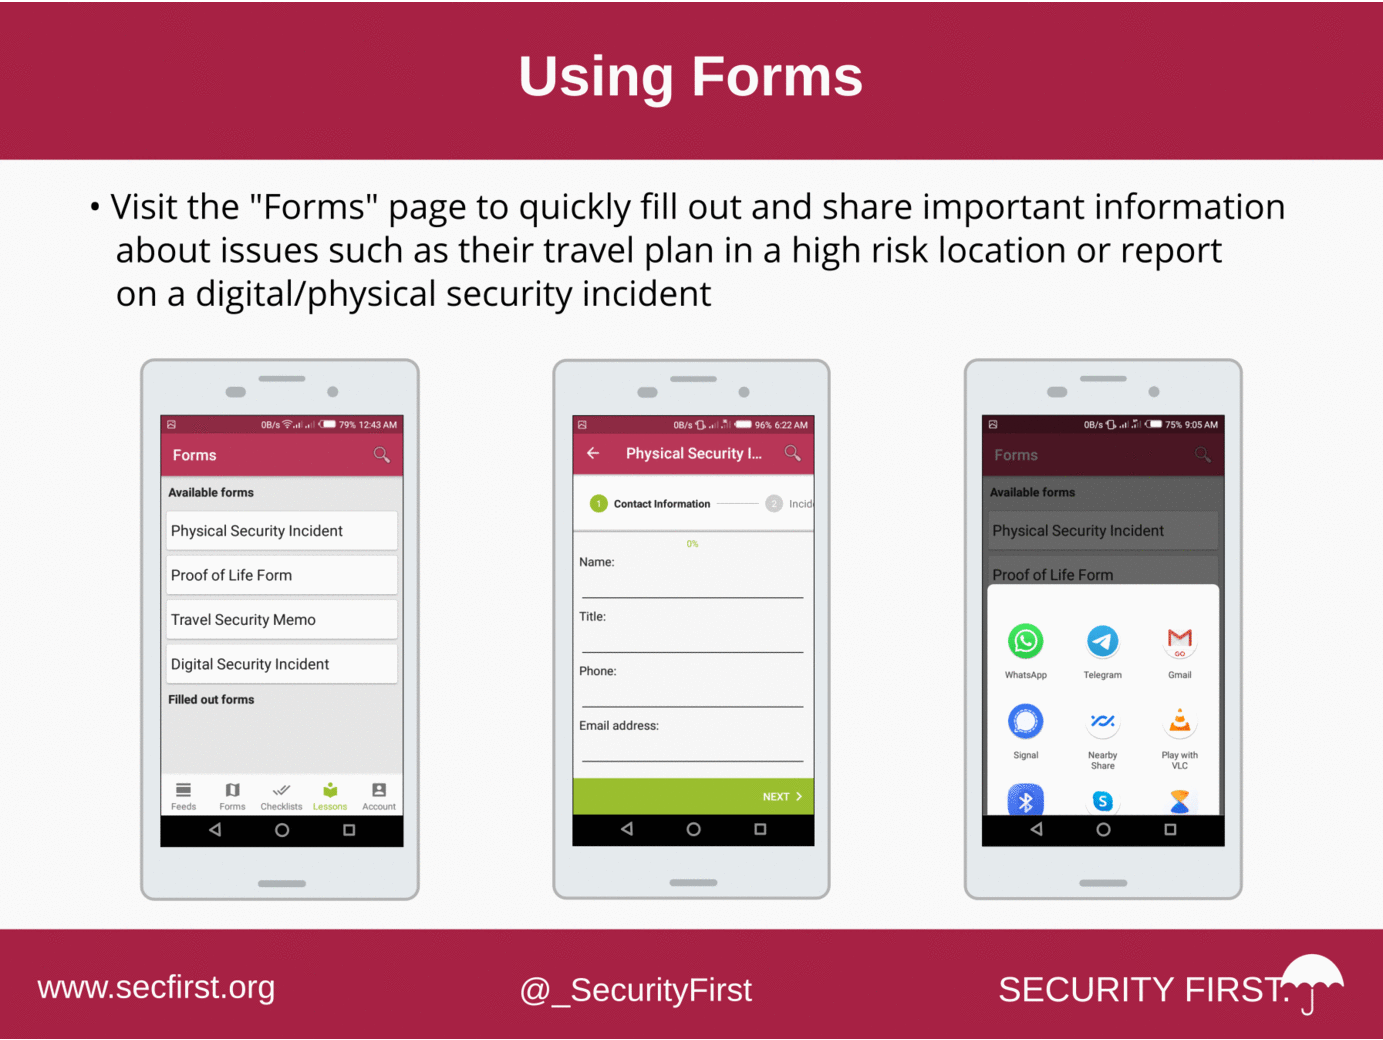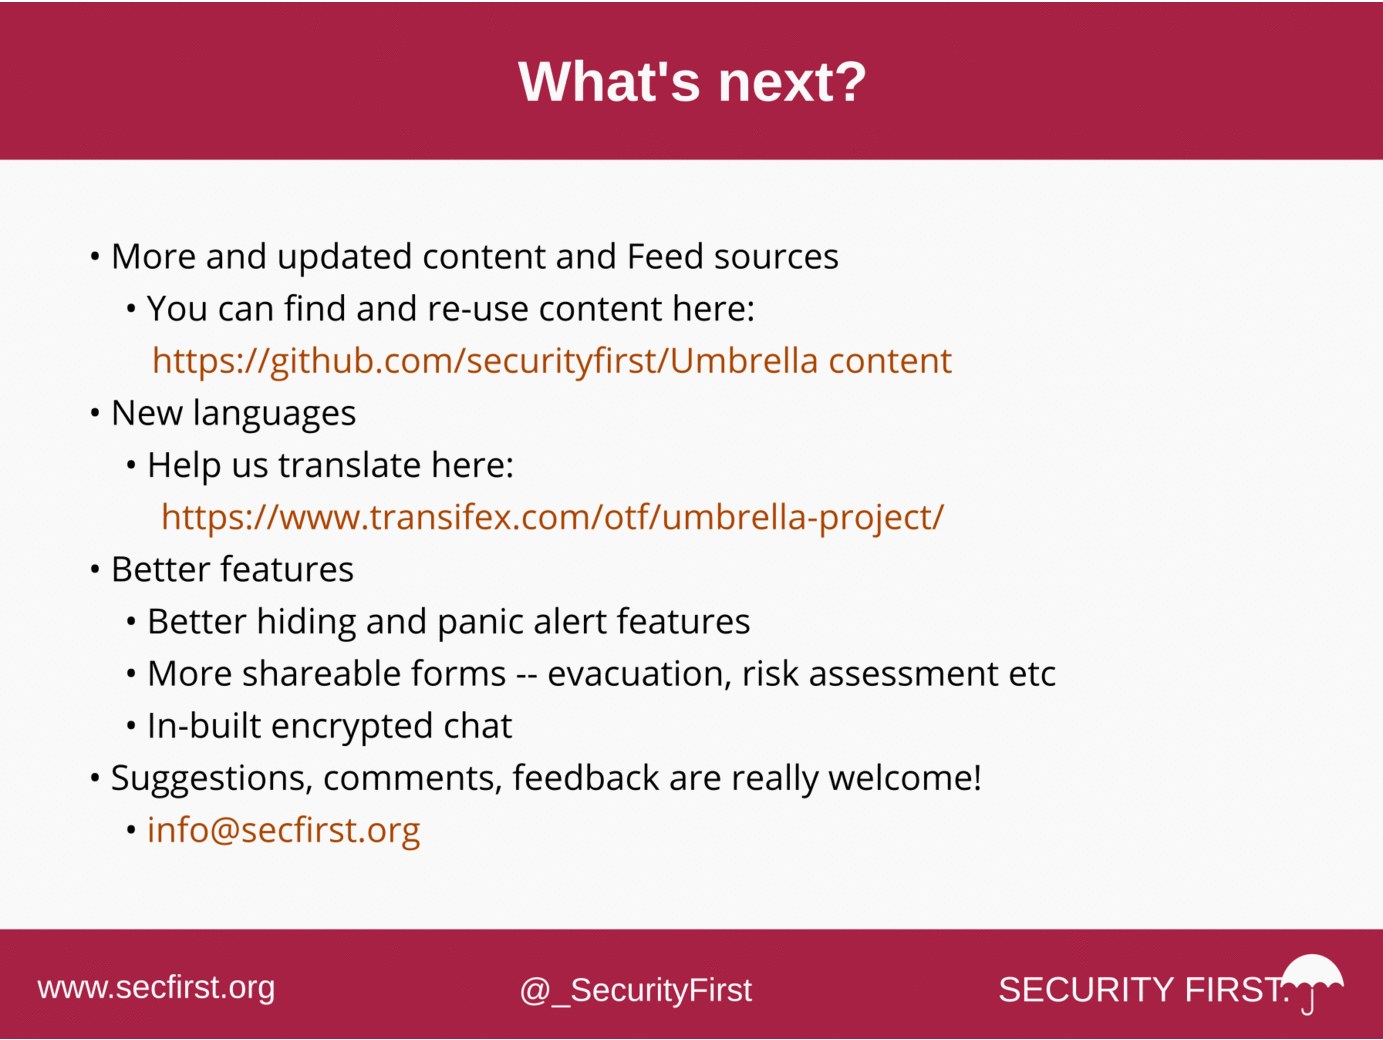
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…

Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.

❤️ Free batch image & video geolocation digital forensics tool. Automatically extract EXIF data, visualize GPS coordinates on maps, and reconstruct…

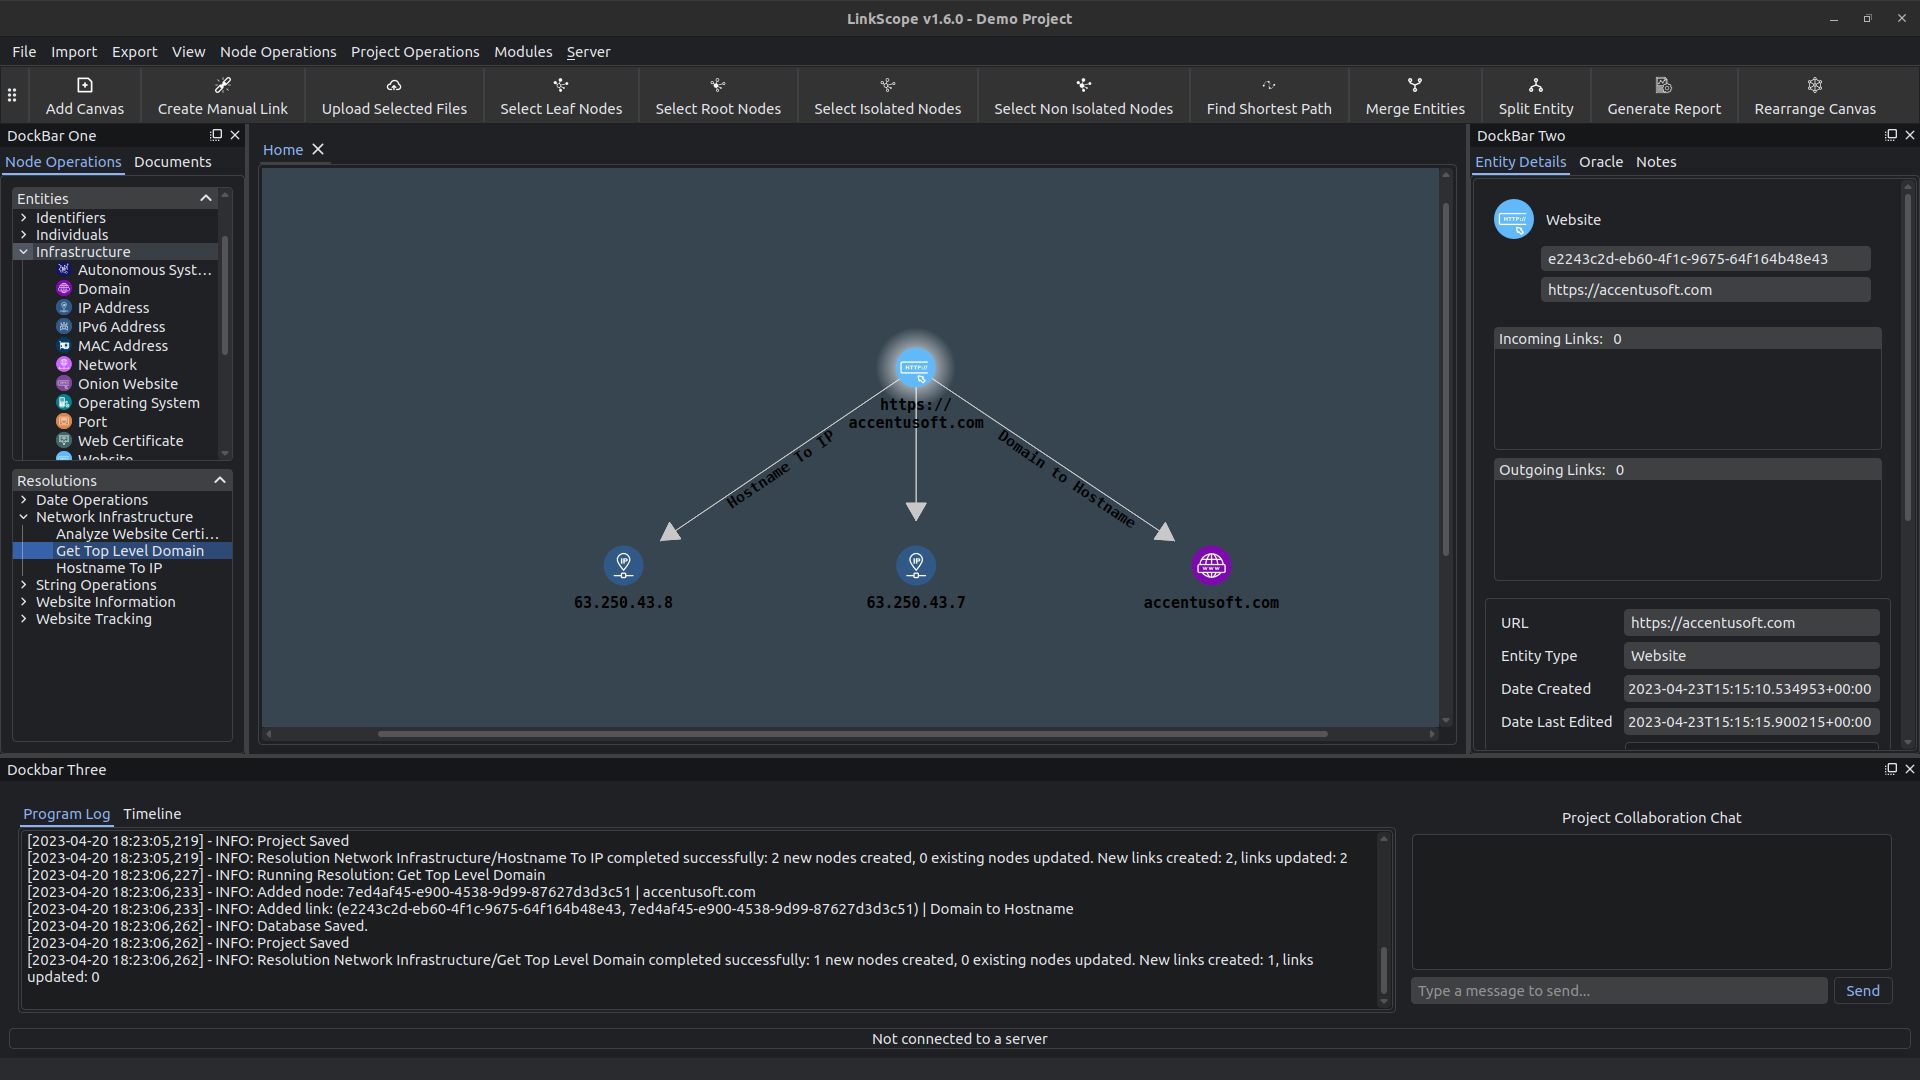
Repository for the LinkScope Client software.

Bash script to extract data from a "chekcra1ned" iOS device

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

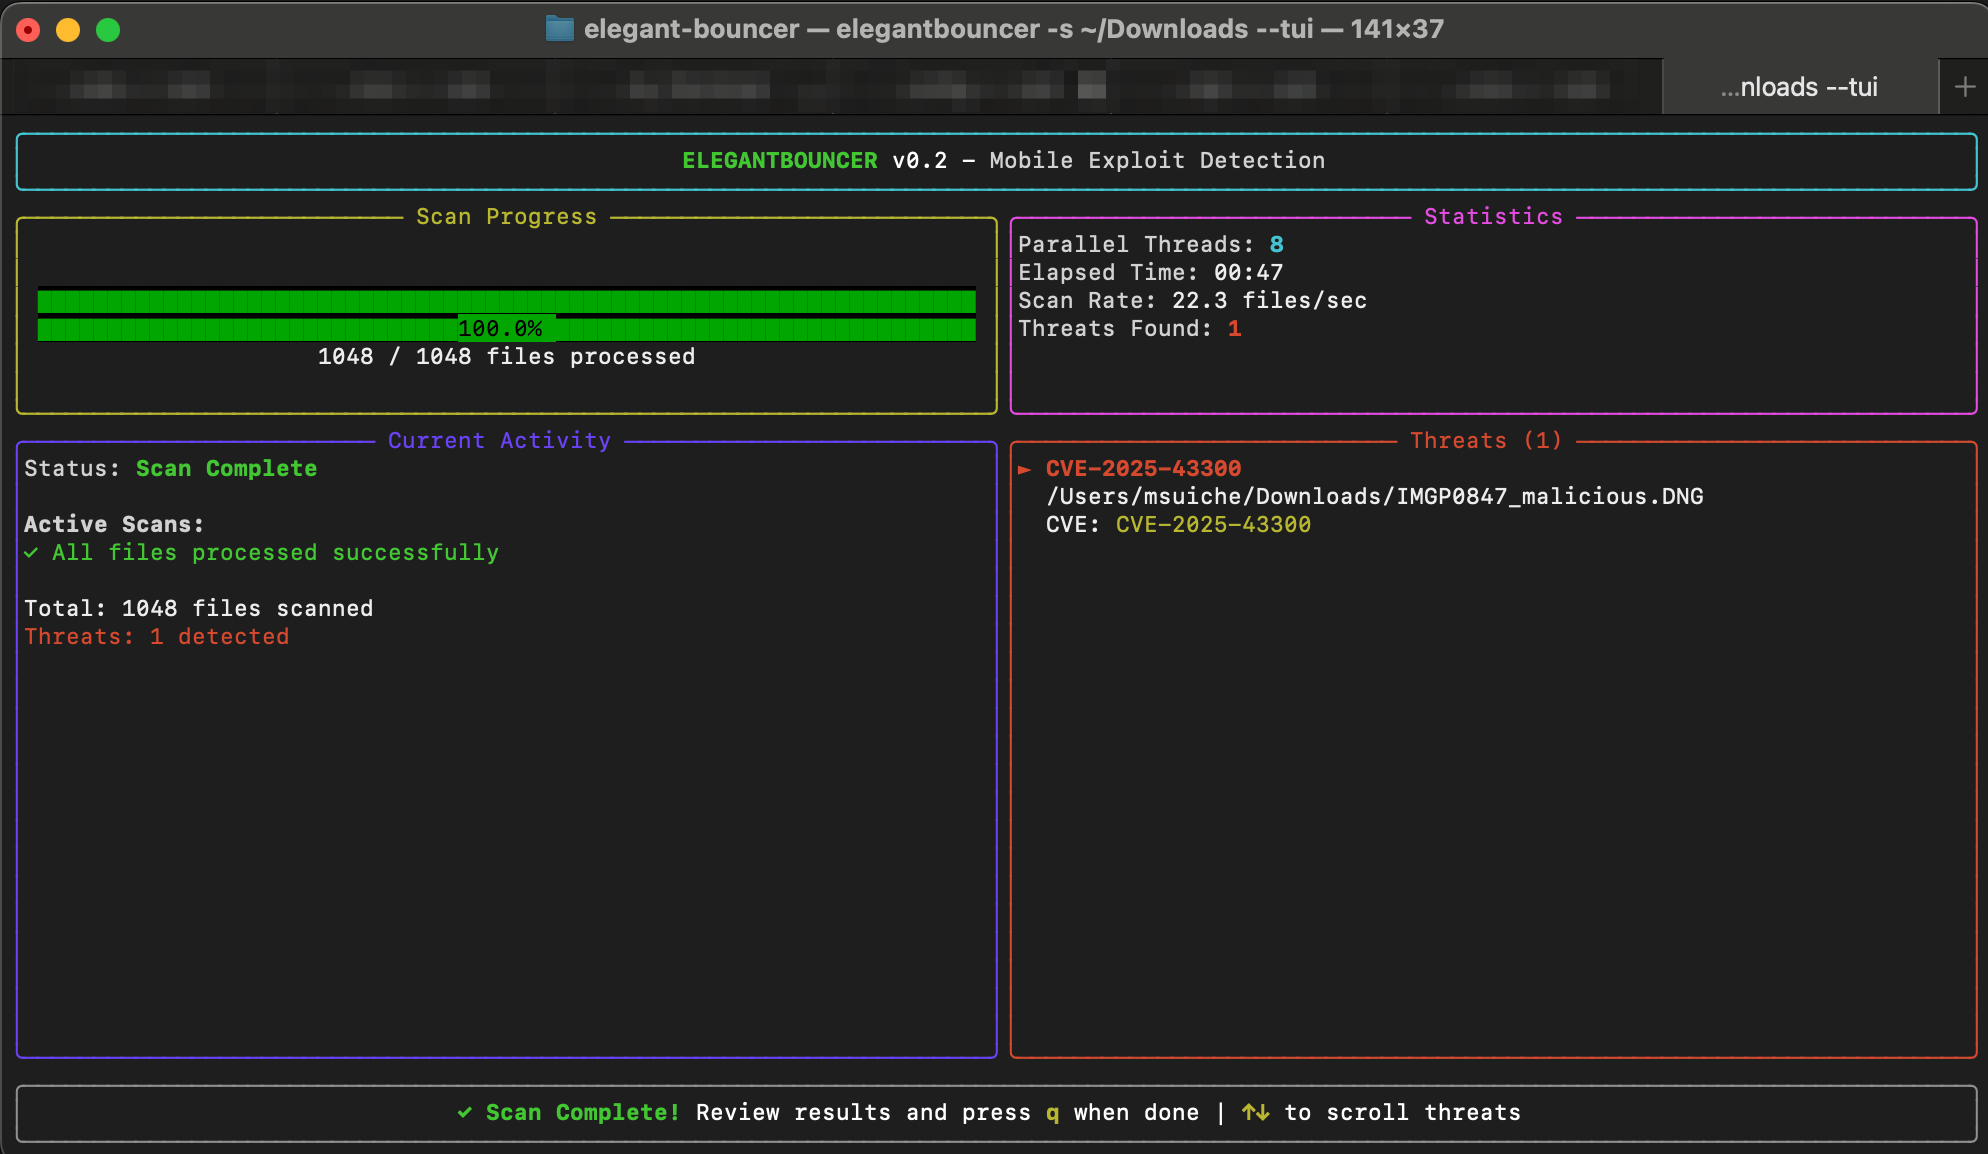
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.

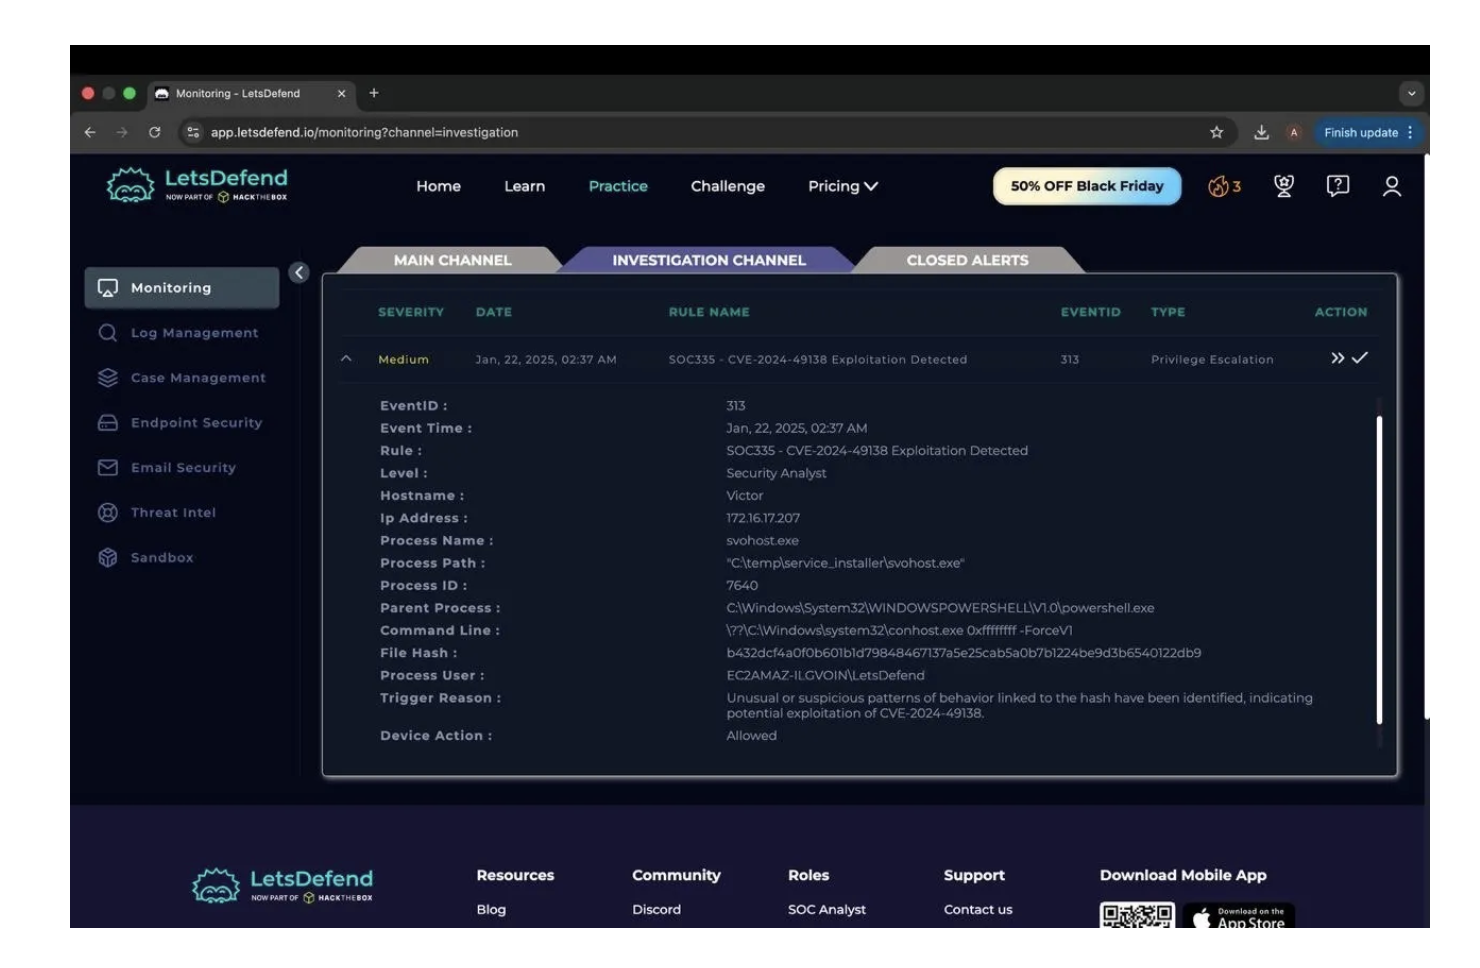
SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…

Malware analysis from the domain goxlr.net

Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.

Sources of Synacktiv's challenge for leHack 2026

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

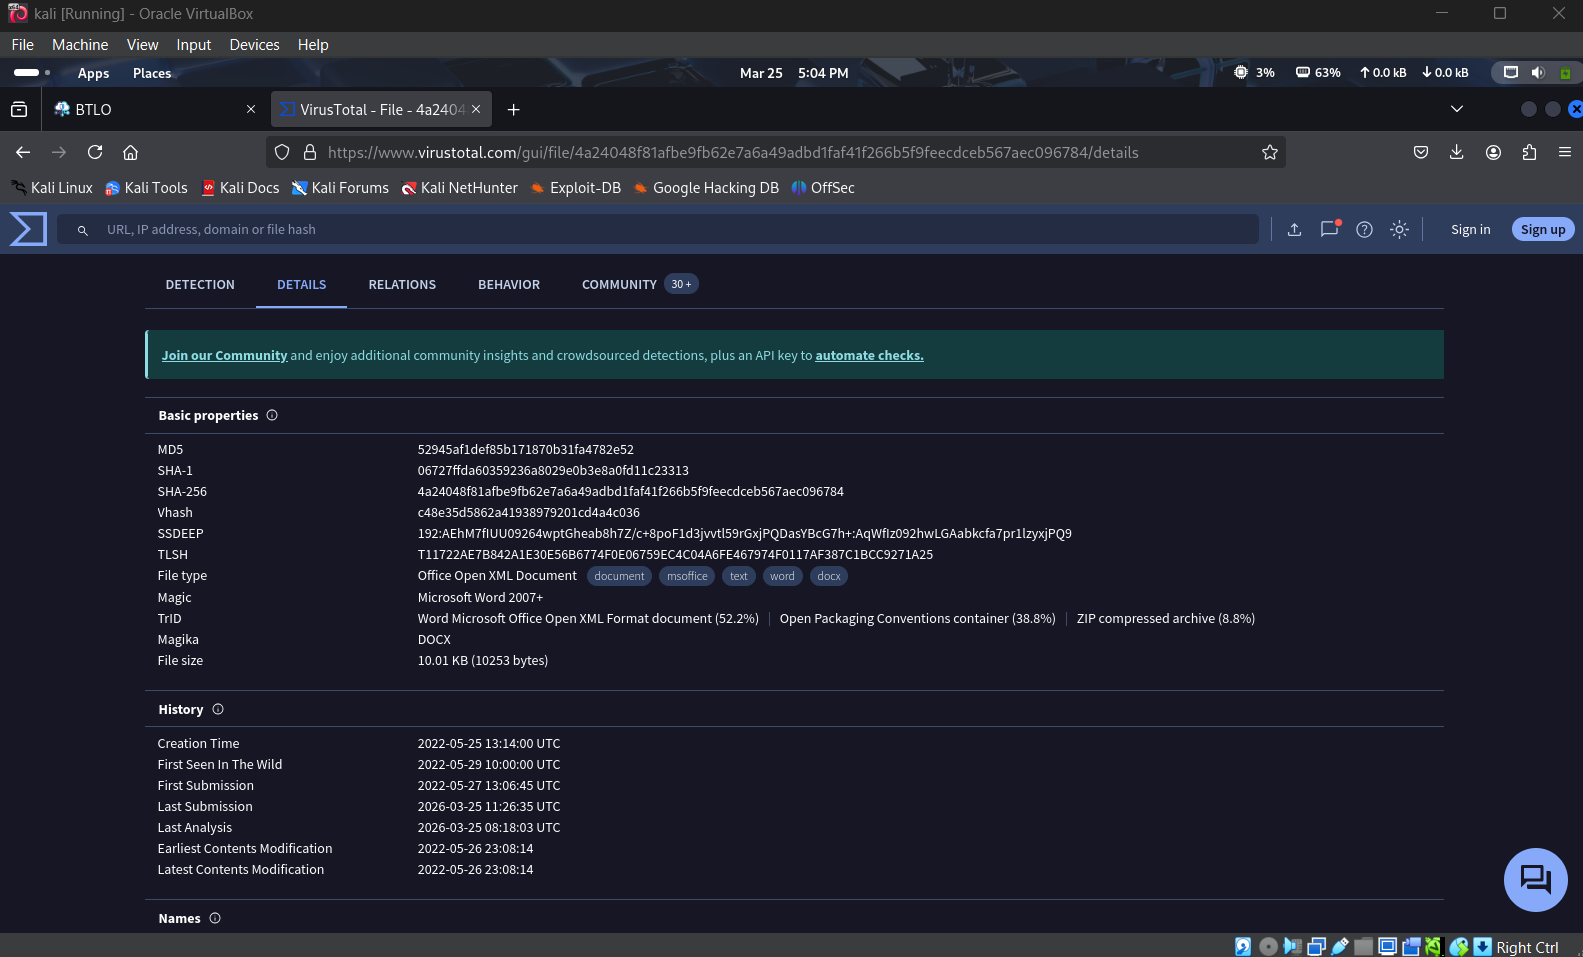
Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online

Repository containing the compromised certificate seen in recent CVE-2022-30190 (Follina) attacks.

SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

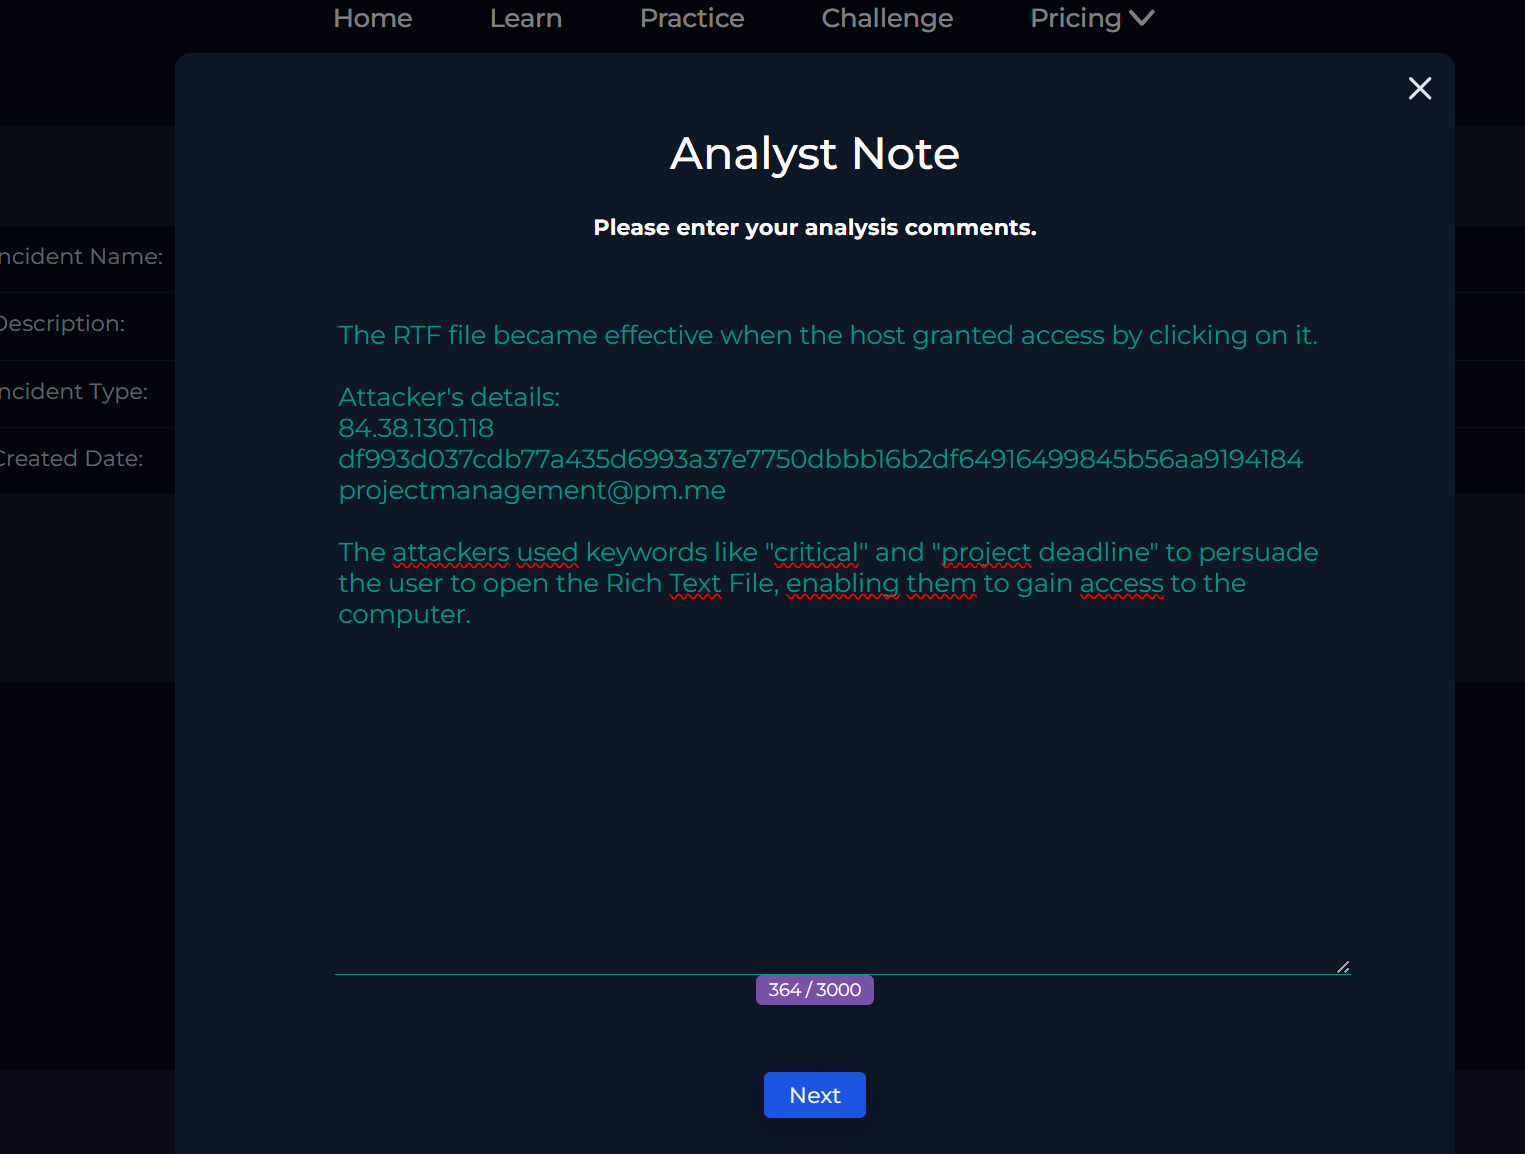
We are expected to investigate a critical alert reporting a Windows OLE zero-click RCE exploitation (CVE-2025-21298) delivered via a malicious RTF…