
CVE-2019-19781-DFIR-Notes
 azeemering/cve-2019-19781-dfir-notes
My Citrix ADC NetScaler CVE-2019-19781 Vulnerability DFIR notes.
curated-resourcesdigital-forensicseducation+5
azeemering/cve-2019-19781-dfir-notesMy Citrix ADC NetScaler CVE-2019-19781 Vulnerability DFIR notes.
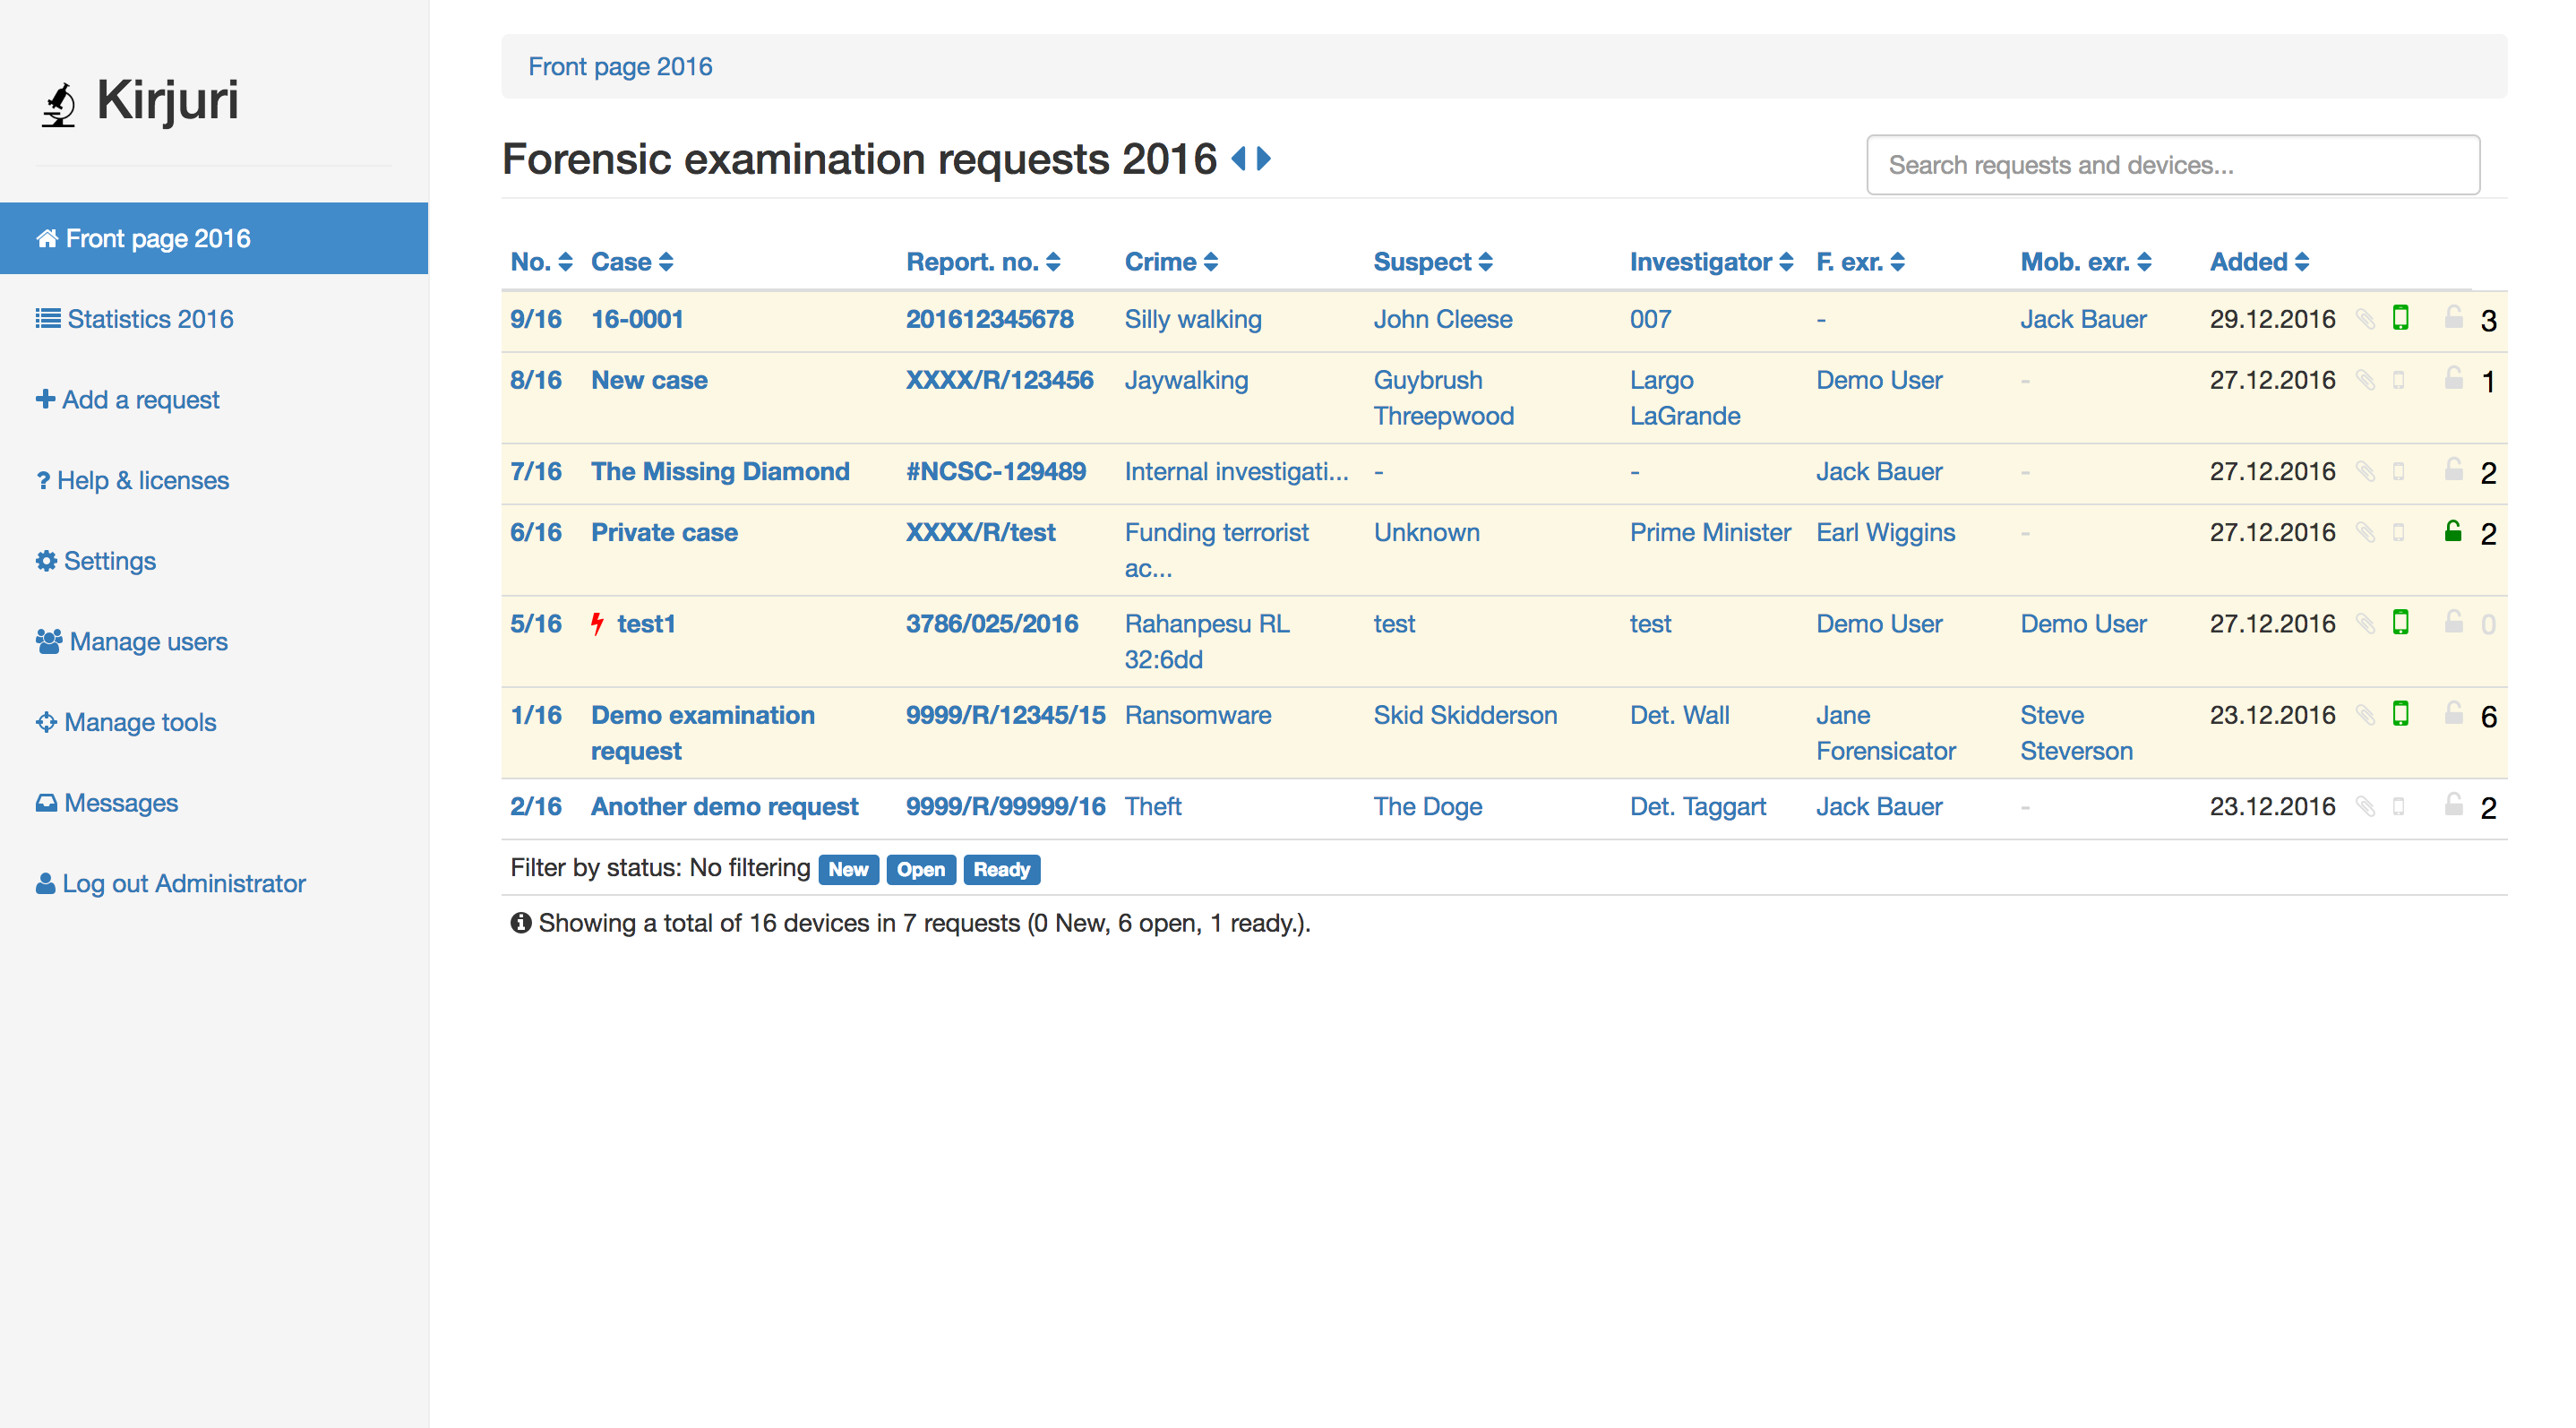 anttikurittu/kirjuri
Kirjuri is a web application for managing cases and physical forensic evidence items.
 libyal/libfsntfs
Library and tools to access the Windows New Technology File System (NTFS)
 libyal/libvmdk
Library and tools to access the VMware Virtual Disk (VMDK) format
 libyal/libvhdi
Library and tools to access the Virtual Hard Disk (VHD) image format
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 libyal/libqcow
Library and tools to access the QEMU Copy-On-Write (QCOW) image format
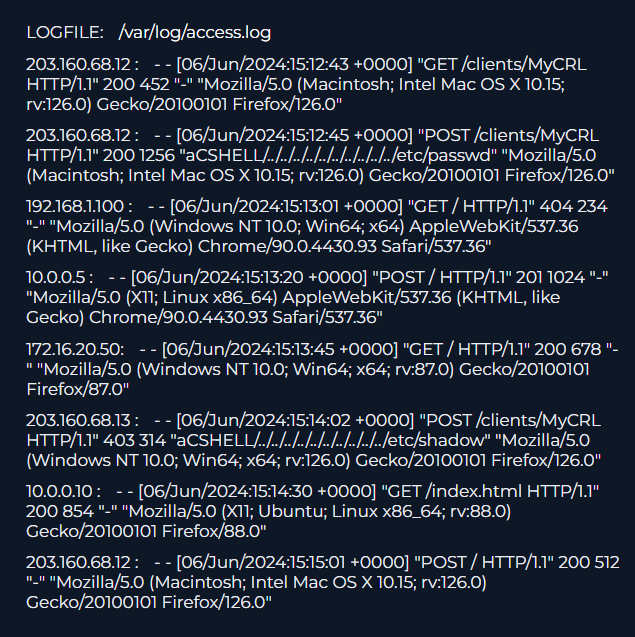 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 libyal/libfwsi
Library to access the Windows Shell Item format
 nccgroup/killedprocesscanary
A canary designed to minimize the impact from certain Ransomware actors
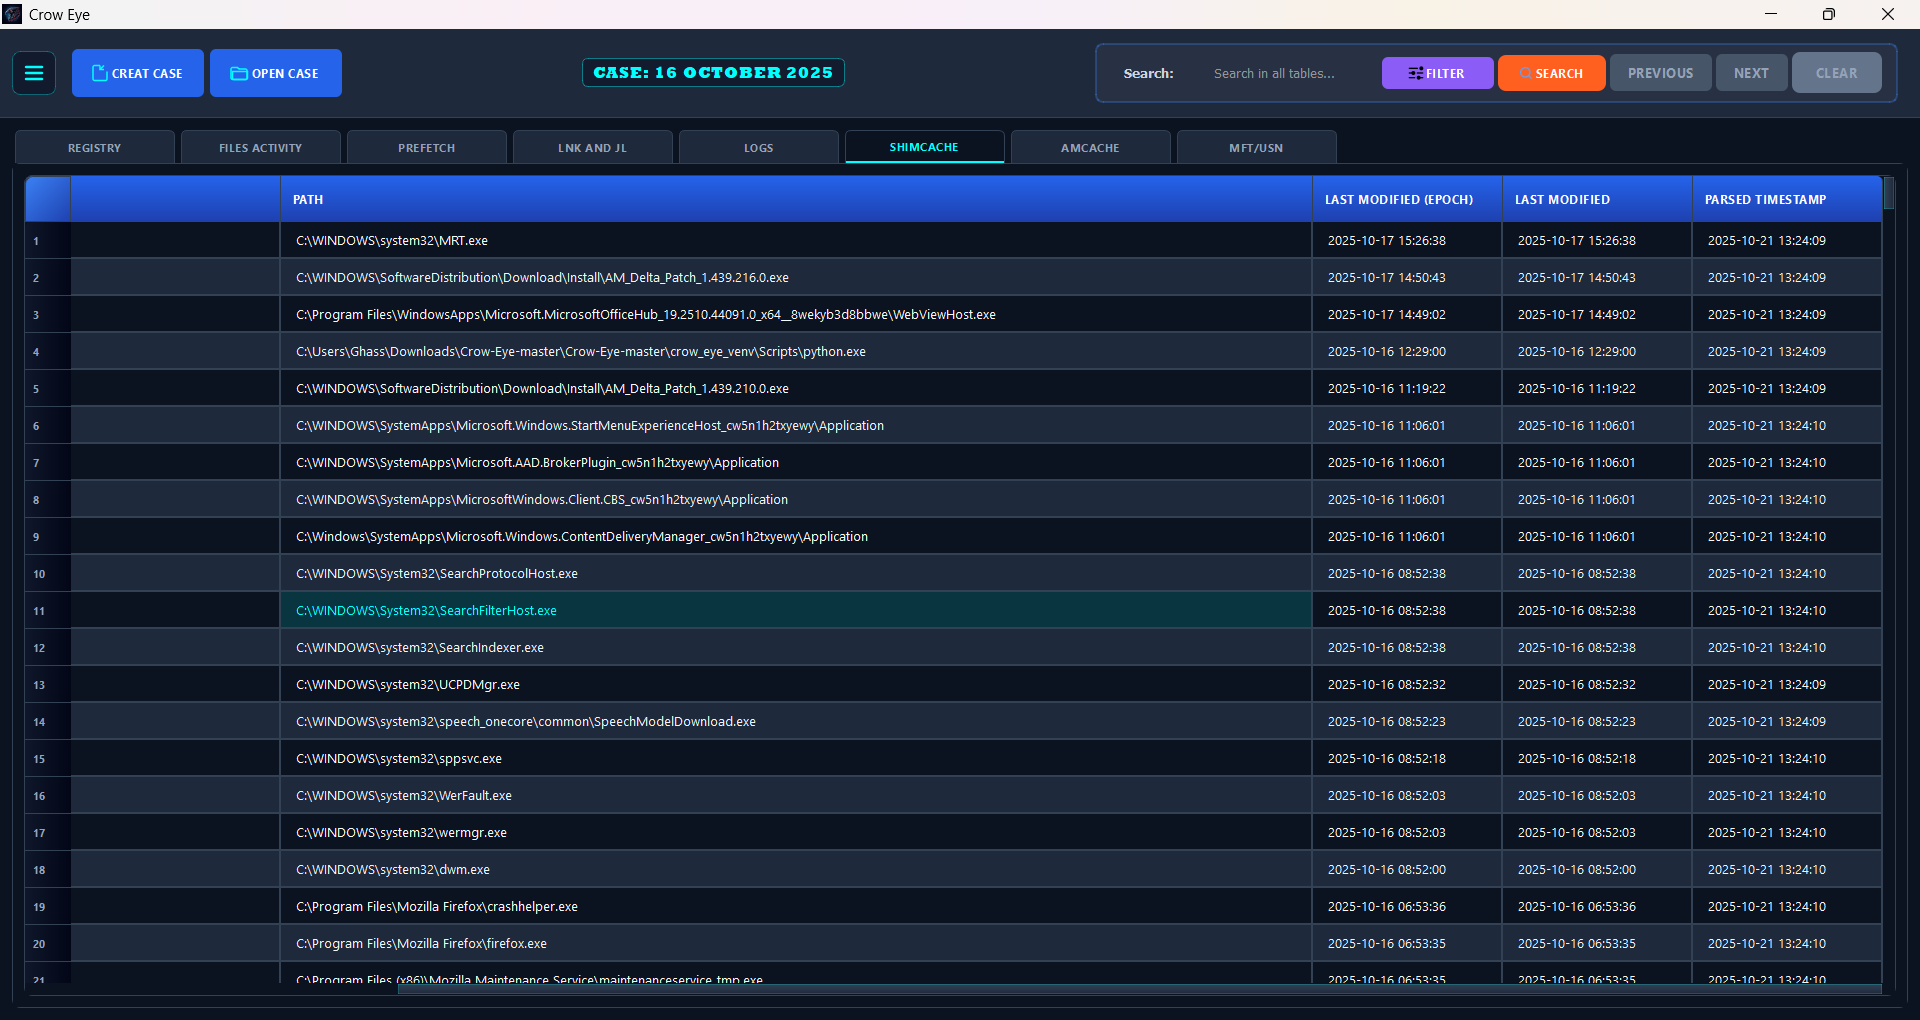 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 zedocun/sharepoint-toolshell-cve-2025-53770-incident-analysis
Technical analysis of a SharePoint ToolShell (CVE-2025-53770) exploitation attempt involving RCE, webshell deployment, and MachineKey extraction.
 libyal/libewf
C library and command-line toolkit for forensic EWF image handling: acquire, export, verify, recover, and mount evidence files in EnCase and SMART…
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification