
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
59 results
Argos preview

Argos

GitLabfunctori/argos/argos

Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)

anomaly-detectiondigital-forensicsinformation-gathering+3
1
13h 20m ago
TCPViewer preview

TCPViewer

GitHubproxymanapp/tcpviewer

The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
digital-forensicsforensicsinformation-gathering+3
6214h 6m ago
sniperscope preview

sniperscope

GitHubkamehameha-ctrl/sniperscope

External attack surface management workstation that correlates DNS, certificate transparency, Shodan, CVEDB, TLS and OSINT data into risk-scored…

digital-forensicsdns-analysisemail-harvesting+8
418h 58m ago
arkime preview

arkime

GitHubarkime/arkime

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

defensive-toolsdigital-forensicsforensics+7
7.4k2 days ago
iDescriptor preview

iDescriptor

GitHubidescriptor/idescriptor

privacy-first, open-source and free idevice management tool written in Rust and Qt
digital-forensicsforensicsinformation-gathering+6
4.1k2 days ago
sentrysearch preview

sentrysearch

GitHubssrajadh/sentrysearch

Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
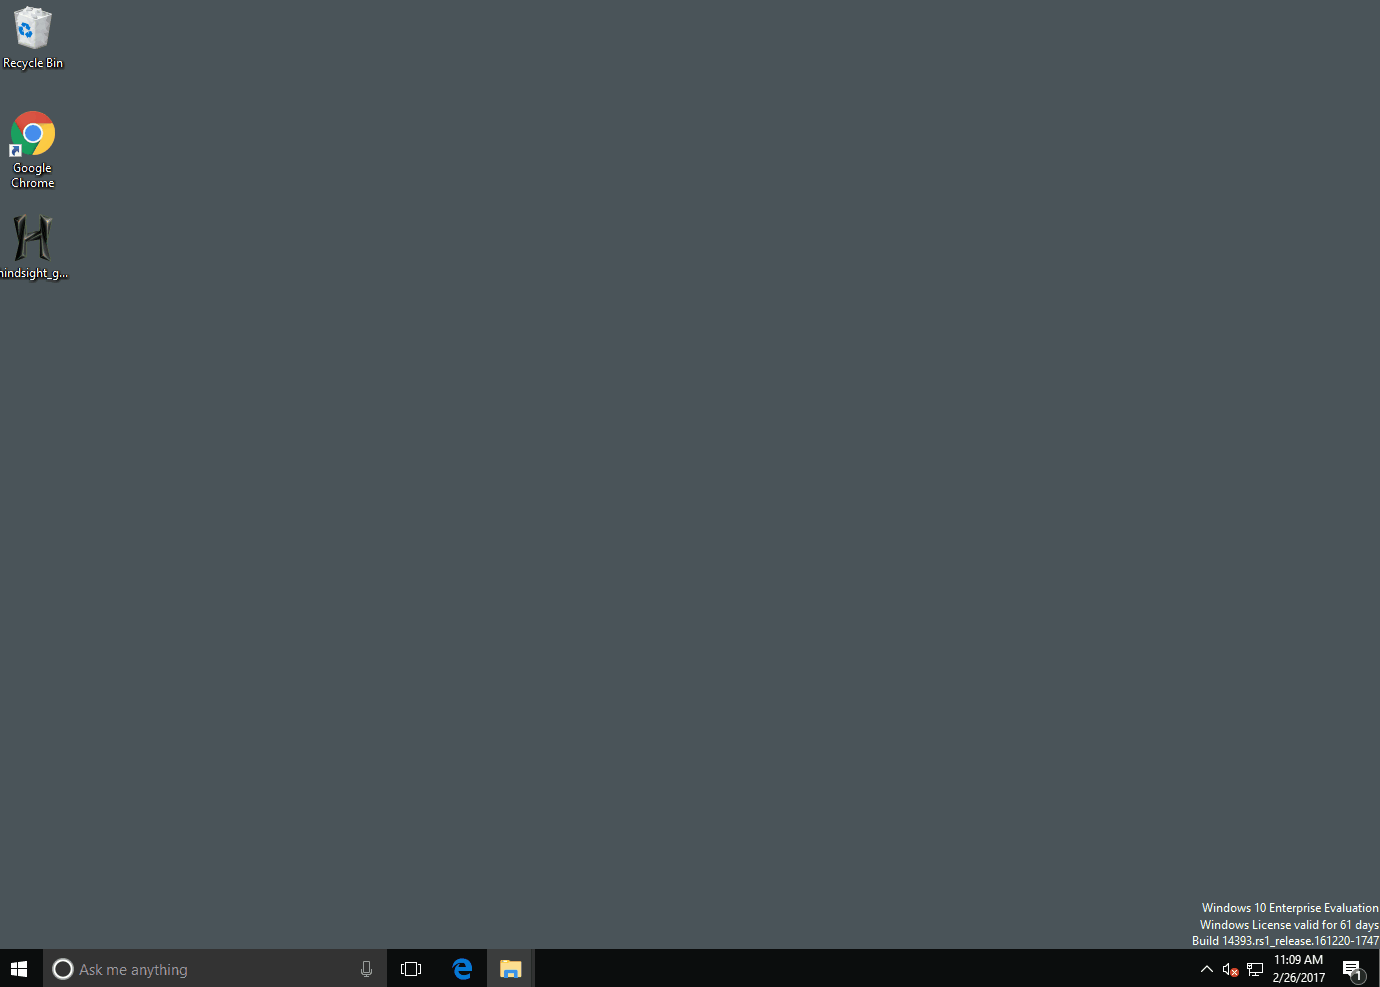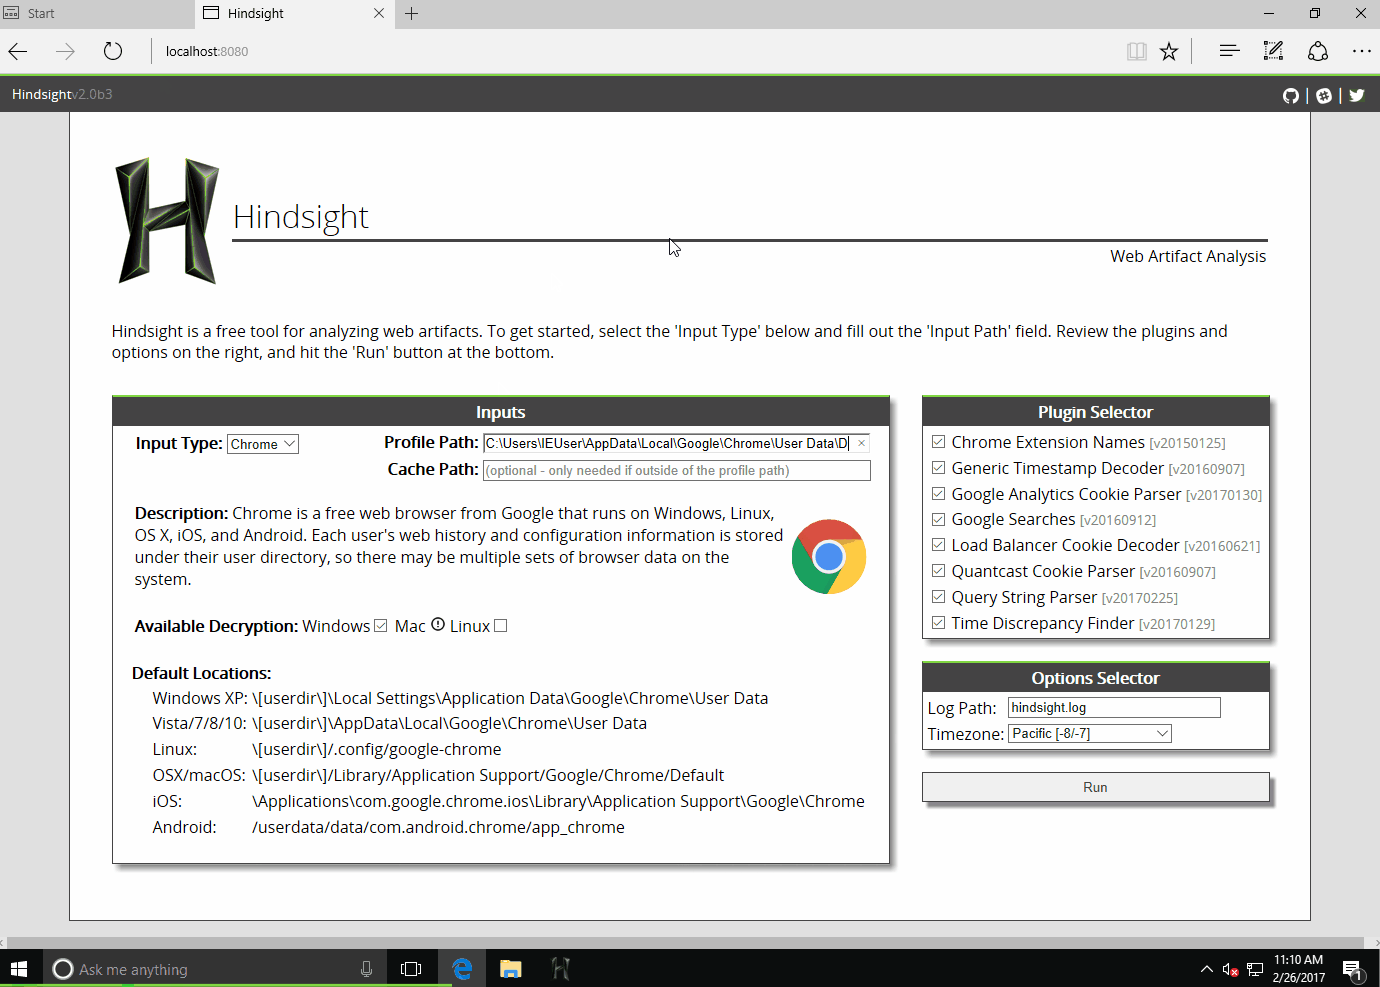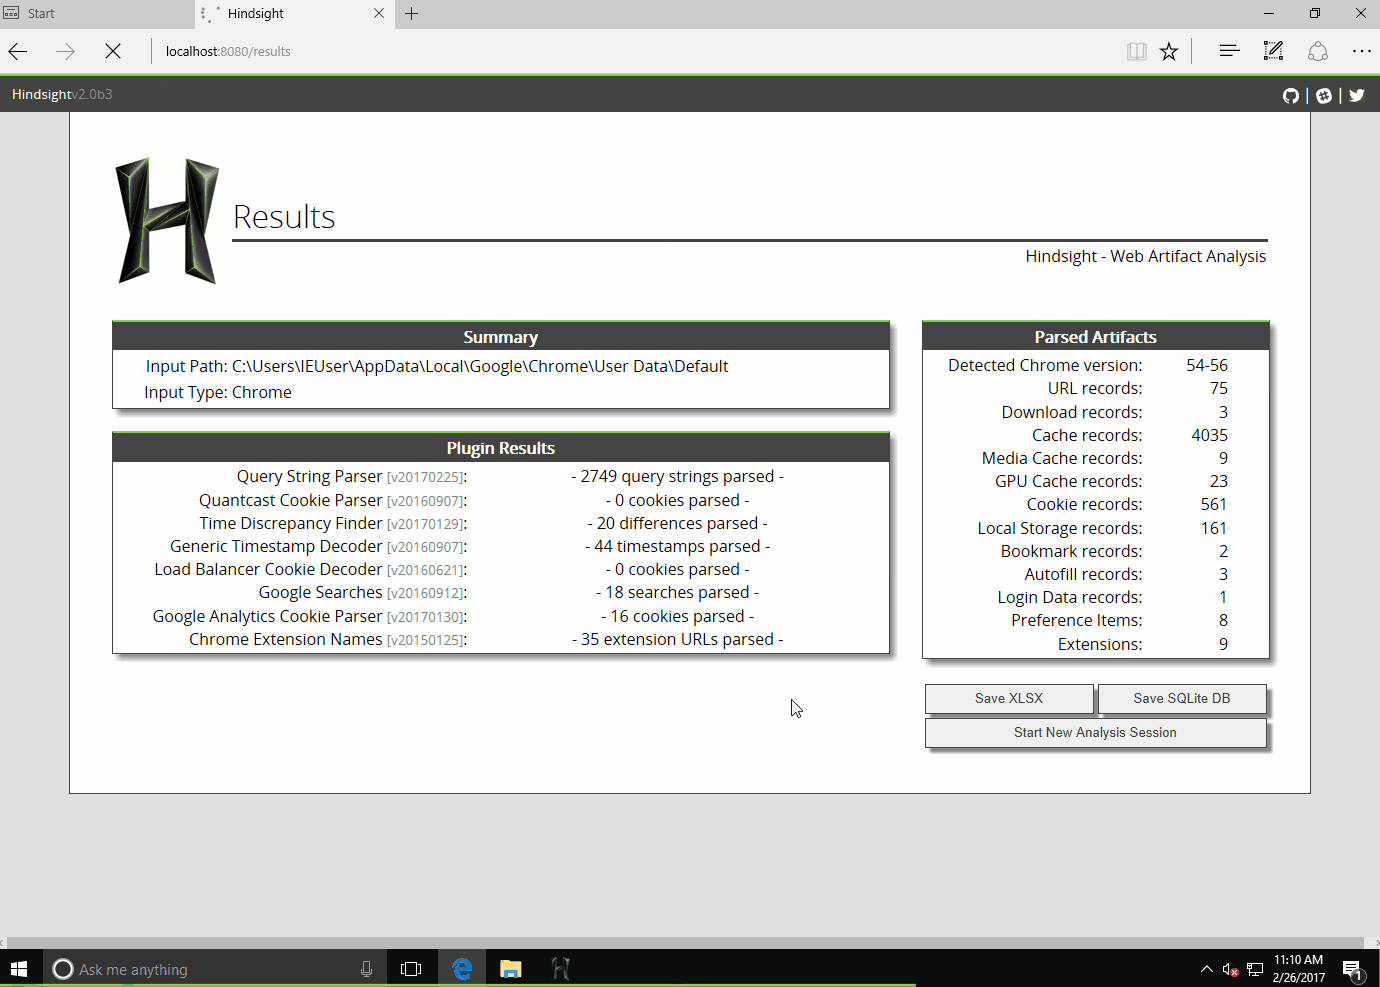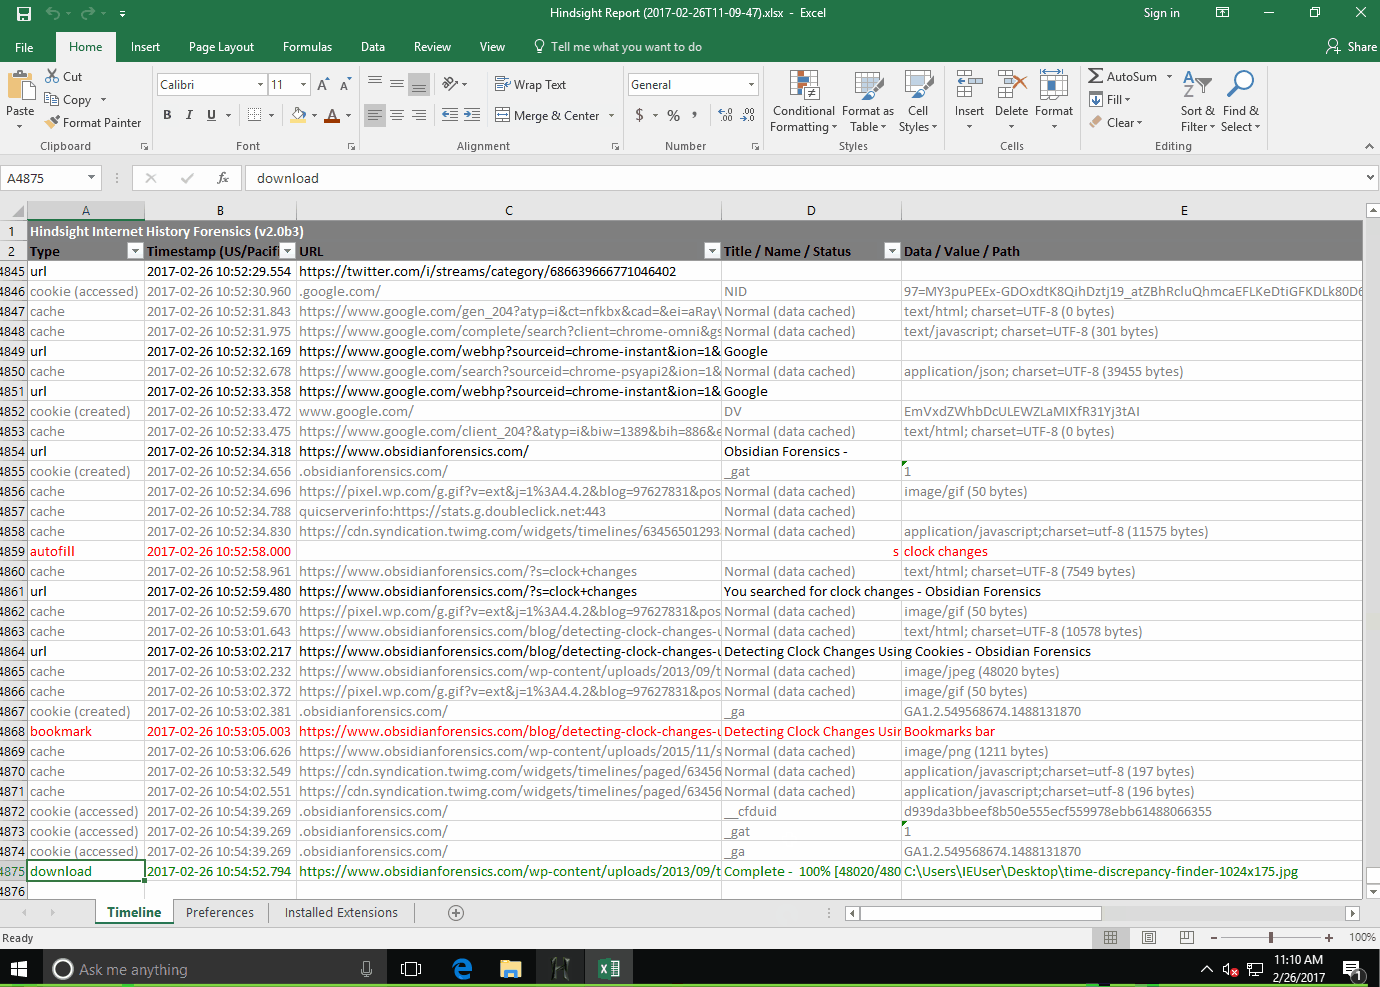
digital-forensicsforensicsinformation-gathering+3
4.4k3 days ago
hindsight preview

hindsight

GitHubryandfir/hindsight

Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
digital-forensicsforensicsinformation-gathering+1
1.5k4 days ago
Threat-Remediation-Scripts preview

Threat-Remediation-Scripts

GitHubxephora/threat-remediation-scripts

This repository contains a list of new remediation scripts.
defensive-toolsdigital-forensicsincident-response+5
19015 days ago
Cortex preview

Cortex

GitHubthehive-project/cortex

Cortex: a Powerful Observable Analysis and Active Response Engine
digital-forensicsincident-responseinformation-gathering+5
1.6k16 days ago
untitledgoosetool preview

untitledgoosetool

GitHubcisagov/untitledgoosetool

Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
cloud-securitydefensive-toolsdigital-forensics+4
96322 days ago
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecting & Hunting for IOCs with gusto and style

digital-forensicsforensicsincident-response+6
23823 days ago
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.4k1 month ago
tgscope preview

tgscope

GitHubitsmoorgrove/tgscope

Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
crawlerdigital-forensicsinformation-gathering+1
2 months ago
phantomprint preview

phantomprint

GitHubharuu77g/phantomprint

Passive hybrid fingerprinting engine — identify hosts without sending a single packet
digital-forensicsinformation-gatheringnetwork-mapping+7
42 months ago
ALPC-Enumerator preview

ALPC-Enumerator

GitHubtalha-nazeef-ahmed/alpc-enumerator

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
digital-forensicsinformation-gatheringmalware-analysis+4
312 months ago
Microsoft-Extractor-Suite preview

Microsoft-Extractor-Suite

GitHubinvictus-ir/microsoft-extractor-suite

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
cloud-securitydigital-forensicsincident-response+3
8374 months ago
GOXLR-malware-family preview

GOXLR-malware-family

GitHubdestiny-creates/goxlr-malware-family

Malware analysis from the domain goxlr.net
digital-forensicsinformation-gatheringioc-management+3
45 months ago
sharker preview

sharker

GitHubsynacktiv/sharker

A simple, reliable and reasonably fast network capture analyzer.

digital-forensicsinformation-gatheringnetwork-security+3
335 months ago
Previous1234Next