

awesome-lists
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
mthcht/awesome-listsCurated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 cea-sec/usbsas
Tool and framework for securely reading untrusted USB mass storage devices.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

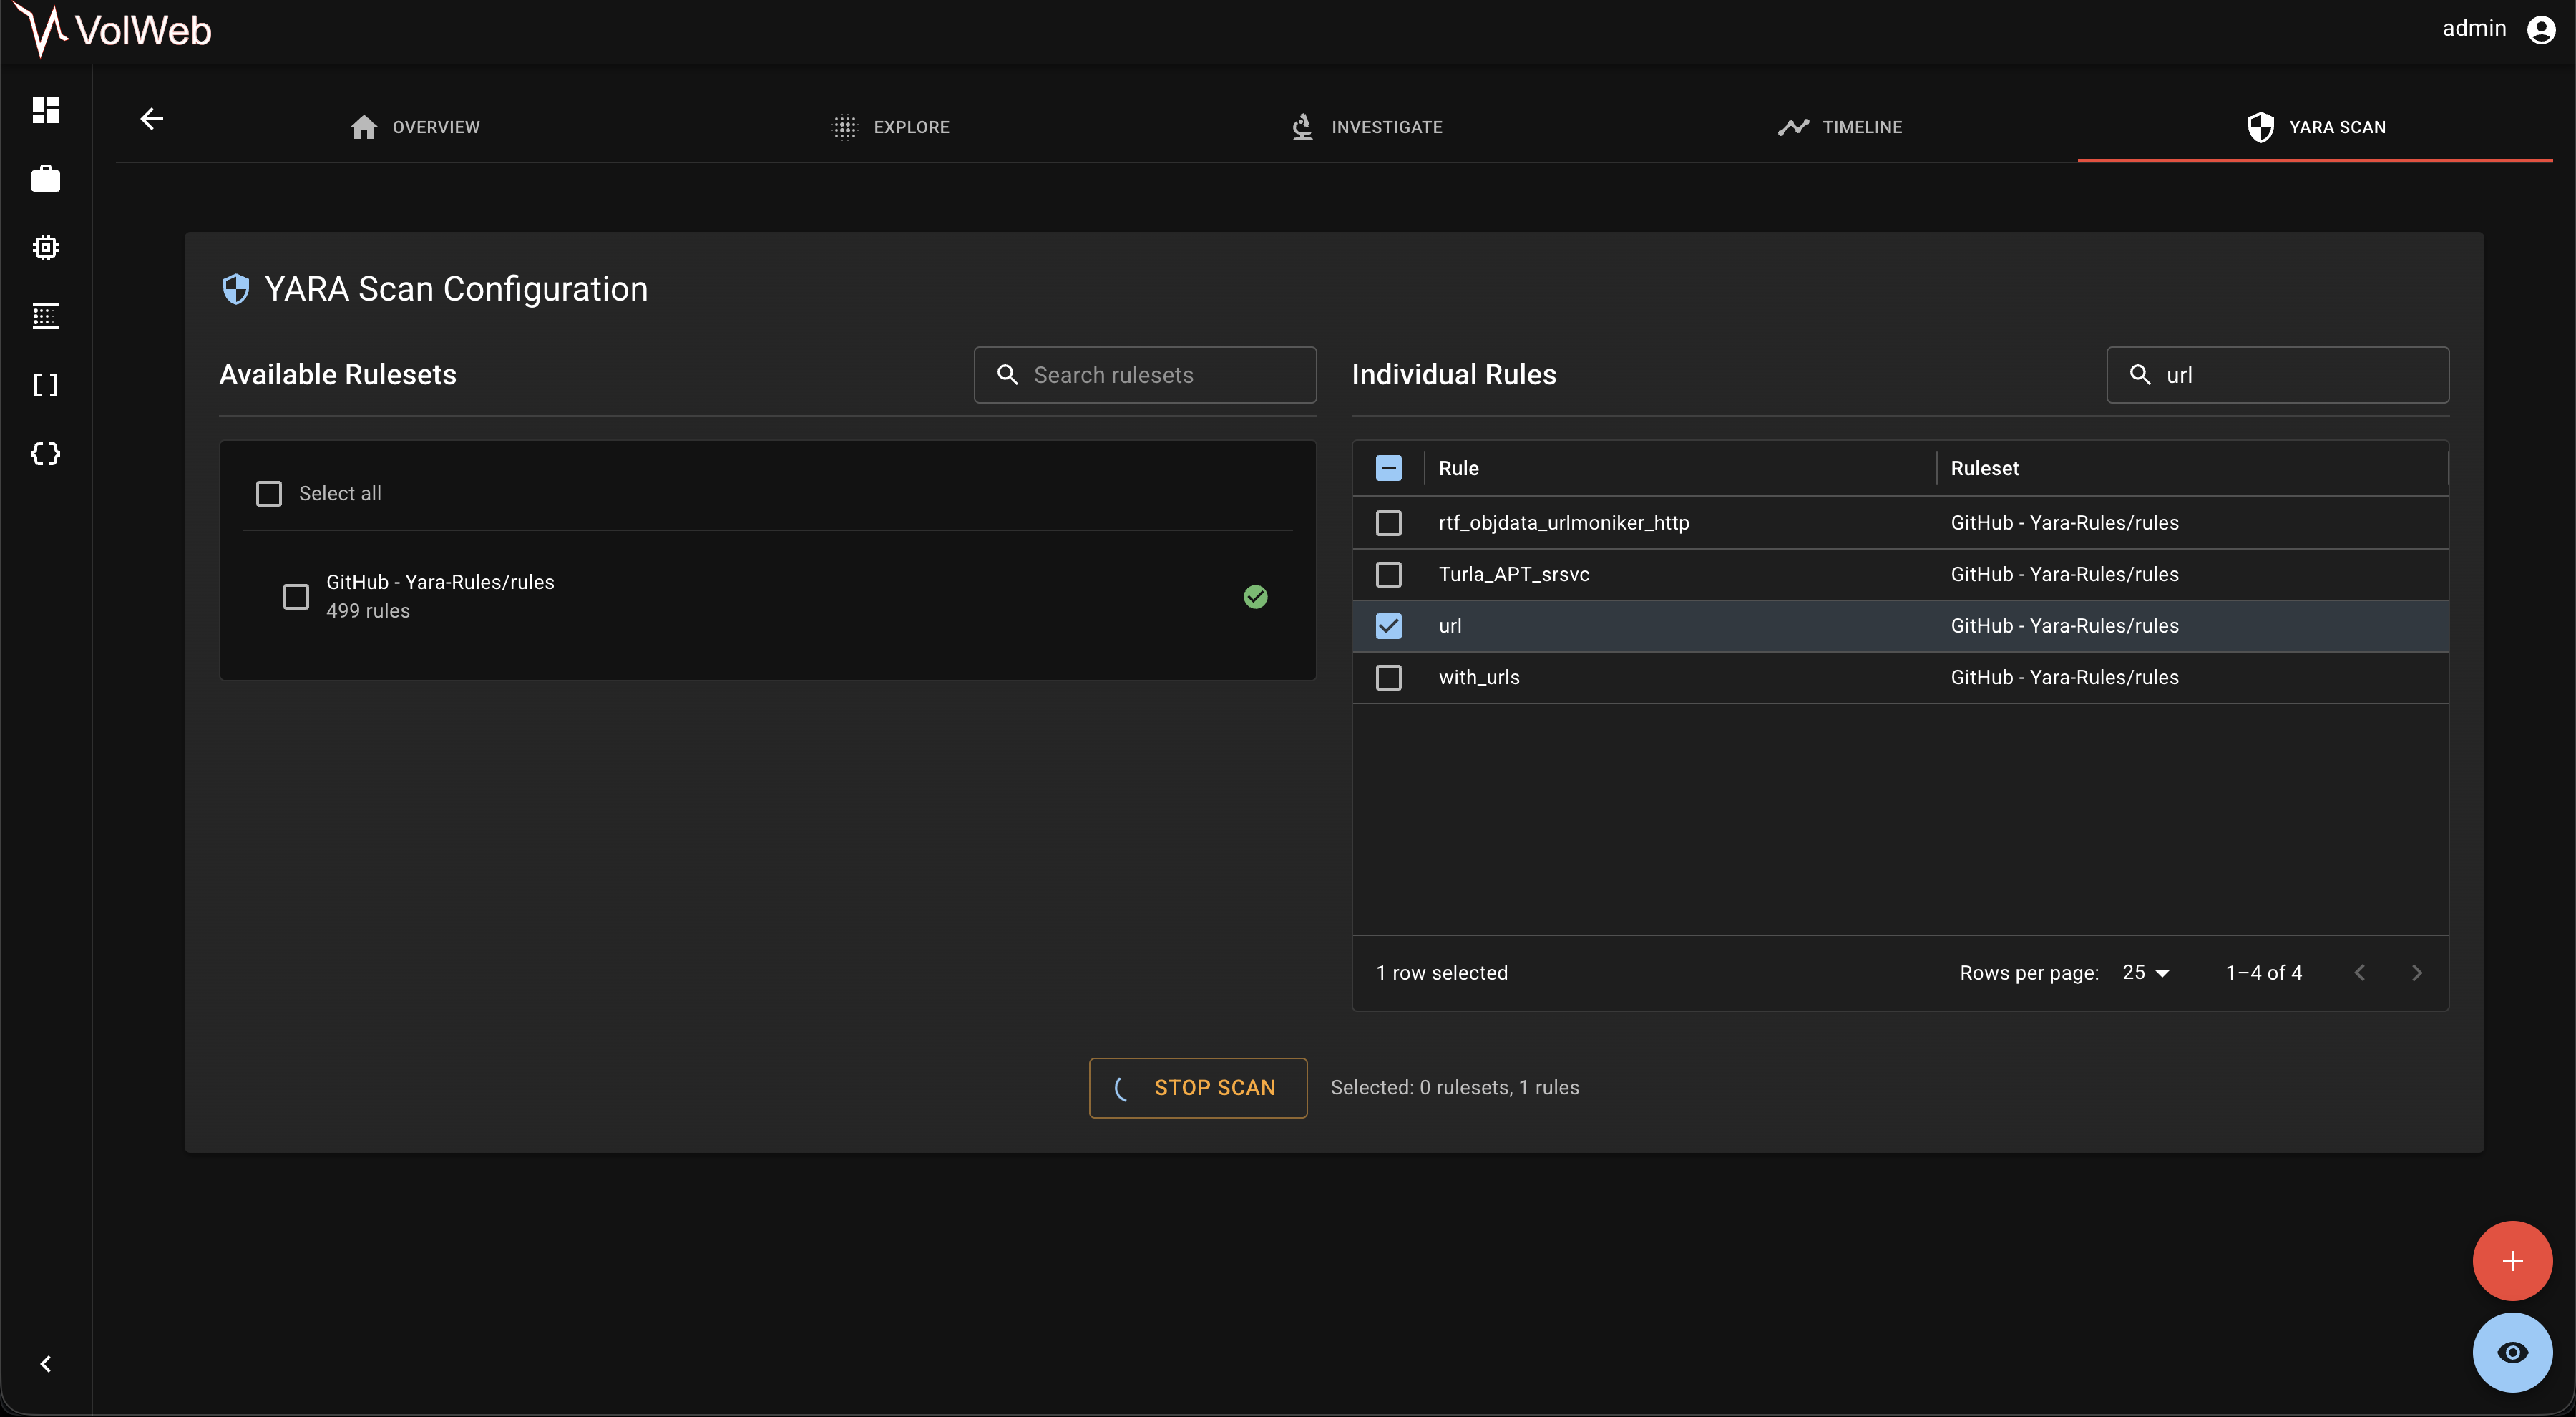 k1nd0ne/volweb
A centralized and enhanced memory analysis platform

 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
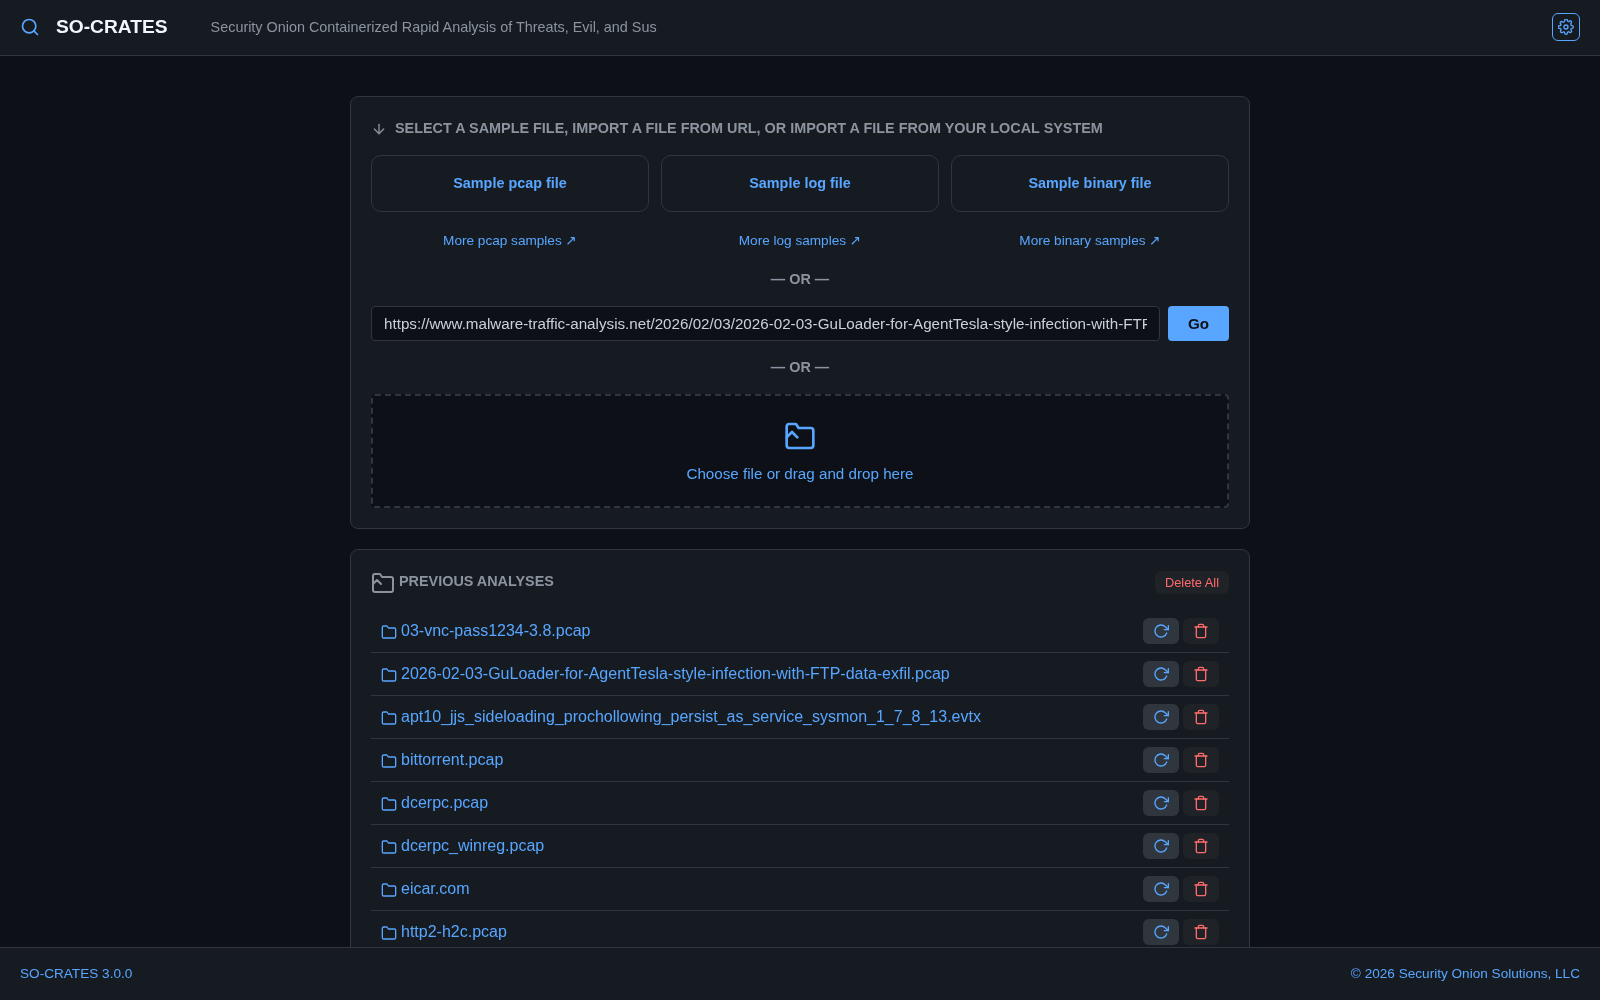 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!