

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
13.1k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 kraxel/virt-firmware
Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…
 dahnutz/zimbra-cve-2026-73570-ir
Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…
 cristianzsh/forensictools
Collection of forensic tools
 creamyg31337/ncentral-compromise-ioc-triage
Read-only N-able N-central CVE-2026-18556/CVE-2026-18577 post-exploitation IoC hunter for Windows endpoints
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
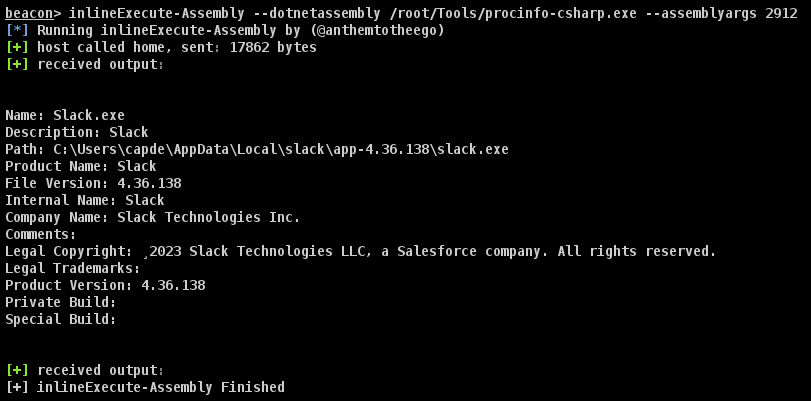 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 jfarley248/meat
This toolkit aims to help forensicators perform different kinds of acquisitions on iOS devices
 navytitanium/eitest-tools-scripts-iocs
IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…