

ubuntils
 asmitdesai/ubuntils
Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
configuration-auditingdefensive-toolsdigital-forensics+7
4
asmitdesai/ubuntilsPython CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 rails/rails-forensics-cve-2026-66066
Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…
 politoinc/xwfacropalypse
X-Ways Acropalypse extension detects CVE-2023-21036 in common images
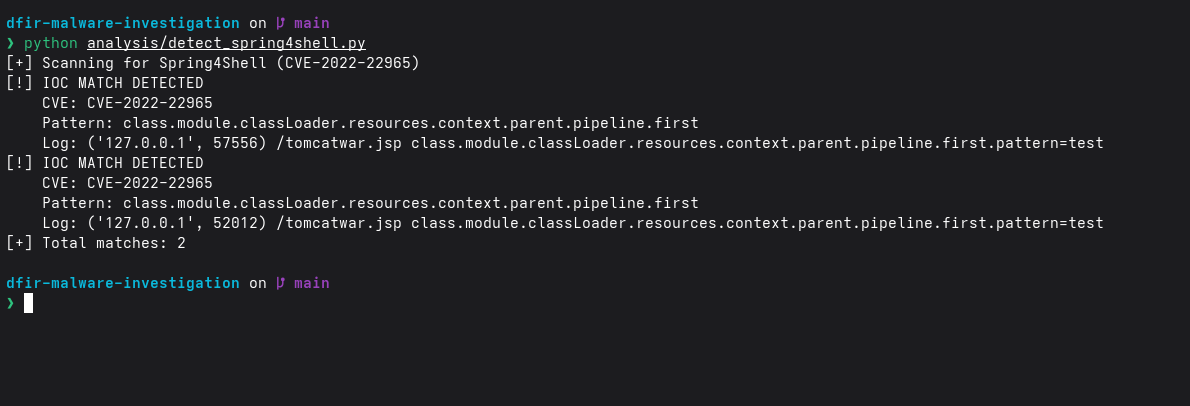 suyash-r-k/dfir-malware-investigation
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…