
Nimbus Vestige
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
cloud-securitydigital-forensicseducation+6
2
dobybaxter127/nimbus-vestigeA forensic reconstruction engine for cloud and identity incident response.

 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 maldev-academy/dumpbrowsersecrets
Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
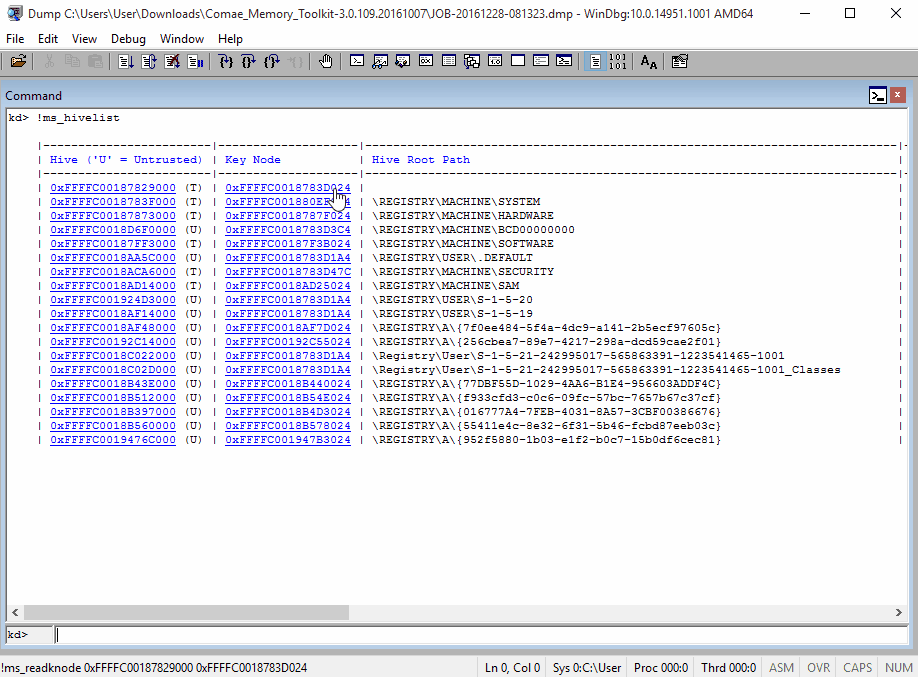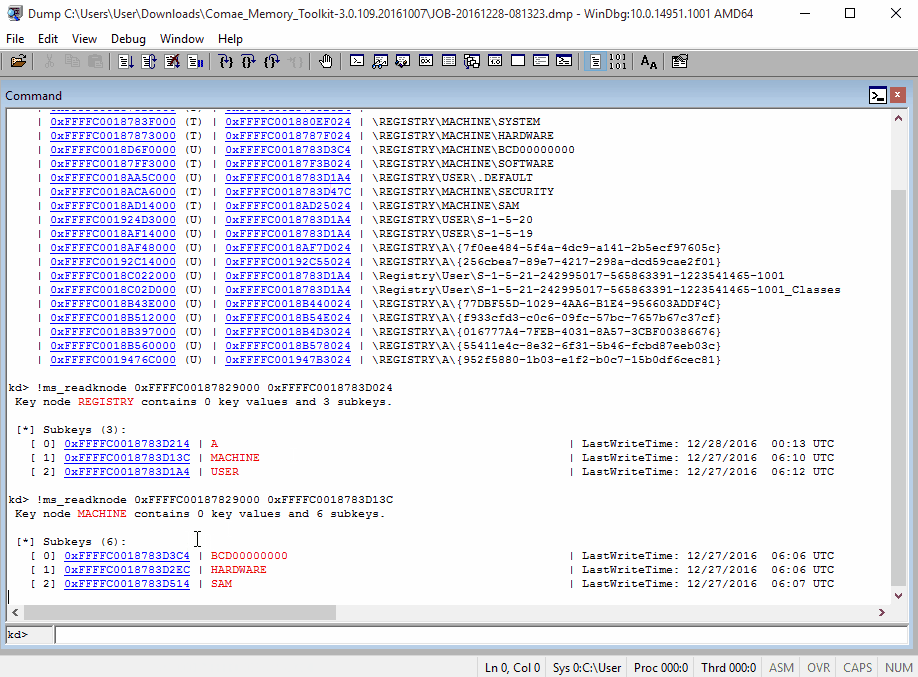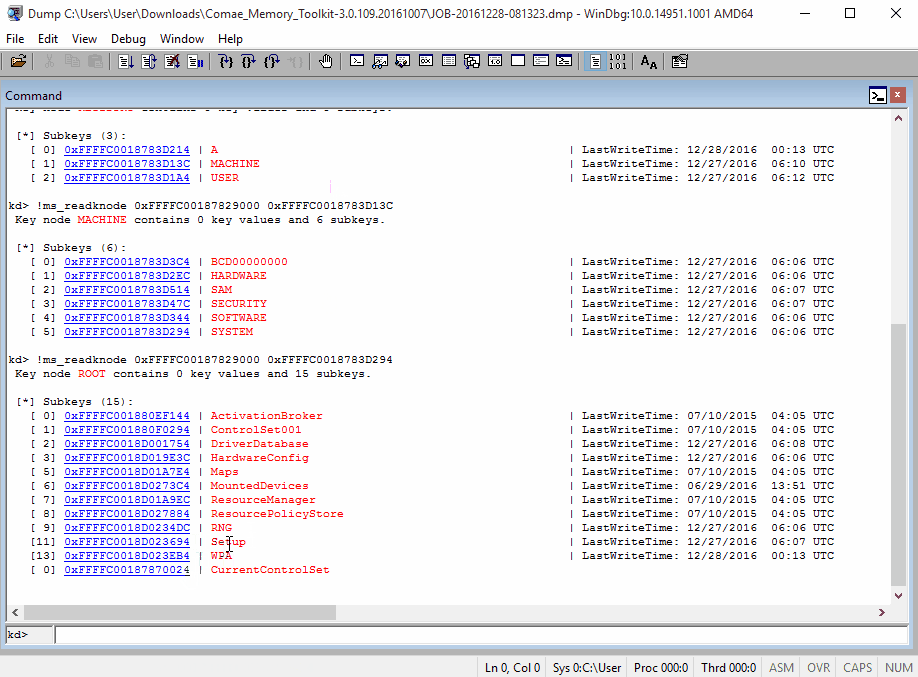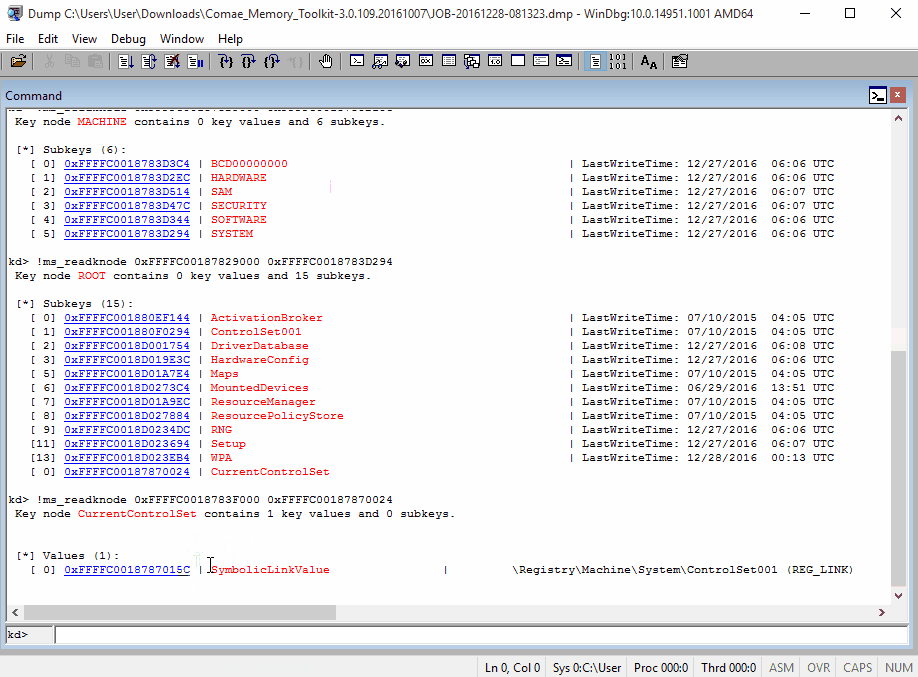 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension