
whatfiles
 spieglt/whatfiles
Log what files are accessed by any Linux process
digital-forensicsforensicsgeneral-purpose-utilities
spieglt/whatfilesLog what files are accessed by any Linux process
 qg5casz/walletool
Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
 neccie/yellowkey-bitlocker-cve-2026-45585
Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
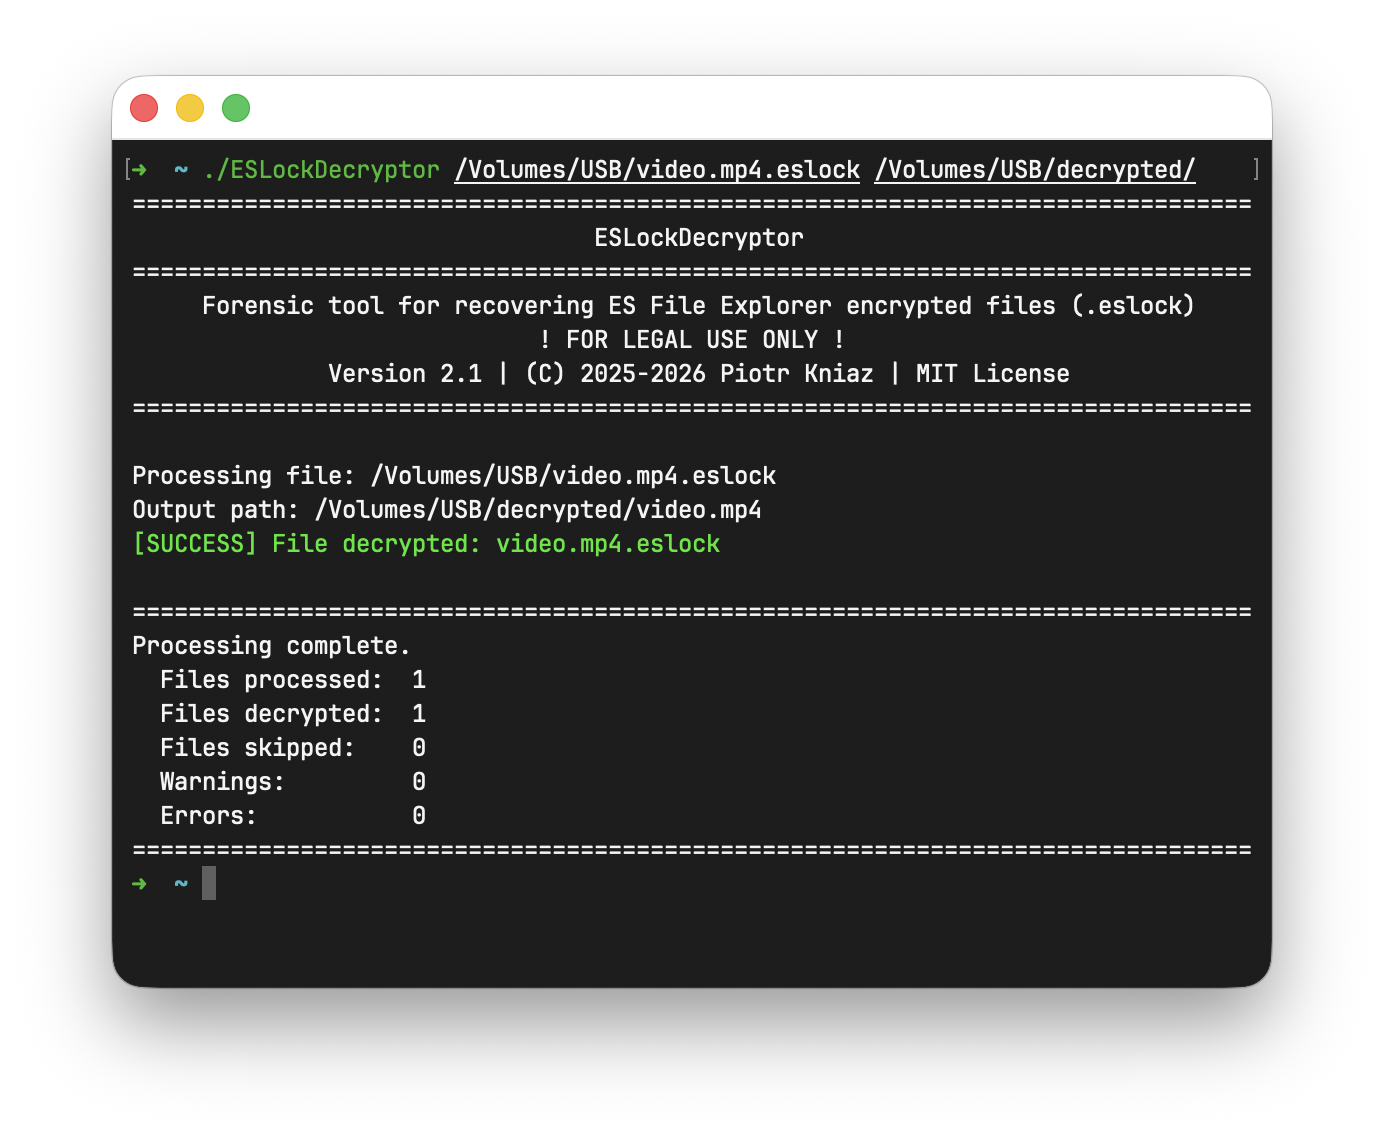 piotr-kniaz/eslockdecryptor
Utility for recovering ES File Explorer encrypted files (.eslock)
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
 volatilityfoundation/volatility
An advanced memory forensics framework
 m31r0n/sniprecover-cli
Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 mandiant/citrix-ioc-scanner-cve-2023-3519
Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 certcc/keyfinder
A tool for finding and analyzing private (and public) key files, including support for Android APK files.
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…