

volatility3
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.4k
volatilityfoundation/volatility3Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
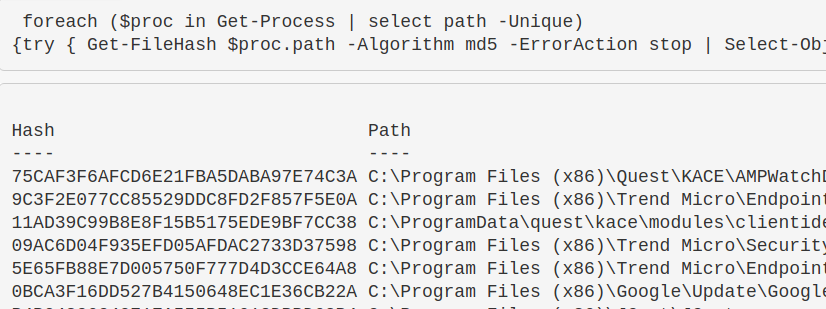 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
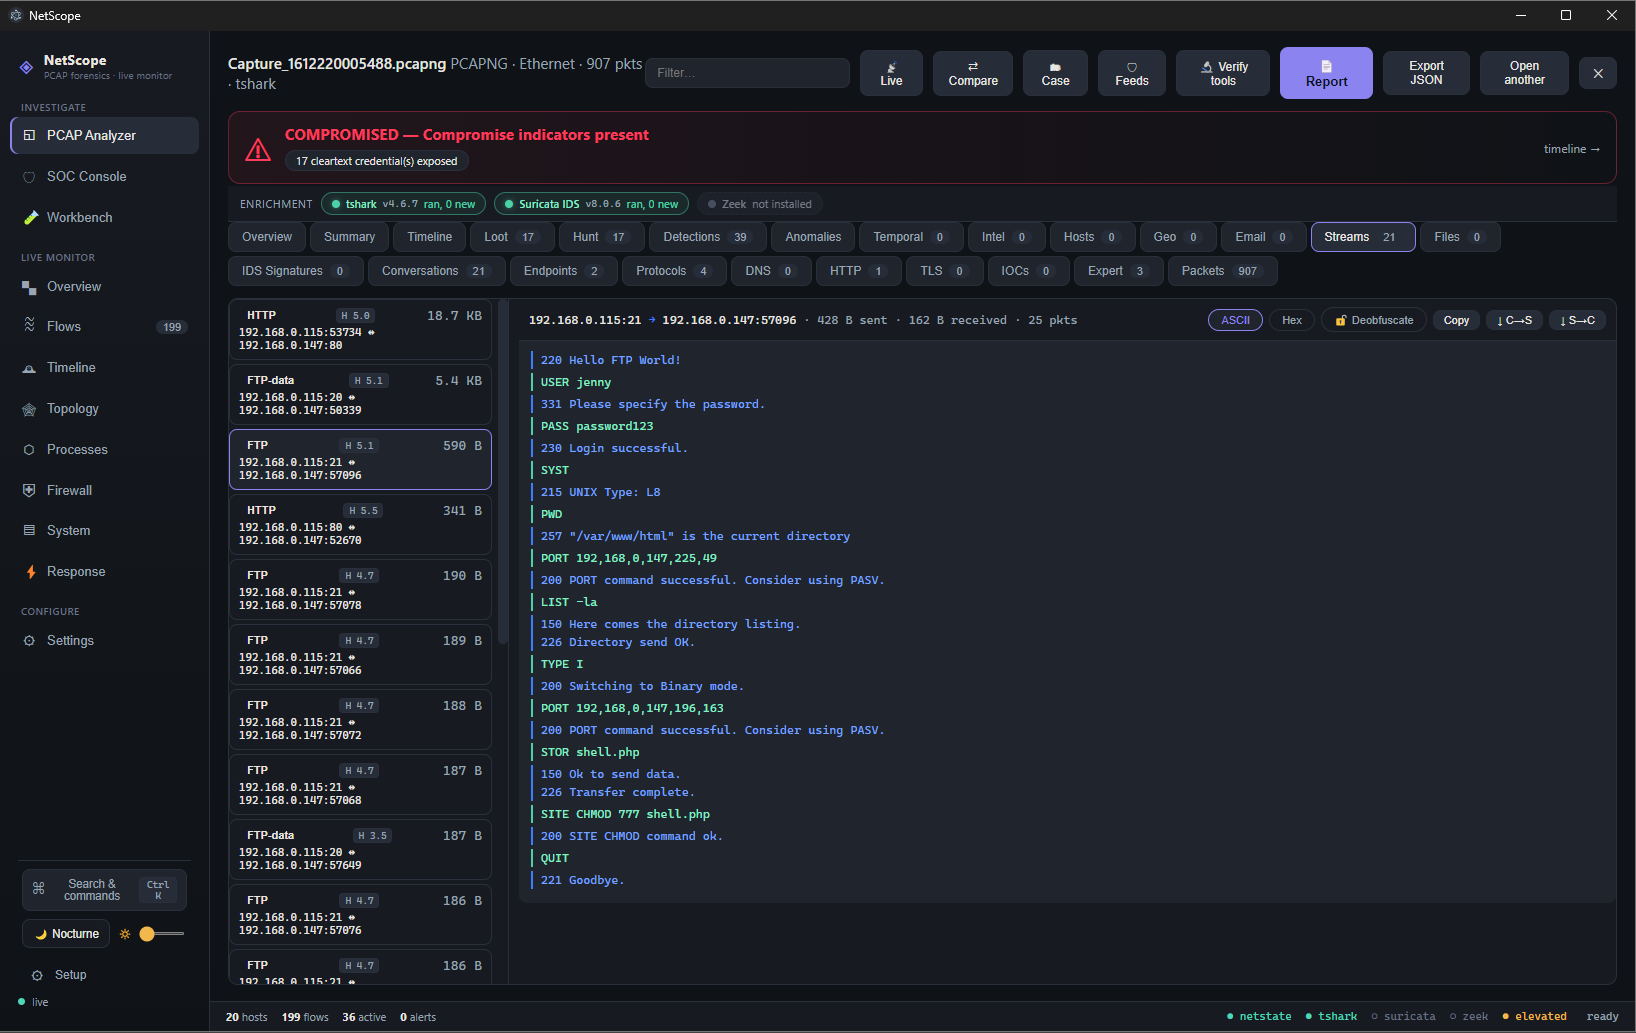 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
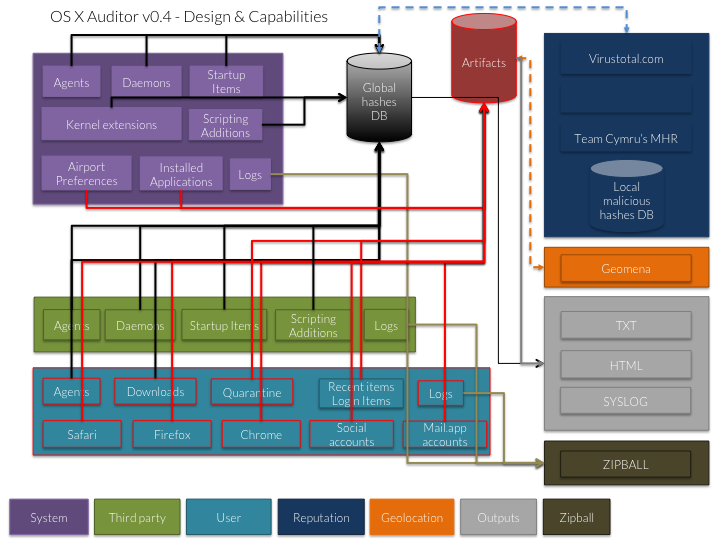 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics