
persisthunt
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
container-securitydigital-forensicsforensics+6
raj3shp/persisthuntLinux Persistence Detection, Hunting and Artifact Collection script
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 w116tjb/plex2shell-windows-hunt
Plex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 iqbaalilmii/acropalypse-reconstructor
A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 bjbakker1984/yellowkey-mitigation
PowerShell script that automates the WinRE mitigation workflow for CVE-2026-45585, with verification steps and conditional commit to avoid…
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
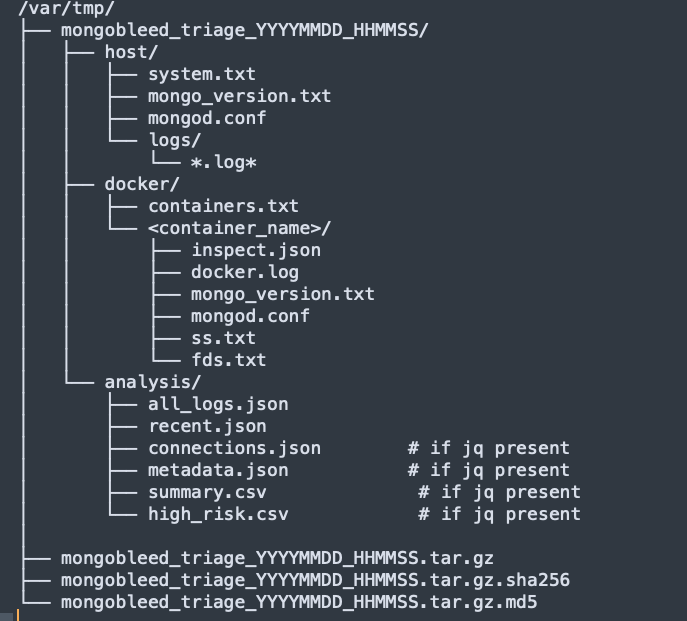 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…