
dfir-orc
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
defensive-toolsdigital-forensicsforensics+2
dfir-orc/dfir-orcForensics artefact collection tool for systems running Microsoft Windows
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
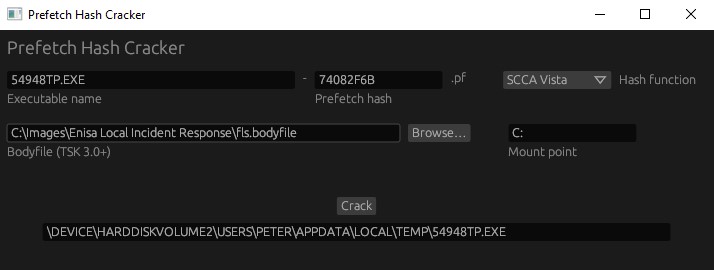 harelsegev/prefetch-hash-cracker
Brute-force tool that recovers full executable paths from Windows prefetch hashes using bodyfiles, supporting XP, Vista, and 2008 hash functions for…
 security-onion-solutions/security-onion
Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781