
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
digital-forensicsforensicsincident-response+2
2.0k
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
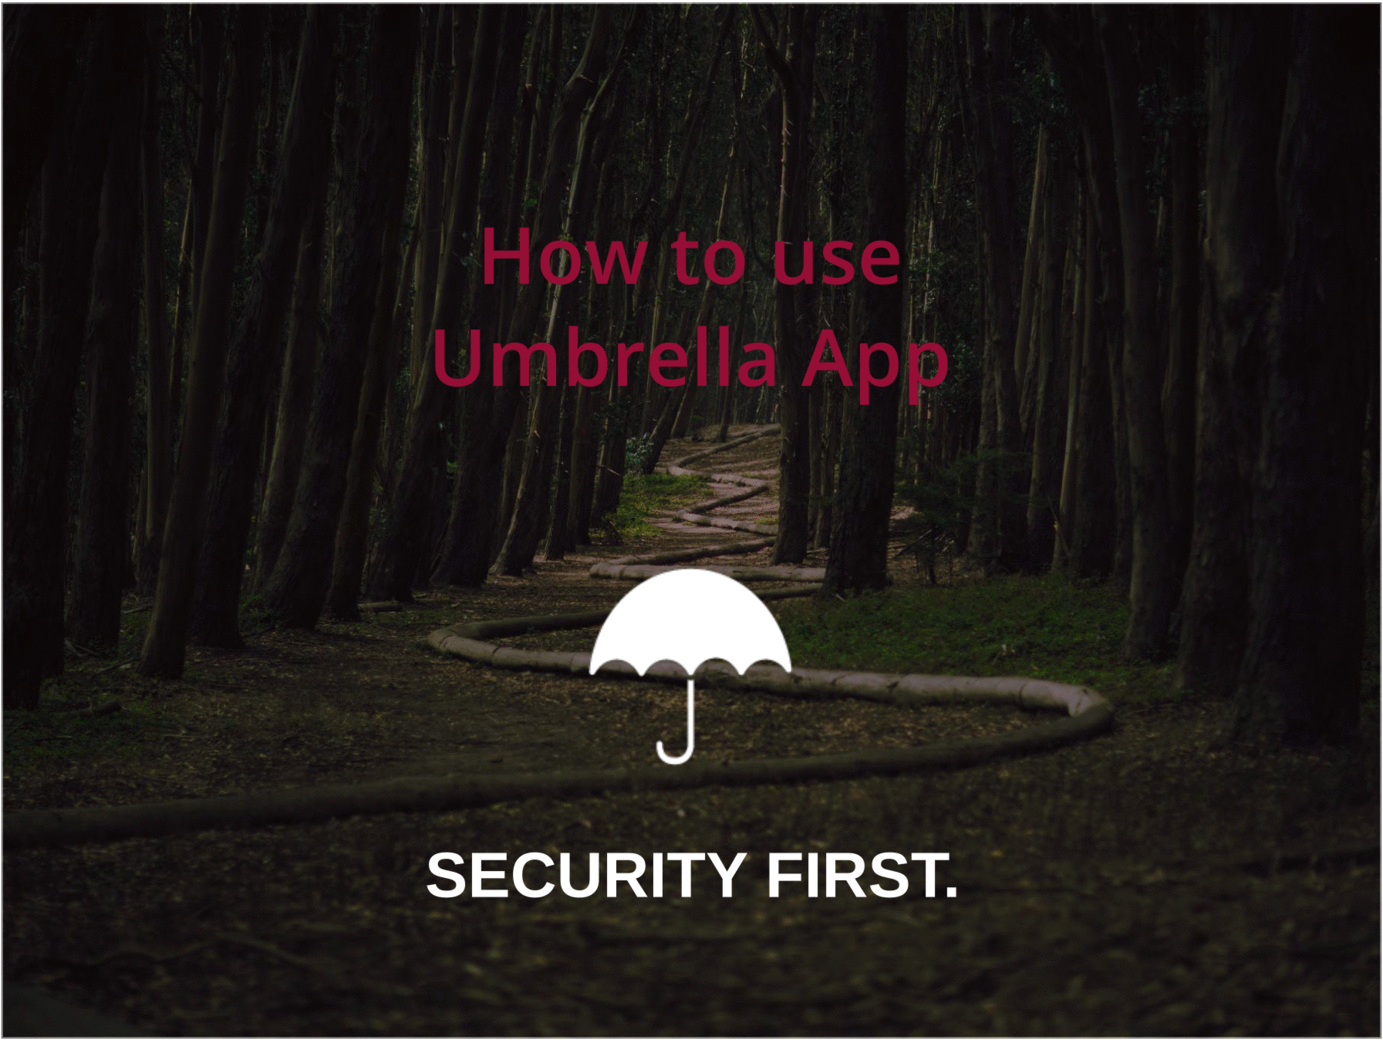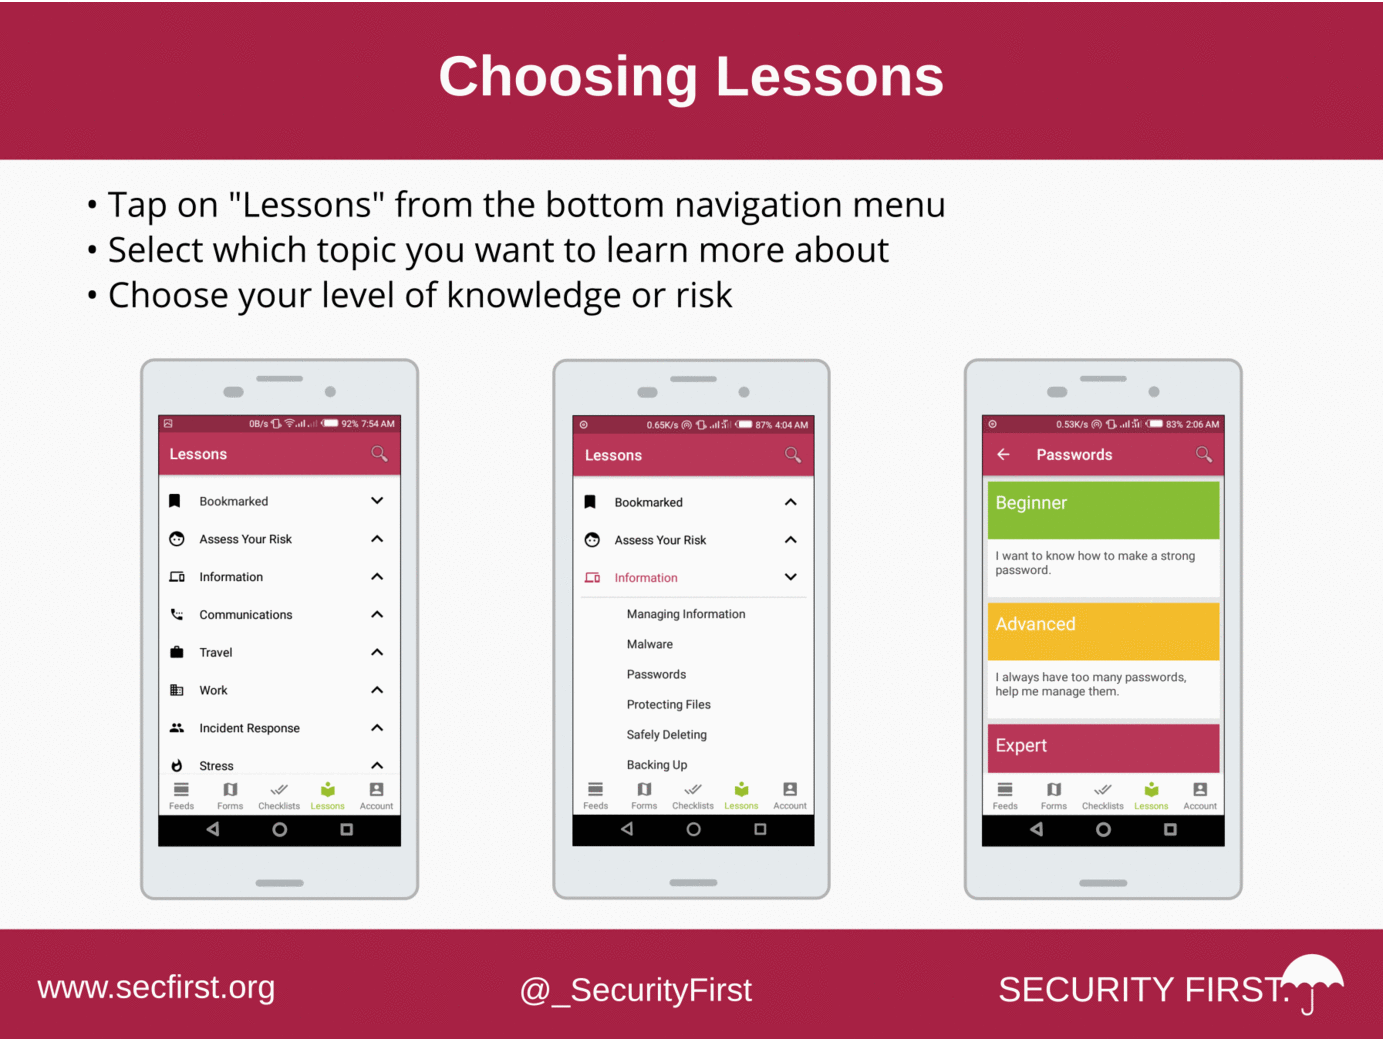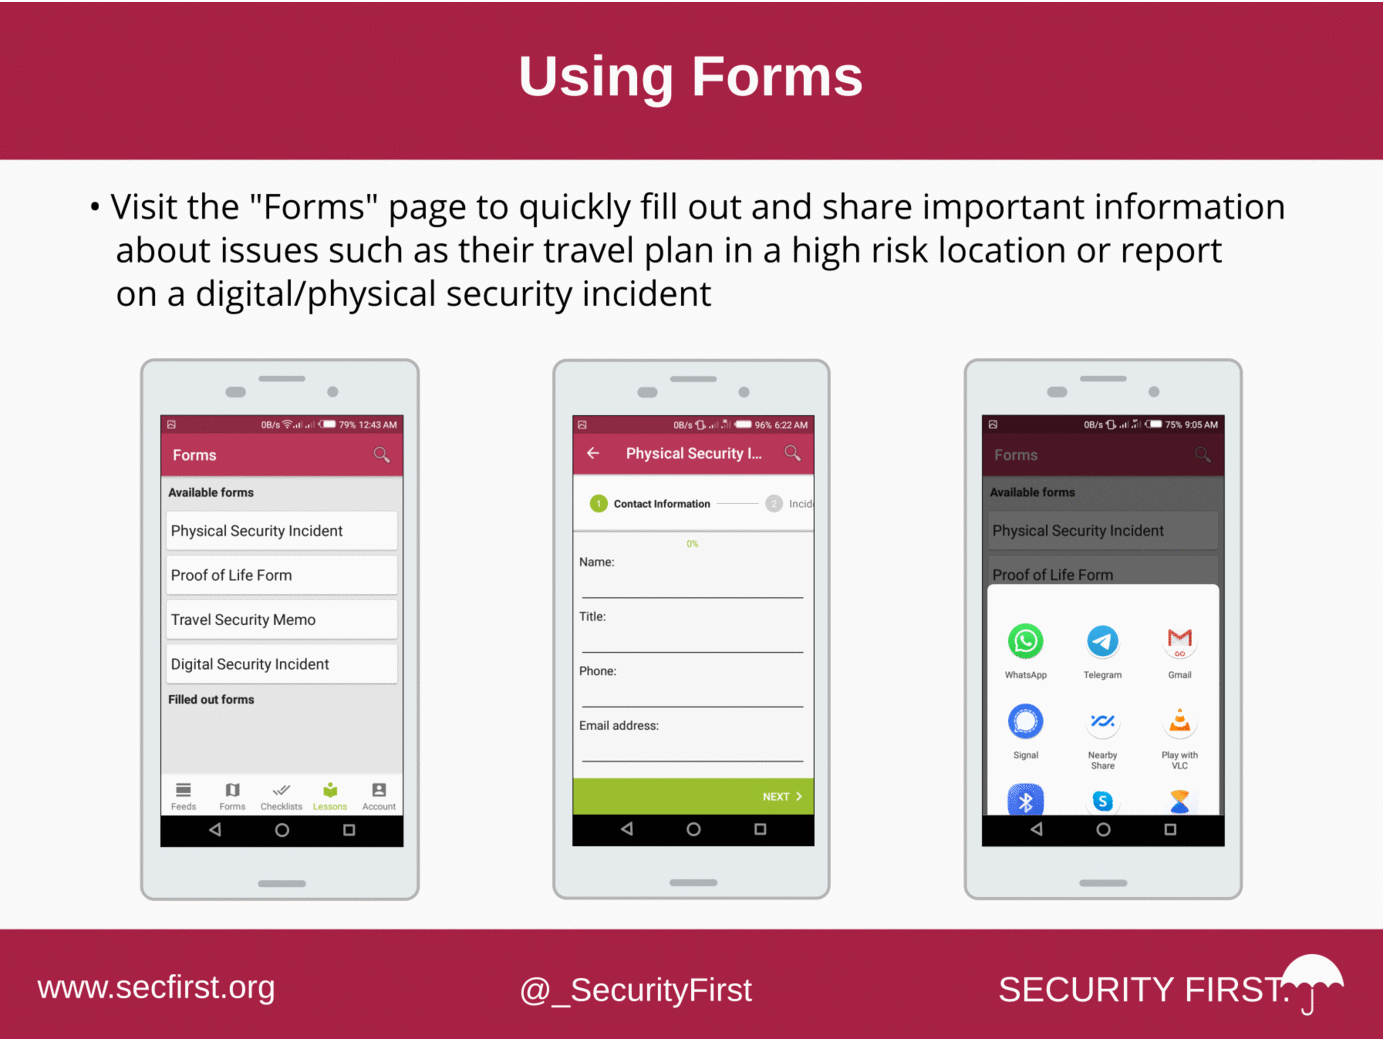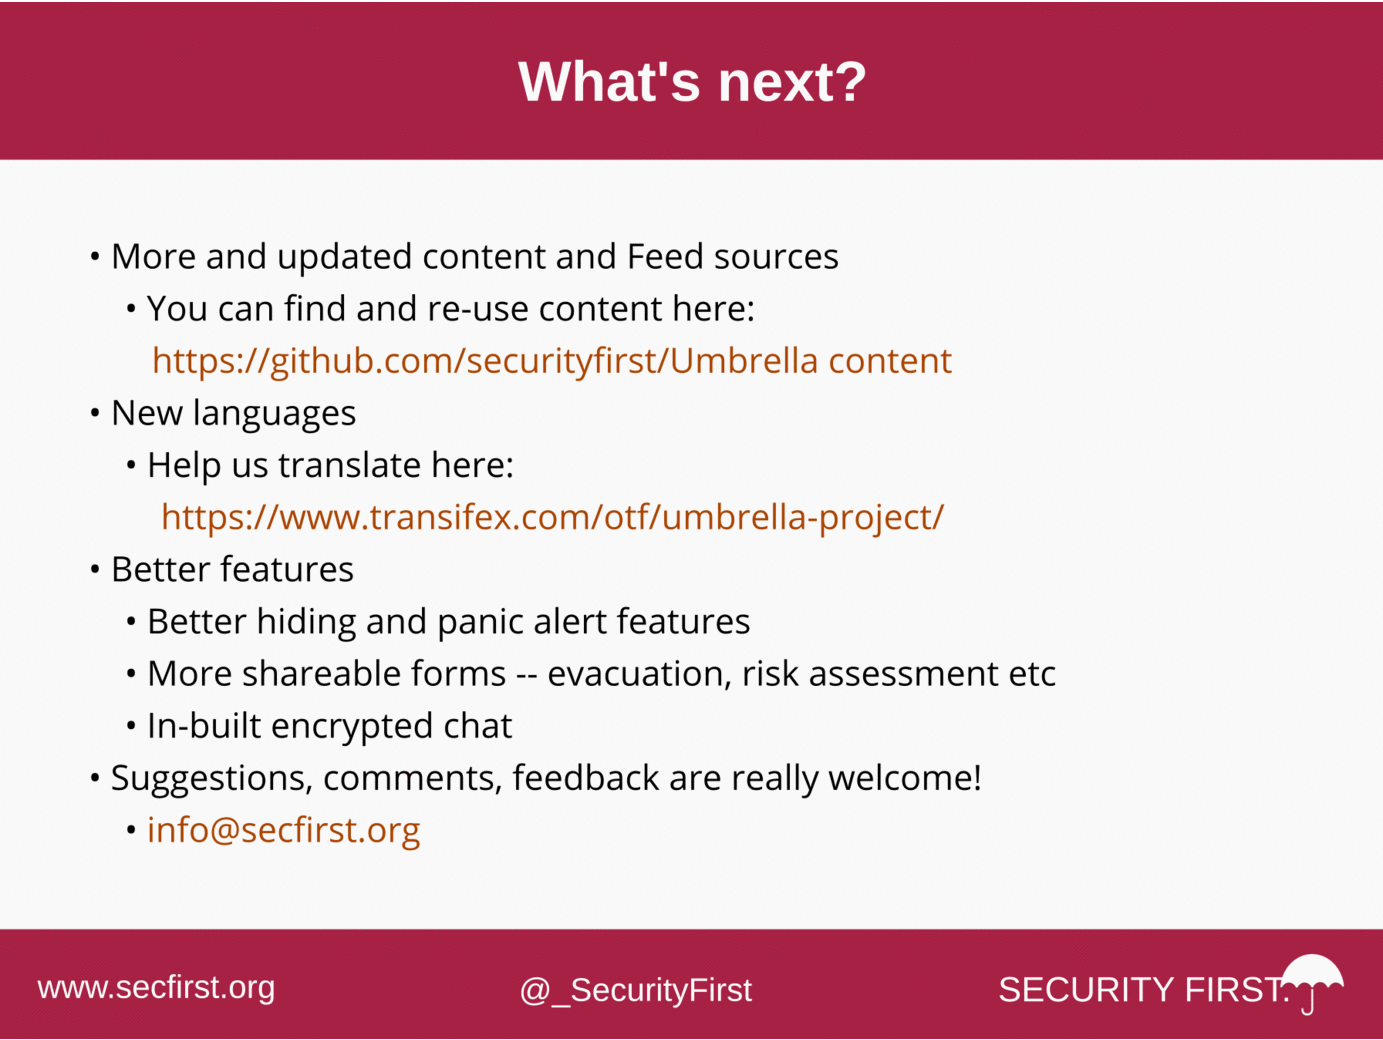 securityfirst/umbrella_android
Open source Android, iOS and Web app for learning about and managing digital and physical security. From how to send a secure message to dealing with…