
memdumper
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
digital-forensicsids-ips-evasioninformation-gathering+4
1
cenobyte-vincit/memdumperAbuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
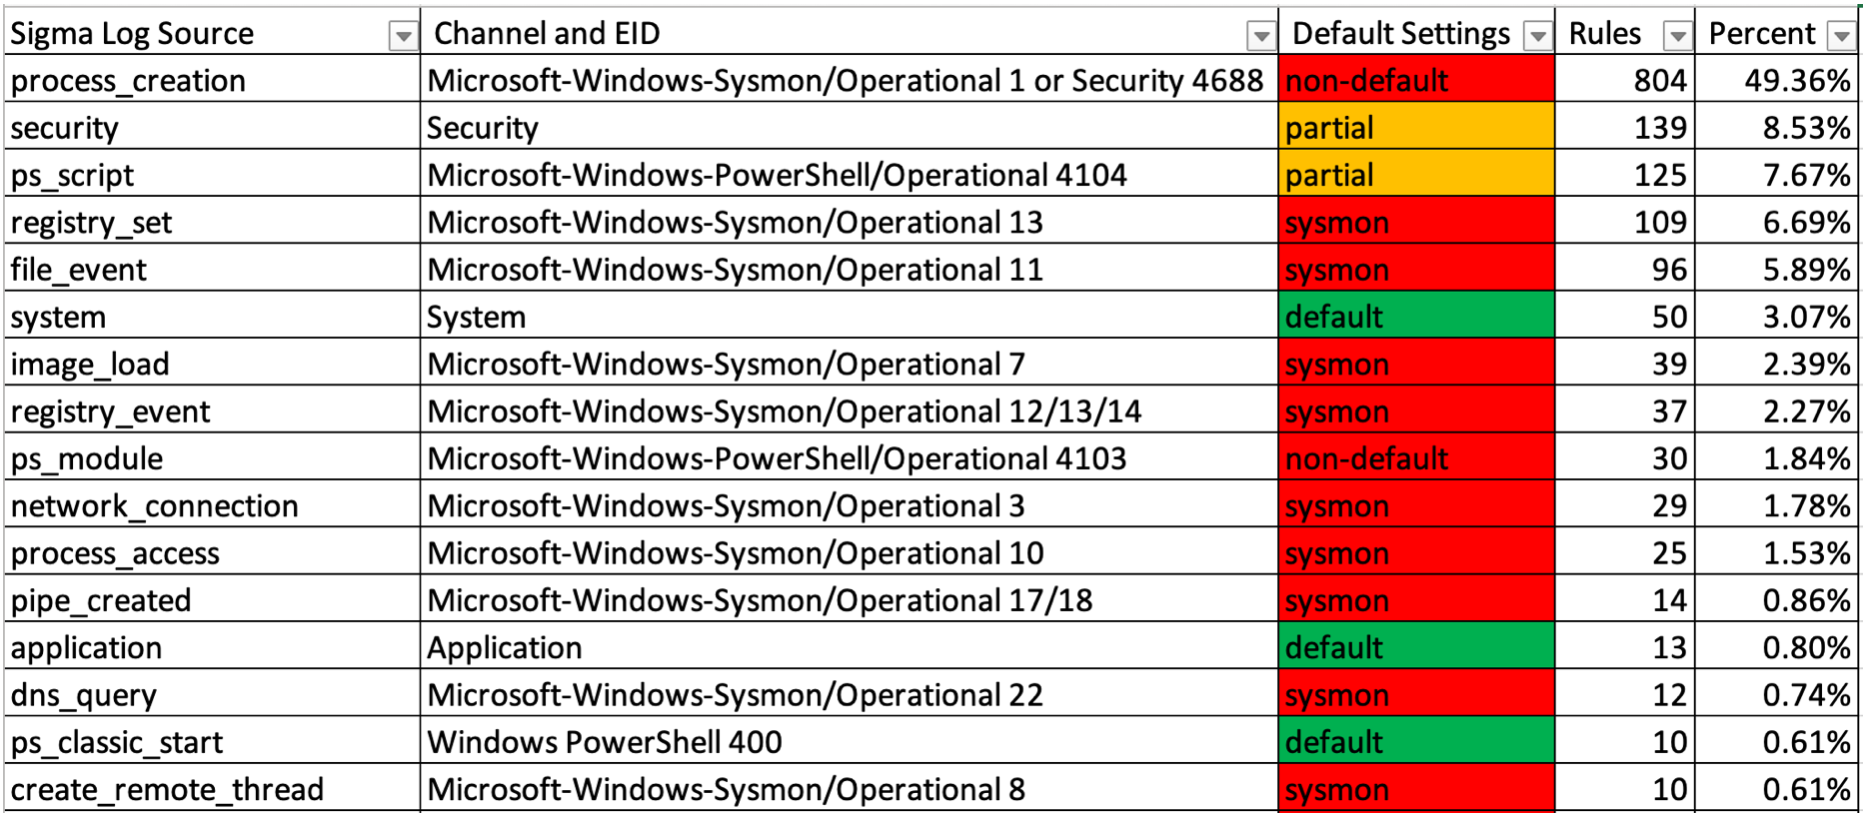 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 ssrajadh/sentrysearch
Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
 spieglt/whatfiles
Log what files are accessed by any Linux process