

ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
990
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
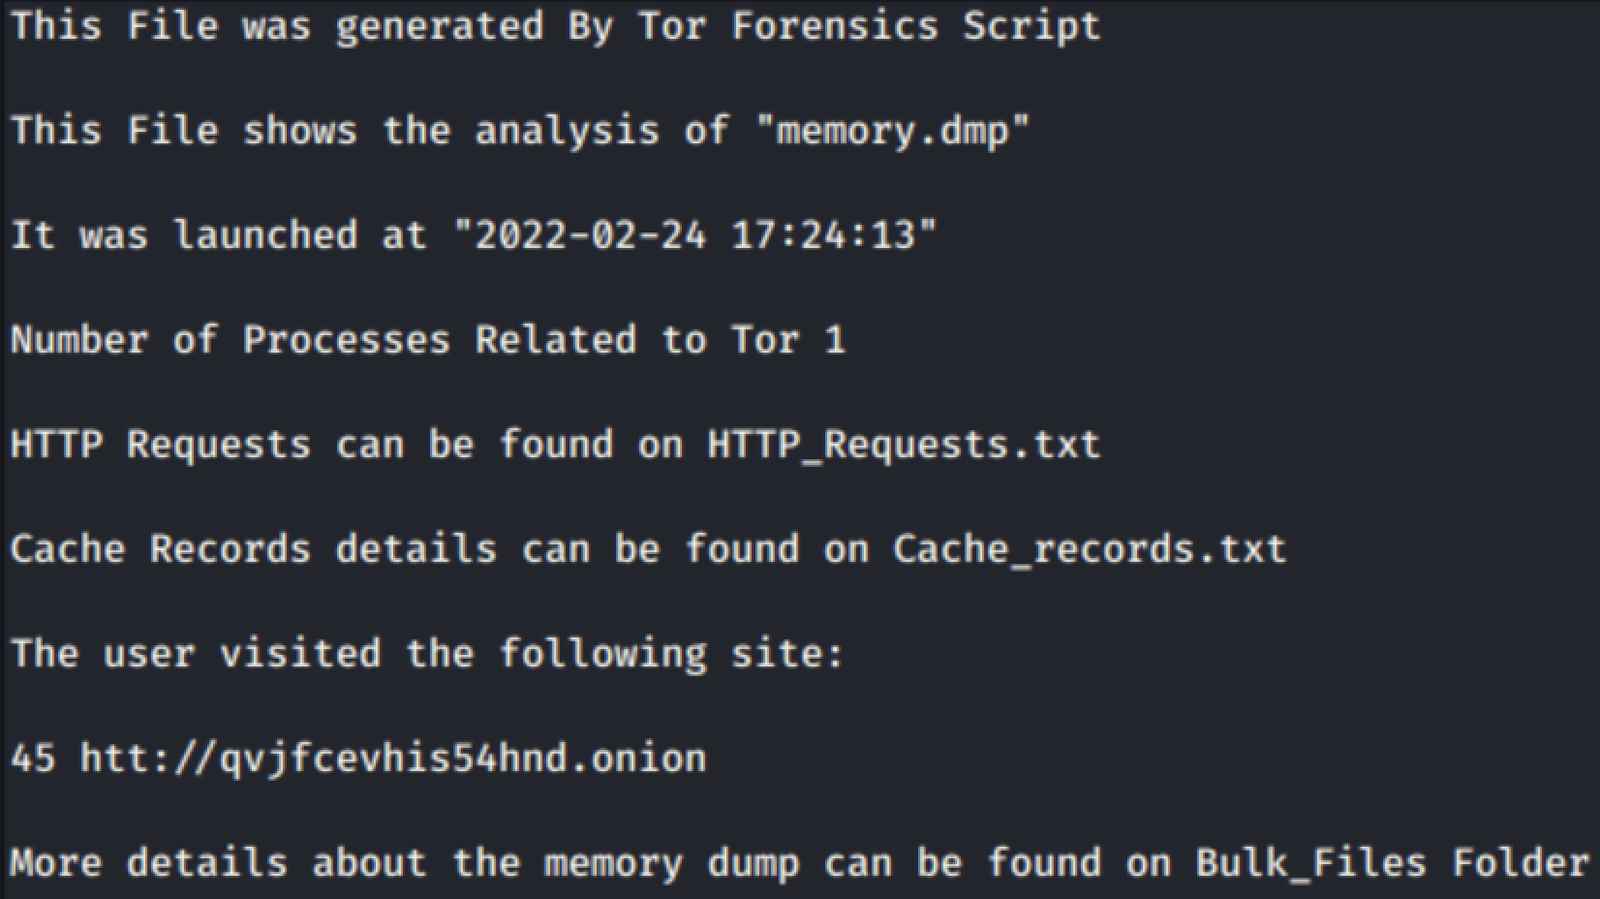 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
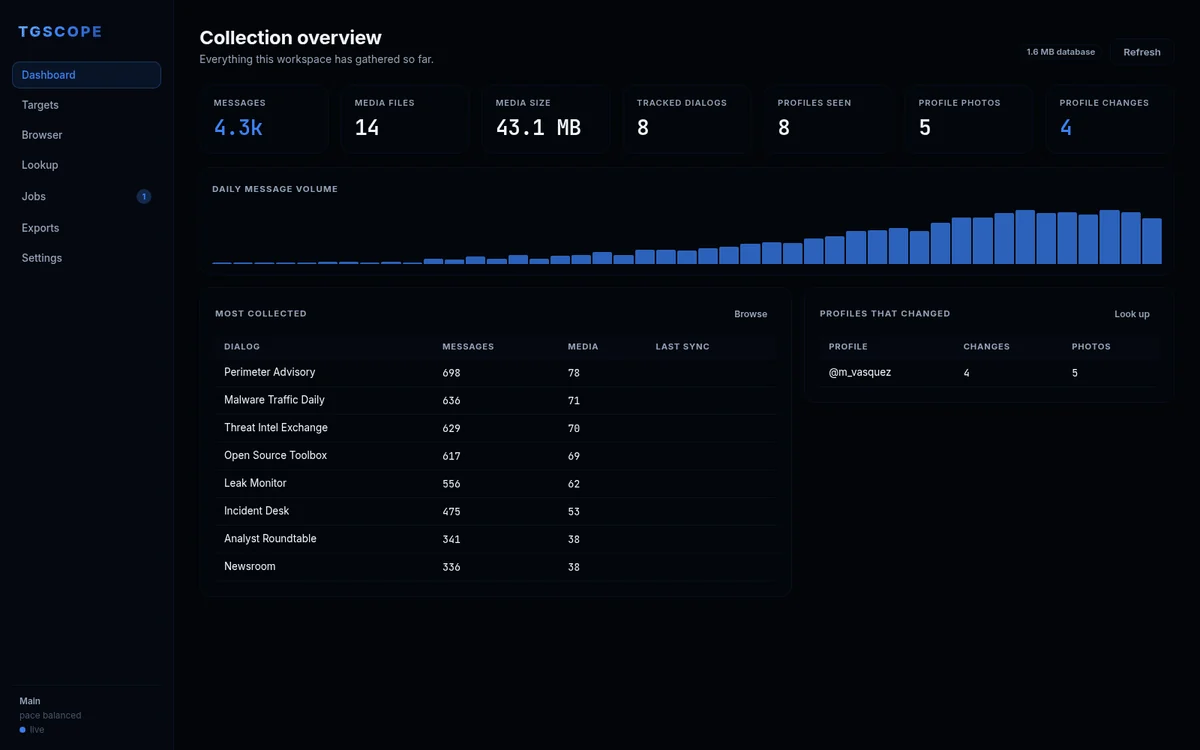 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
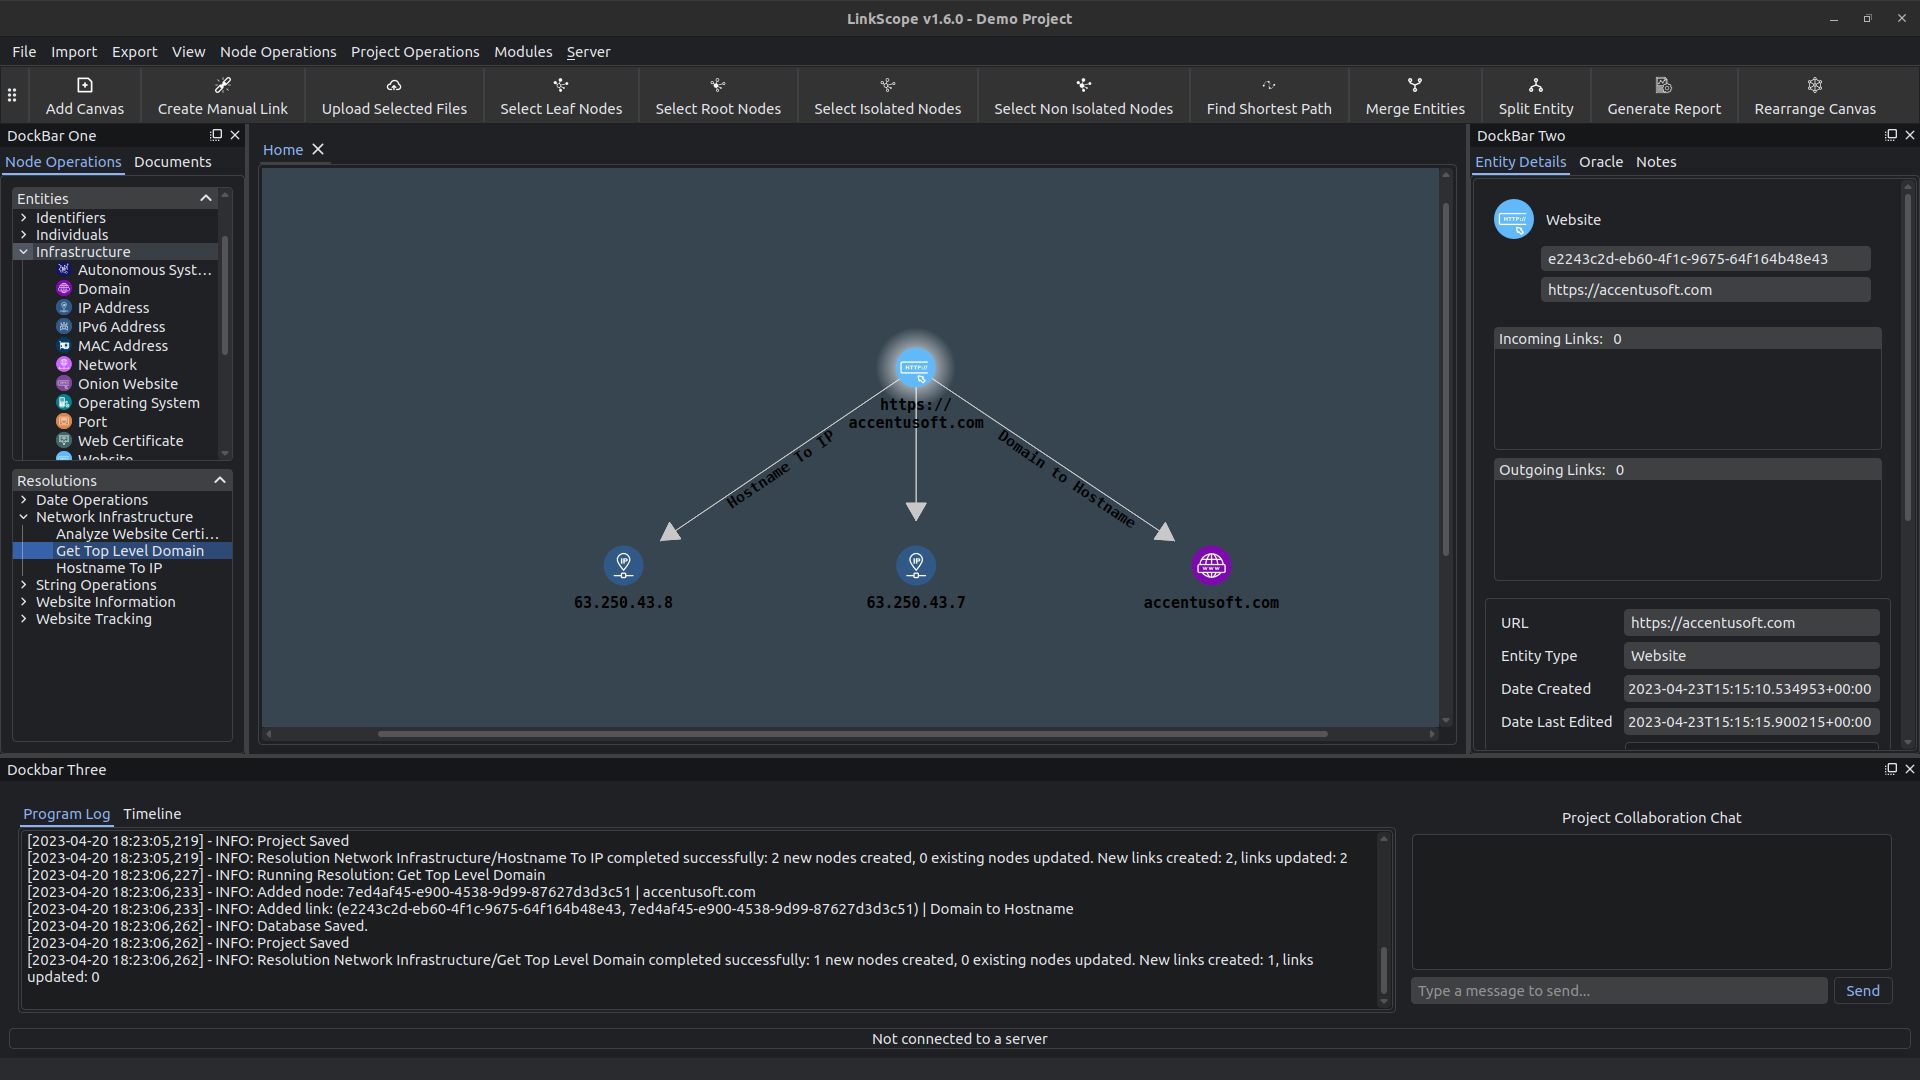 accentusoft/linkscope_client
Repository for the LinkScope Client software.


 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.
 c0decave/pdfgrab
Tool for searching pdfs withthin google and extracting pdf metadata
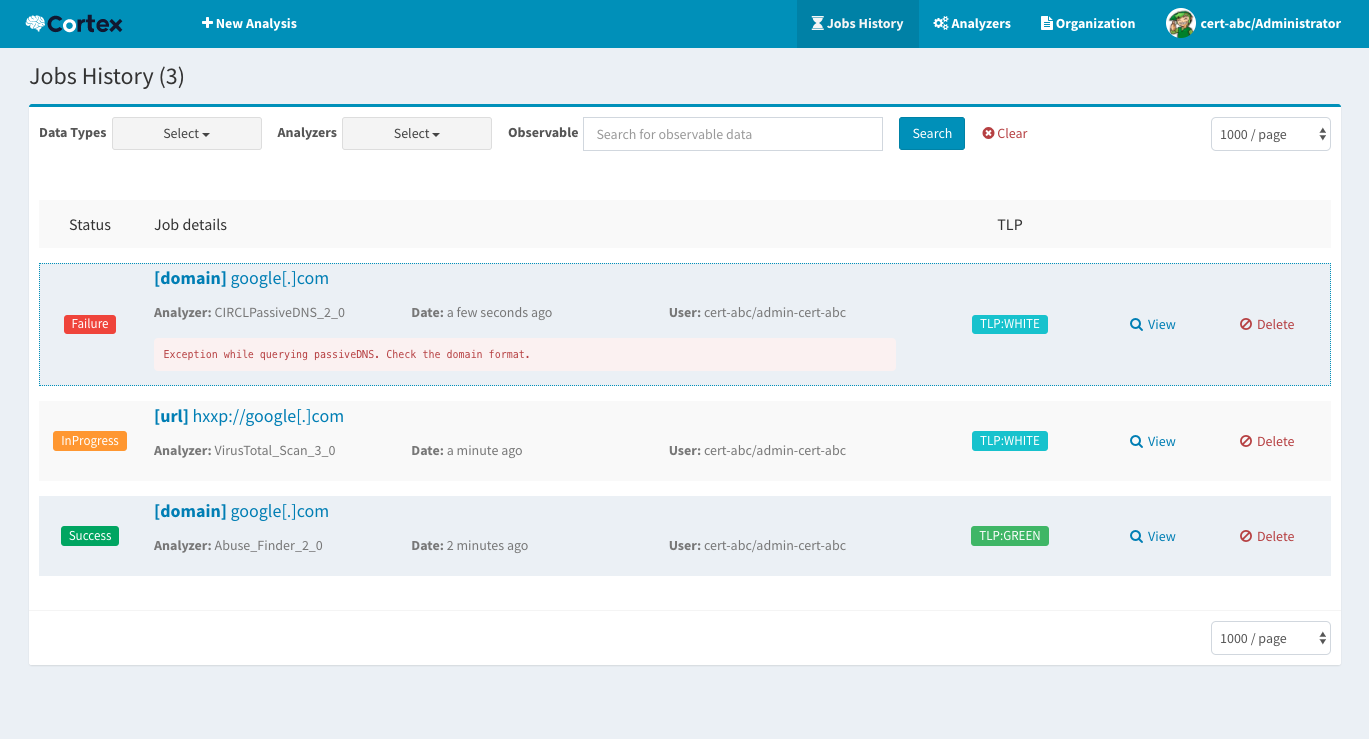 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
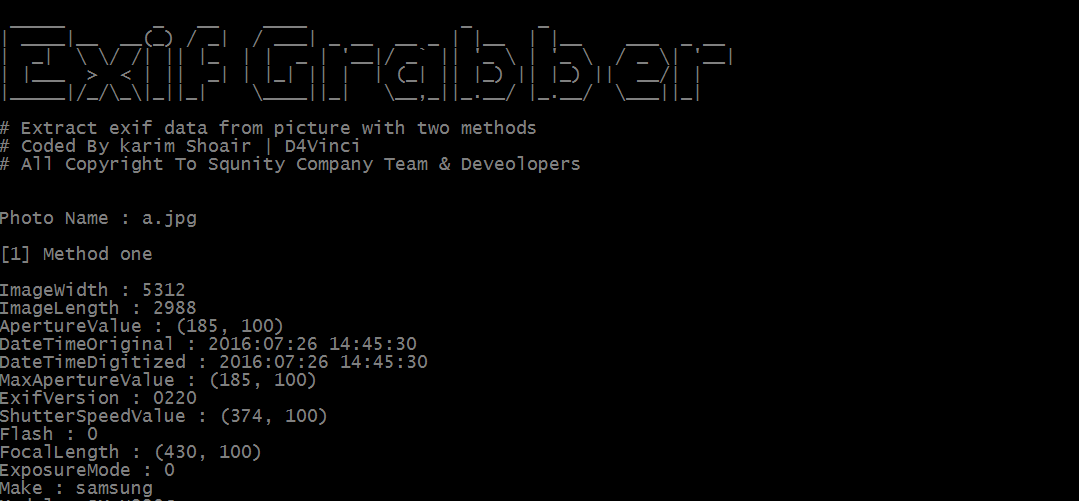 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
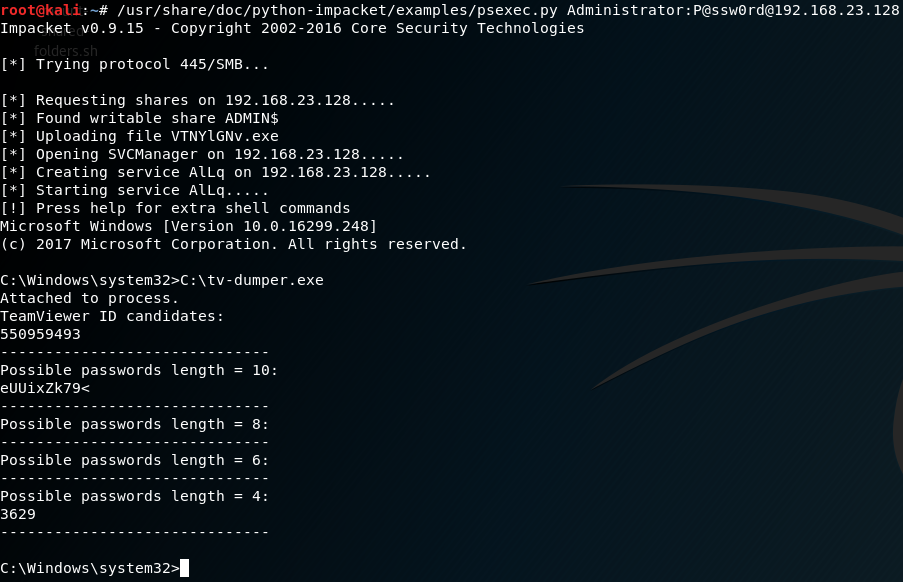 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.
 destiny-creates/goxlr-malware-family
Malware analysis from the domain goxlr.net
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping