
HashPrint
 tahaqaisar/hashprint
CLI forensic tool that identifies 90+ hash algorithms (MD5, bcrypt, SHA256) from single values, files, or recursive directory scans, with JSON, YAML,…
cryptographydigital-forensicsforensics+3
tahaqaisar/hashprintCLI forensic tool that identifies 90+ hash algorithms (MD5, bcrypt, SHA256) from single values, files, or recursive directory scans, with JSON, YAML,…
 masriyan/cve-2026-85097
Detection, verification and incident-response toolkit for CVE-2026-85097: remote Bricksforge assessment, log IOC hunting, filesystem implant audit,…
 a3igner/plex-codec-cache-implant
Incident write-up: unsigned .so in the Plex Media Server codec cache executes a dropper on every transcode (CVE-2026-96656) — IOCs, STIX, YARA
 w116tjb/plex2shell-windows-hunt
Plex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script
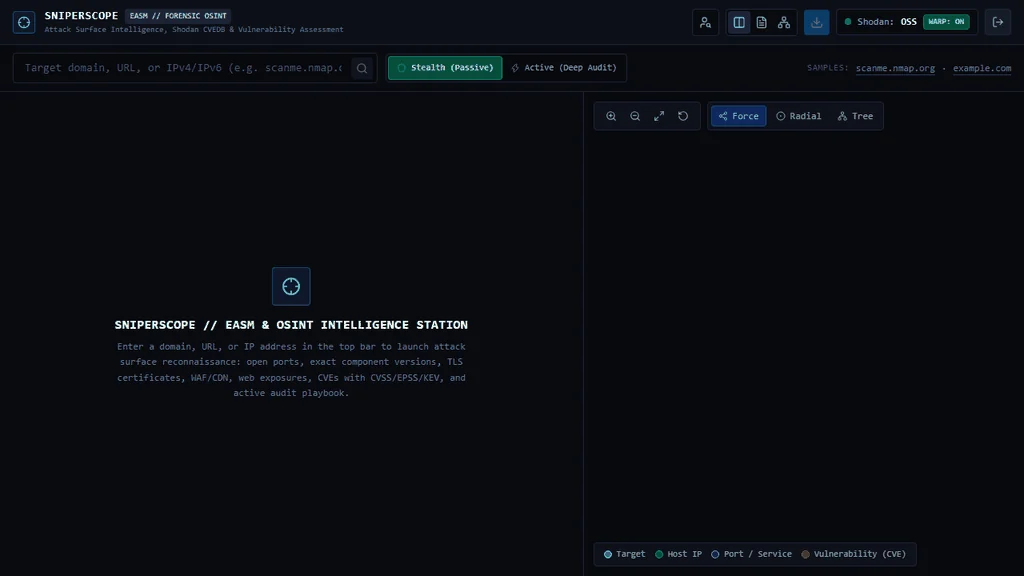 kamehameha-ctrl/sniperscope
External attack surface management workstation that correlates DNS, certificate transparency, Shodan, CVEDB, TLS and OSINT data into risk-scored…
 ctsit/redcap_cve_2026_90817_scan
A read-only, passive scanner that checks a REDCap host for exposure to and compromise by **CVE-2026-90817** — the unauthenticated survey-endpoint…
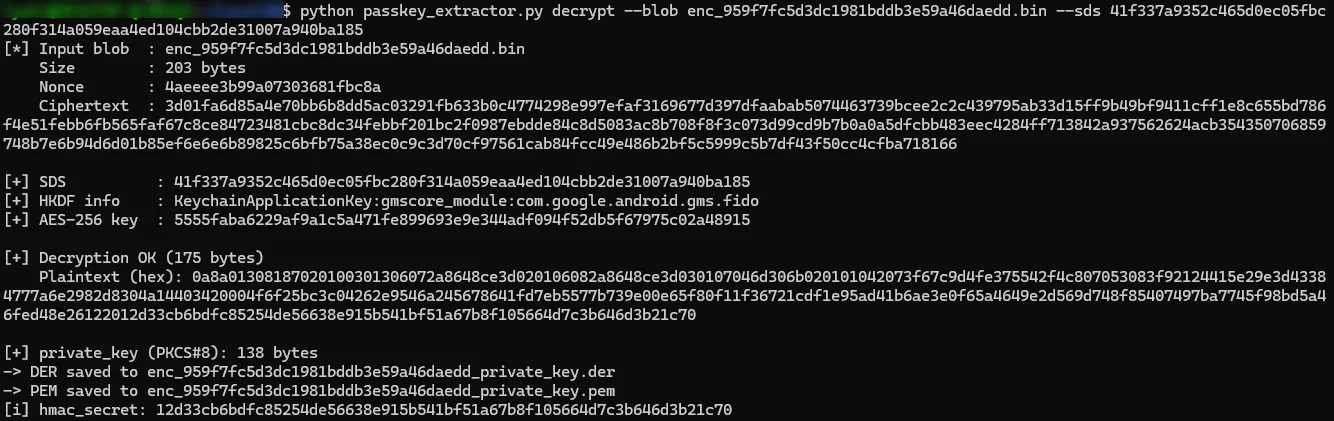 0rcruxe/pass-ta-key
PoC that extracts the Google Password Manager Security Domain Secret from Chrome process memory and decrypts synced GPM passkey ECDSA P-256 private…
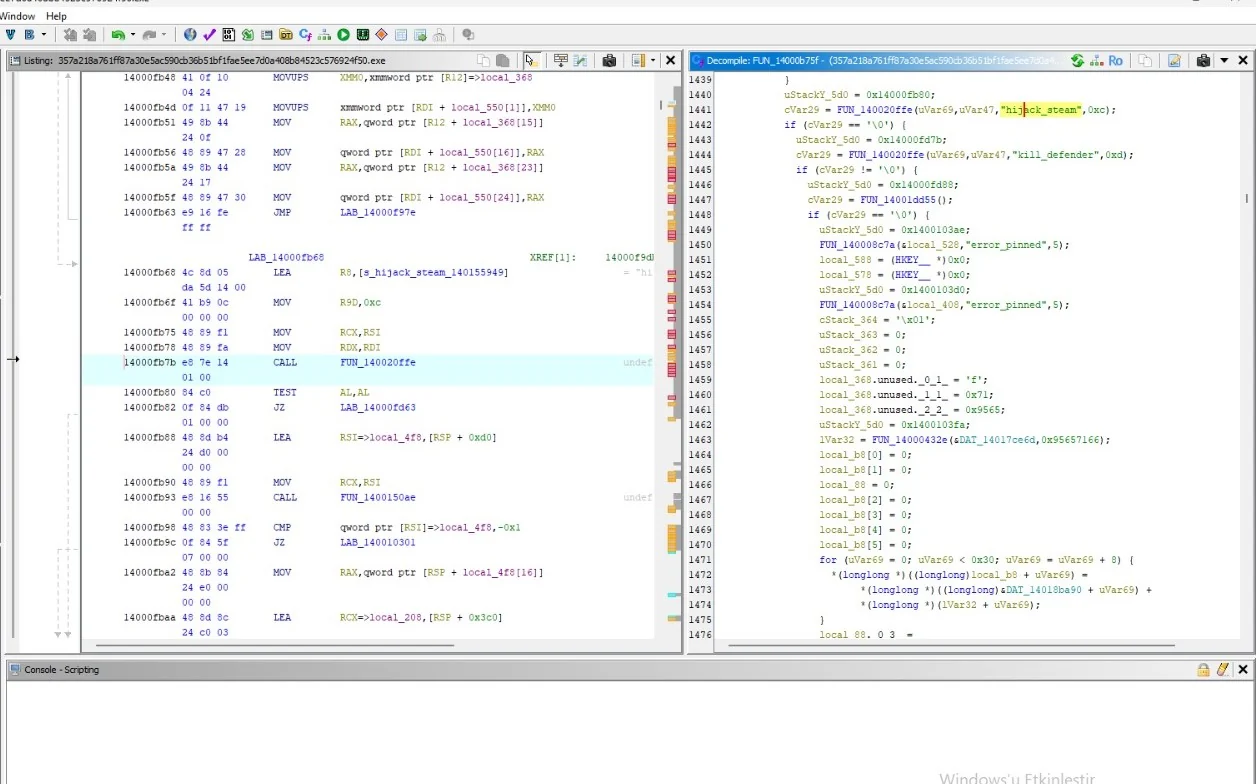 kaandemir993/rusty-stealer-keylogger-screen-streaming-service-persistence-defender-evasion-analysis
Reverse engineering Rusty Stealer: A Rust-based RAT featuring advanced keylogging, live screen streaming, and aggressive defense evasion (killing…
 kowntaewook/mcptrace
Volatility 3 plugin that carves MCP/JSON-RPC message candidates from Windows and Linux memory dumps, preserving raw bytes, addresses, and SHA-256 for…
 bb1nfosec/information-security-tasks
Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 happyhackingspace/claude-code-backdoor-check
Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 giordanosconti/icloudkitextractor
Experimental .NET/WPF forensic toolkit for iCloud auth, CloudKit/MMCS backup download, and Octagon/PCS recovery (ADP, Recovery Key, Lockdown Mode).…
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…