
malware-analysis-fake-hwmonitor
 dmitry-matvienko/malware-analysis-fake-hwmonitor
Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
defensive-toolsdigital-forensicseducation+6
dmitry-matvienko/malware-analysis-fake-hwmonitorTechnical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
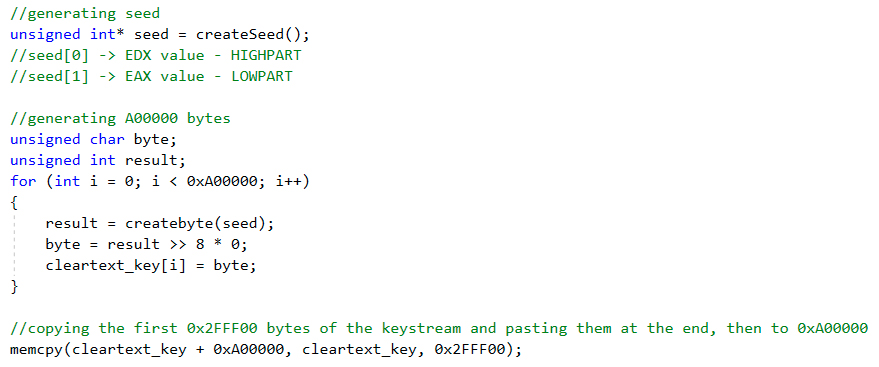 reecdeep/hivev5_keystream_decryptor
bad stuffs by bad guys
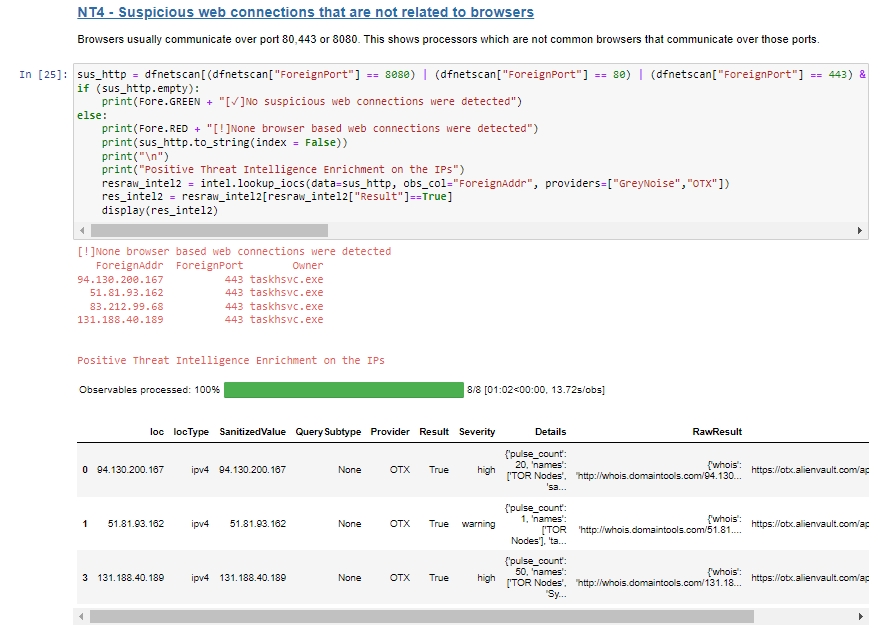 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 gmikisilva/cve-2024-33901-proofofconcept
Short program that demonstrates the vulnerability CVE-2024-33901 in KeePassXC version 2.7.7
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 opensourcemalware/vercel-april2026-incident-response
This is an incident response playbook we created for the Vercel April 2026 compromise
 crocodyli/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.