

hexvero
 maximilianfeix/hexvero
Know what changed inside your app: inspect Electron apps and binaries, trace findings to file and line, compare releases. Locally, without executing…
ai-securityandroid-securitybinary-analysis+9
8
maximilianfeix/hexveroKnow what changed inside your app: inspect Electron apps and binaries, trace findings to file and line, compare releases. Locally, without executing…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
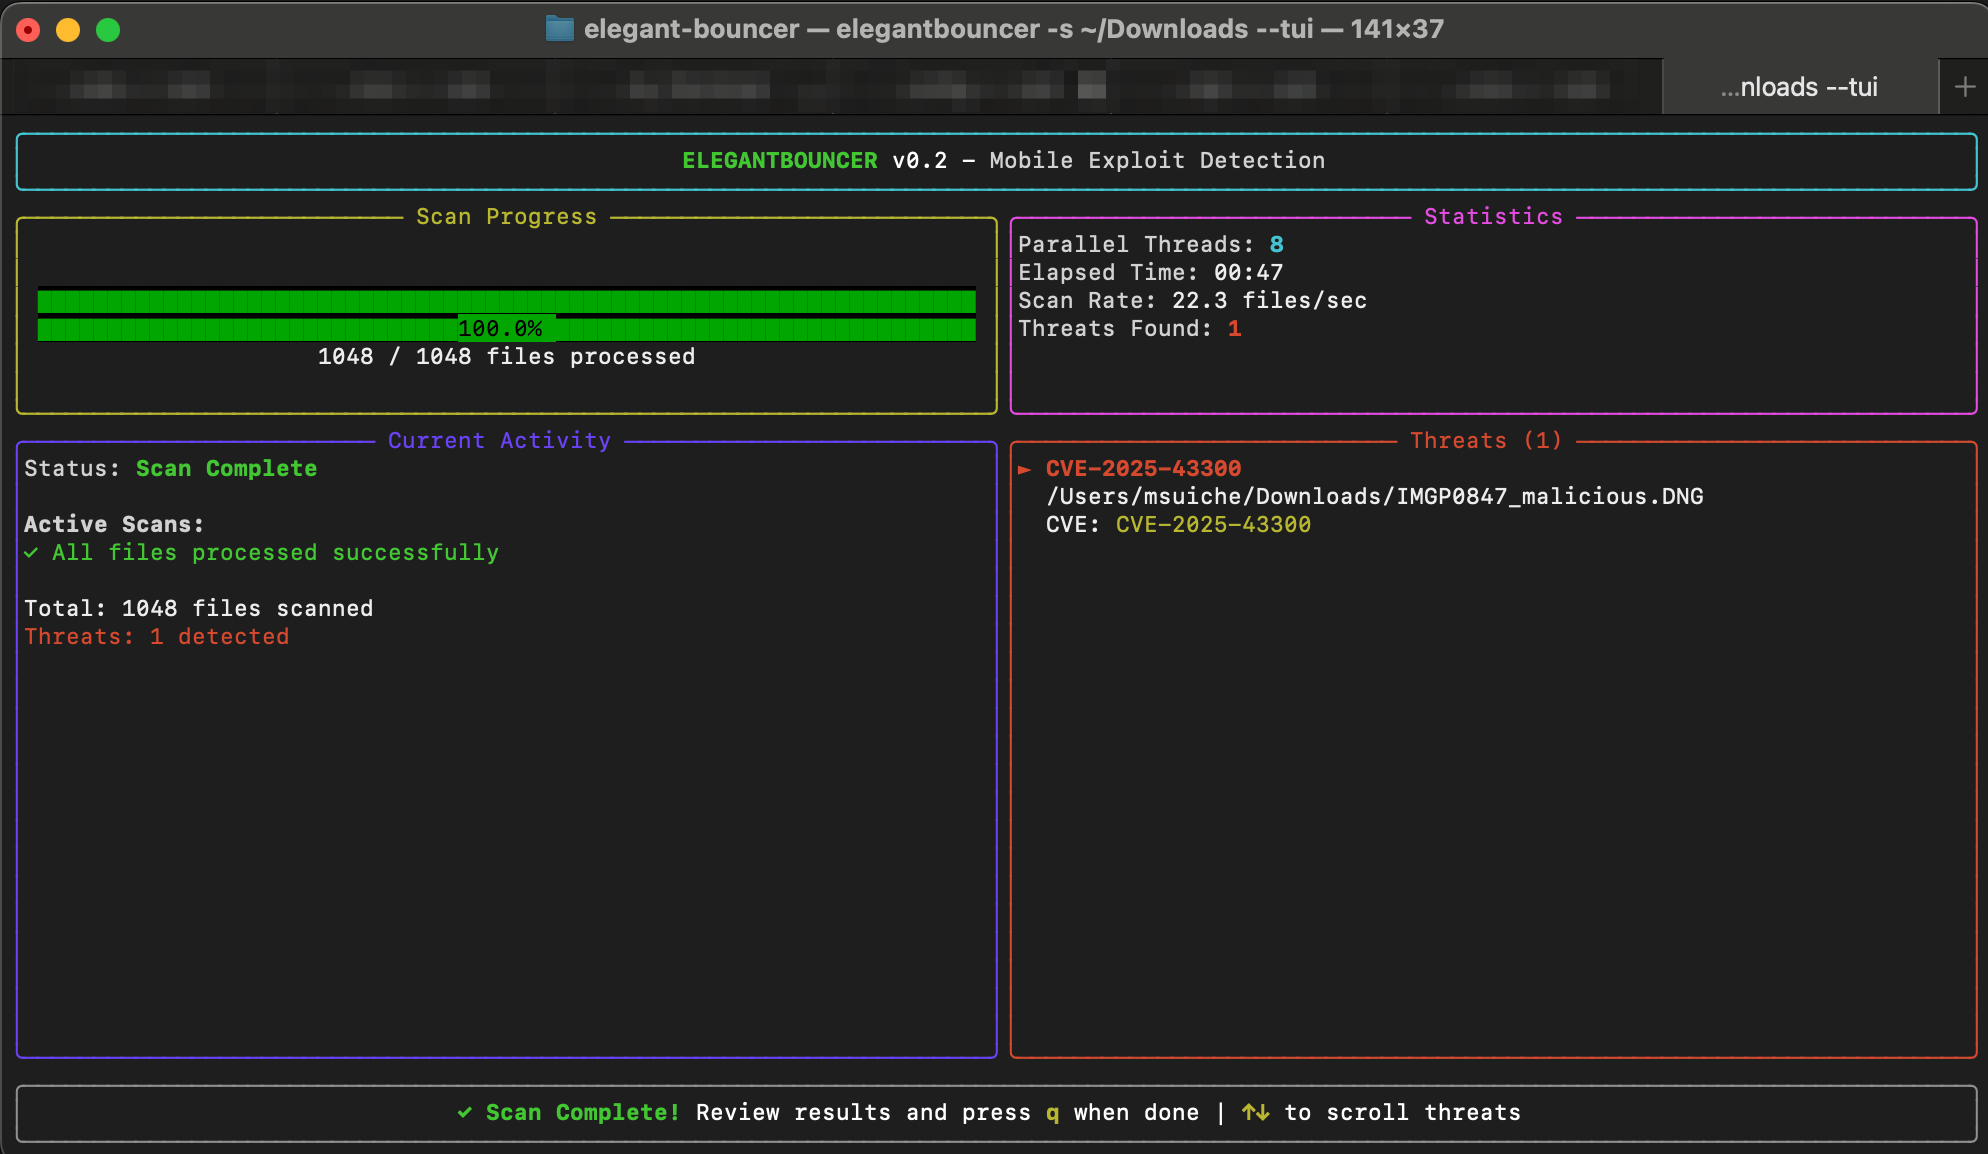 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
 simsong/bulk_extractor
This is the development tree. Production downloads are at:

 jeffssh/cve-2021-30860
Collection of materials relating to FORCEDENTRY
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 mikeroyal/digital-forensics-guide
Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux