

plex2shell-windows-hunt
 w116tjb/plex2shell-windows-hunt
Plex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script
defensive-toolsdigital-forensicsincident-response+4
w116tjb/plex2shell-windows-huntPlex2Shell (CVE-2026-96652/54/55/56) IOC/IOA dossier and read-only Windows hunt script
 evyatarmeged/stegextract
Bash script that extracts trailing data, embedded files, and hidden strings from PNG, JPG, and GIF images using magic numbers and hexdump analysis.
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 withsecurelabs/macostriagecollectionscript
Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
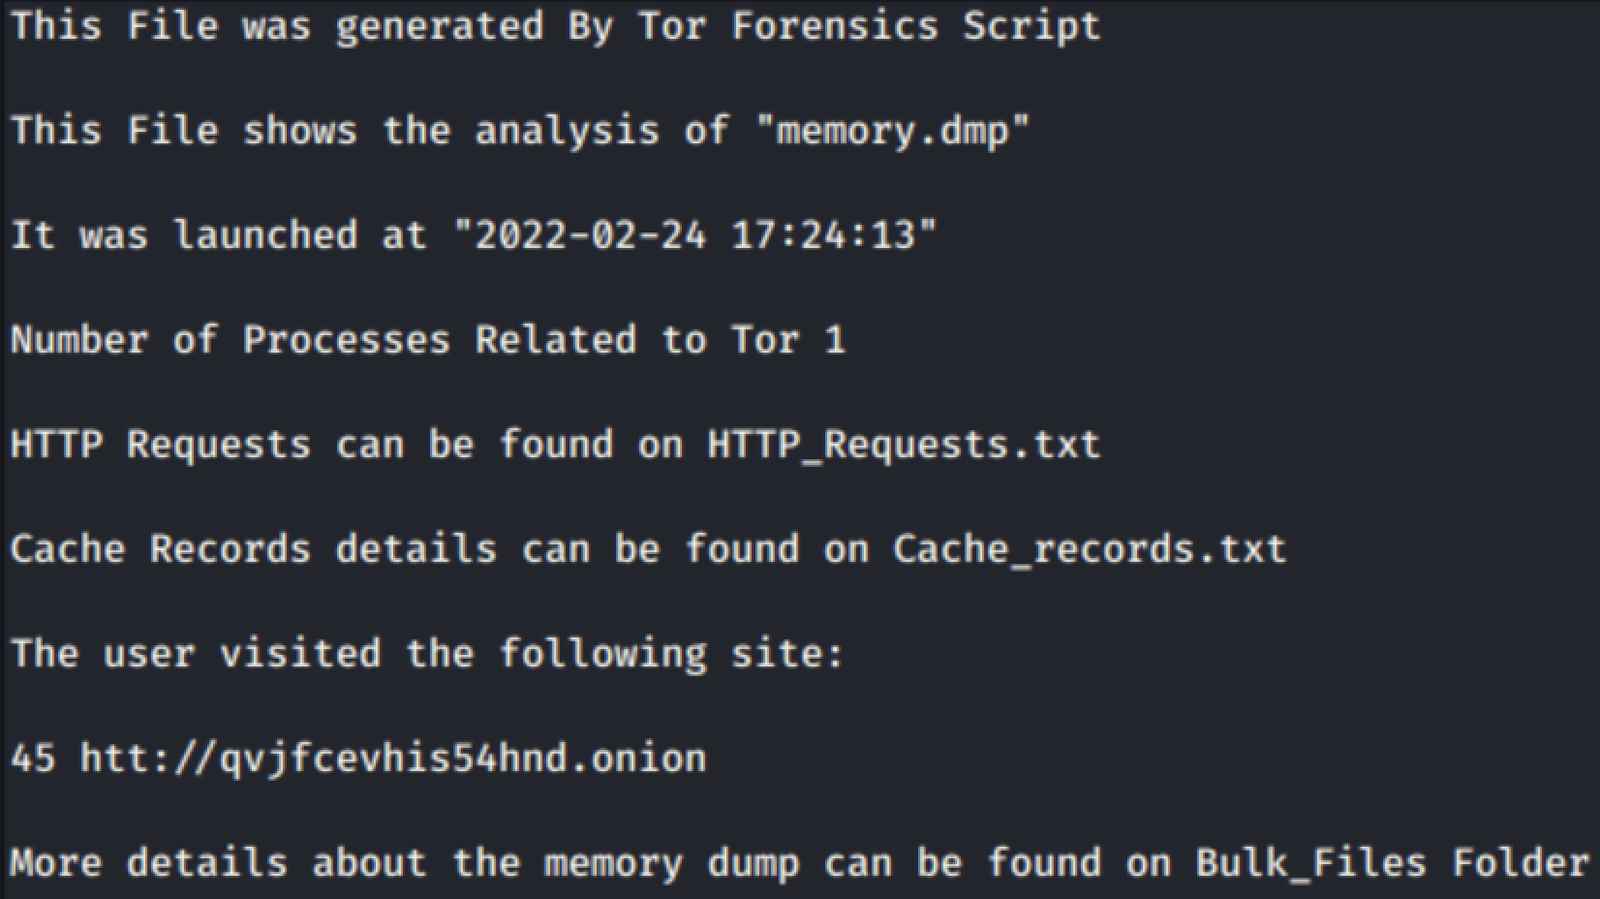 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 0xcomposure/fftstegpic
A python script for digital image steganography using Fast Fourier Transform.
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 nazywam/autoit-ripper
Extract AutoIt scripts embedded in PE binaries
 corelight/log-add-http-post-bodies
Add POST body excerpt to Bro's HTTP log
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR


 d4vinci/chrome-extractor
Python script that will extract all saved passwords from your google chrome database on windows only