SOC335---CVE-2024-49138-Exploitation-Detected

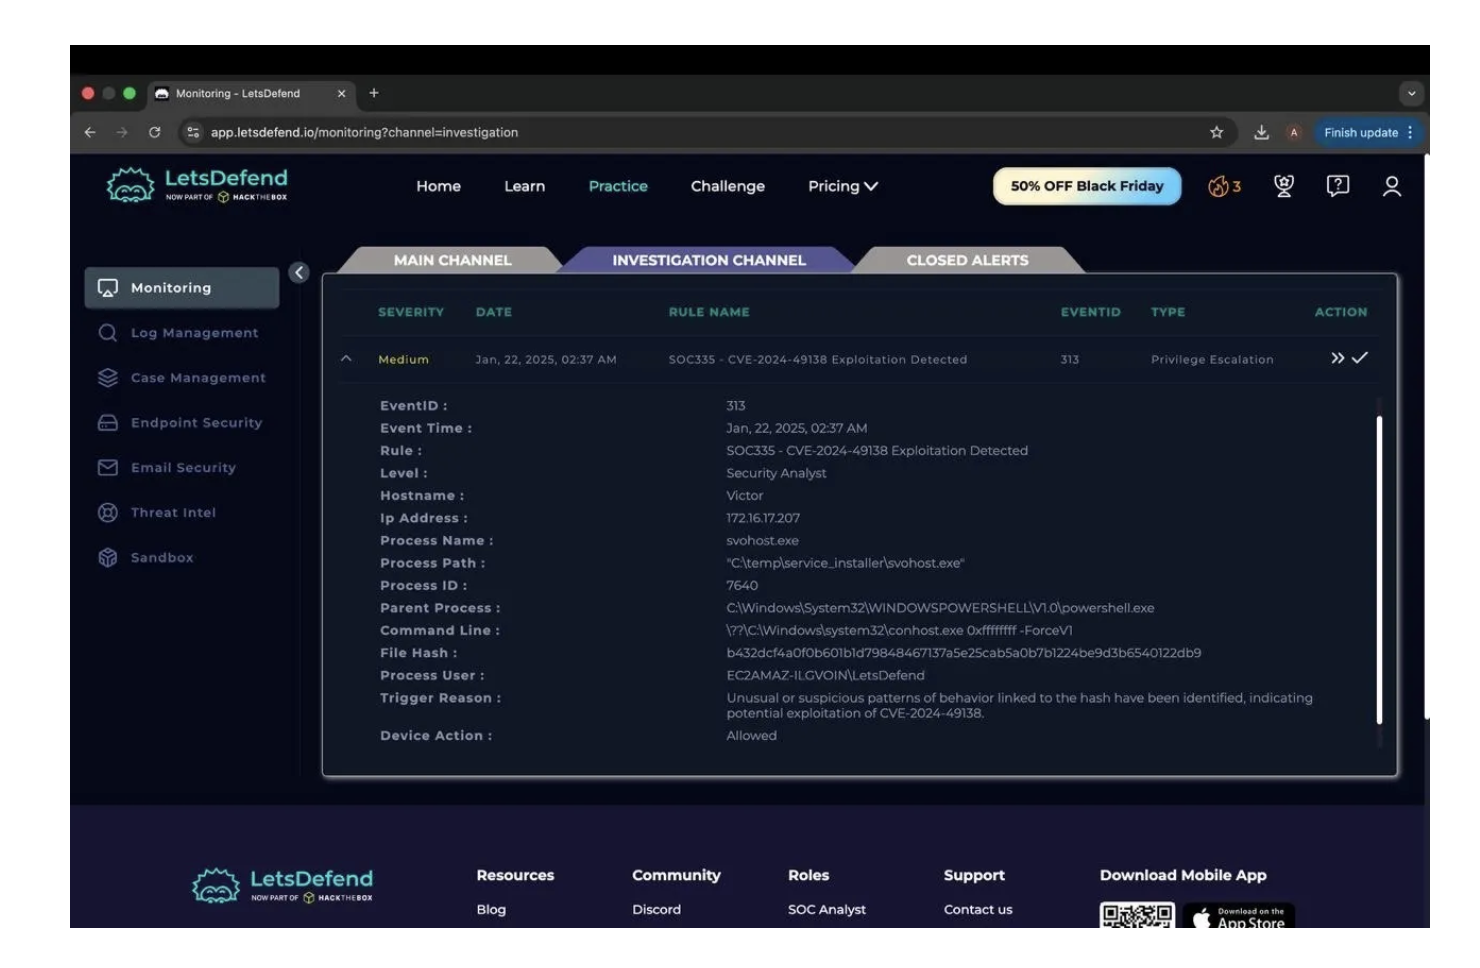
SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.

Incident Response Documentation Platform

Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

SOC investigation of CVE-2024-49138 exploitation involving brute-force activity, PowerShell execution, malicious payload analysis, privilege…

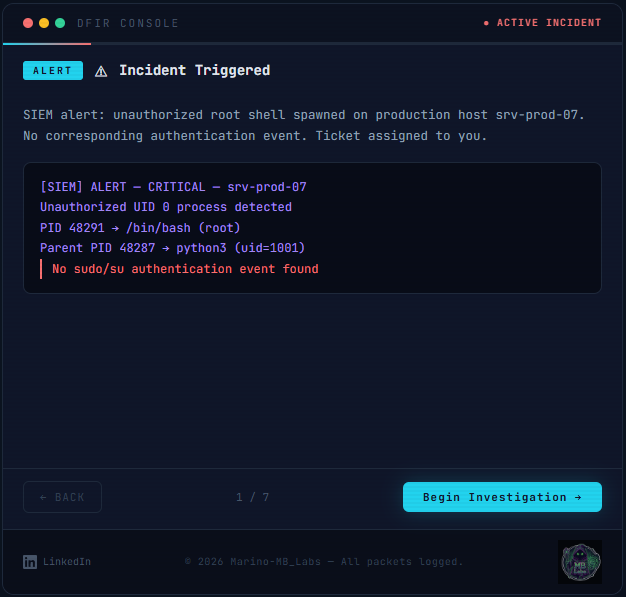
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.


A list of covert channels and steganography/steganalysis resources (books, papers & tools)

A python script for digital image steganography using Fast Fourier Transform.

Repository to index useful tools for CTF's

All-in-one Image Steganography Toolkit for CTFs & Forensics

Network forensics writeup + tooling for a TryHackMe DFIR challenge: reverses a hex→Base64→XOR exfiltration chain from PCAP traffic, then recovers a…

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

Writeup for the DEF CON 30 badge challenge

Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.