
Config-Extractors
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…
digital-forensicsencryption-decryption-toolsmalware-analysis+2
27
Extracts and decrypts malware configuration data from captured samples, automating C2 endpoint discovery, credential extraction, and indicator triage…

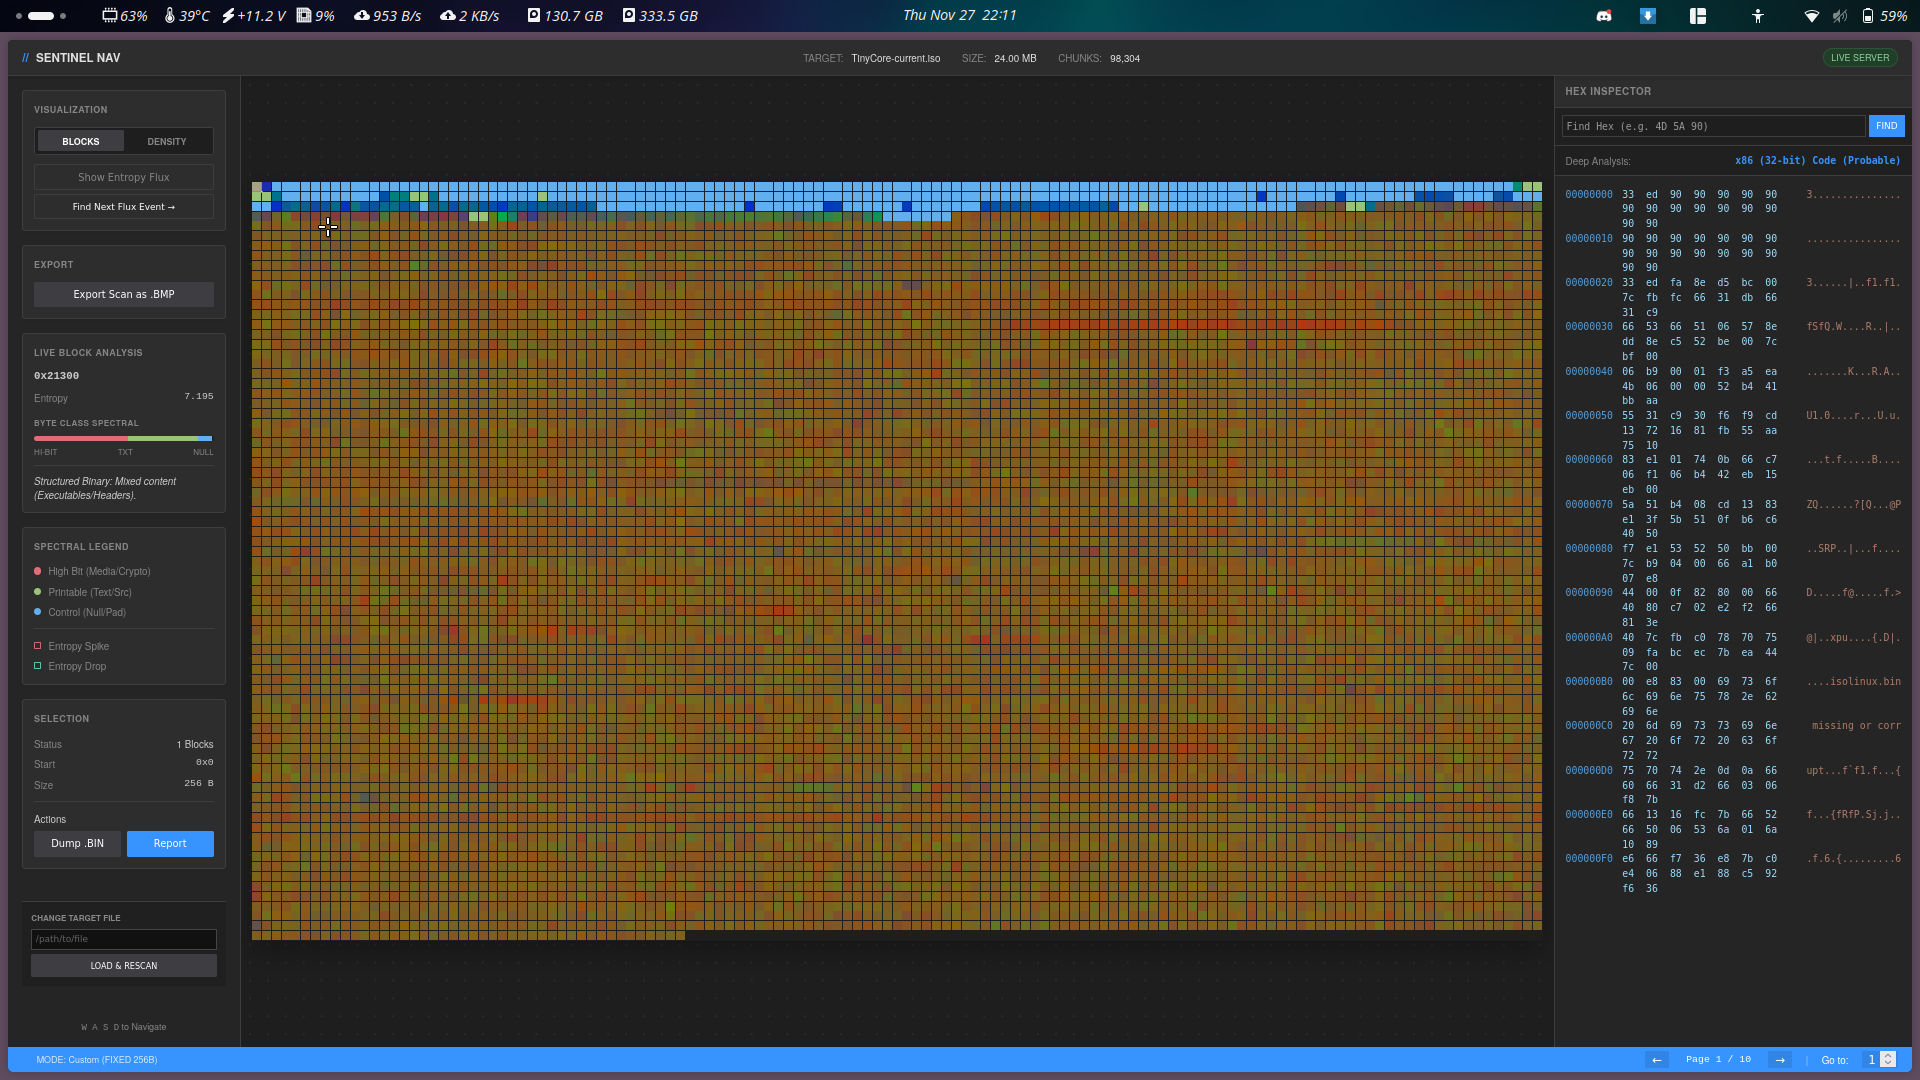
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.

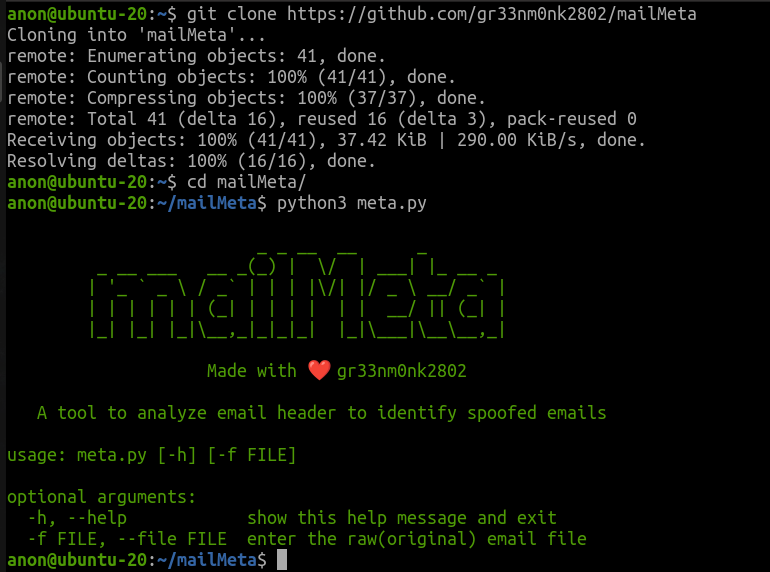
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.