
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
165 results
ADRecon preview

ADRecon

GitHubadrecon/adrecon

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
981
1 year ago
RemotePSpy preview

RemotePSpy

GitHubwithsecurelabs/remotepspy

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
defensive-toolsdigital-forensicsincident-response+3
196 years ago
ecdsa-private-key-recovery preview

ecdsa-private-key-recovery

GitHubbarnew-st/ecdsa-private-key-recovery

A cryptographic research tool for analyzing signature vulnerabilities
cryptographydigital-forensicsexploitation+1
2110 months ago
ESFang preview

ESFang

GitHubwithsecurelabs/esfang

ESF modular ingestion tool for development and research.
digital-forensicsforensicsincident-response+1
384 years ago
YellowKey-Bitlocker-CVE-2026-45585 preview

YellowKey-Bitlocker-CVE-2026-45585

GitHubneccie/yellowkey-bitlocker-cve-2026-45585

Manage BitLocker recovery keys, unlock encrypted drives, and monitor encryption status with this lightweight Windows utility.
data-recoverydigital-forensicsencryption-decryption-tools+1
1 month ago
walletool preview

walletool

GitHubqg5casz/walletool

Extracts cryptocurrency private keys and addresses from wallet.dat files for Bitcoin and Litecoin, enabling wallet recovery and forensic analysis.
cryptographydata-recoverydigital-forensics+2
52513 days ago
walletool preview

walletool

GitHubs4larie/walletool

A utility for extracting cryptocurrency wallet data from wallet.dat files.
cryptographydata-recoverydigital-forensics+2
1710 months ago
Zirconium preview

Zirconium

GitHubbyinarie/zirconium

Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
defensive-toolsdigital-forensicsincident-response+3
25 years ago
scalpel preview

scalpel

GitHubsleuthkit/scalpel

File carving and indexing tool for digital forensics, recovering files from disk images based on header/footer pattern matching, regular expressions,…

data-recoverydigital-forensicsdisk-forensics+1
6905 years ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k15 days ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k10h 23m ago
ALPC-Enumerator preview

ALPC-Enumerator

GitHubtalha-nazeef-ahmed/alpc-enumerator

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

digital-forensicsinformation-gatheringmalware-analysis+4
291 month ago
dfir-orc preview

dfir-orc

GitHubdfir-orc/dfir-orc

Forensics artefact collection tool for systems running Microsoft Windows
defensive-toolsdigital-forensicsforensics+2
4501 month ago
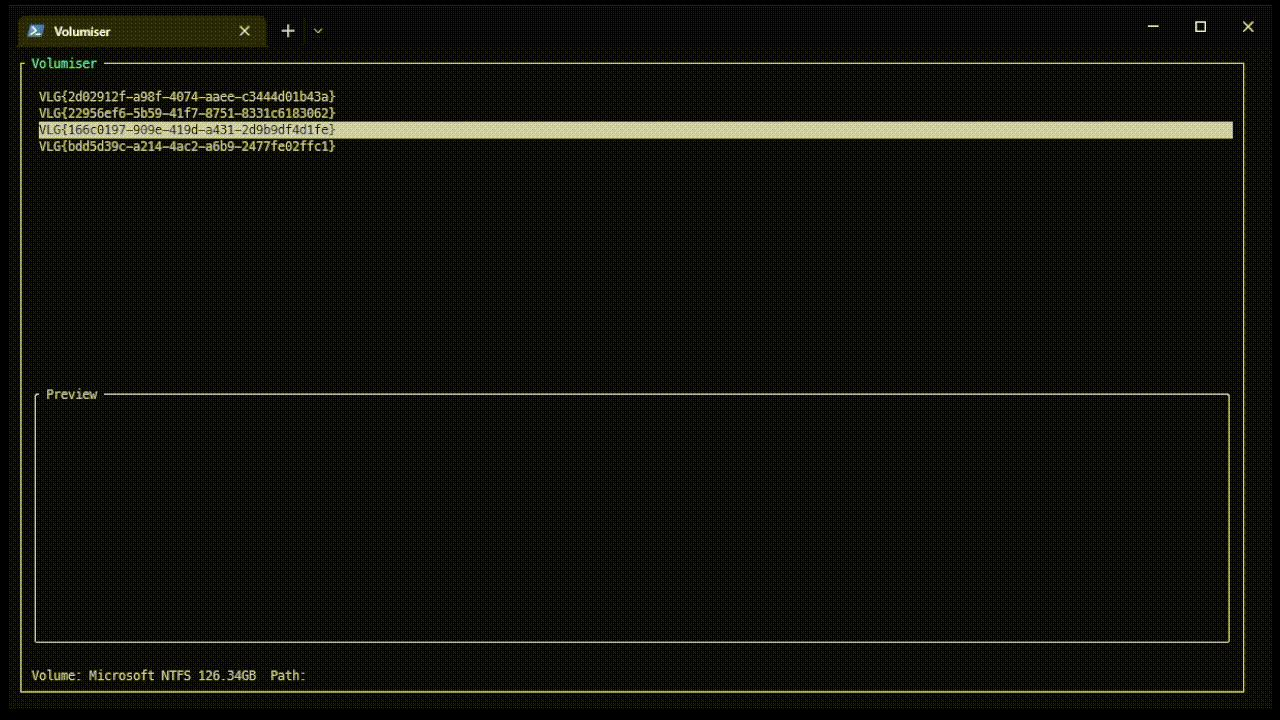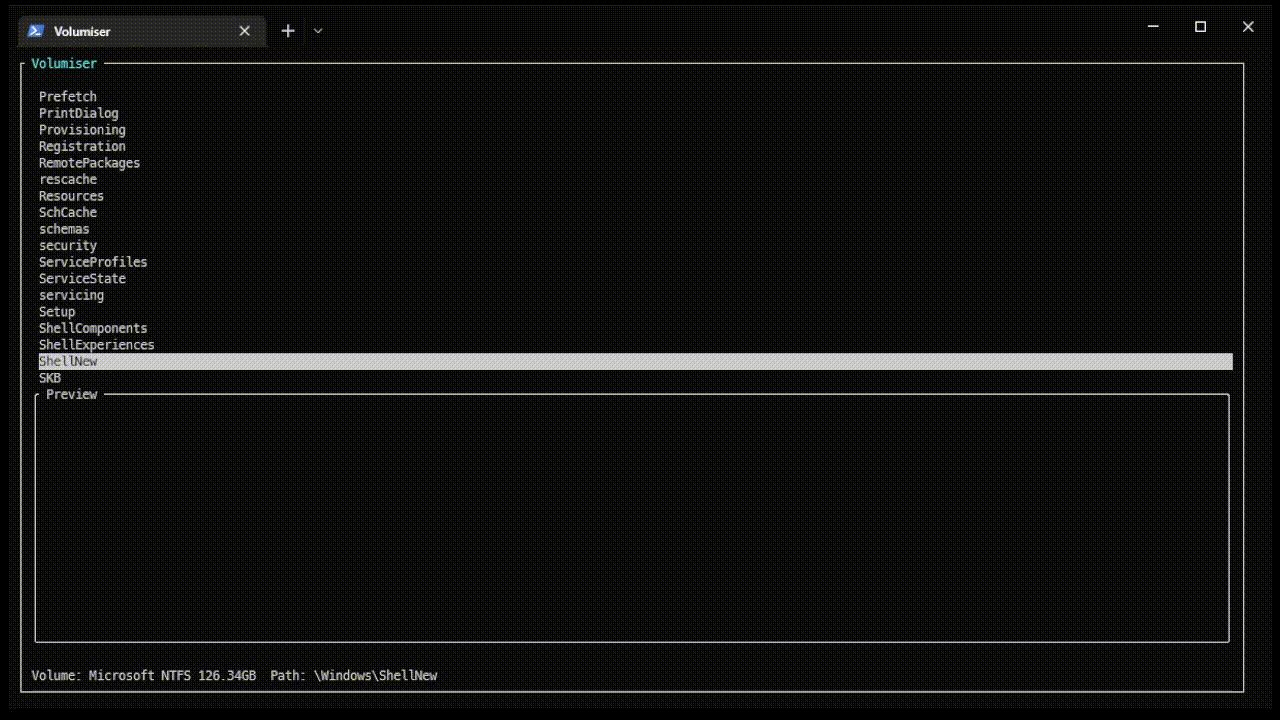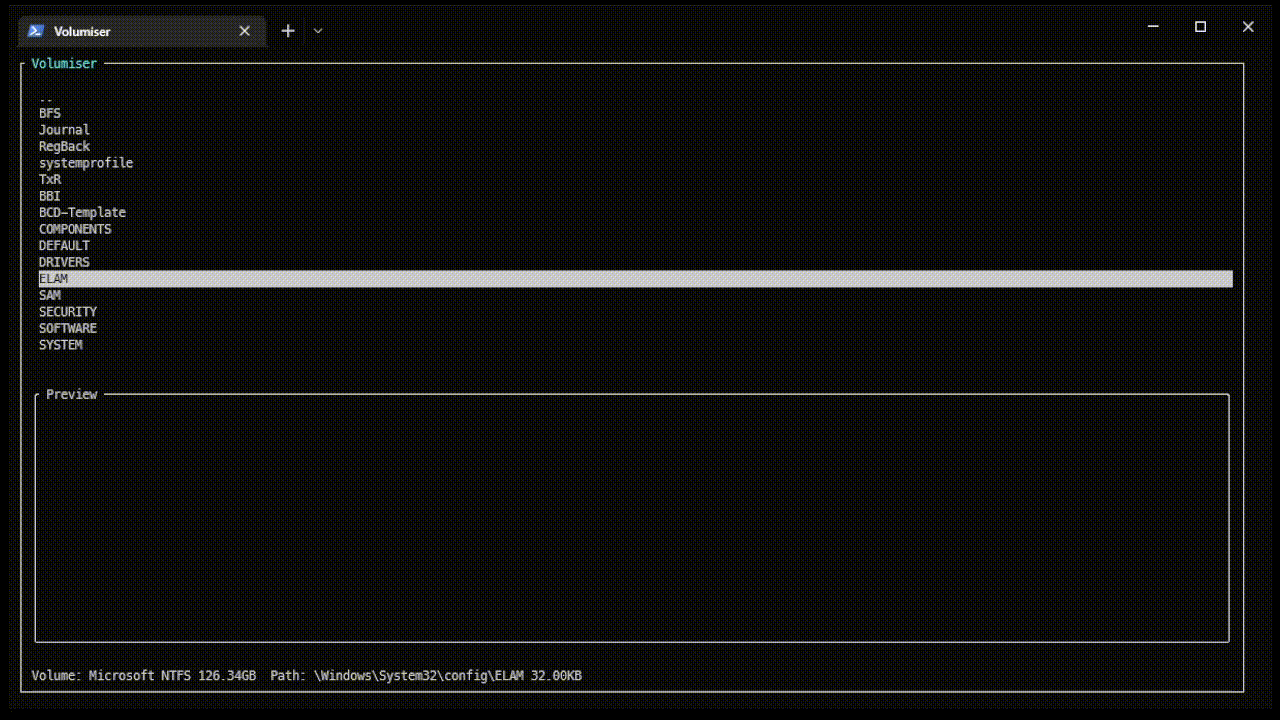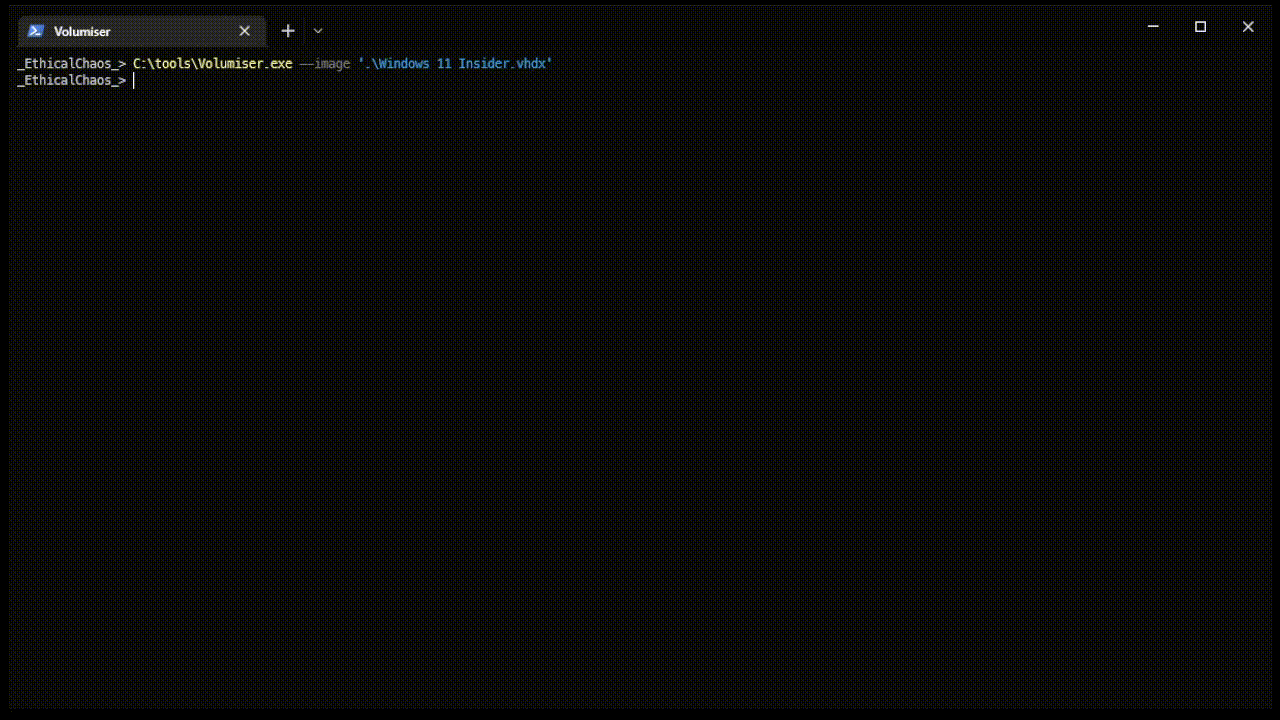
Volumiser preview

Volumiser

GitHubccob/volumiser

CLI and interactive console for listing, browsing, and extracting files from VM disk images (VHDX, VMDK, EBS snapshots, raw disks) for red-team…
command-and-controldata-exfiltrationdigital-forensics+3
4361 year ago
tools preview

tools

GitHubthreatlabz/tools

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

data-recoverydigital-forensicsencryption-decryption-tools+4
1053 months ago
debloat preview

debloat

GitHubsquiblydoo/debloat

A GUI and CLI tool for removing bloat from executables
binary-analysisdigital-forensicsmalware-analysis+1
4563 months ago
VISION-ProcMon preview

VISION-ProcMon

GitHubforensicxlab/vision-procmon

A ProcessMonitor visualization application written in rust.
digital-forensicslog-analysismalware-analysis
1833 years ago
untitledgoosetool preview

untitledgoosetool

GitHubcisagov/untitledgoosetool

Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…

cloud-securitydefensive-toolsdigital-forensics+4
9657 months ago
Previous12…10Next