
chainsaw
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
withsecureopensource/chainsawRapidly Search and Hunt through Windows Forensic Artefacts
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
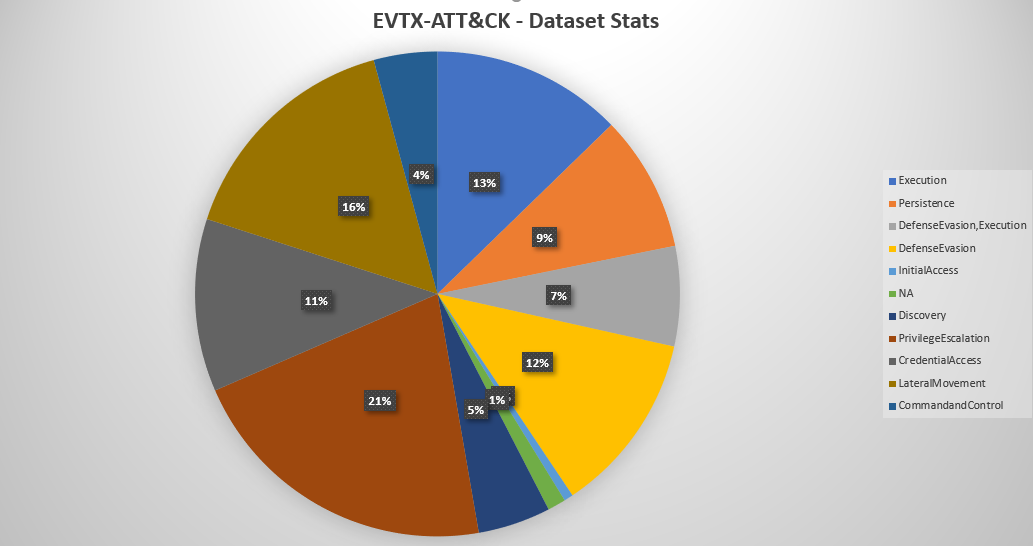 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 guillaumemeyer/watermarks-remover
A privacy-first app that strips AI watermarks from content you own.
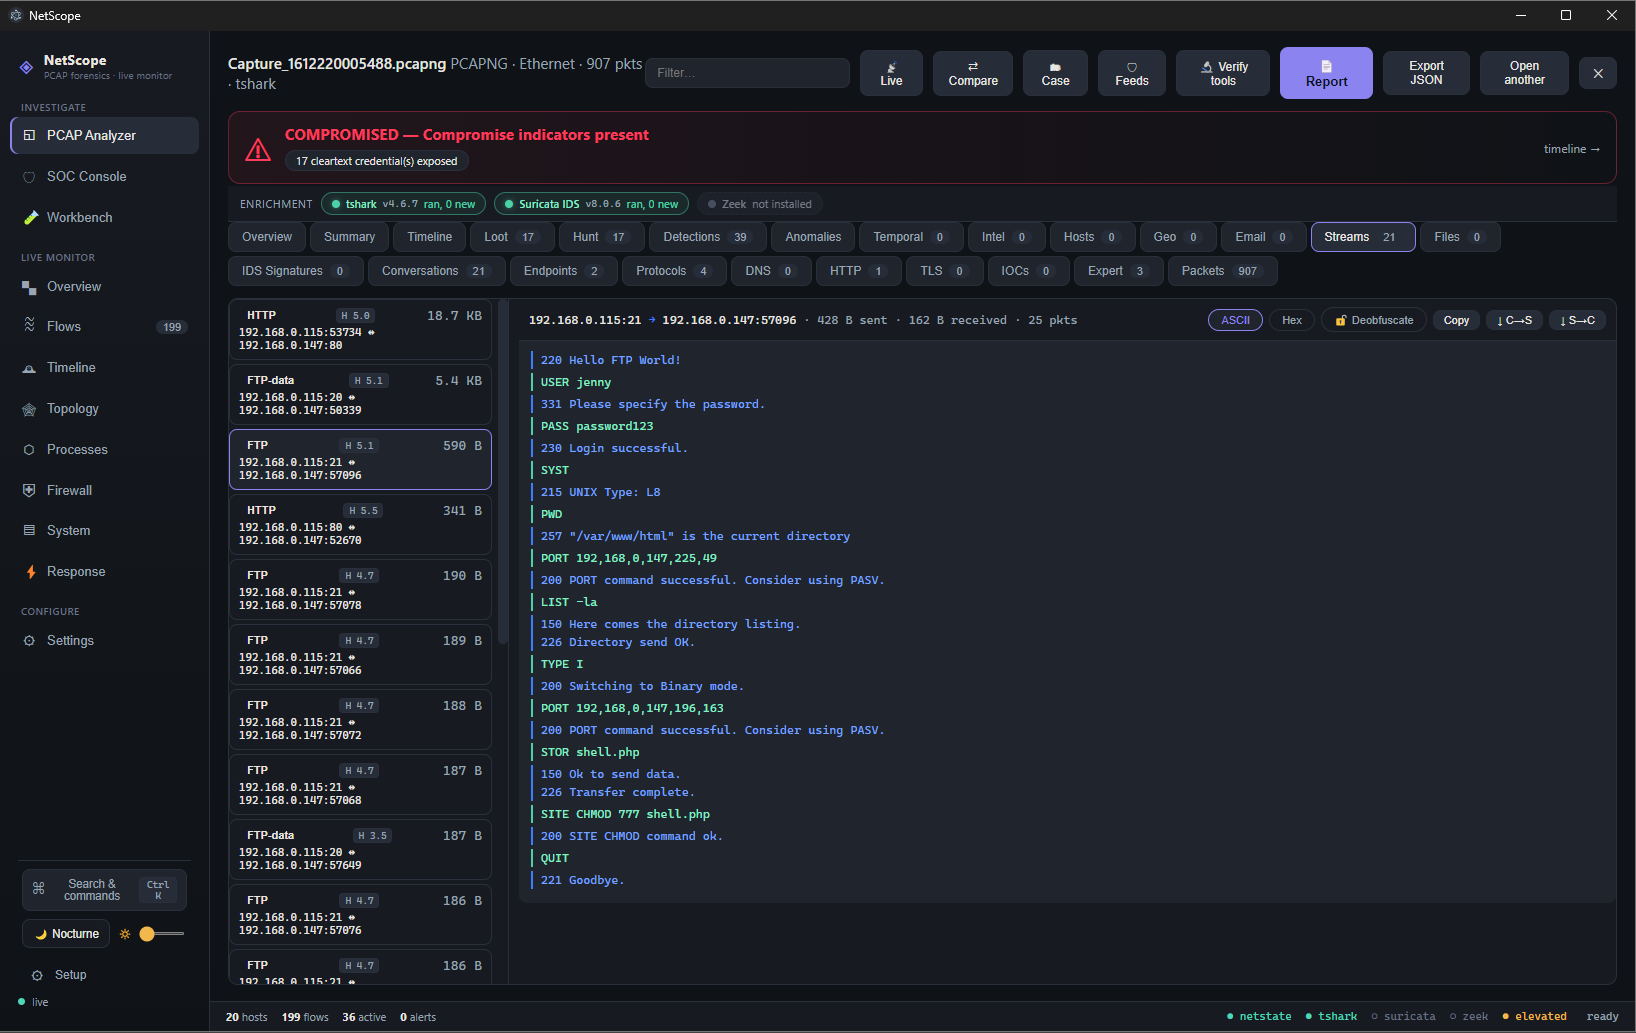 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 strangerealintel/cyberthreatintel
Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups
 bontchev/whodunit
Recognizing the most likely APT groups responsible for an incident
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
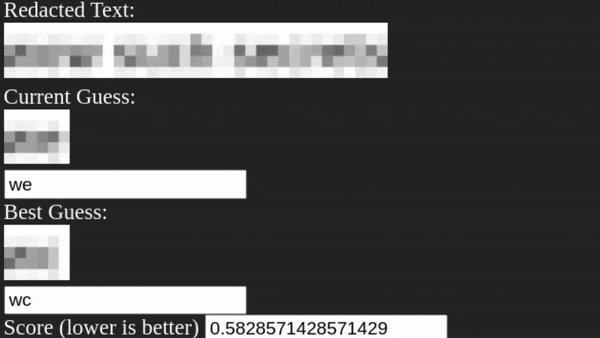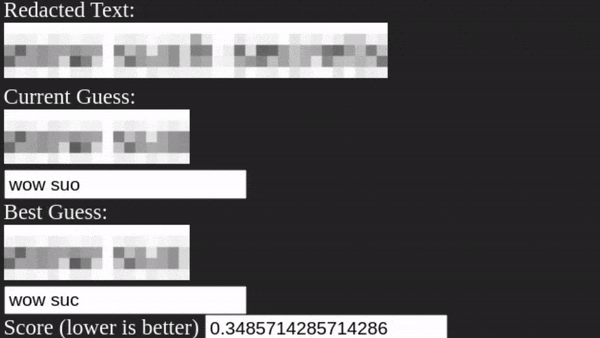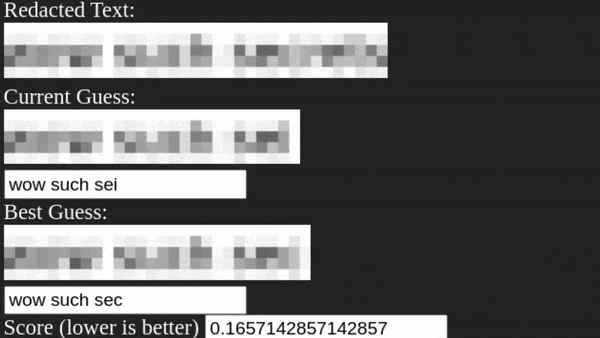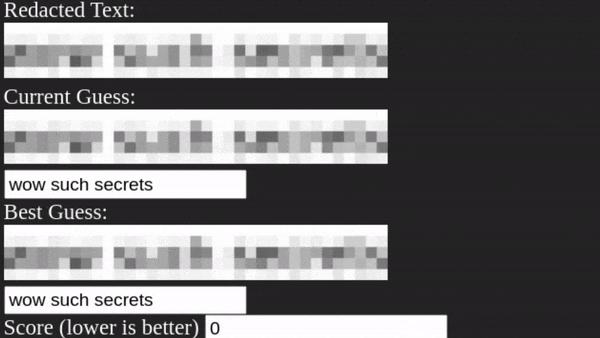 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 cyprianatsyor/cve-2024-24919-incident-report.md
Detailed incident report analyzing CVE-2024-24919 arbitrary file read exploit on Check Point Security Gateway, including technical analysis, response…
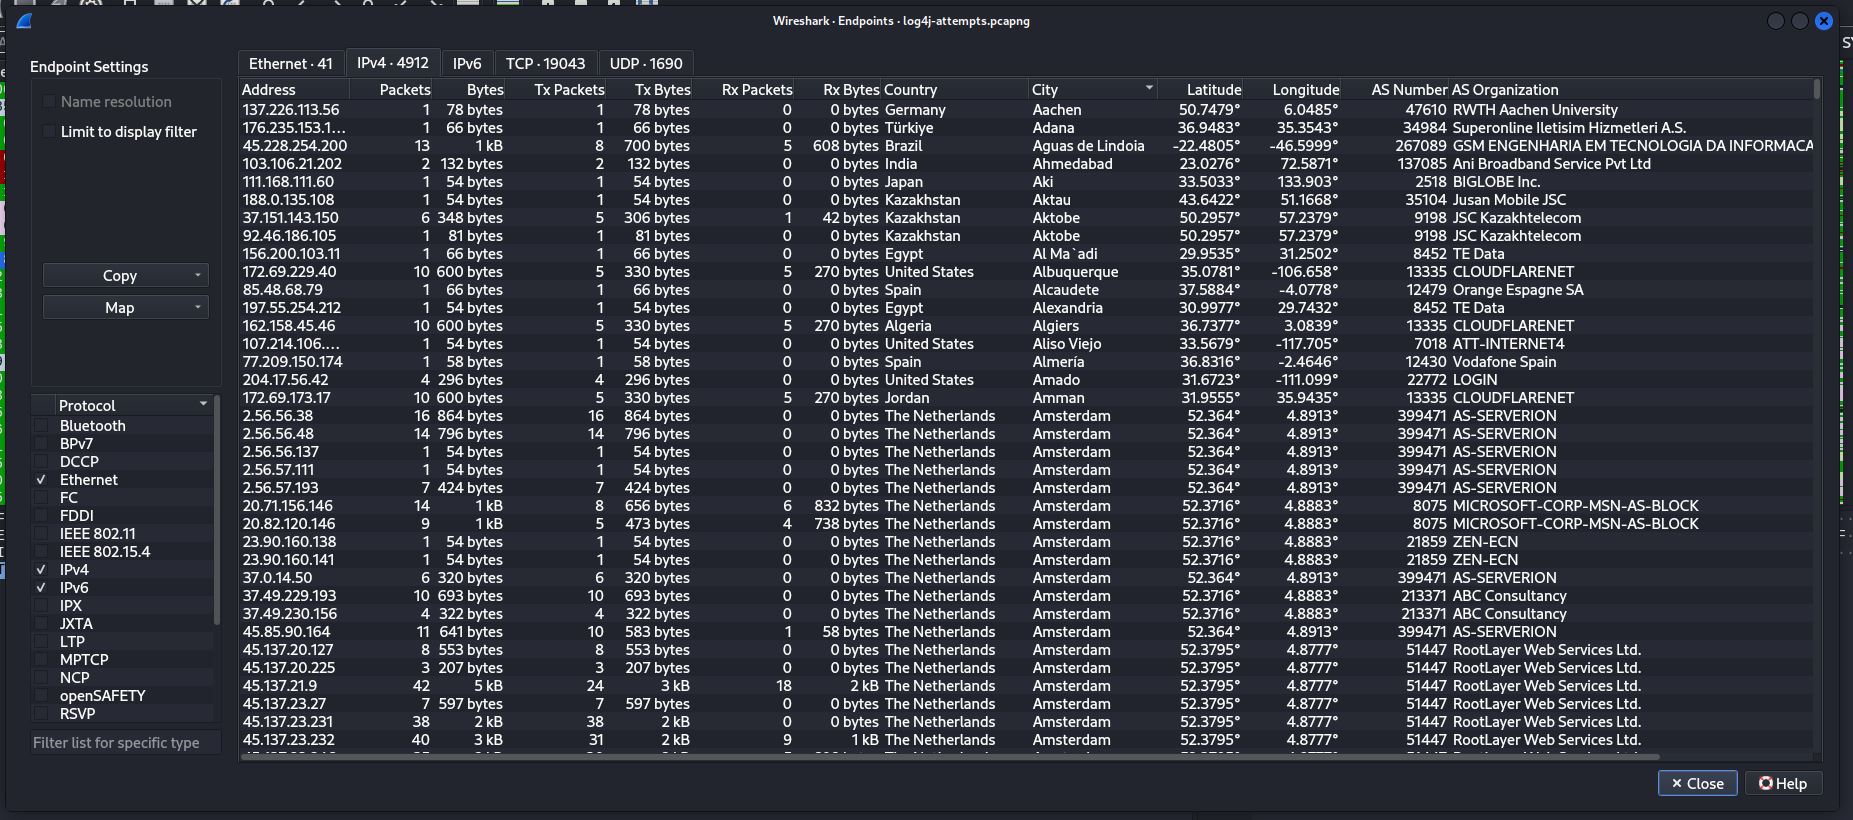 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).