

analyzer
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
324
qeeqbox/analyzerAnalyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
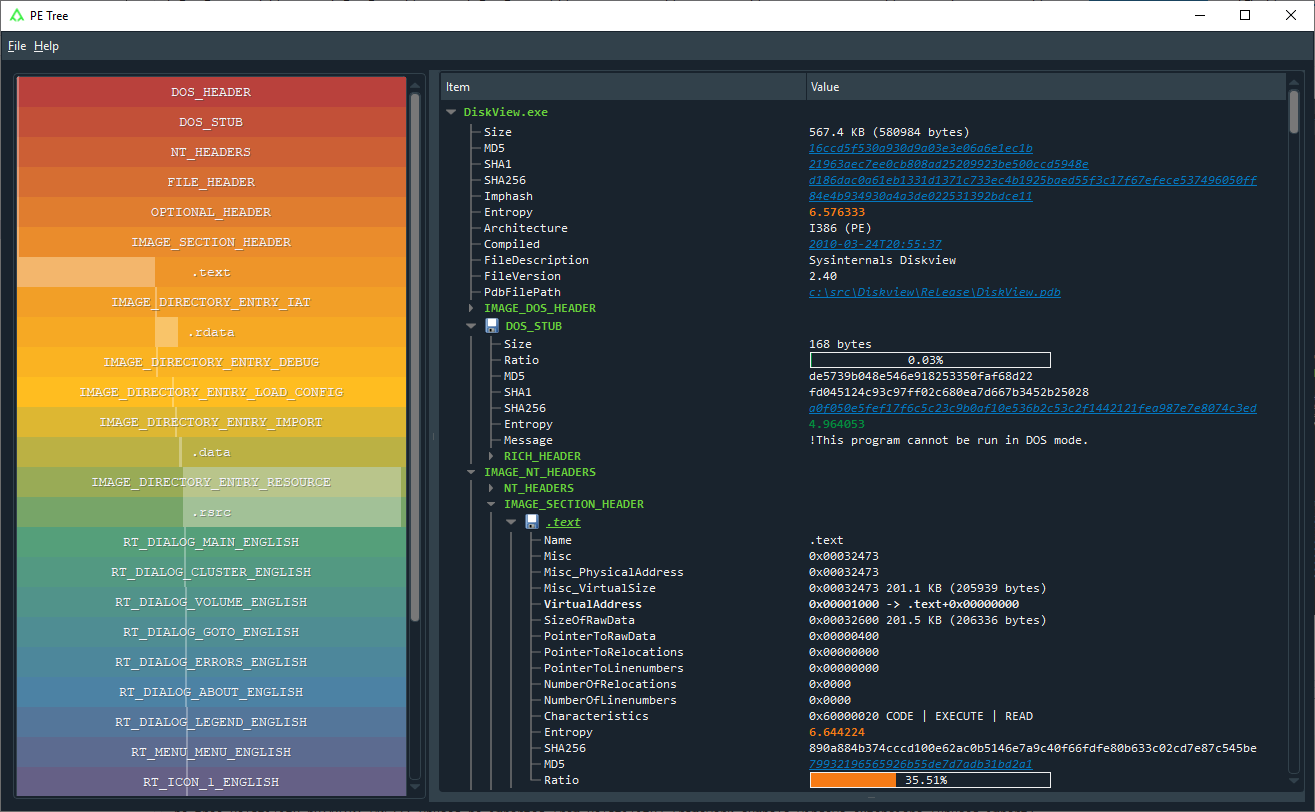 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 dumpanalysis/prologwindbg
Use Prolog to analyze memory dumps and stopped live processes in WinDbg.