

grr
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k2 days ago
google/grrRemote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…
 velocidex/winpmem
The multi-platform memory acquisition tool.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 halpomeranz/lmg
Script for automating Linux memory capture and analysis
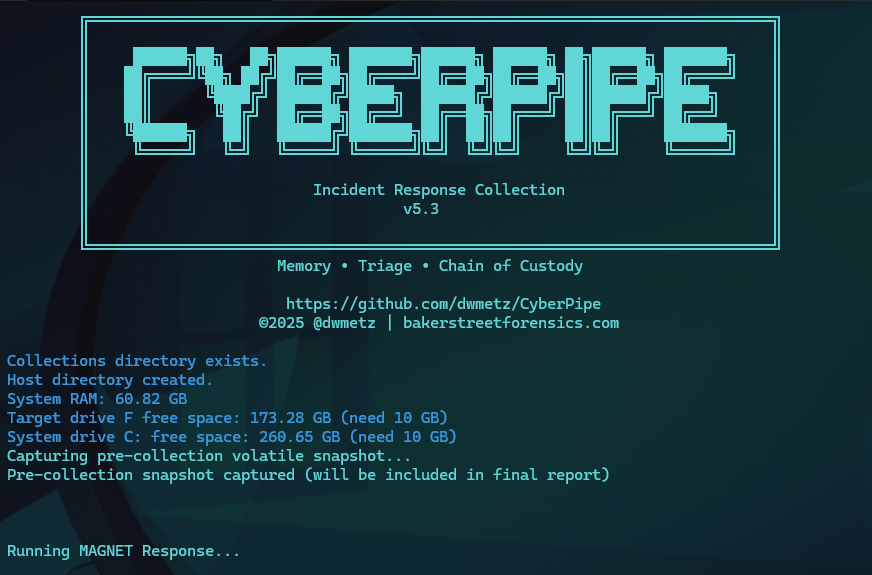 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
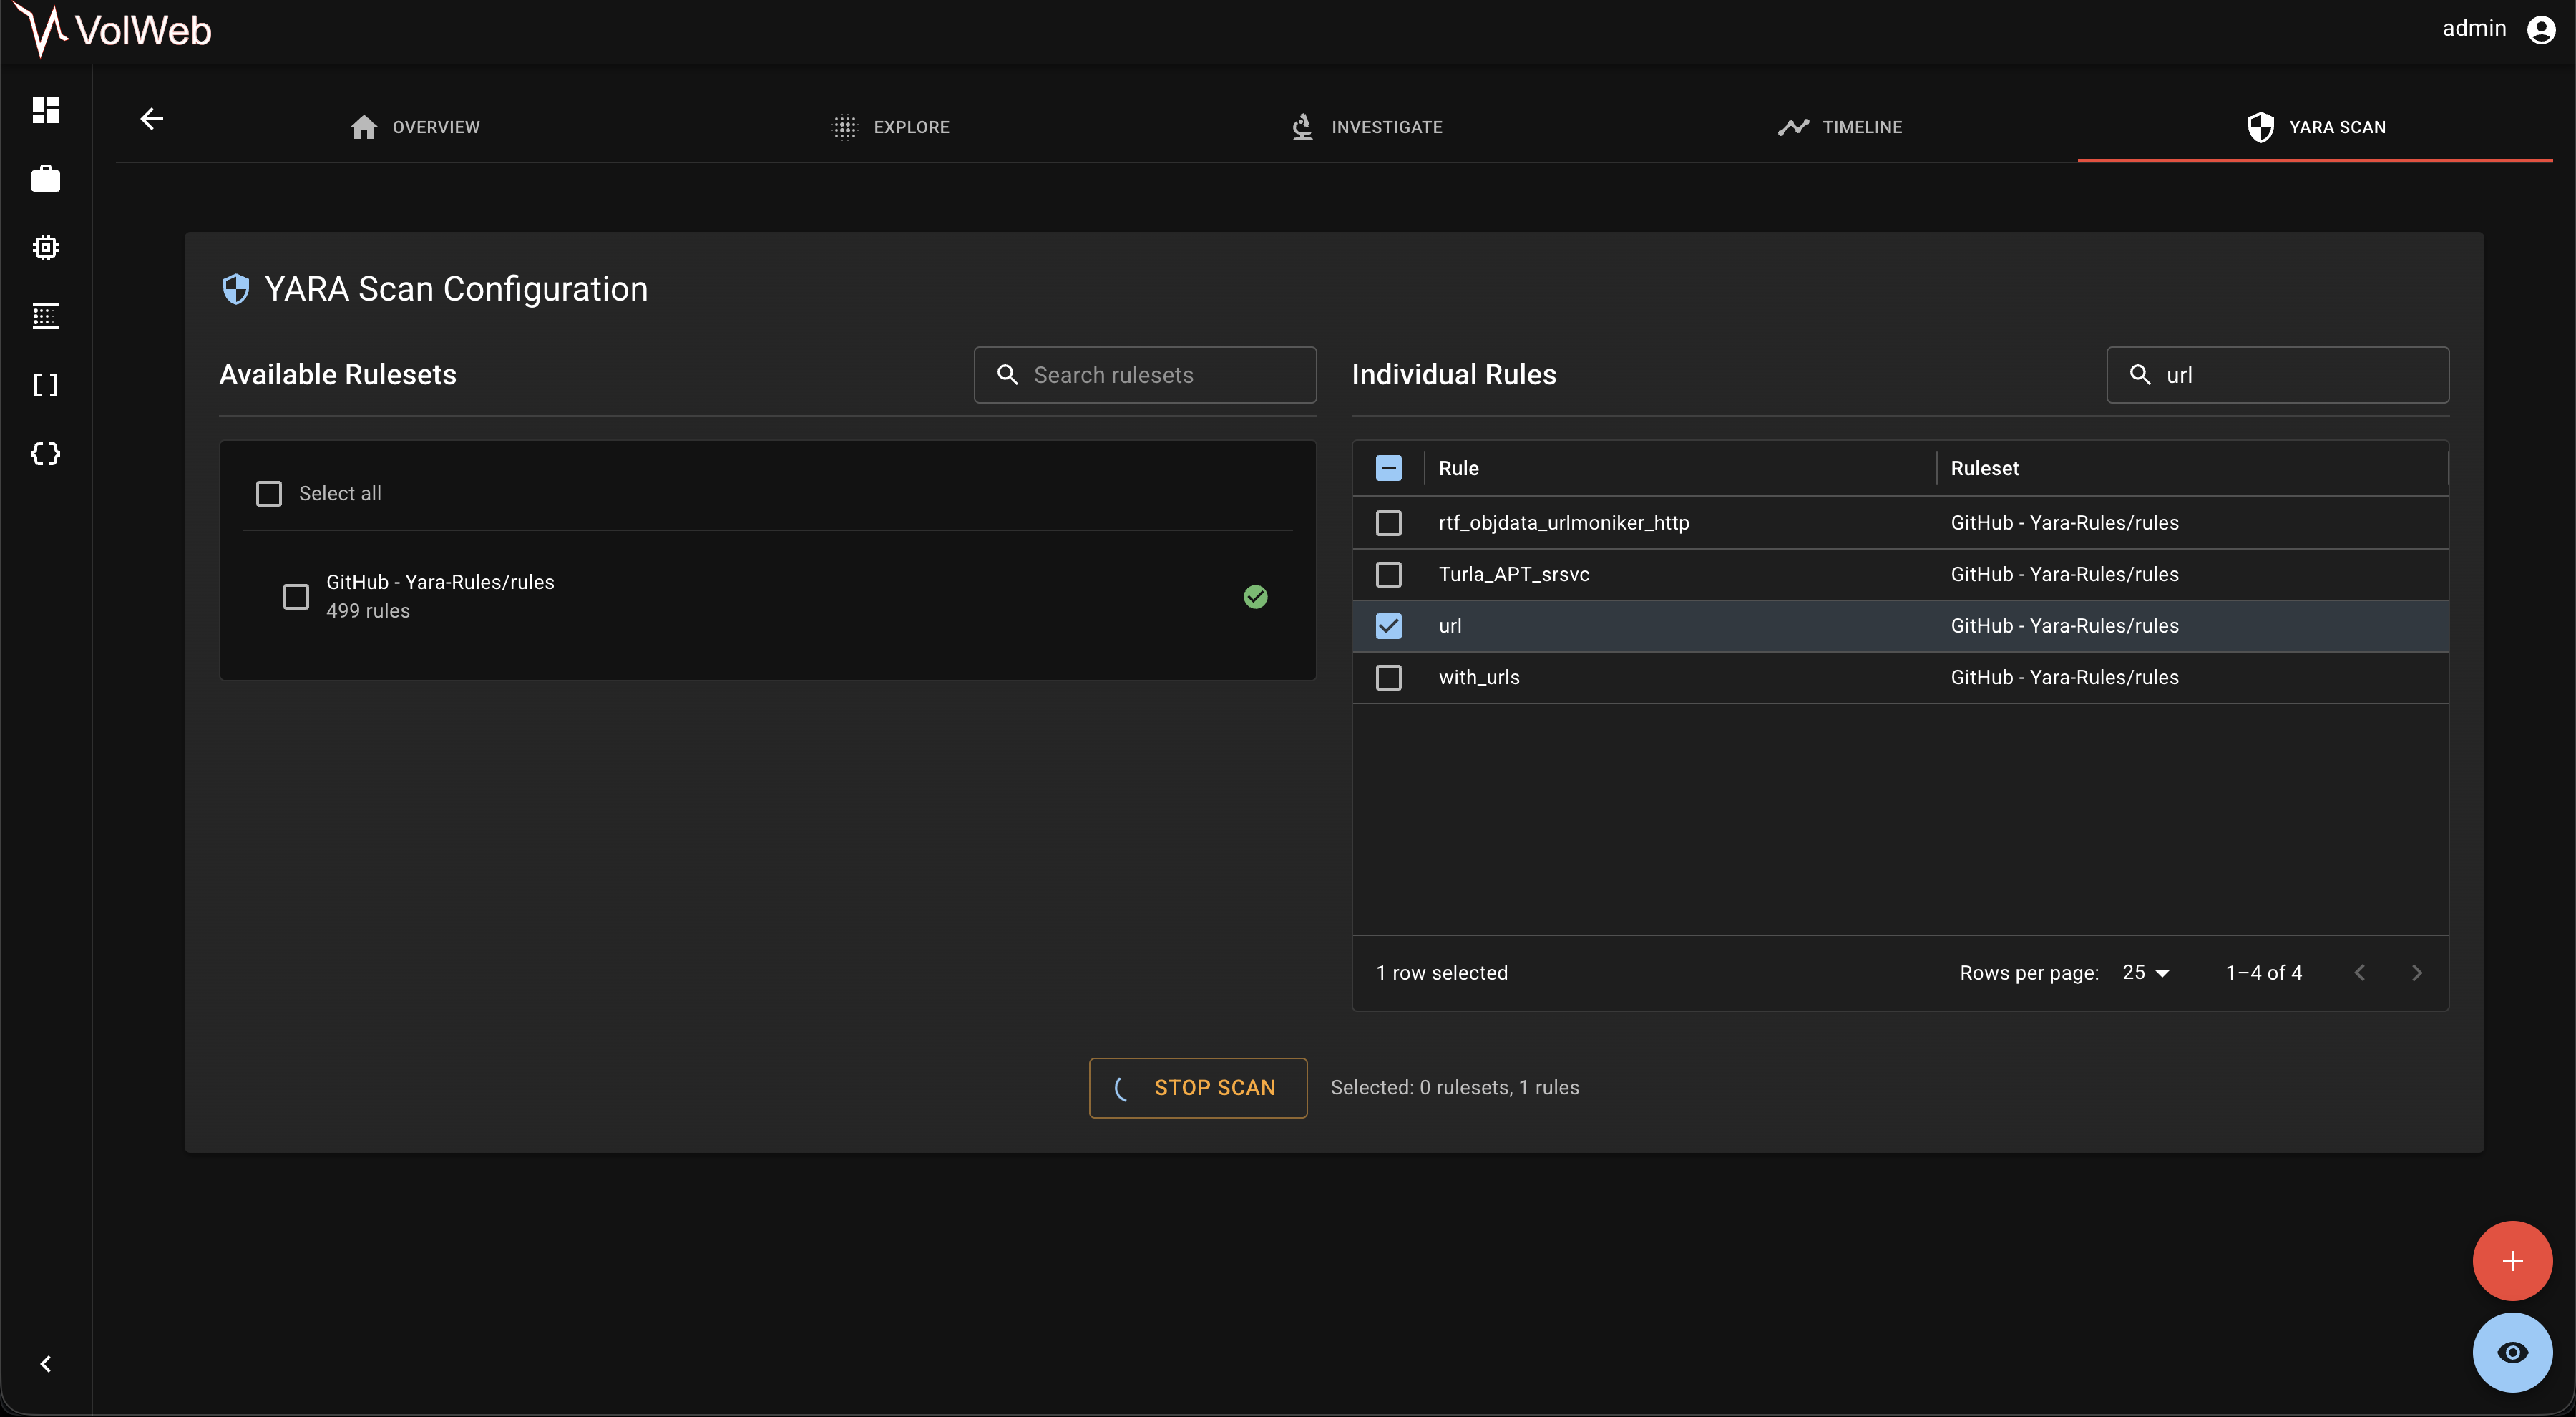 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
 volatilityfoundation/volatility
An advanced memory forensics framework
 volatilityfoundation/community
Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.