
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
659 results
sherlock preview

sherlock

GitHubsherlock-project/sherlock

Hunt down social media accounts by username across social networks
digital-forensicsemail-harvestingforensics+11
92.8k3h 39m ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…

digital-forensicsincident-responselog-analysis+1
1592 years ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
8.0k1 day ago
remove-ai-watermarks preview

remove-ai-watermarks

GitHubwiltodelta/remove-ai-watermarks

Remove visible and invisible AI watermarks and provenance metadata from images and video. Python library and CLI for SynthID, C2PA, EXIF, IPTC, XMP,…
cryptographydata-recoverydigital-forensics+6
5.7k18h 39m ago
pftriage preview

pftriage

GitHubidiom/pftriage

Python tool and library to help analyze files during malware triage and analysis.

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+4
796 years ago
ipsw preview

ipsw

GitHubblacktop/ipsw

iOS/macOS Research Swiss Army Knife

ai-assisted-reversingbinary-analysisdebuggers+9
3.7k16h 1m ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k2 years ago
h4cker preview

h4cker

GitHubthe-art-of-hacking/h4cker

Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…

ai-securityctfcurated-resources+8
29.5k3 days ago
mvt preview

mvt

GitHubmvt-project/mvt

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
14.8k22h 39m ago
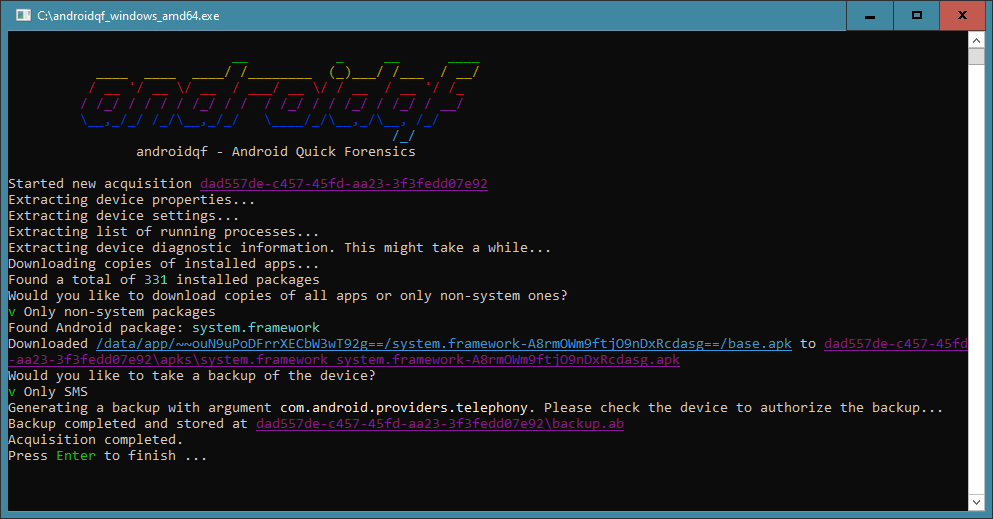
androidqf preview

androidqf

GitHubmvt-project/androidqf

androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…

android-securitydata-recoverydigital-forensics+4
30125 days ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
8164 months ago
wireshark preview

wireshark

GitHubwireshark/wireshark

Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…

bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k2 days ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
digital-forensicsforensicsnetwork-forensics+2
7401 year ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log

ai-securitydigital-forensicsincident-response+2
3.3k1 month ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.1k11h 57m ago
FACT preview

FACT

GitHubunicornunicode/fact

Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.

cloud-securitydigital-forensicsforensics
173 years ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…

digital-forensicsforensicsincident-response+2
3.4k11h 59m ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
Previous12…37Next