
SessionView
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
digital-forensicsforensicsincident-response+3
lsecqt/sessionviewA portable C# utility for enumerating local and remote windows sessions
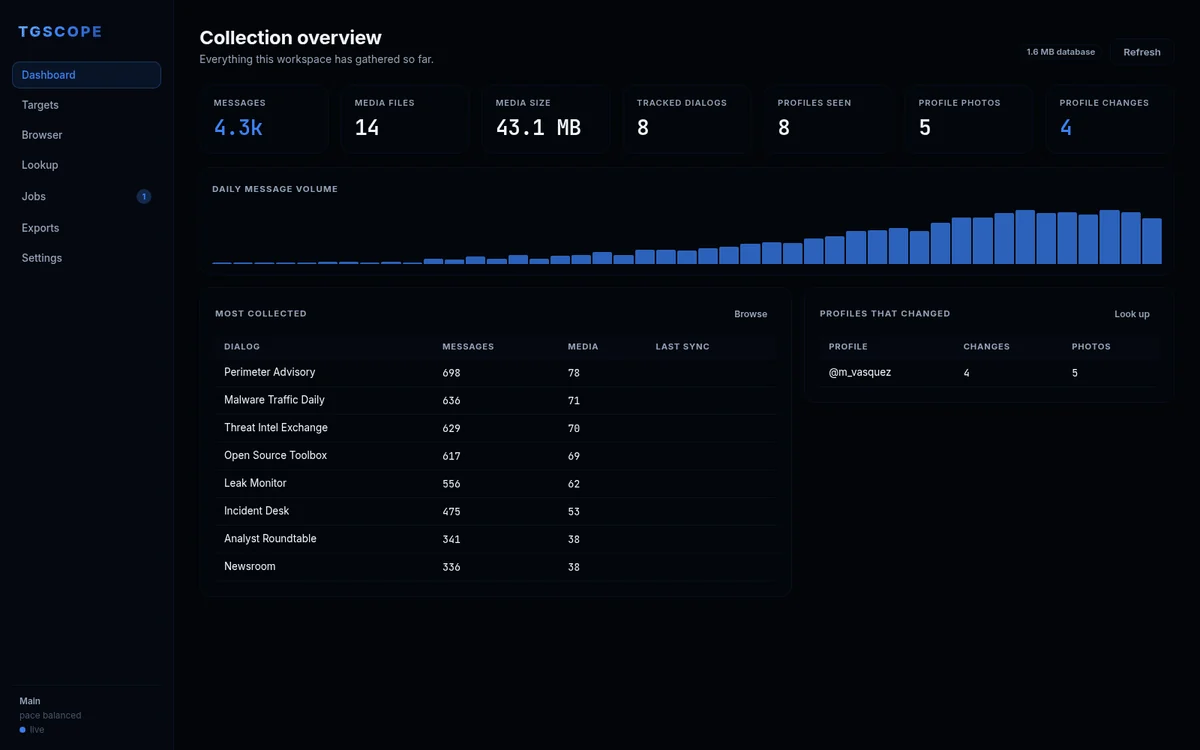 itsmoorgrove/tgscope
Telegram OSINT, scraping and archival as a local web app. Multi-account collection, profile lookup with historic photos and change diffs, ten export…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…

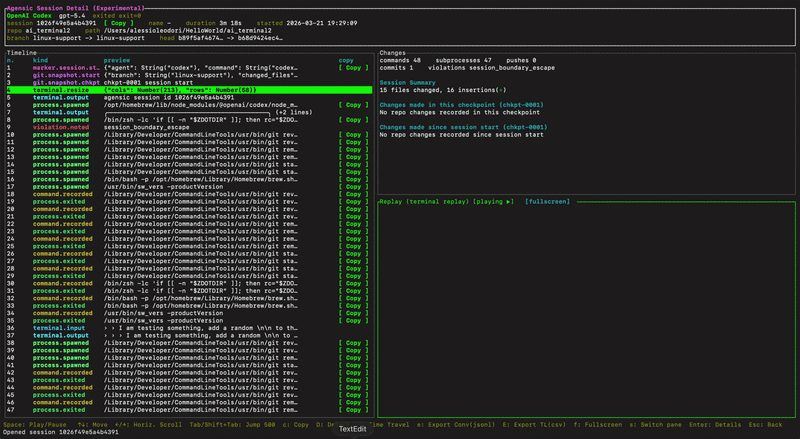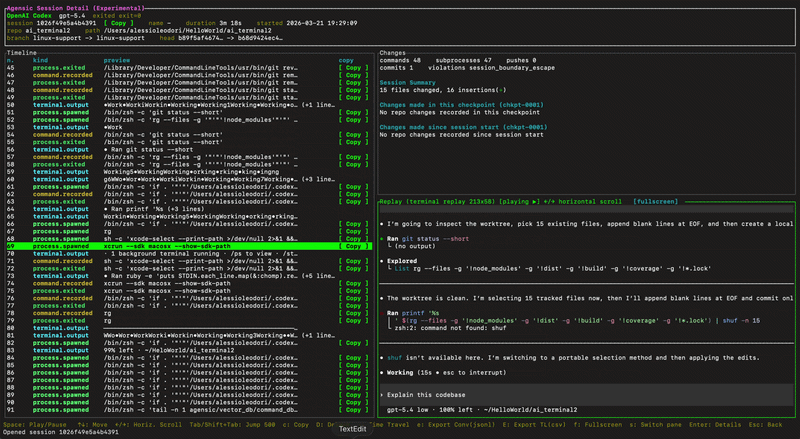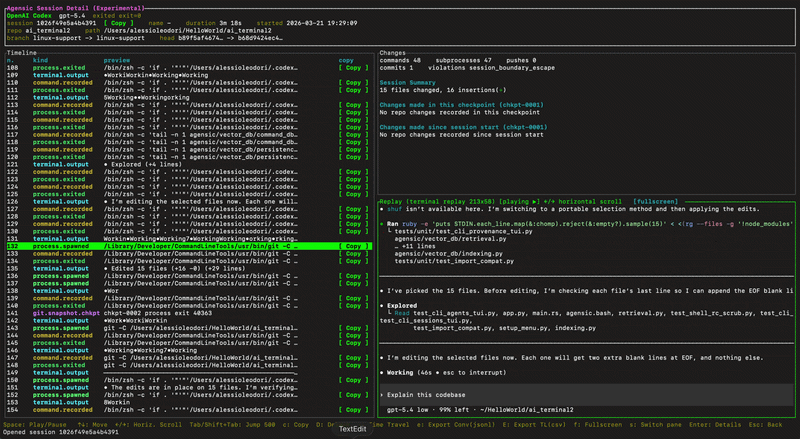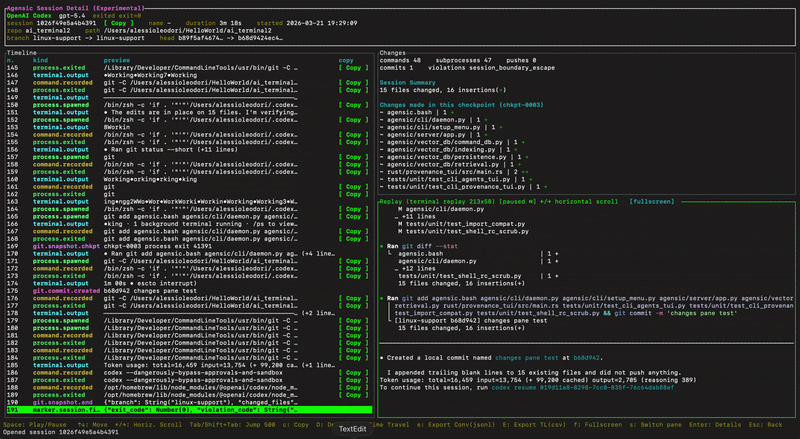 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
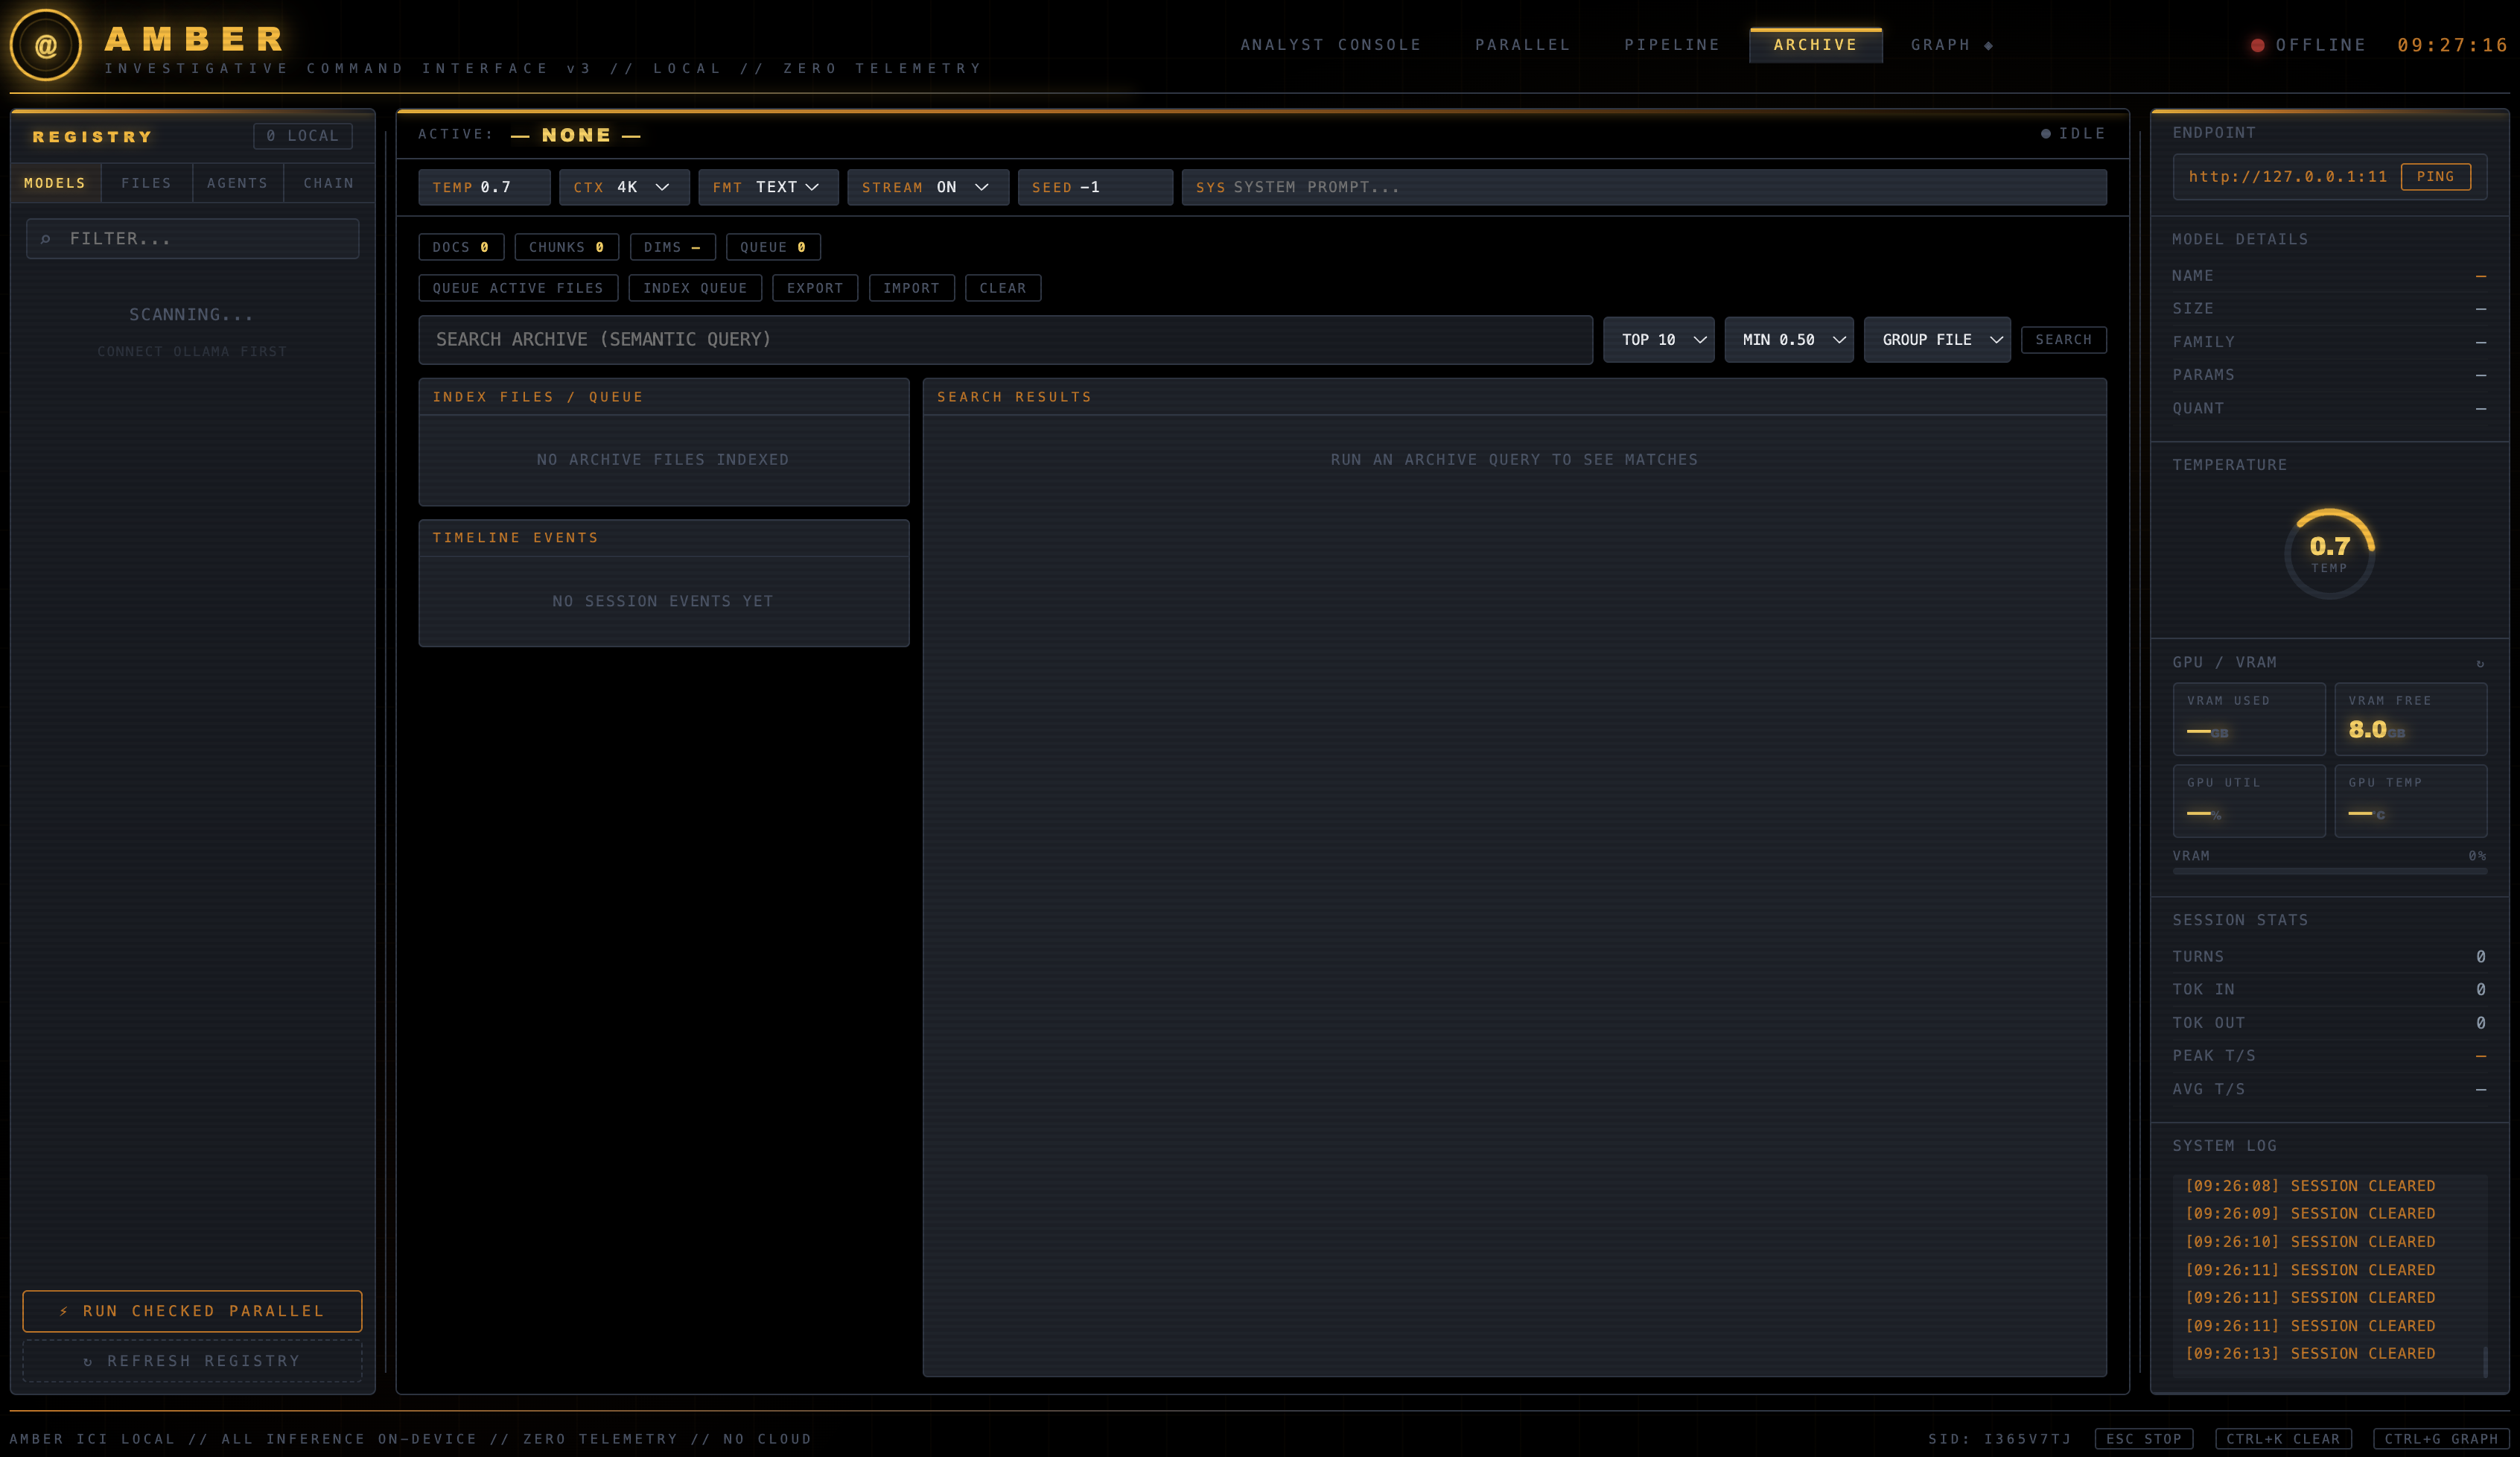 gs-ai/amber-ici
AMBER ICI v5: local-first Ollama investigative command center with case-scoped evidence, agent chains, hybrid retrieval, streaming analysis, graph…
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
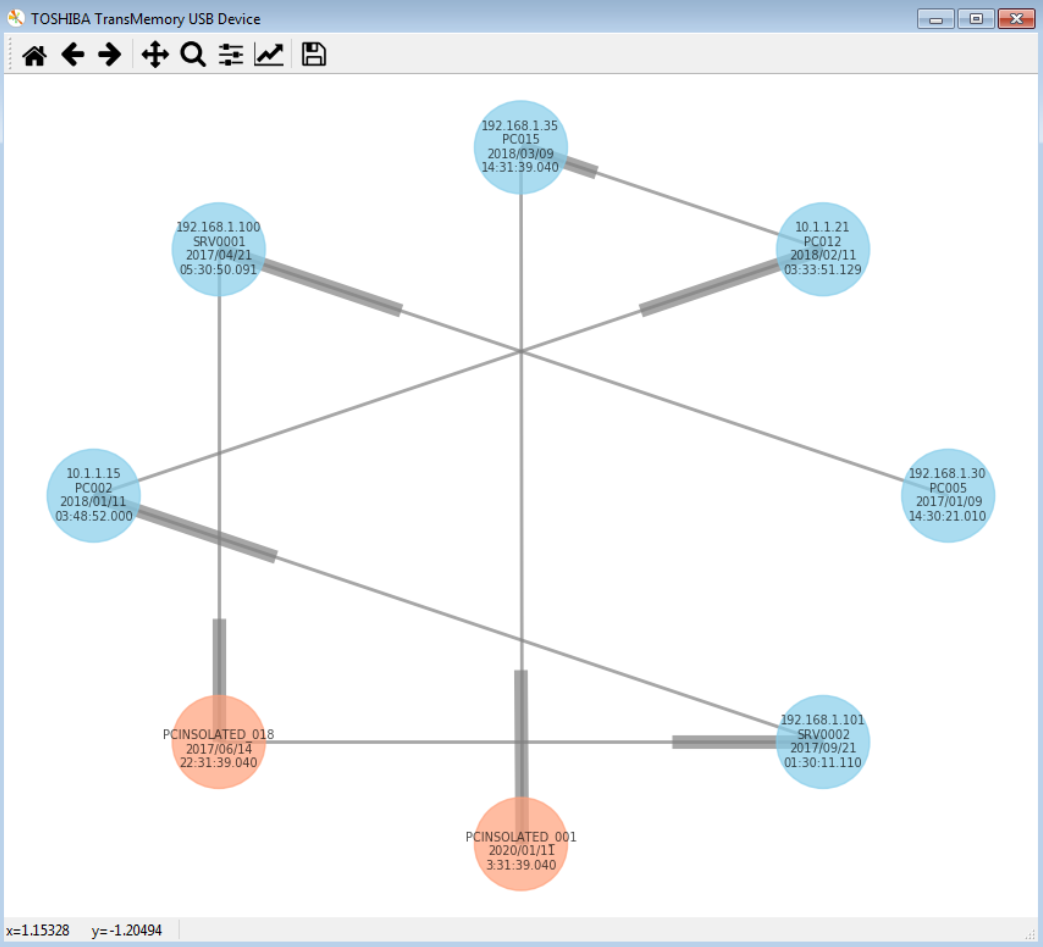 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 landw-hub/cve-2025-50422
Proof-of-concept for CVE-2025-50422: demonstrates heap memory disclosure in Poppler's pdftocairo, allowing local attackers to recover clear-text PDF…
 levilutz/cve-2021-30860
Scan for evidence of CVE-2021-30860 (FORCEDENTRY) exploit
 kd8bny/limeaide
A python application designed to remotely dump RAM of a Linux client and create a volatility profile for later analysis on your local host.
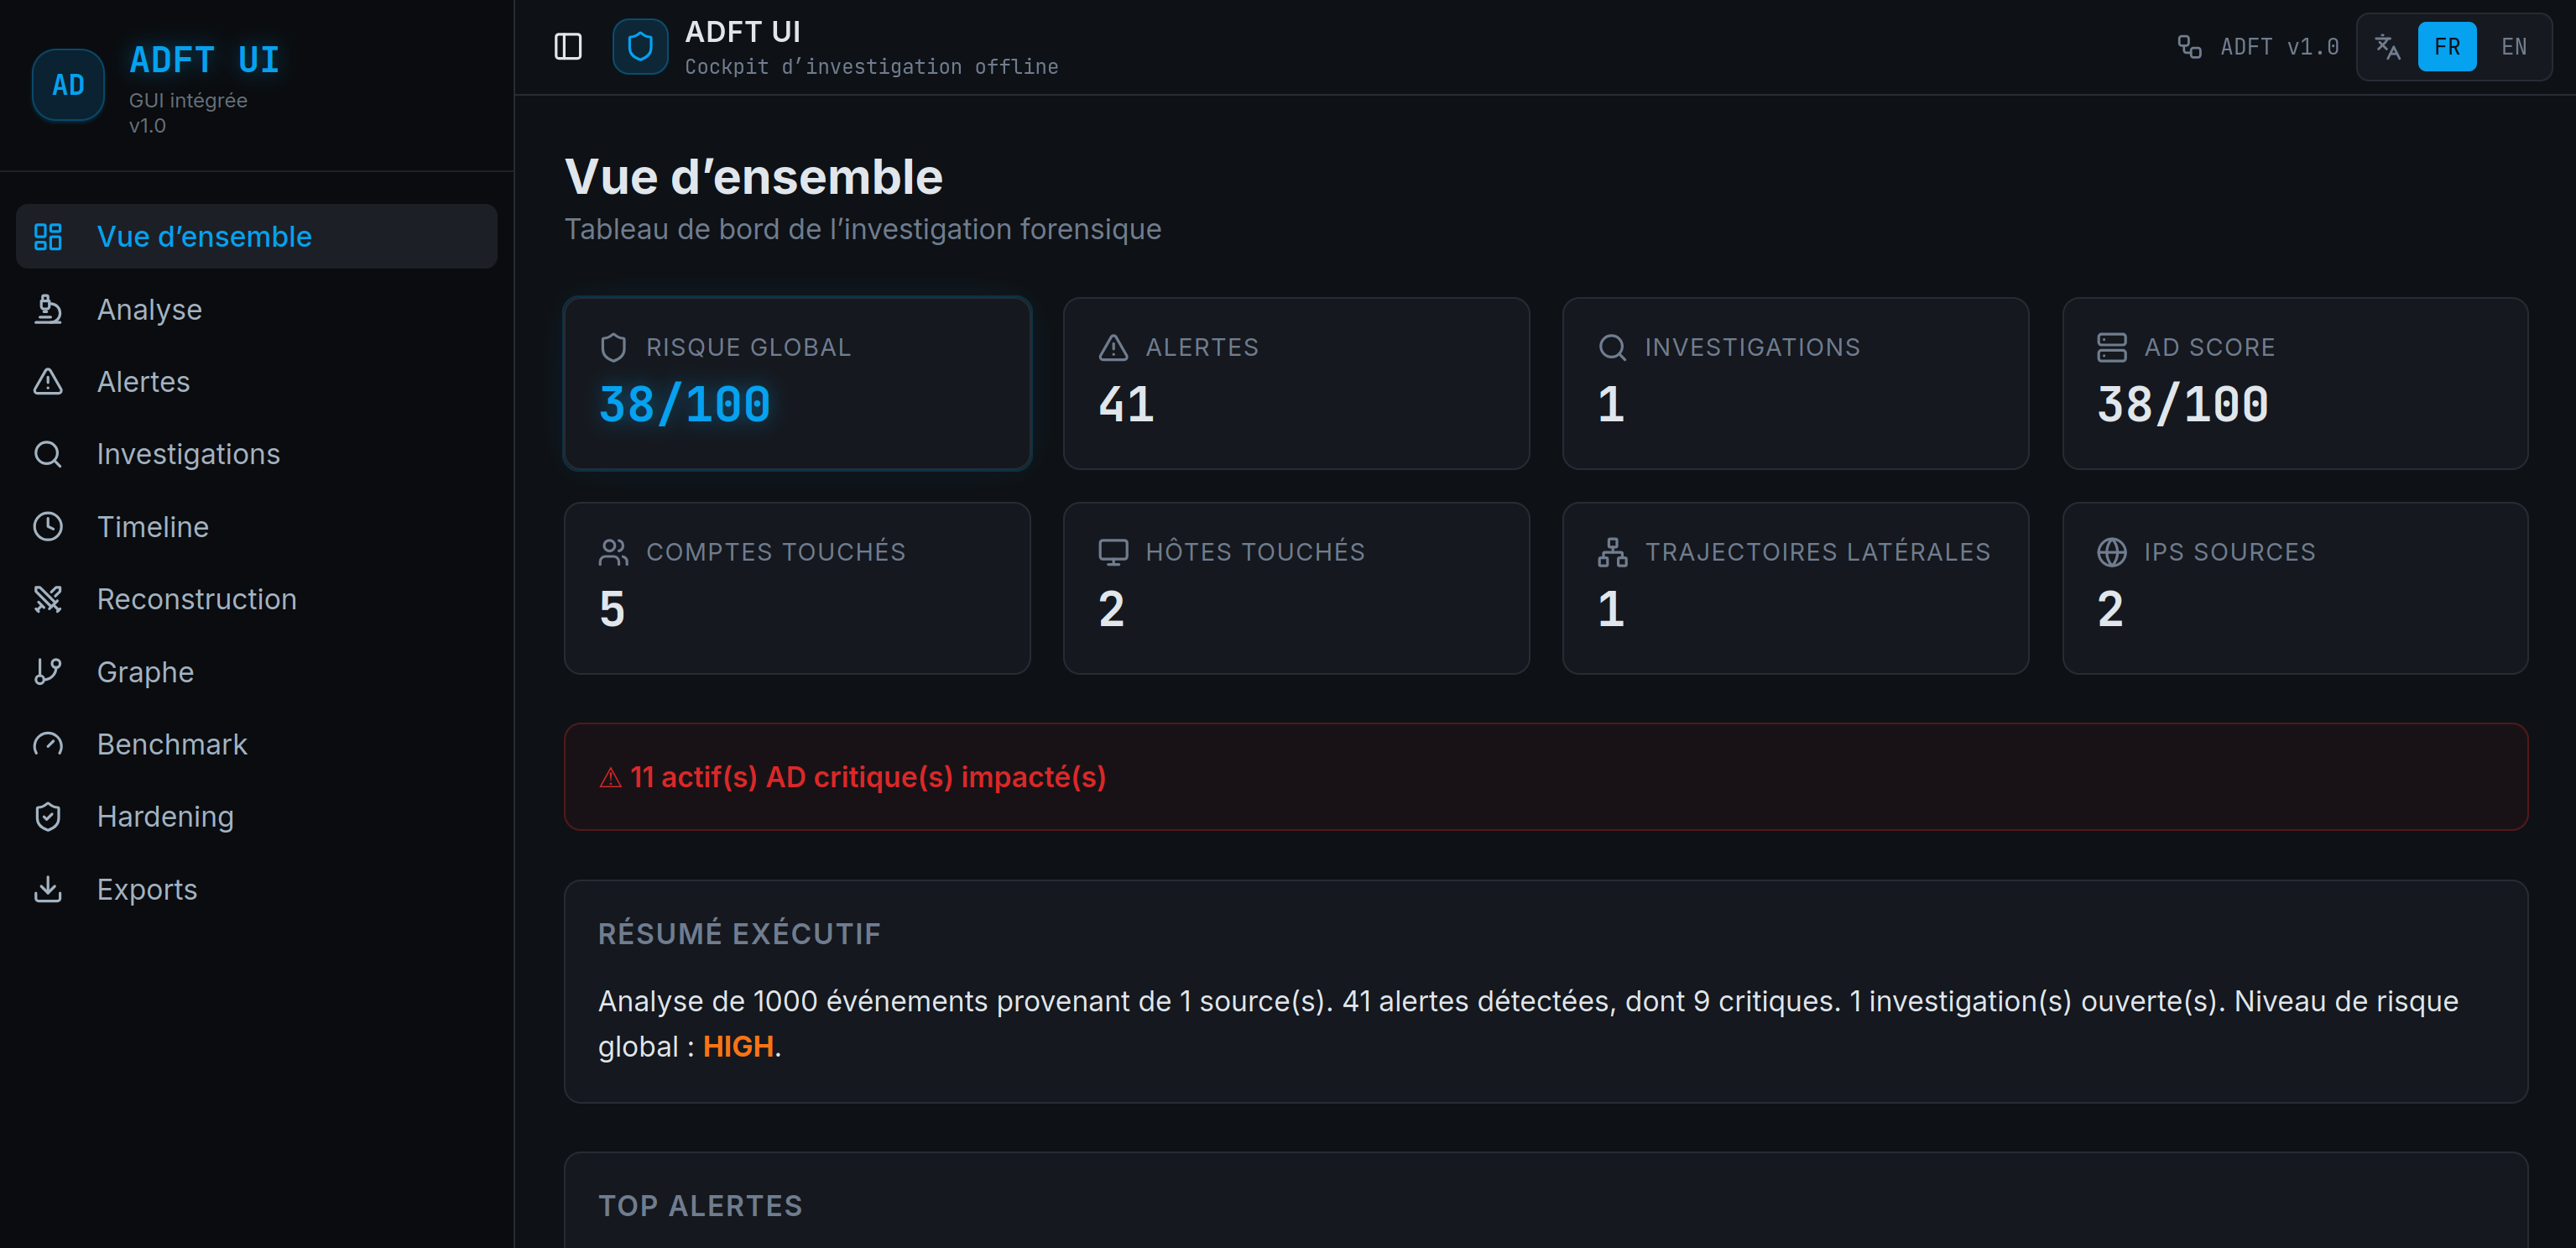 kjean13/adft
Active Directory Forensic Toolkit : Detect & reconstruct AD attacks from Windows event logs (EVTX)
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.