

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 nmatt0/moria
IoT firmware identification and extraction
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 bitcoin/bitcoin
Full-node Bitcoin client that validates transactions and blocks on the peer-to-peer network, with integrated wallet, cryptographic security, and…
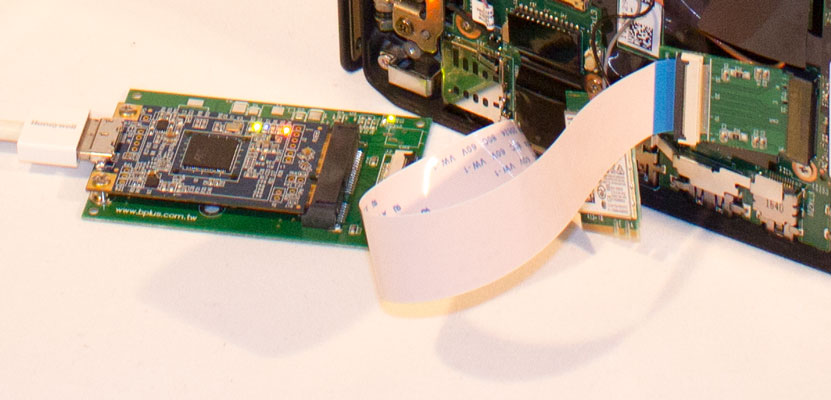 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 wmal/linux-kodachi
Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…
 daddycocoaman/dumpscan
Finding secrets in kernel and user memory
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs