
ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
981
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
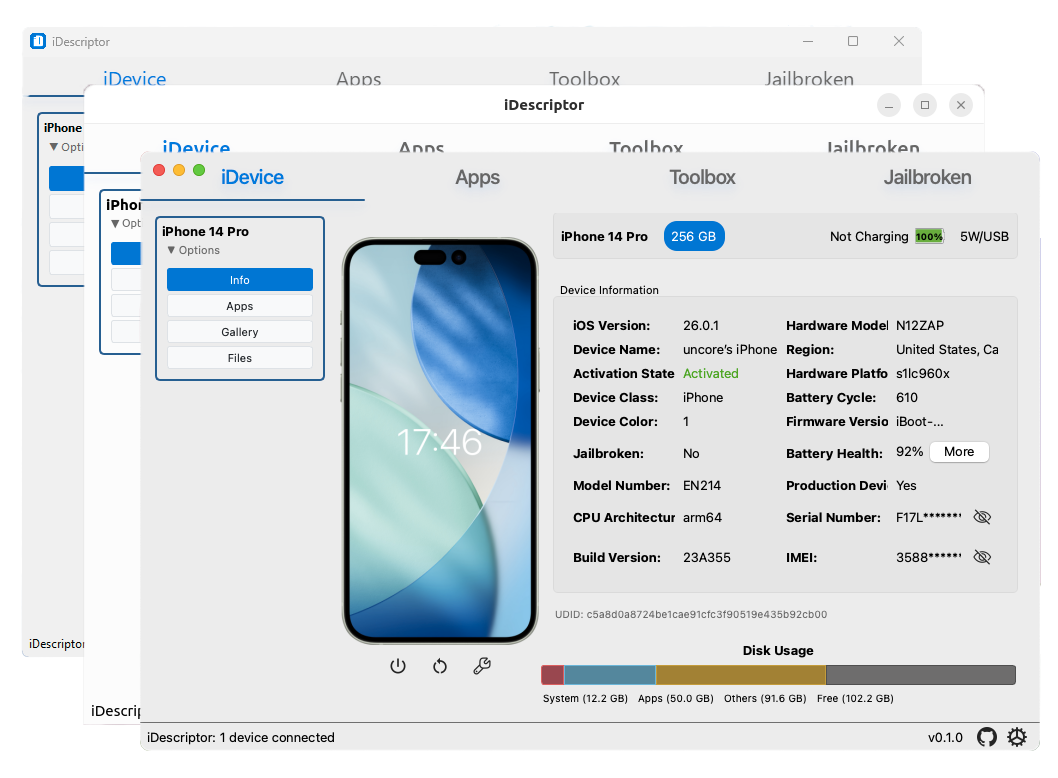 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 haruu77g/phantomprint
Passive hybrid fingerprinting engine — identify hosts without sending a single packet
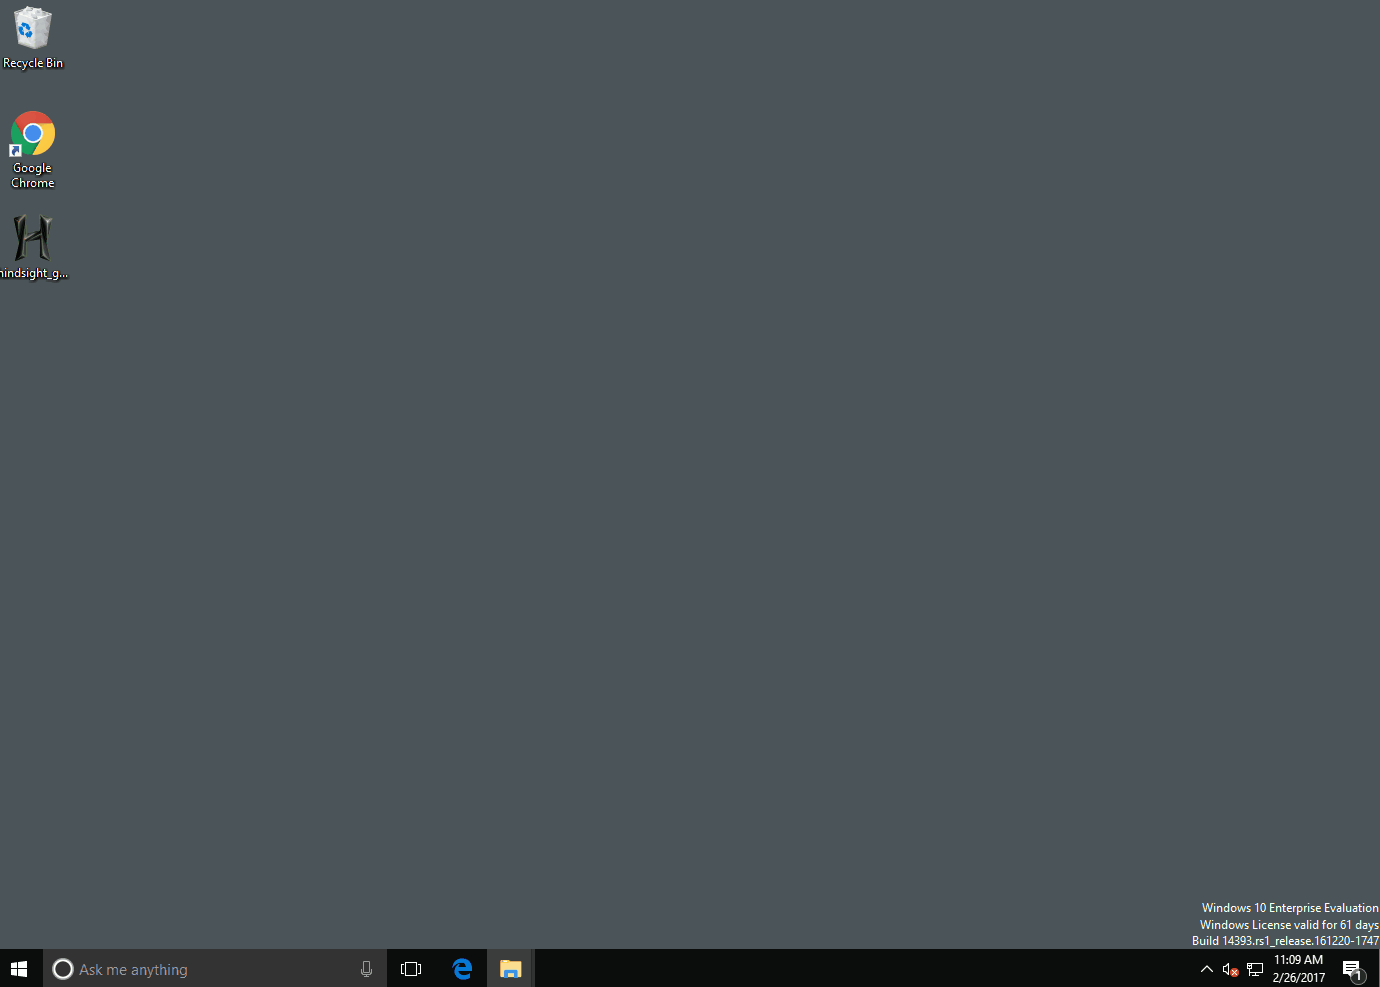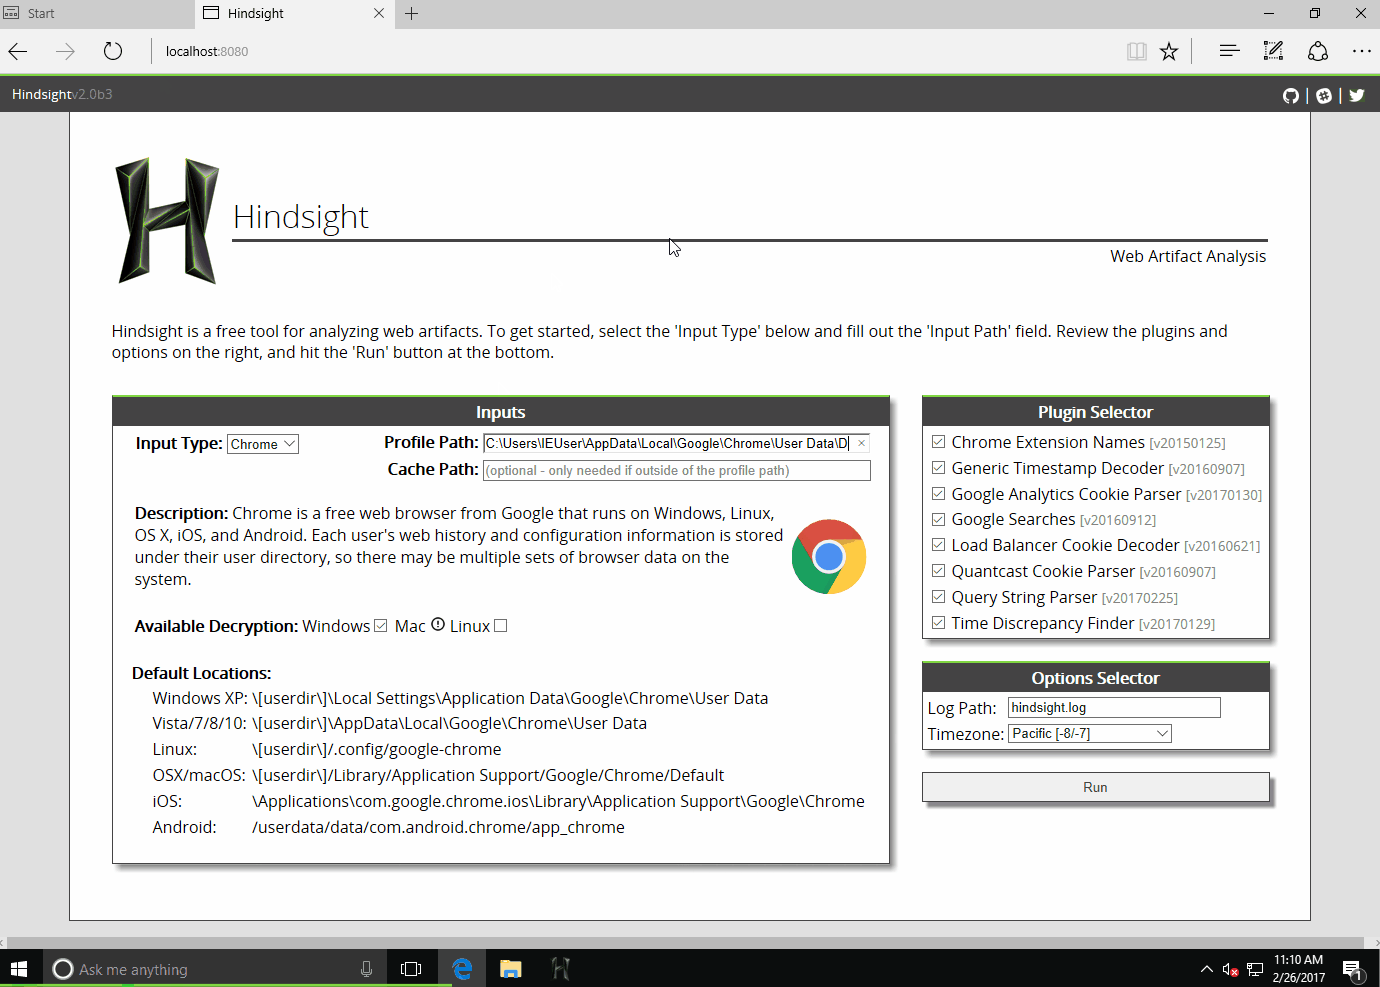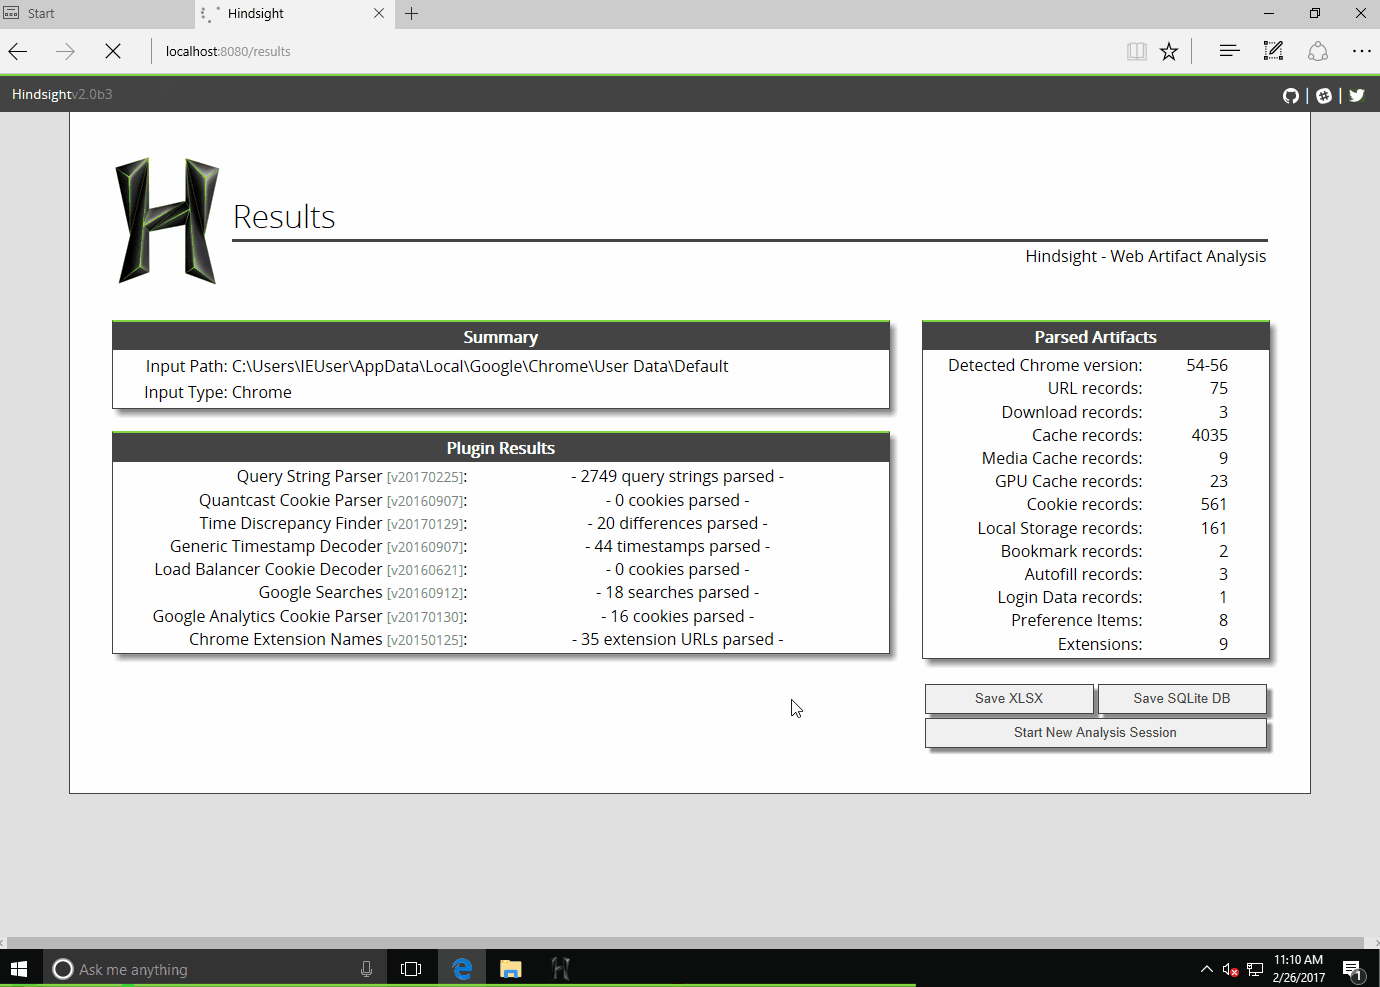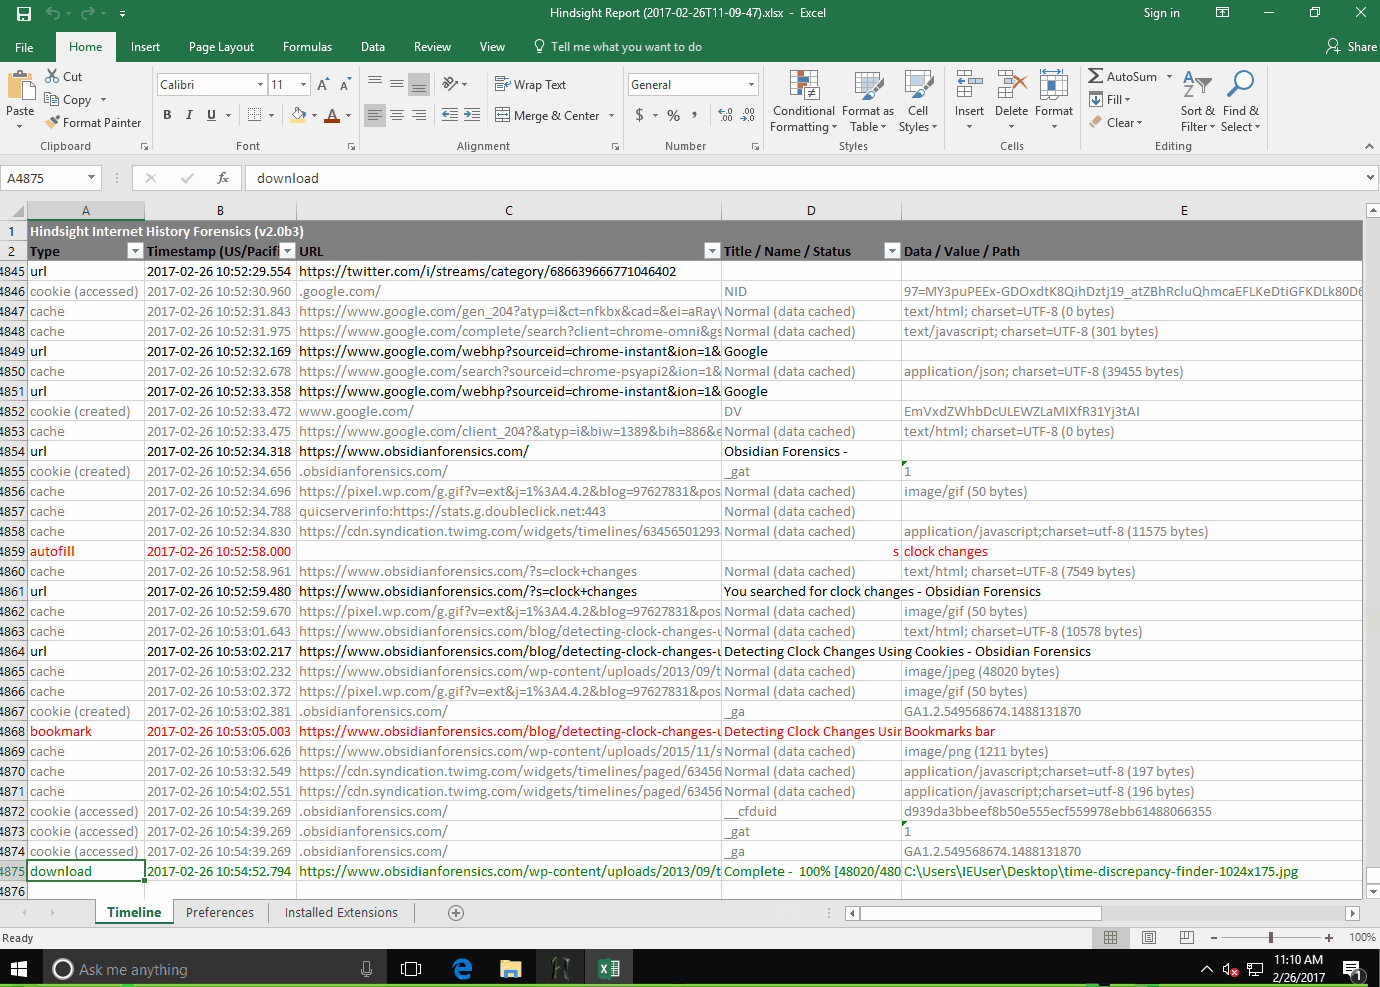 ryandfir/hindsight
Browser forensics tool for Google Chrome, other Chromium-based browsers, and Mozilla Firefox
 redaelli/imago-forensics
Imago is a python tool that extract digital evidences from images.
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 mr-r3b00t/crime-mapper
A tool for mapping cyber crime
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
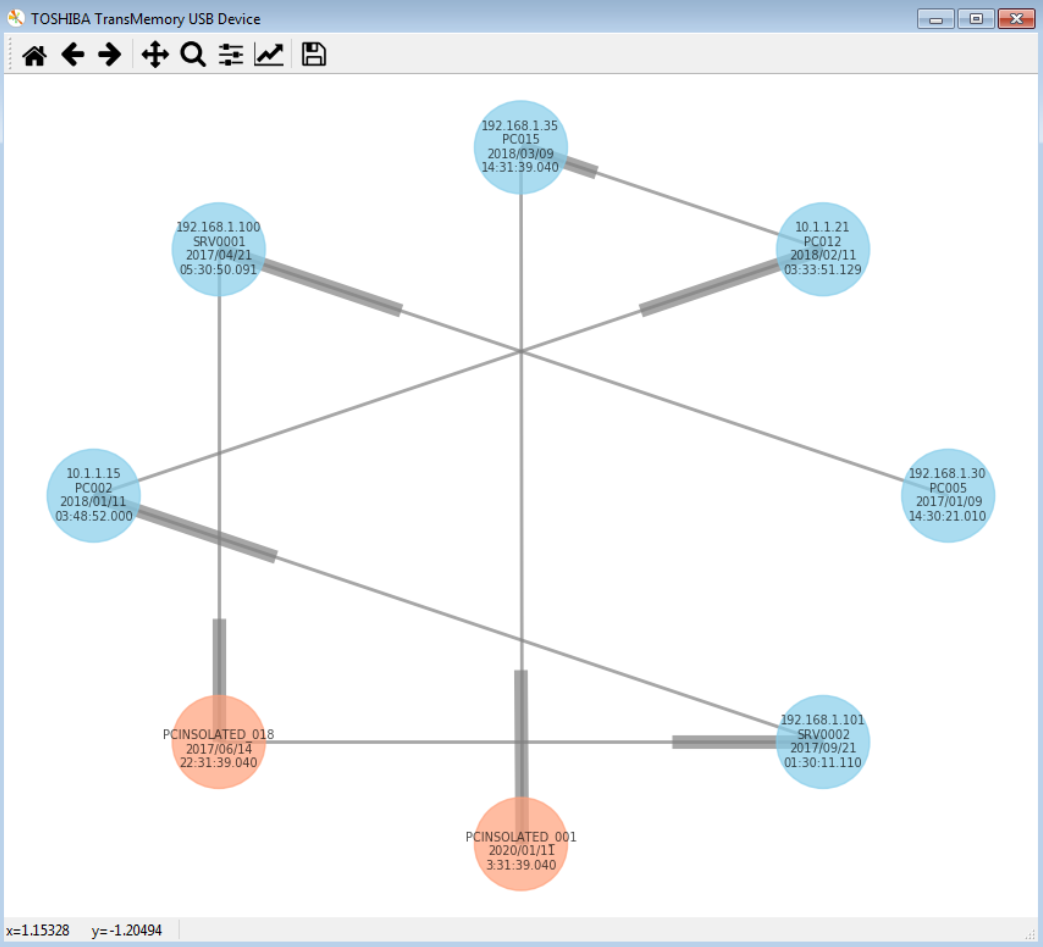 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
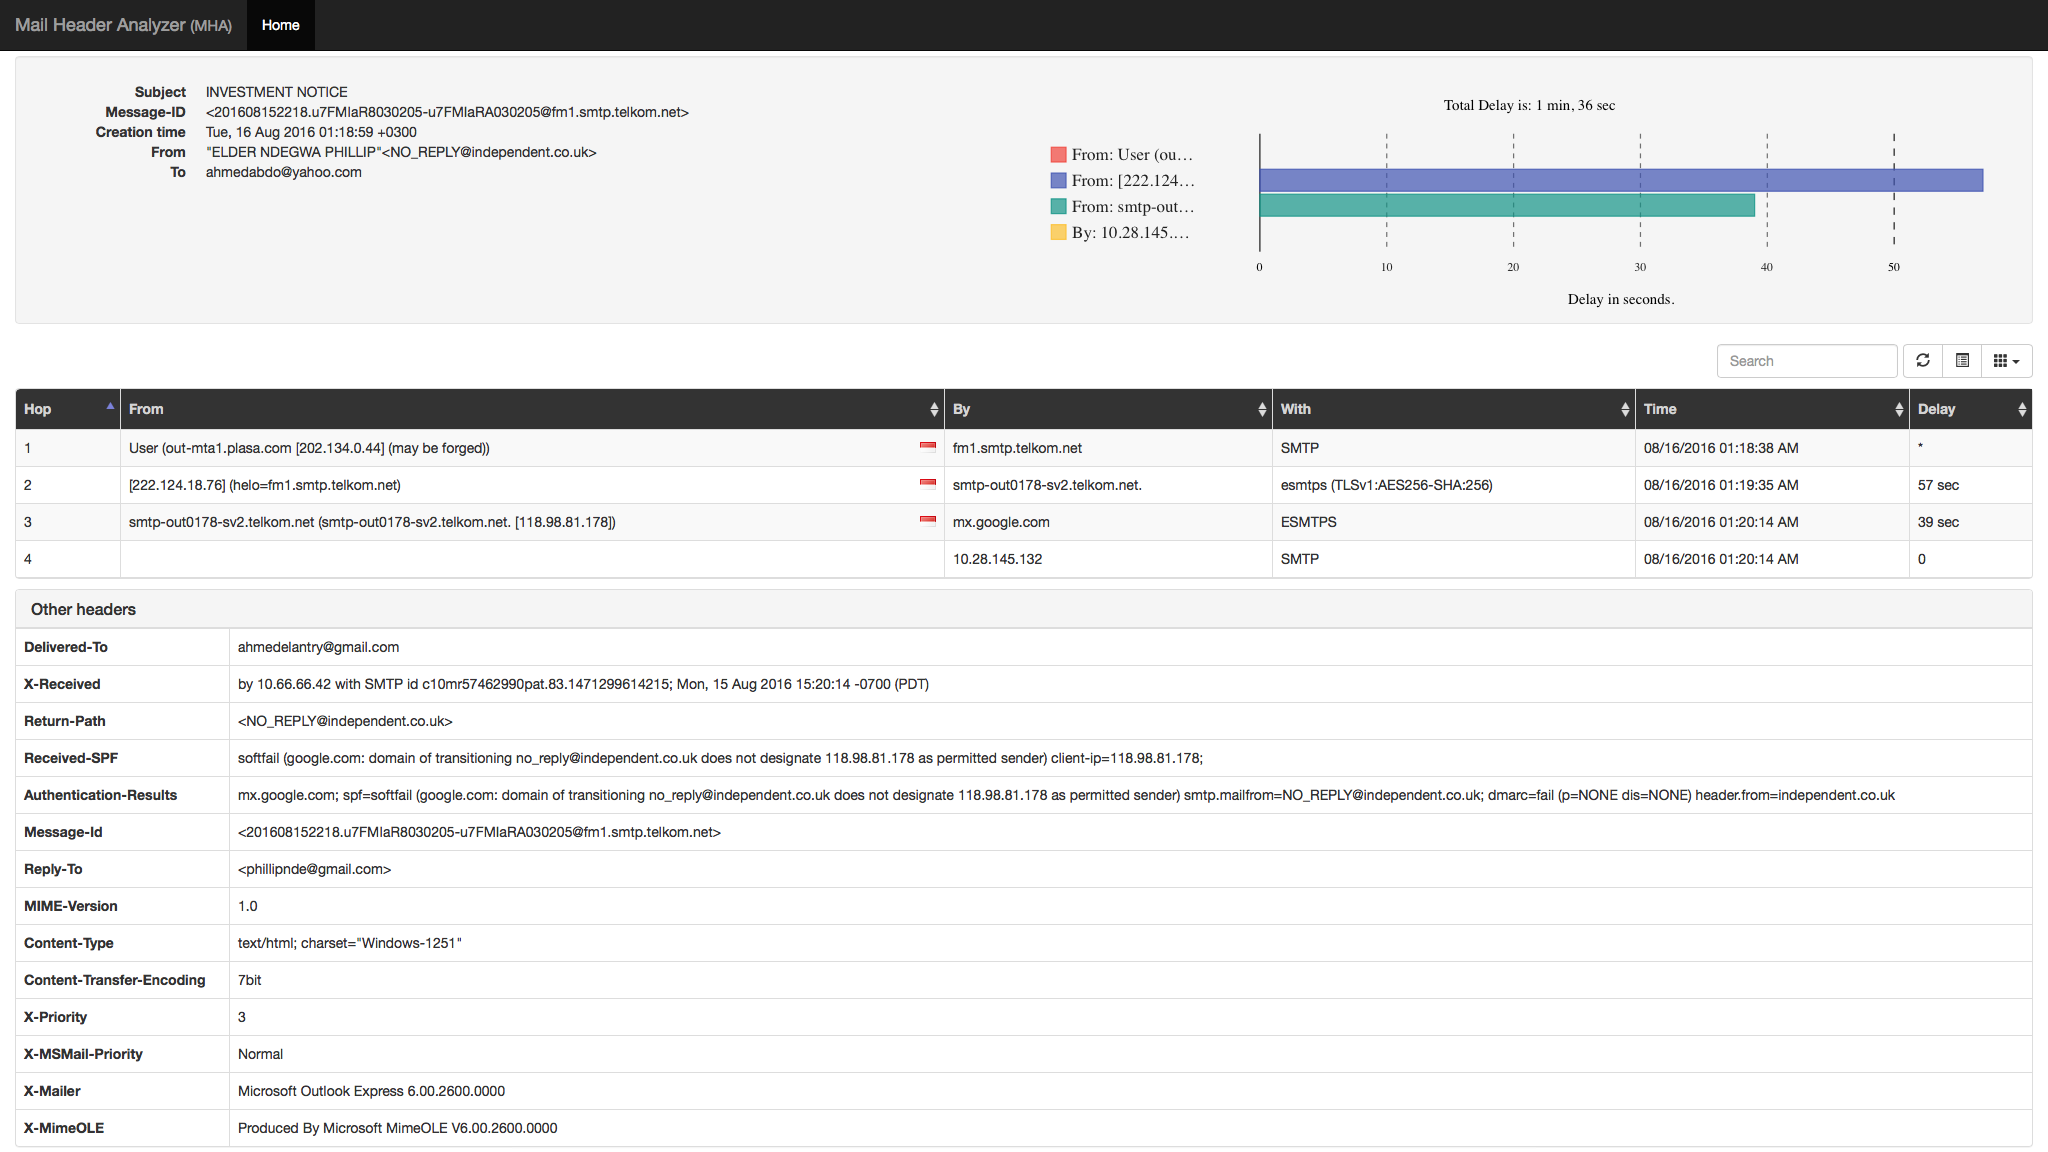 cyberdefenders/email-header-analyzer
E-Mail Header Analyzer
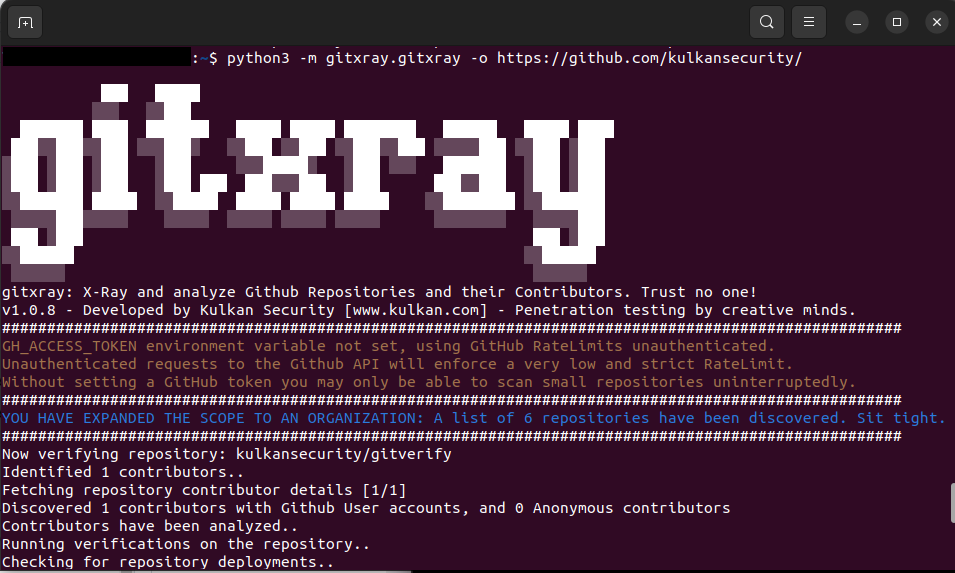 kulkansecurity/gitxray
A multifaceted security tool which leverages Public GitHub REST APIs for OSINT, Forensics, Pentesting and more.
 nccgroup/metadataplus
A tool to use novel locations to extract metadata from Office documents.