
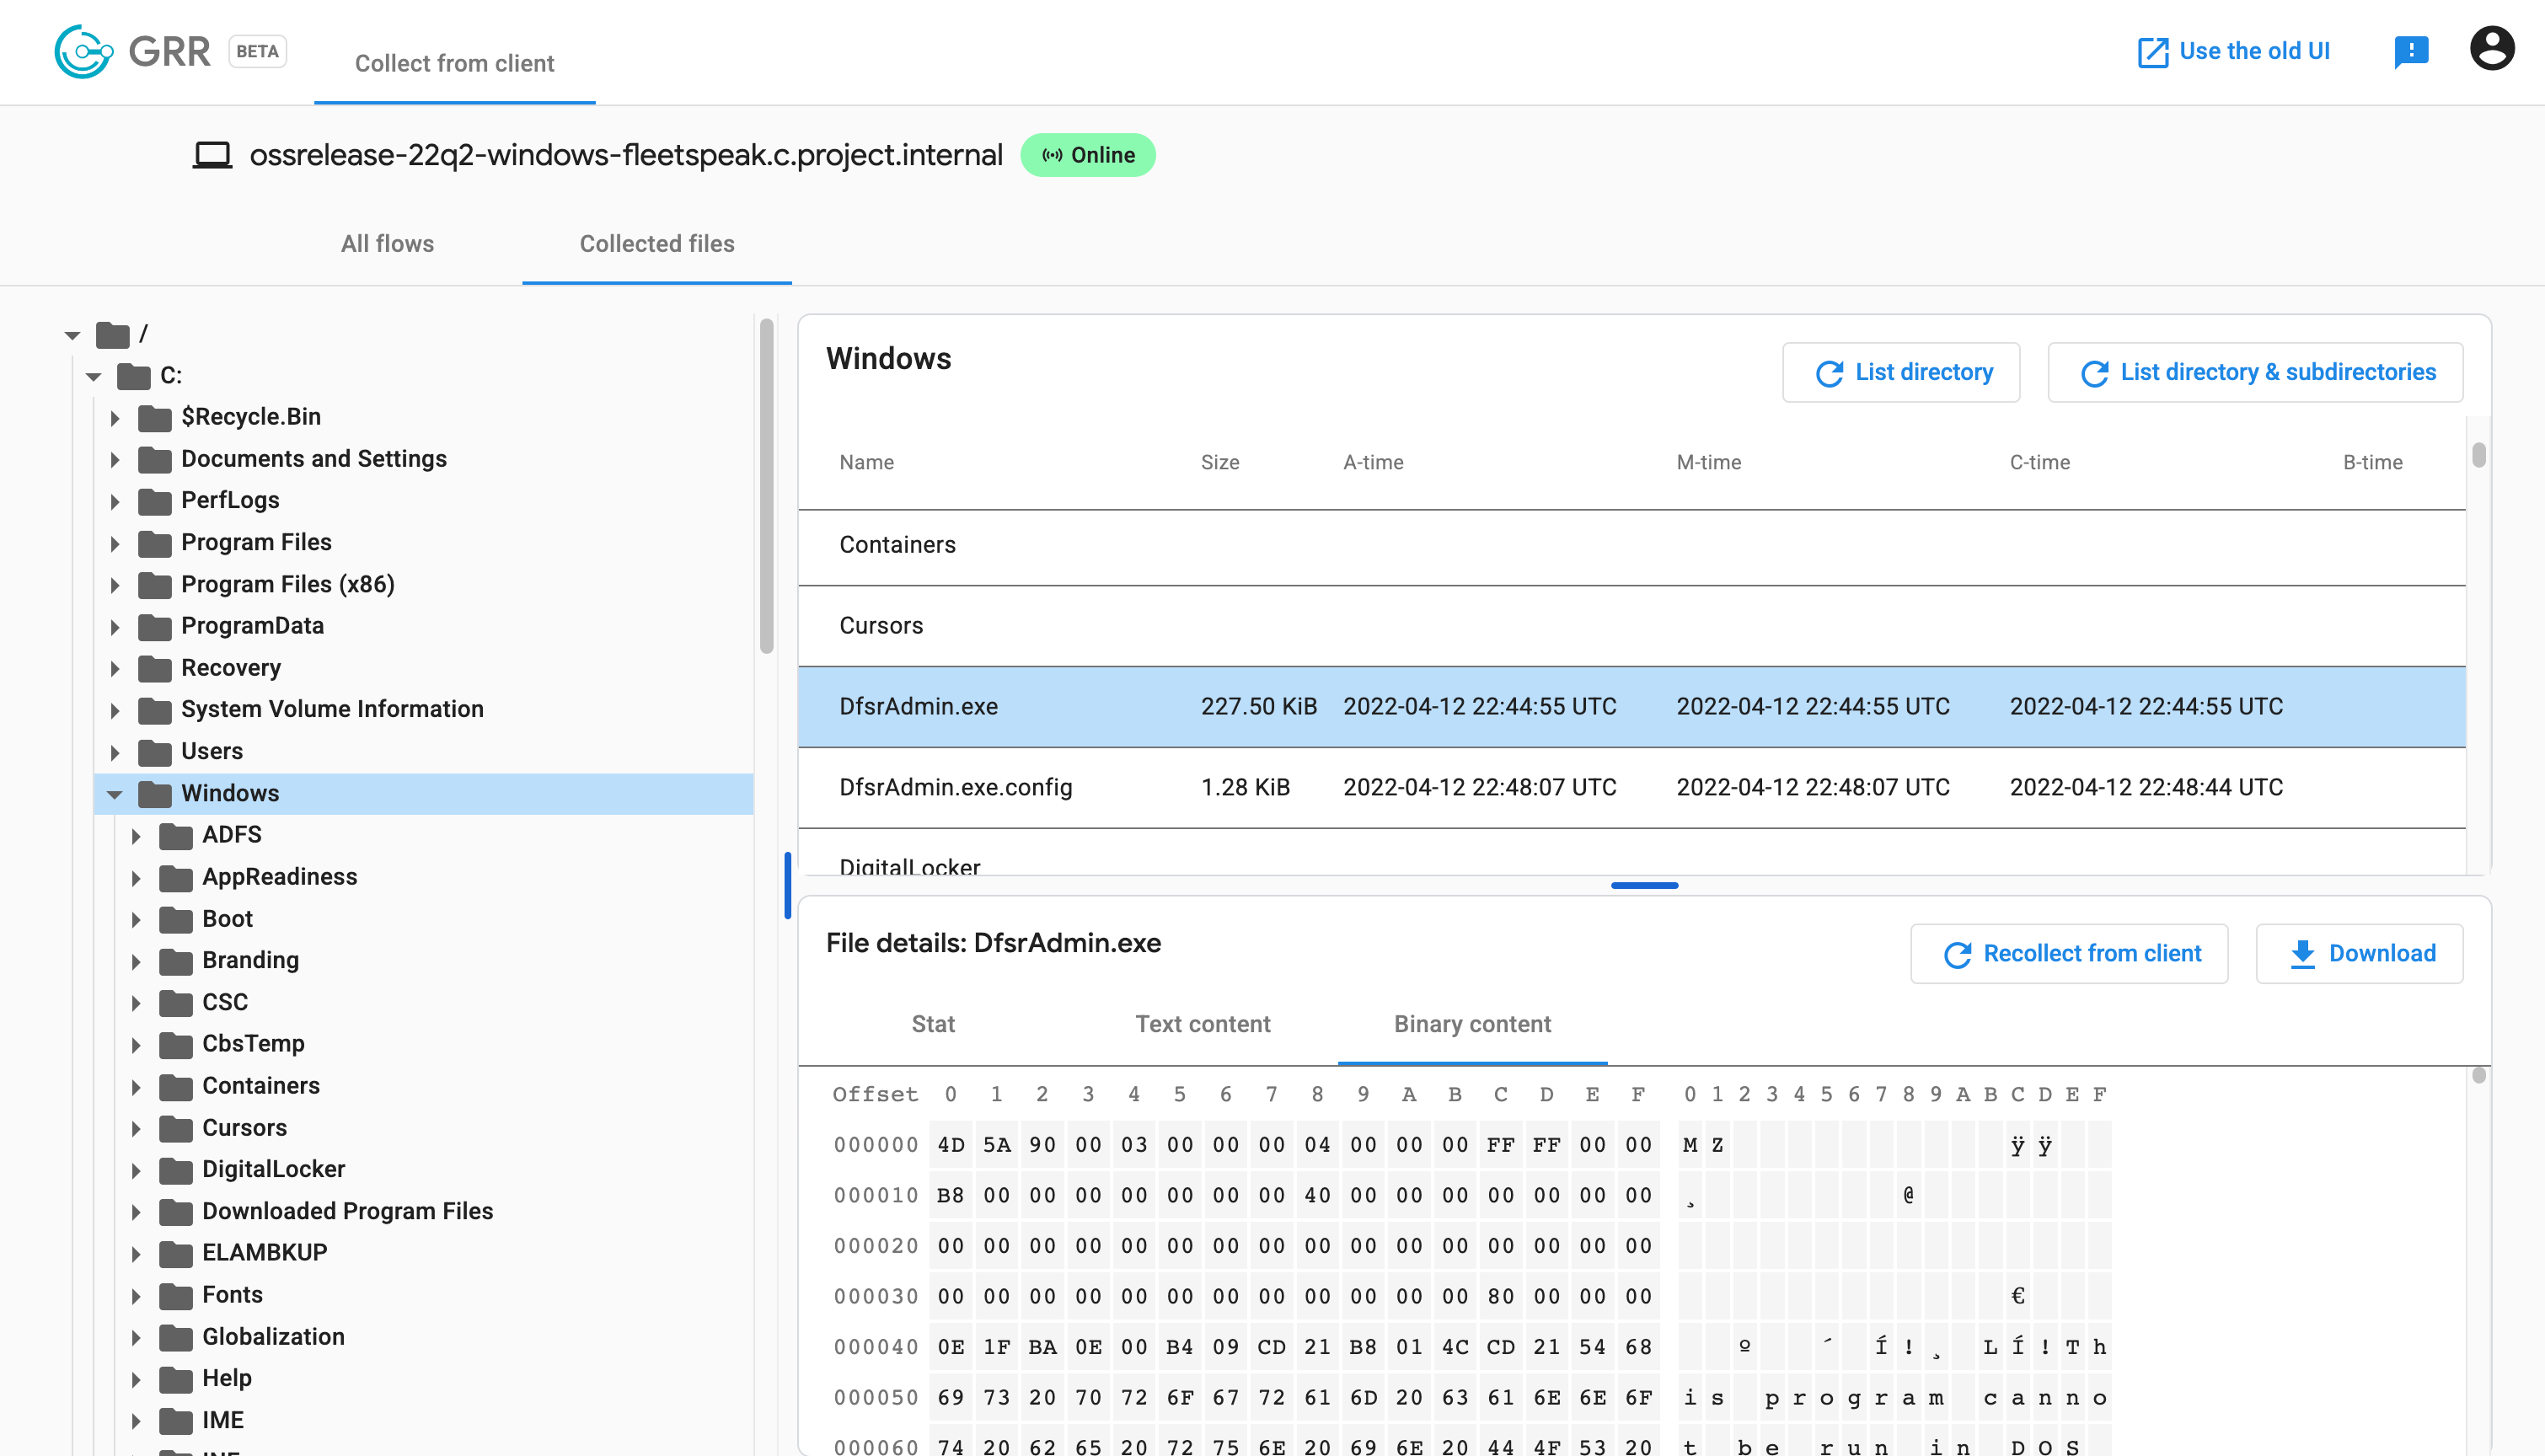
grr
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k1 month ago
google/grrRemote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 volatilityfoundation/volatility
An advanced memory forensics framework
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 omriher/captipper
Malicious HTTP traffic explorer
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics