
Archived
HAFNIUM-IOC
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
digital-forensicsforensicsincident-response+3
soteria-security/hafnium-iocA PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
 itres-labs/cve-2025-31702
Repository with tools, exploits, and material associated with the analysis and discovery process of CVE-2025-31702 and other related security issues.
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 jwa7470/cve-2026-20131-post-incident-written-report
Post-incident report on CVE-2026-20131 (CVSS 10.0), a Cisco FMC insecure deserialization vulnerability exploited by Interlock ransomware. Details…
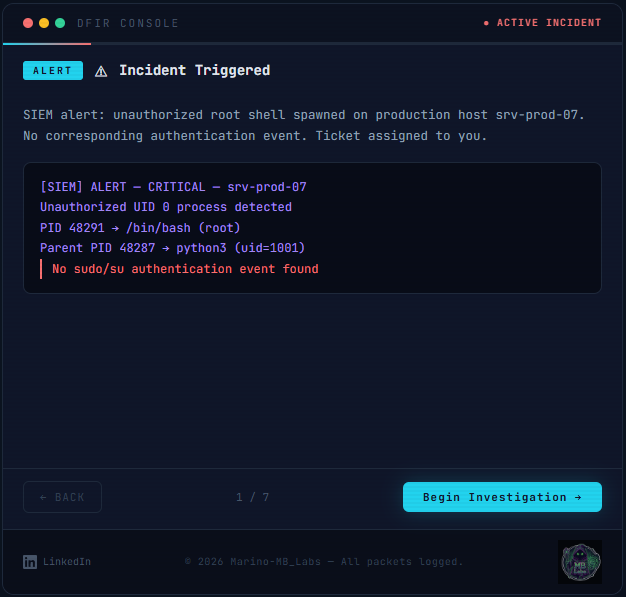 ledlight33/copyfail-dfir
Interactive DFIR walkthrough of CVE-2026-31431 (Copy Fail) - from SIEM alert to confirmed verdict. Real Volatility 3 commands, verified methodology.
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
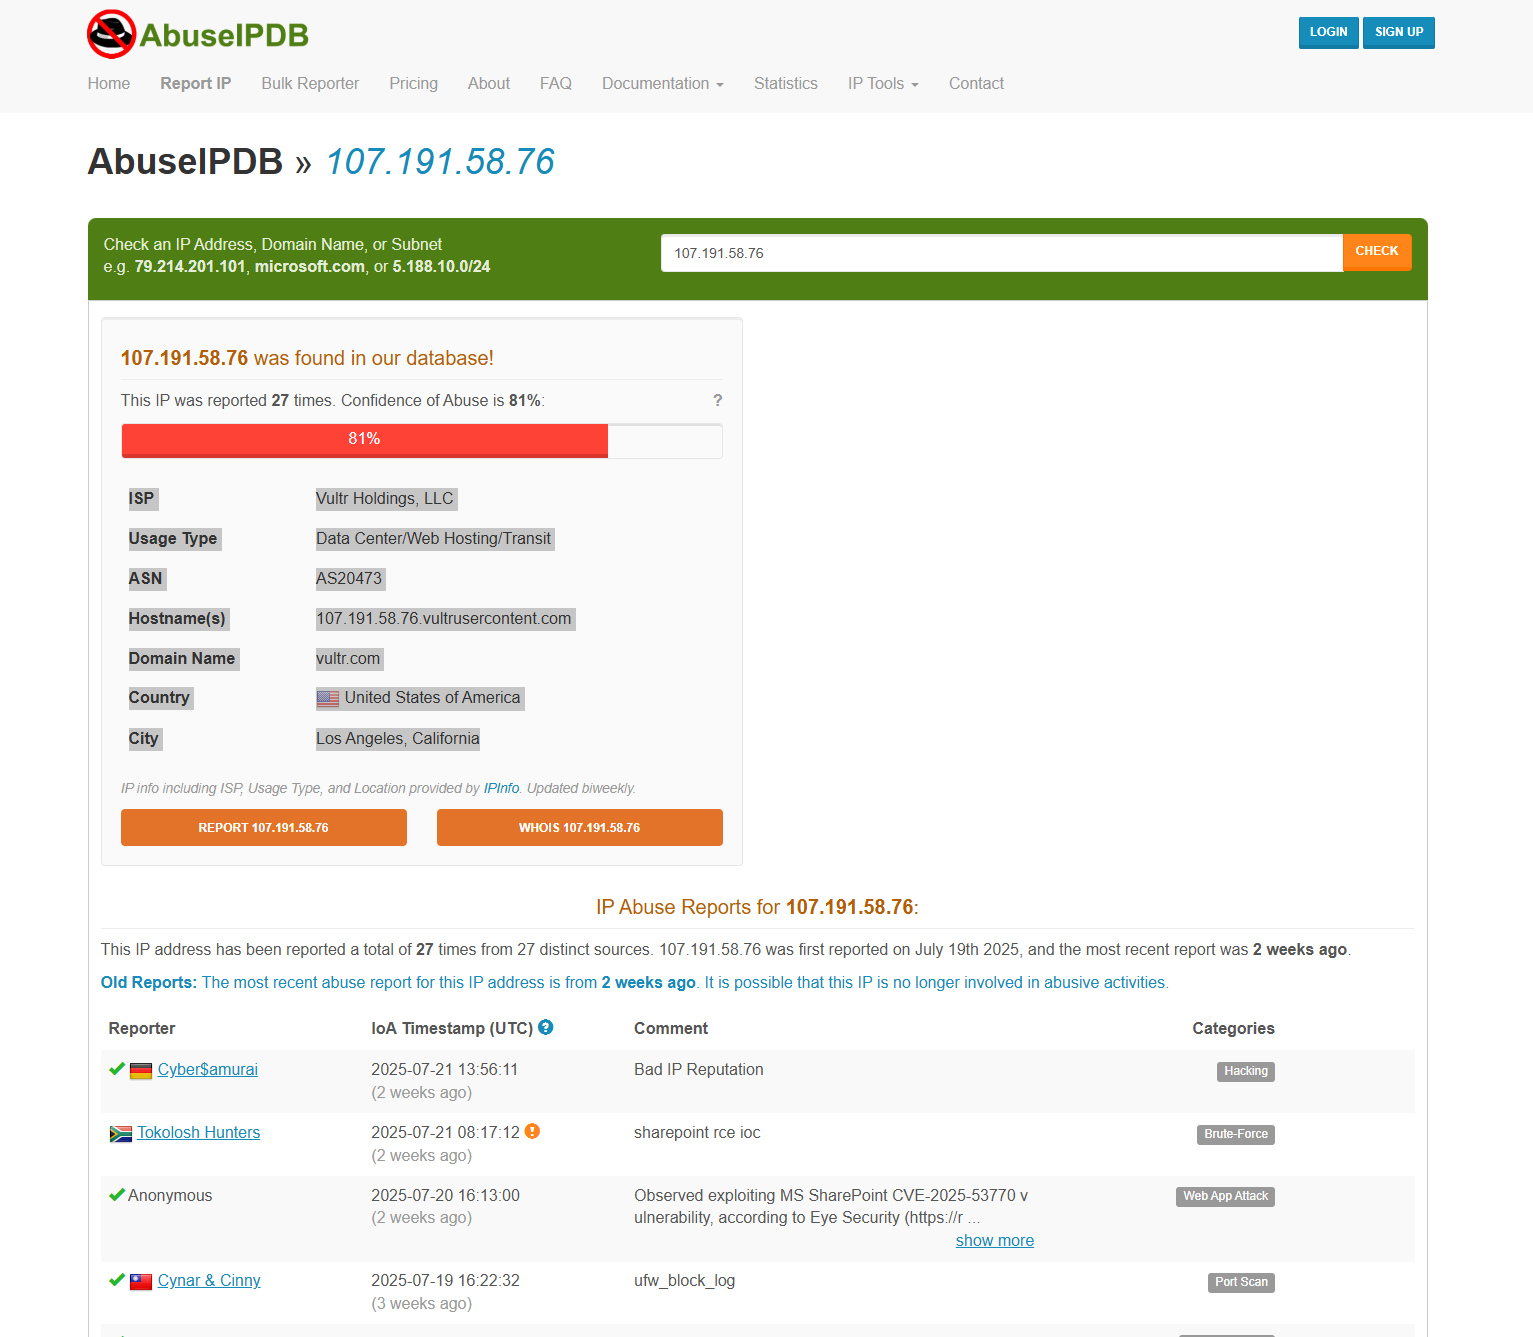 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
 fevar54/cve-2026-68820-mitigation-poc-
Demostracion educativa de mitigacion de CVE-2026-68820: Use-After-Free en afd.sys de Windows.
 vignesh-hp/lockbit-ransomware-analysis
Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
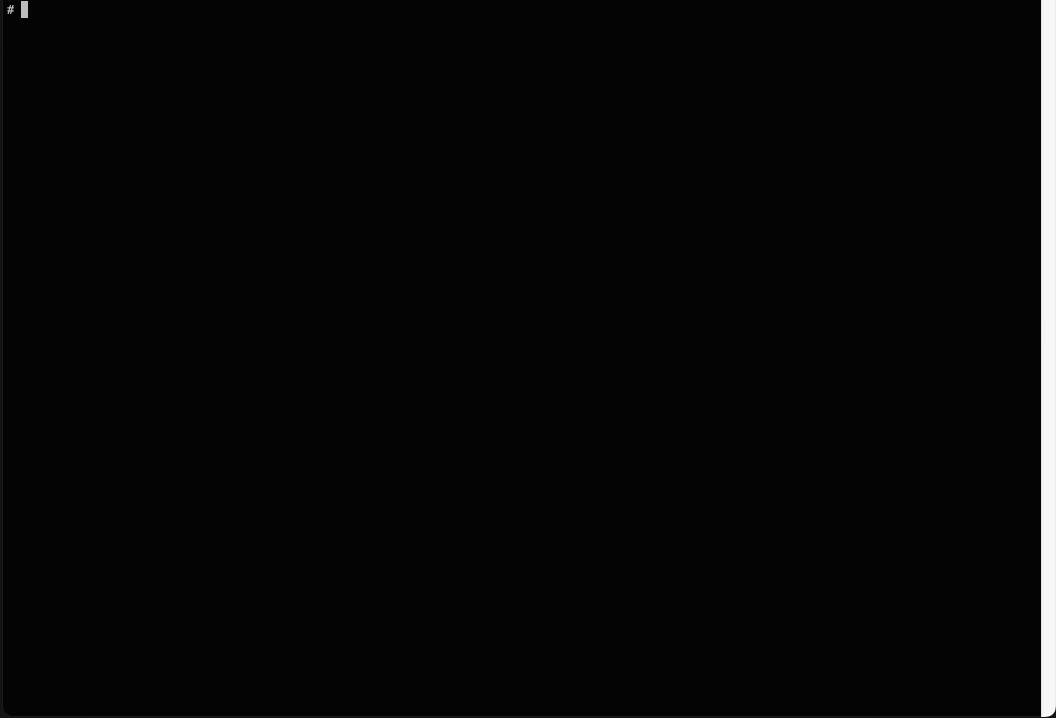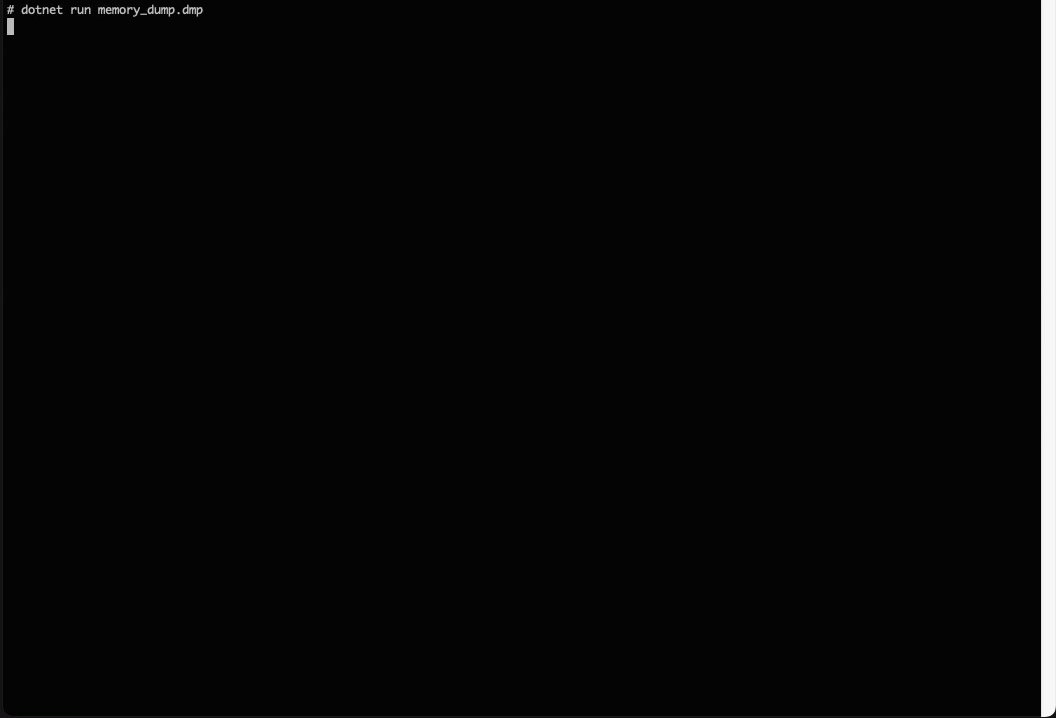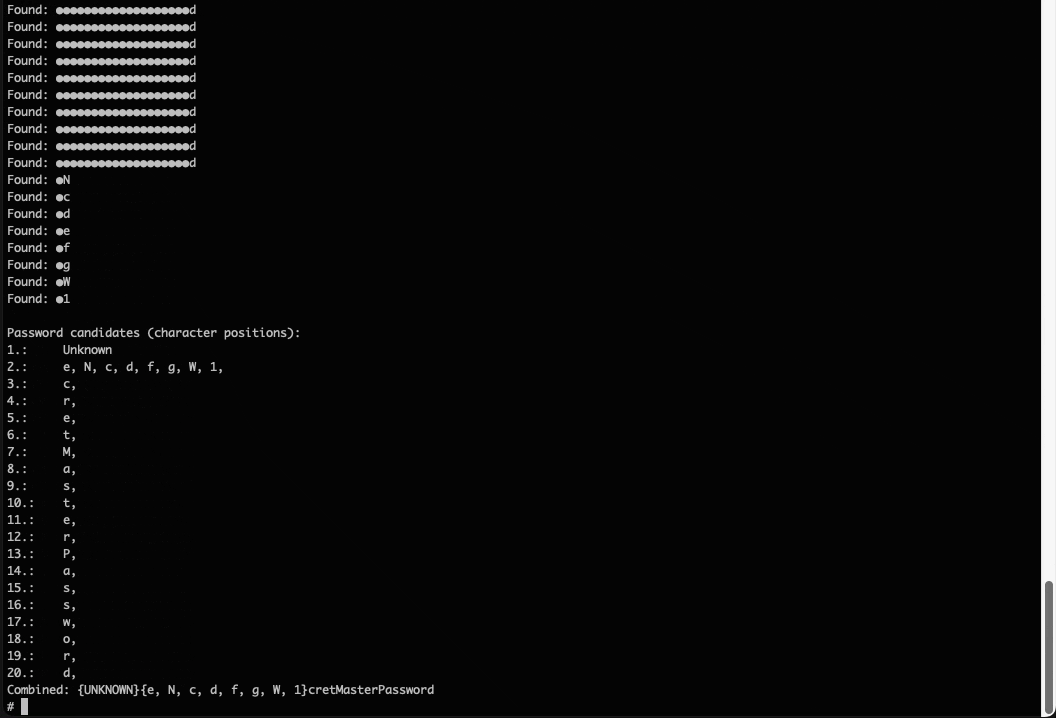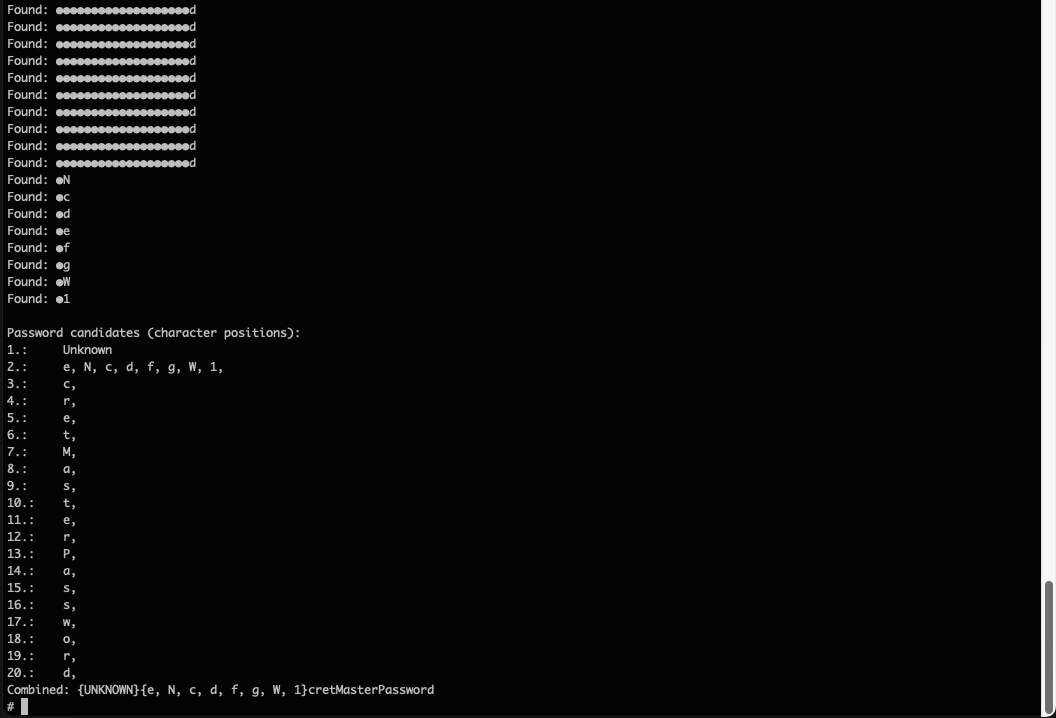 vdohney/keepass-password-dumper
Original PoC for CVE-2023-32784