citrix-netscaler-triage

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.

Script for automating Linux memory capture and analysis

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252

Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…

Add POST body excerpt to Bro's HTTP log

Extract AutoIt scripts embedded in PE binaries

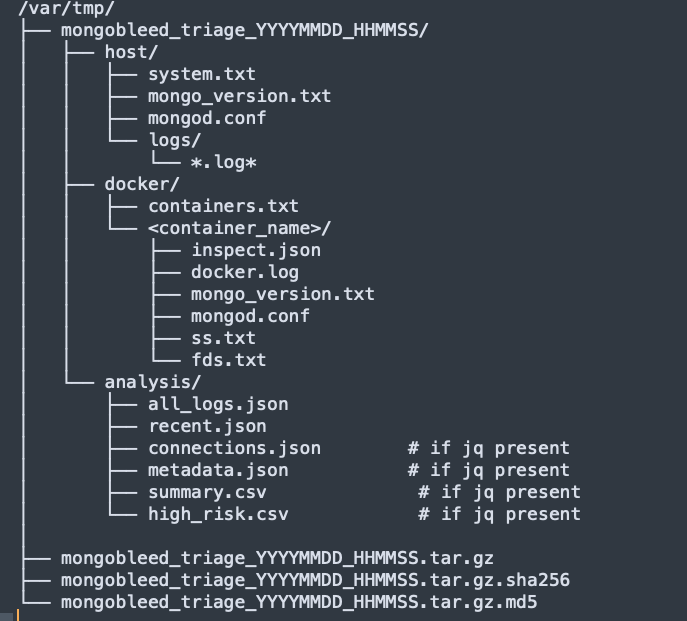
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…


A forensic evidence collection & analysis toolkit for OS X

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

A python script for digital image steganography using Fast Fourier Transform.

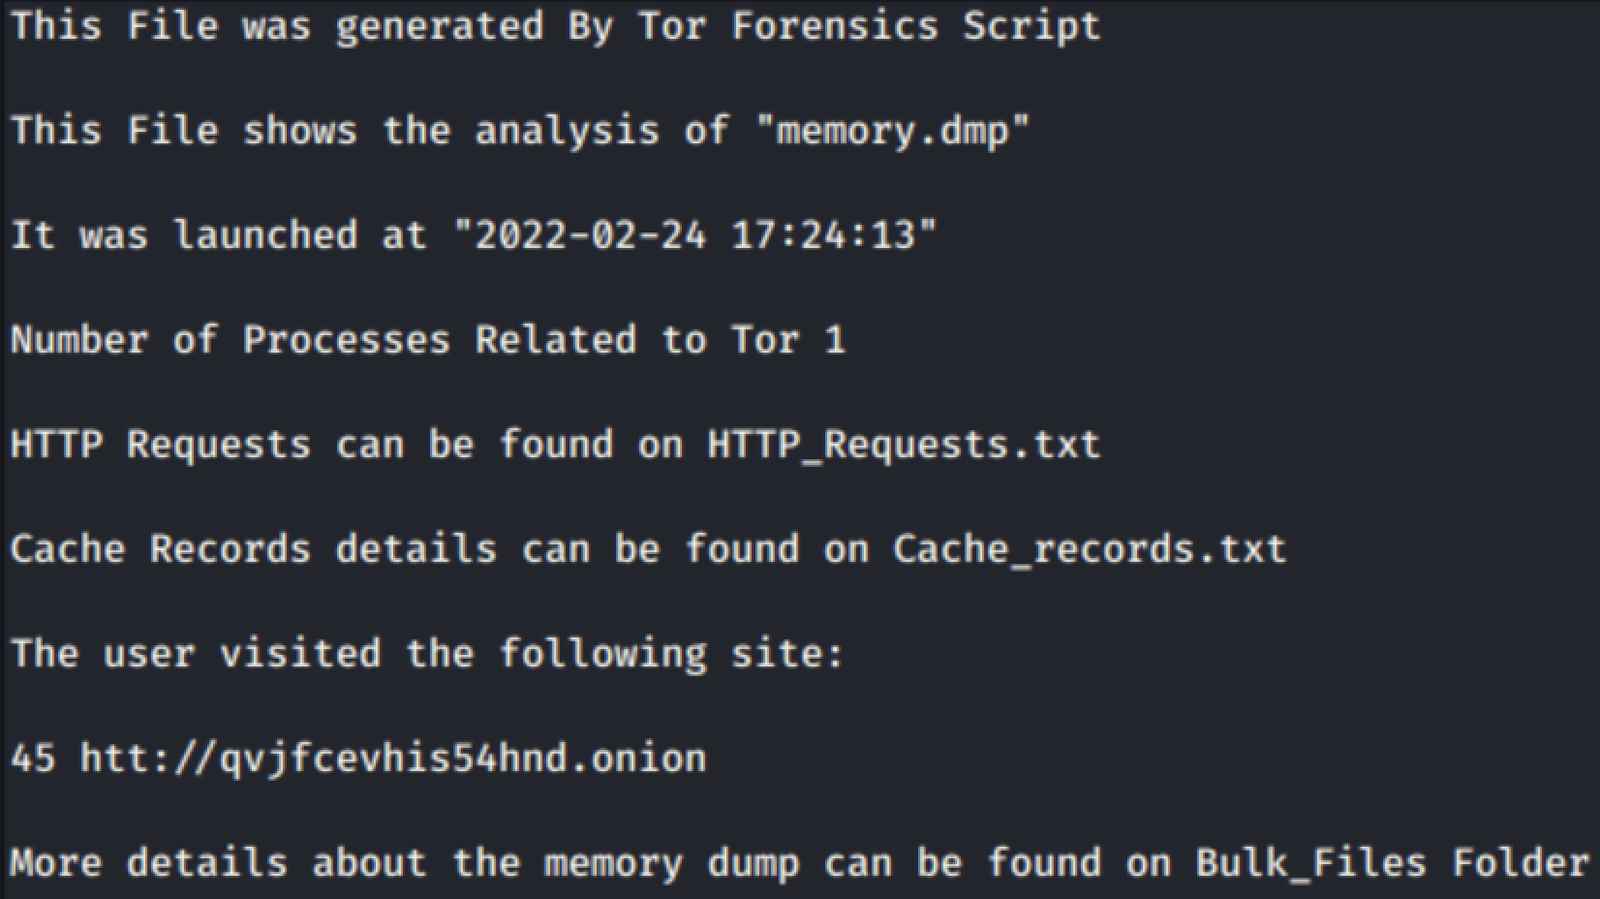
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…

Incident Response collection and processing scripts with automated reporting scripts