rails-activestorage-vips-audit

Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…

Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…

Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…

A static analysis security vulnerability scanner for Ruby on Rails applications

Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…

Patch CVE-2020-5267 for Rails 4 and Rails 3

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

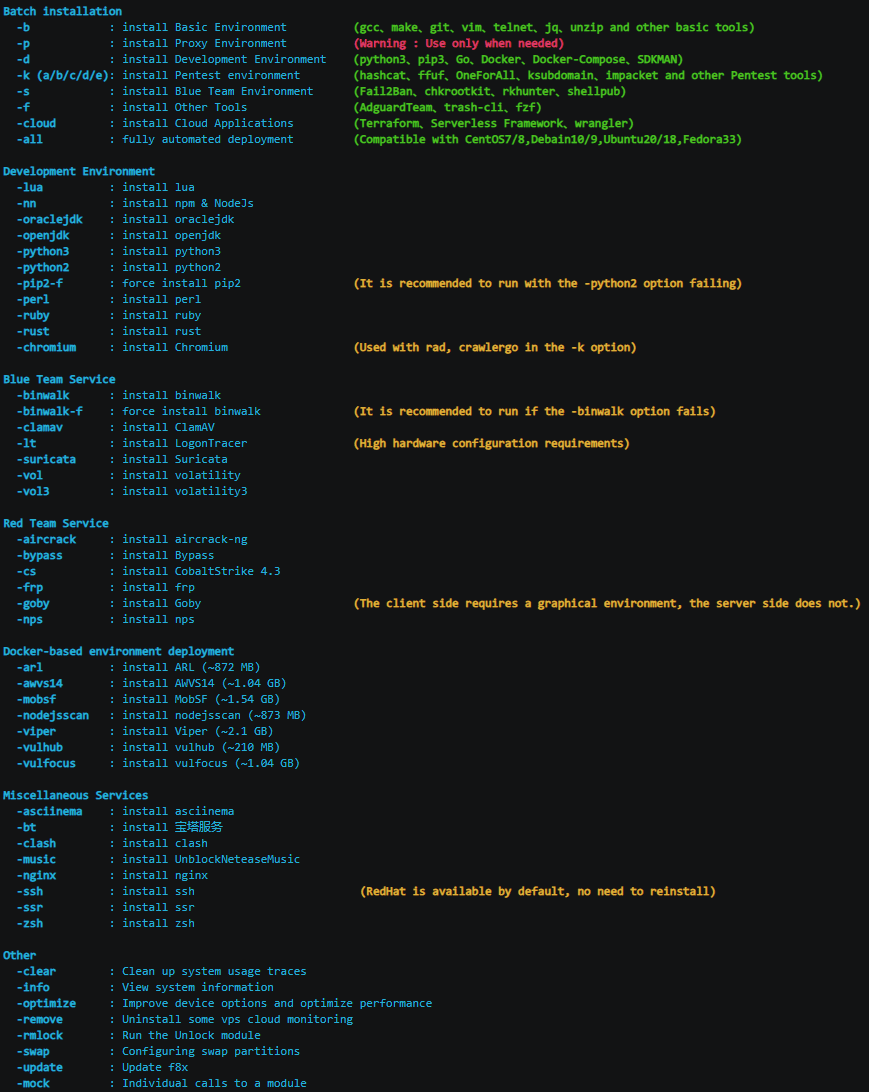
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

SecureML - Securing and Watermarking AL models

Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.