
enject
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
authenticationcloud-securitydevsecops+3
503
greatscott/enjectenject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 aws-samples/kubernetes-log4j-cve-2021-44228-node-agent
Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
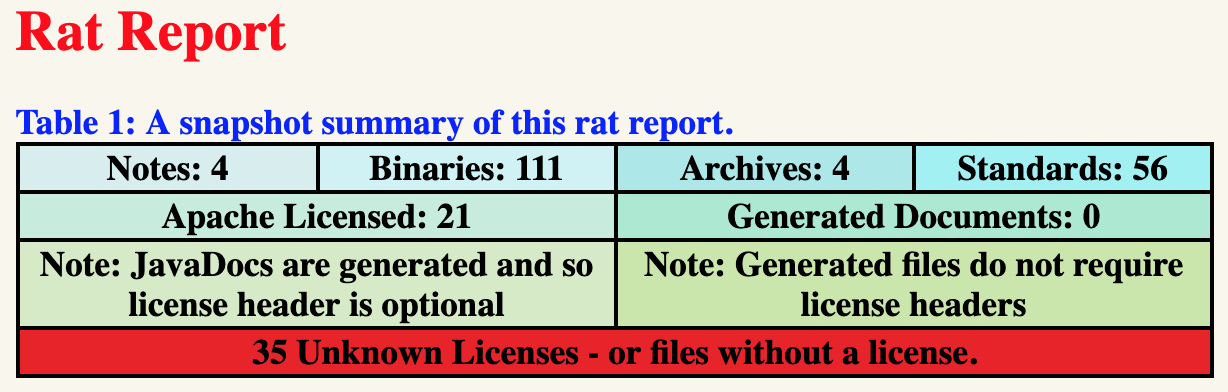 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 owasp/docksec
AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…

 components/dependency-scanning
Generates CycloneDX SBOMs and dependency scanning reports to identify project dependencies, licenses, and vulnerabilities within GitLab CI/CD…
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…