

ShipProof
 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
cloud-securitycode-analysisconfiguration-auditing+6
divyanshukumar0014/shipproofSOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
 adversis/tailsnitch
A security auditor for Tailscale configurations. Scans your tailnet for misconfigurations, overly permissive access controls, and security best…
 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
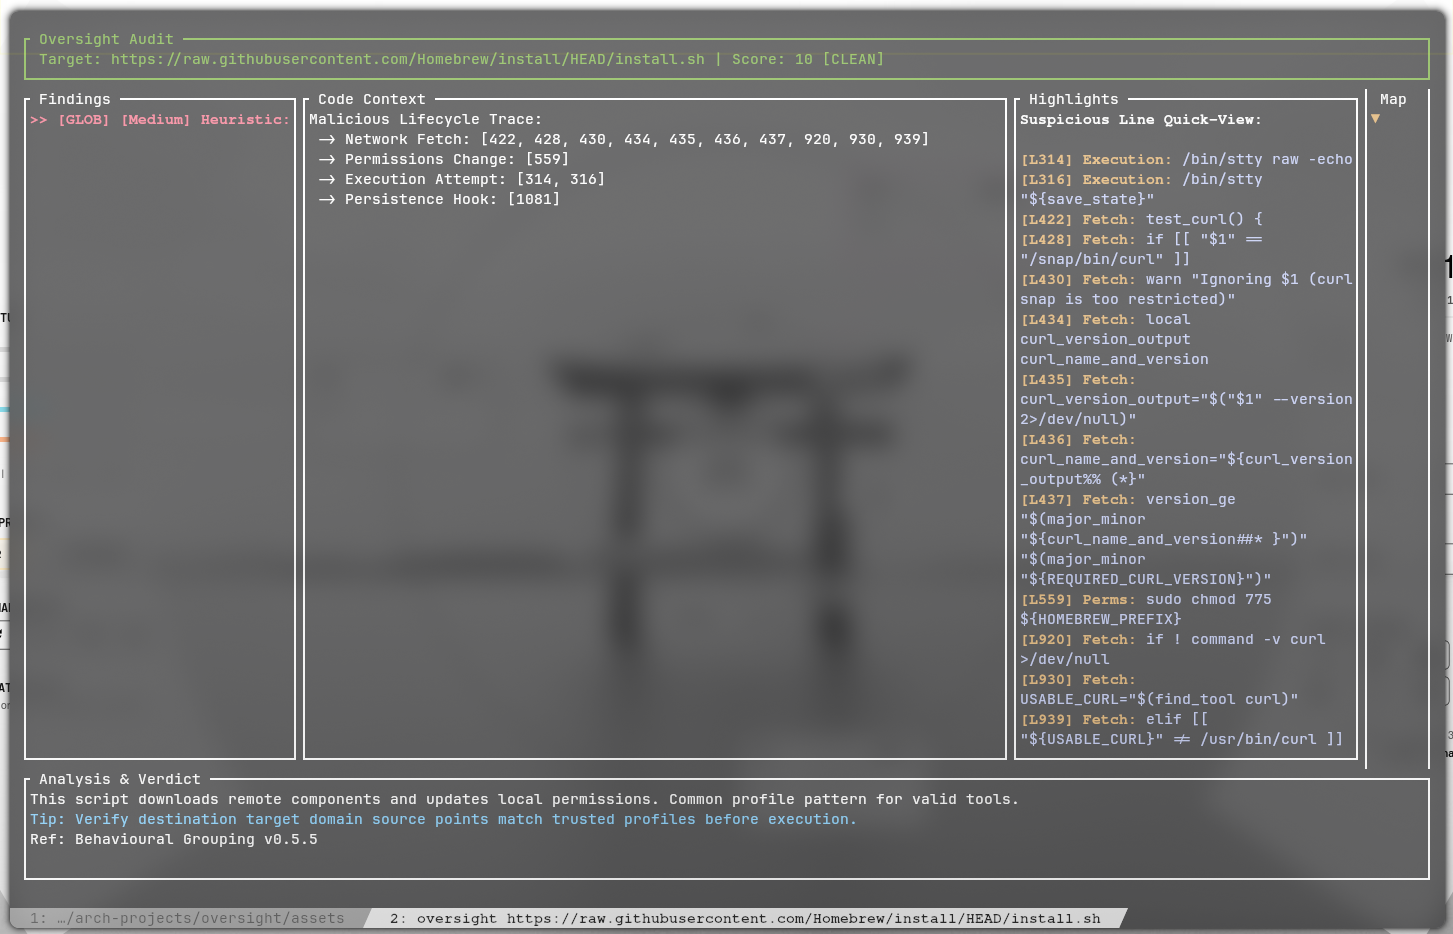 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
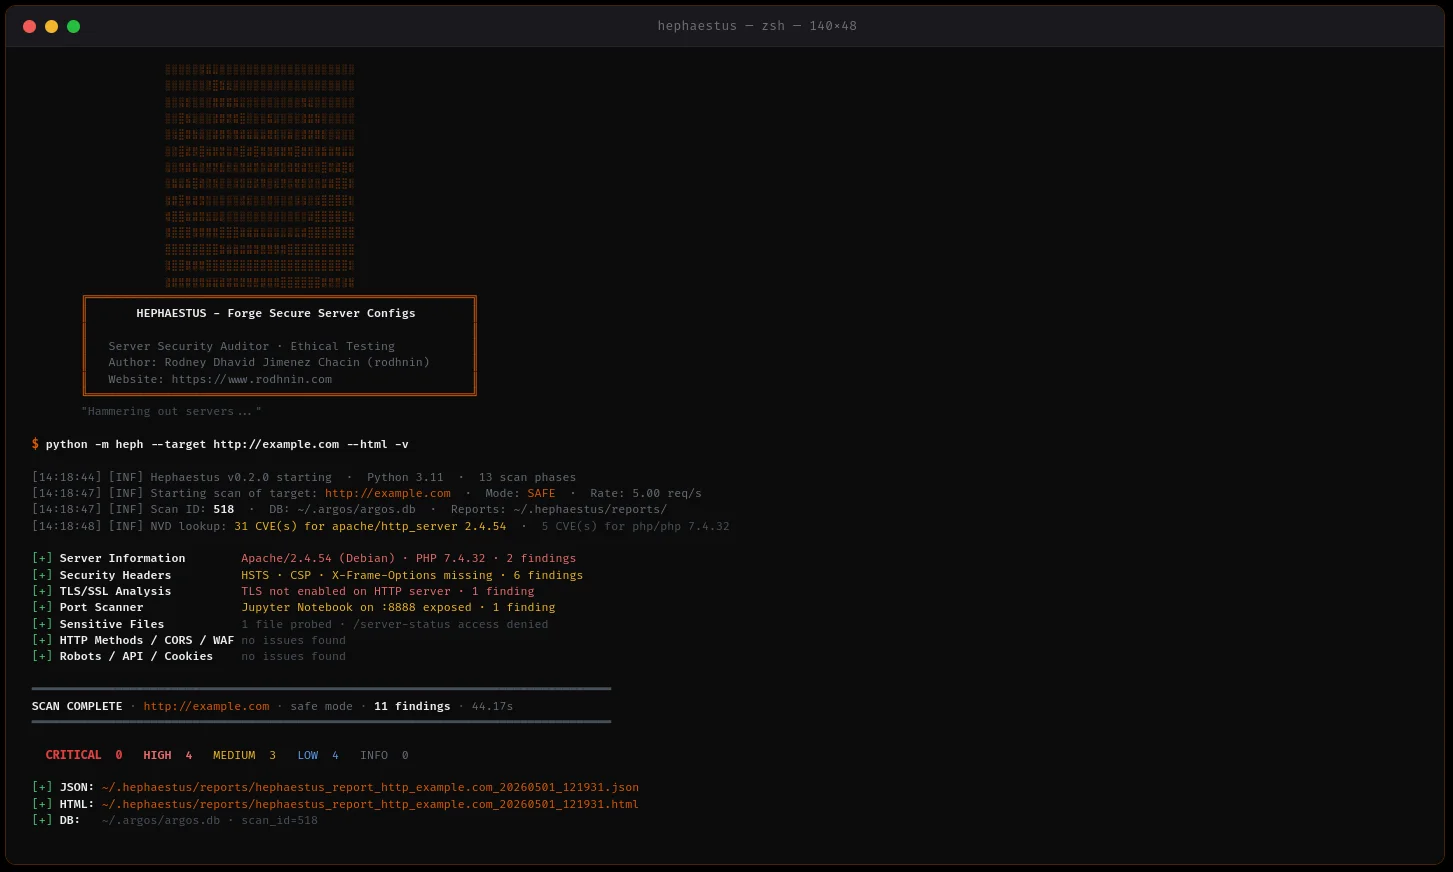 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.