

gitleaks
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
code-analysisdevsecopssecret-detection+3
30.1k
gitleaks/gitleaksFast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
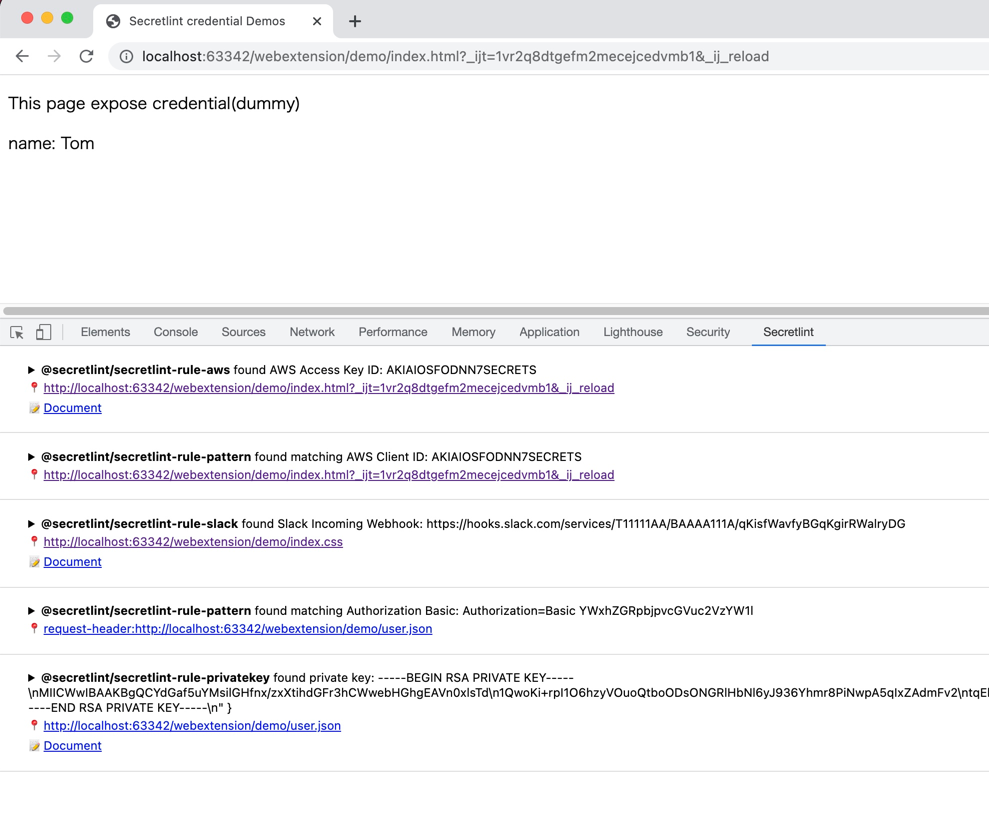 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
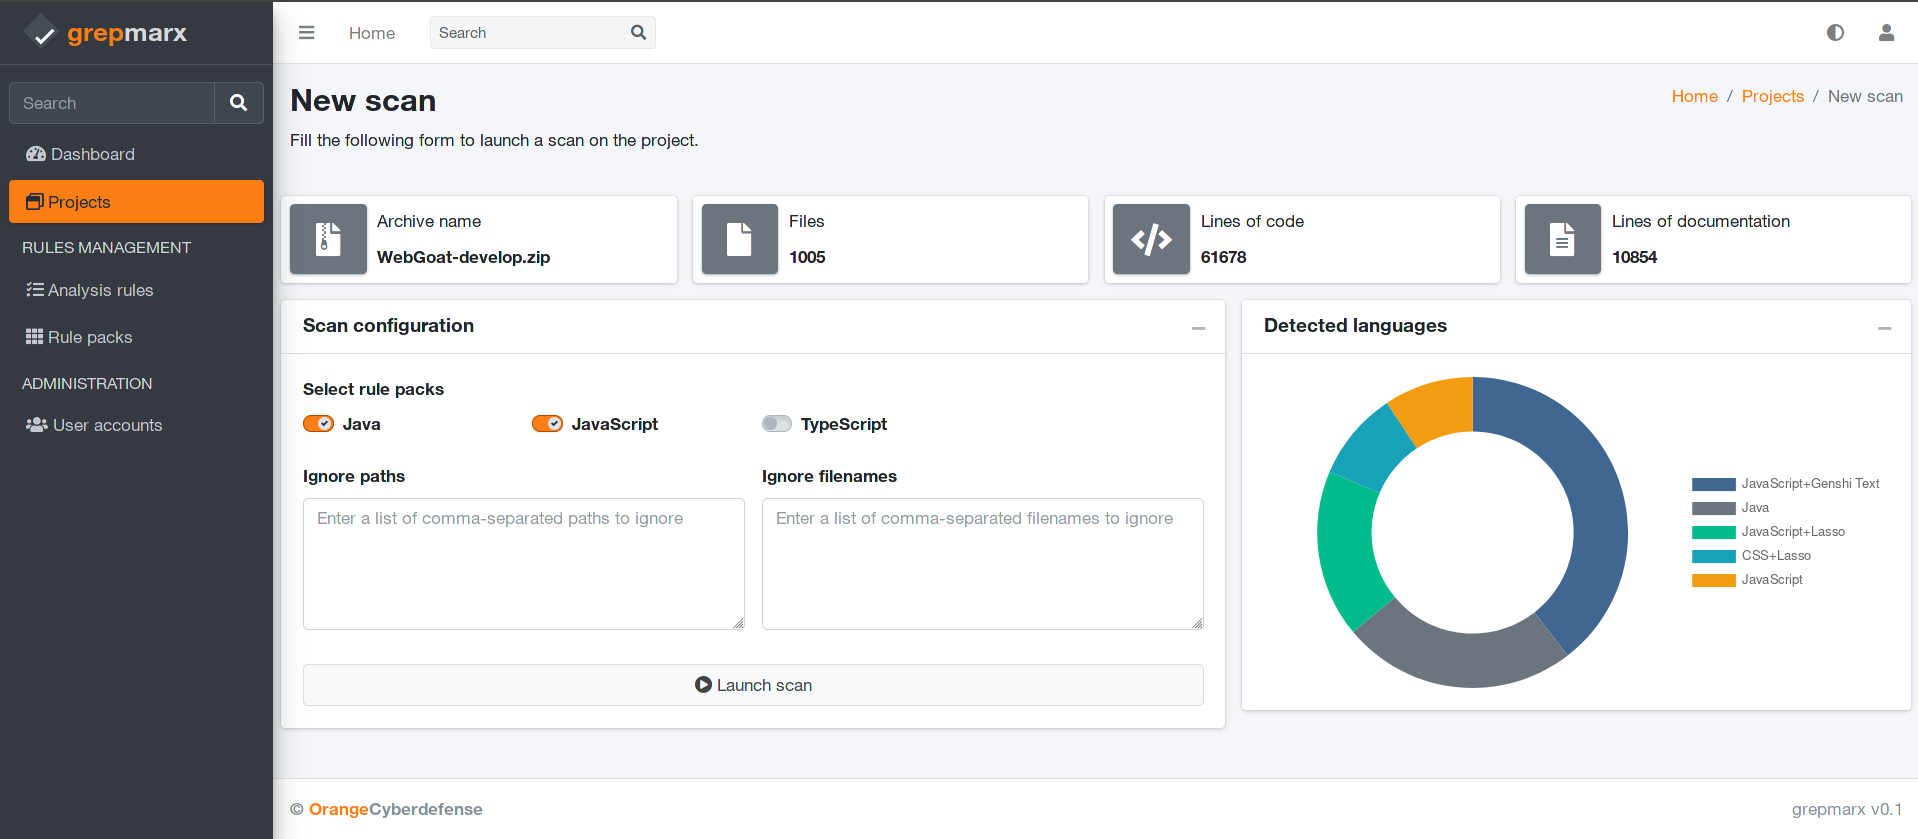 orange-cyberdefense/grepmarx
A source code static analysis platform for AppSec enthusiasts.
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
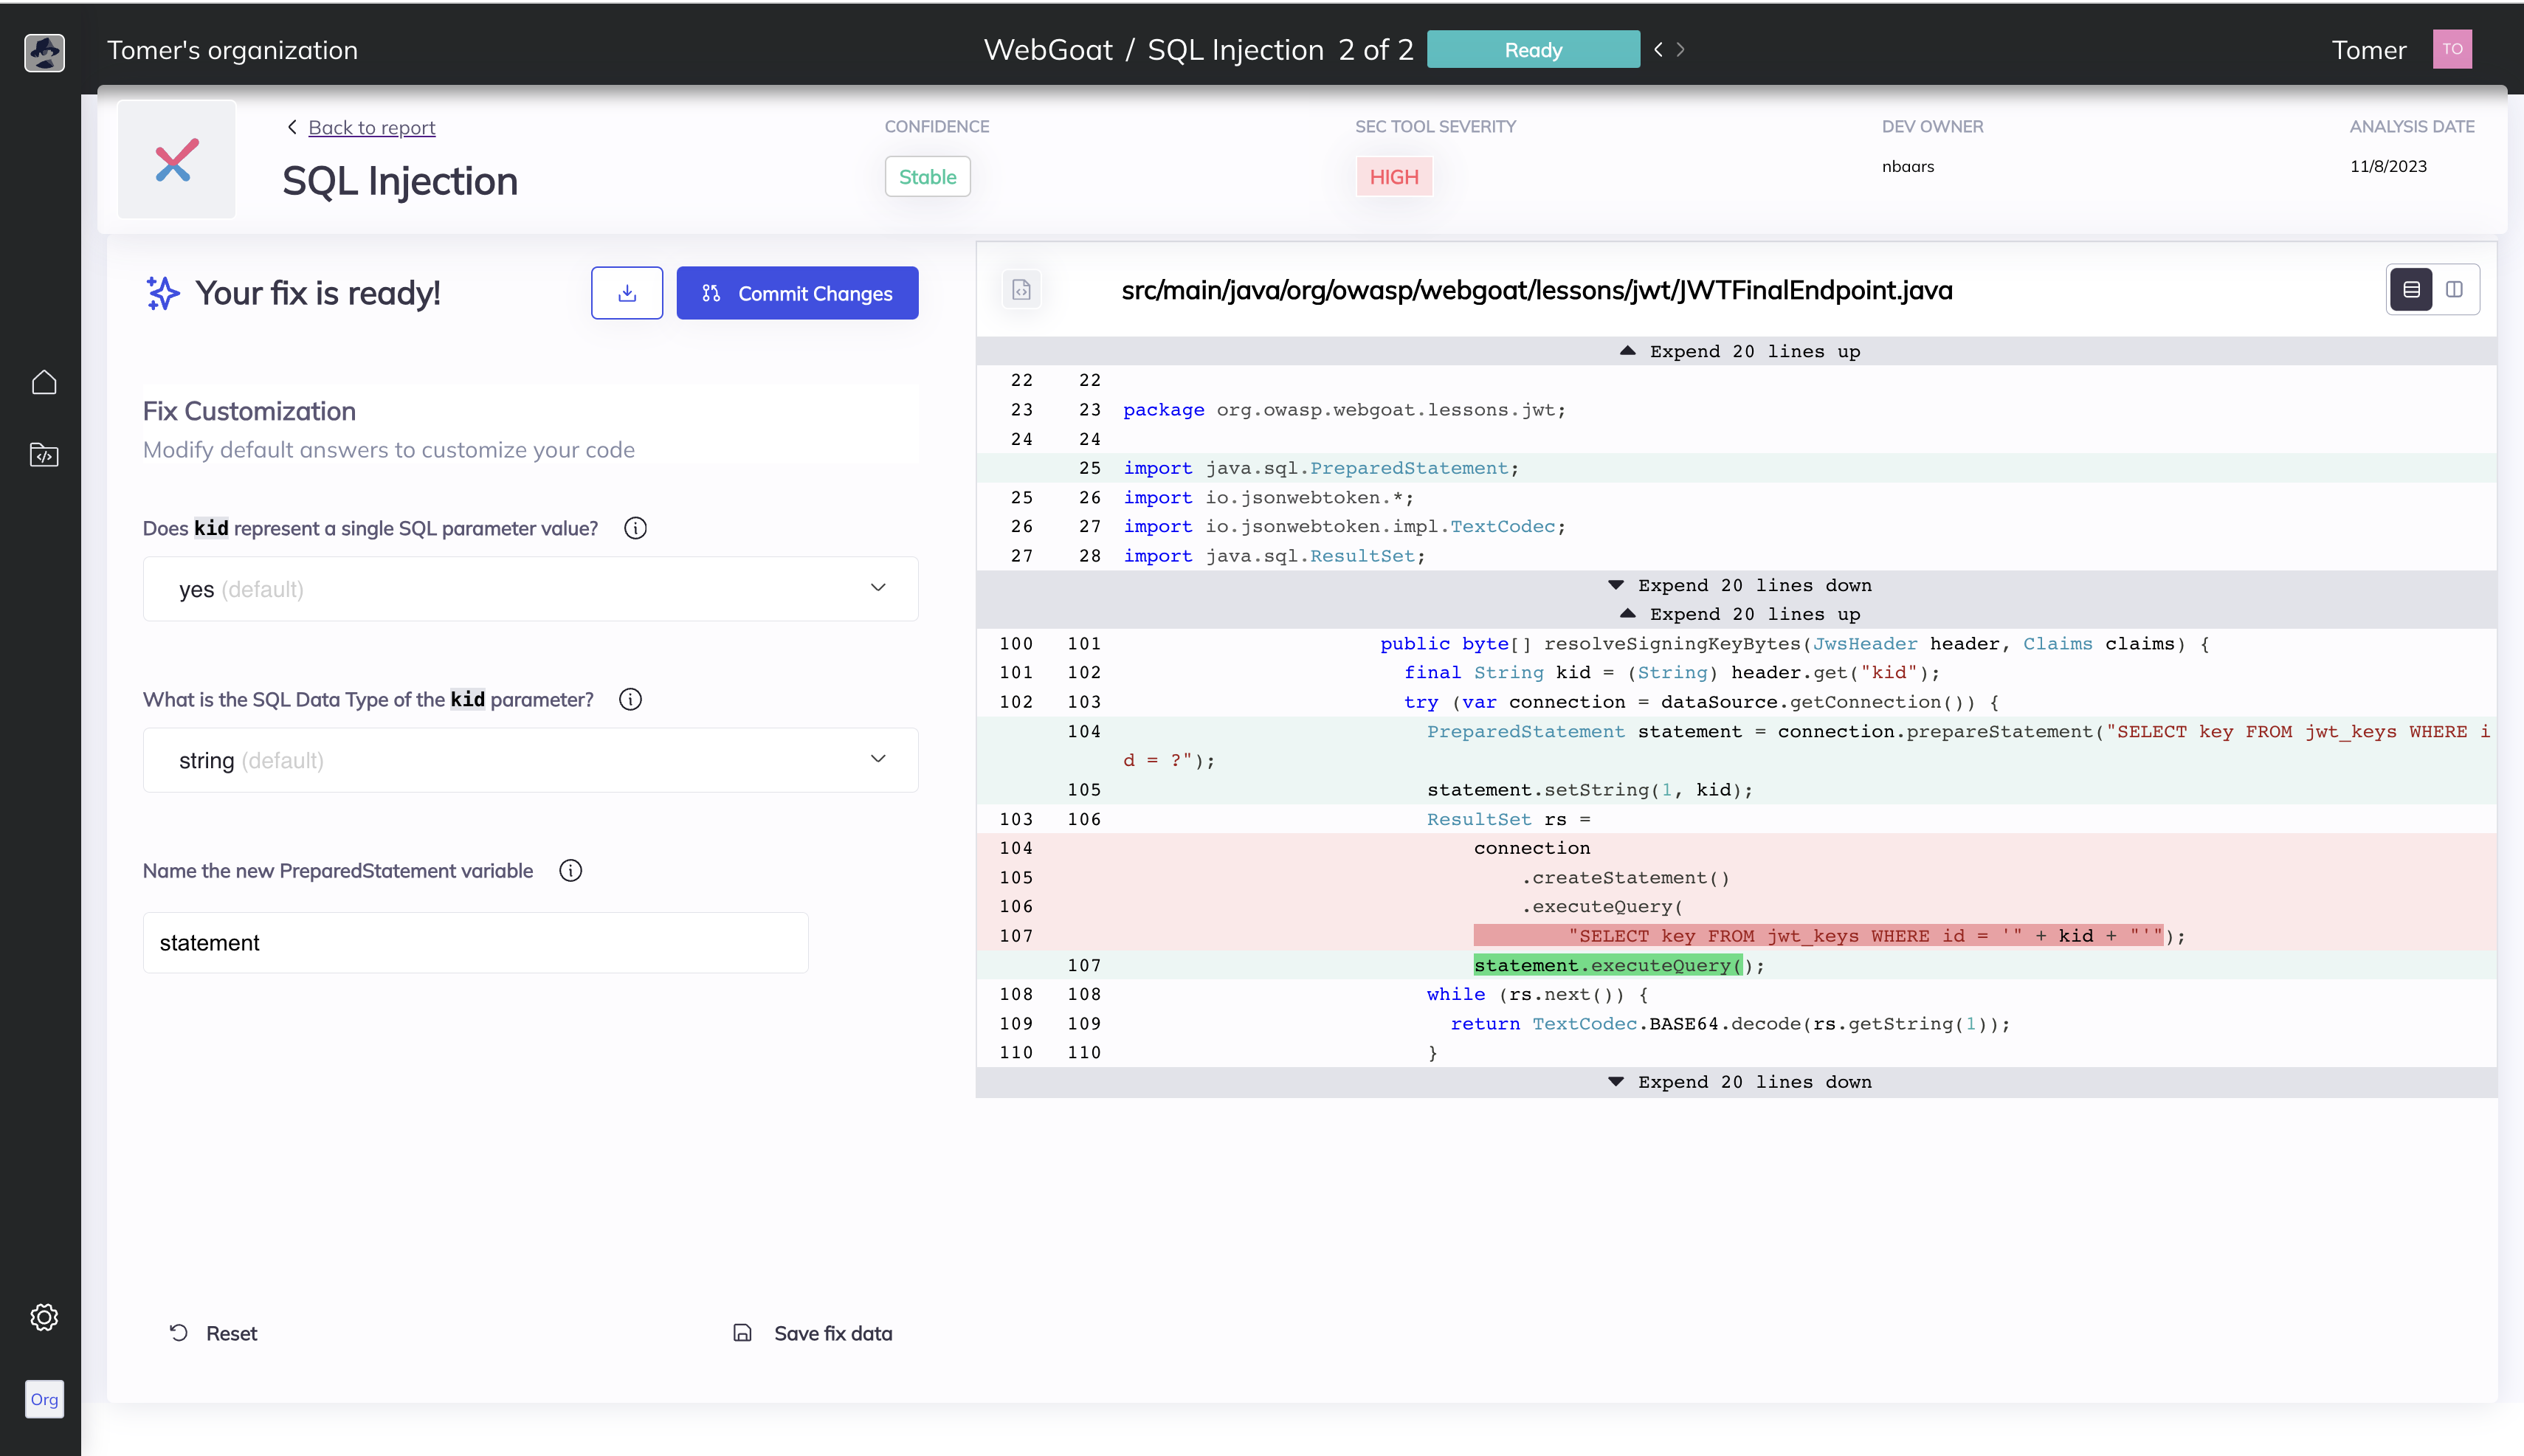 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 nccgroup/ccs
Regex-based scanner for detecting hard-coded credentials in codebases, designed for CI/CD integration with suppression comment support and low…
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 abtonc/next-cve-2025-66478
Scans local projects for CVE-2025-66478 vulnerability and reports affected instances without fixing them.
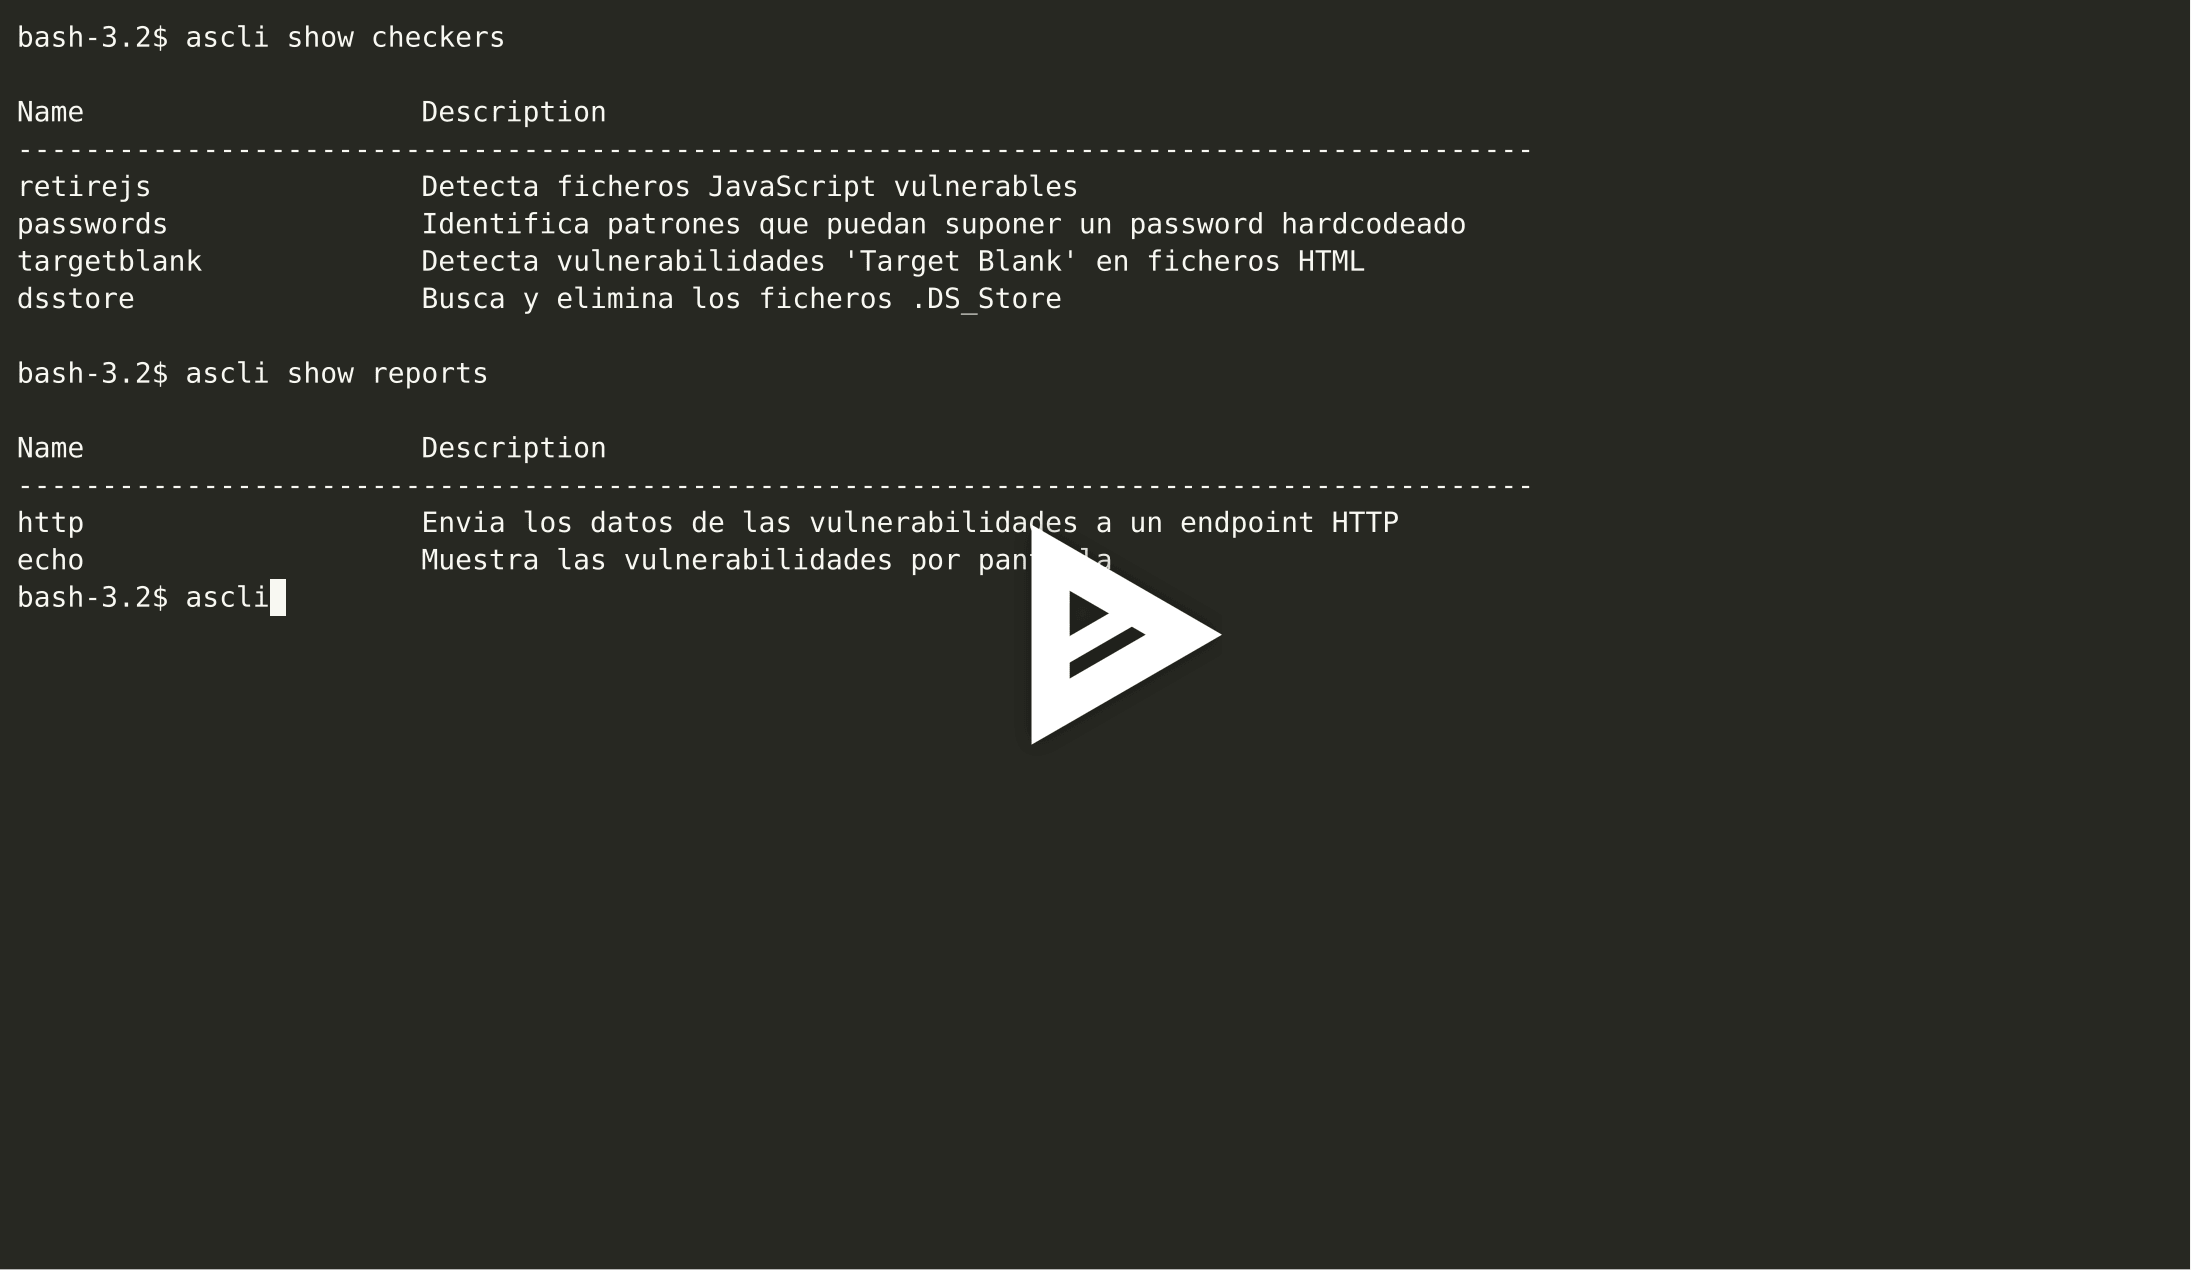 elevenpaths/atomshields-cli
CLI for AtomShields static analysis scanner. Install, uninstall, and run checkers and reports to detect vulnerabilities in source code projects.
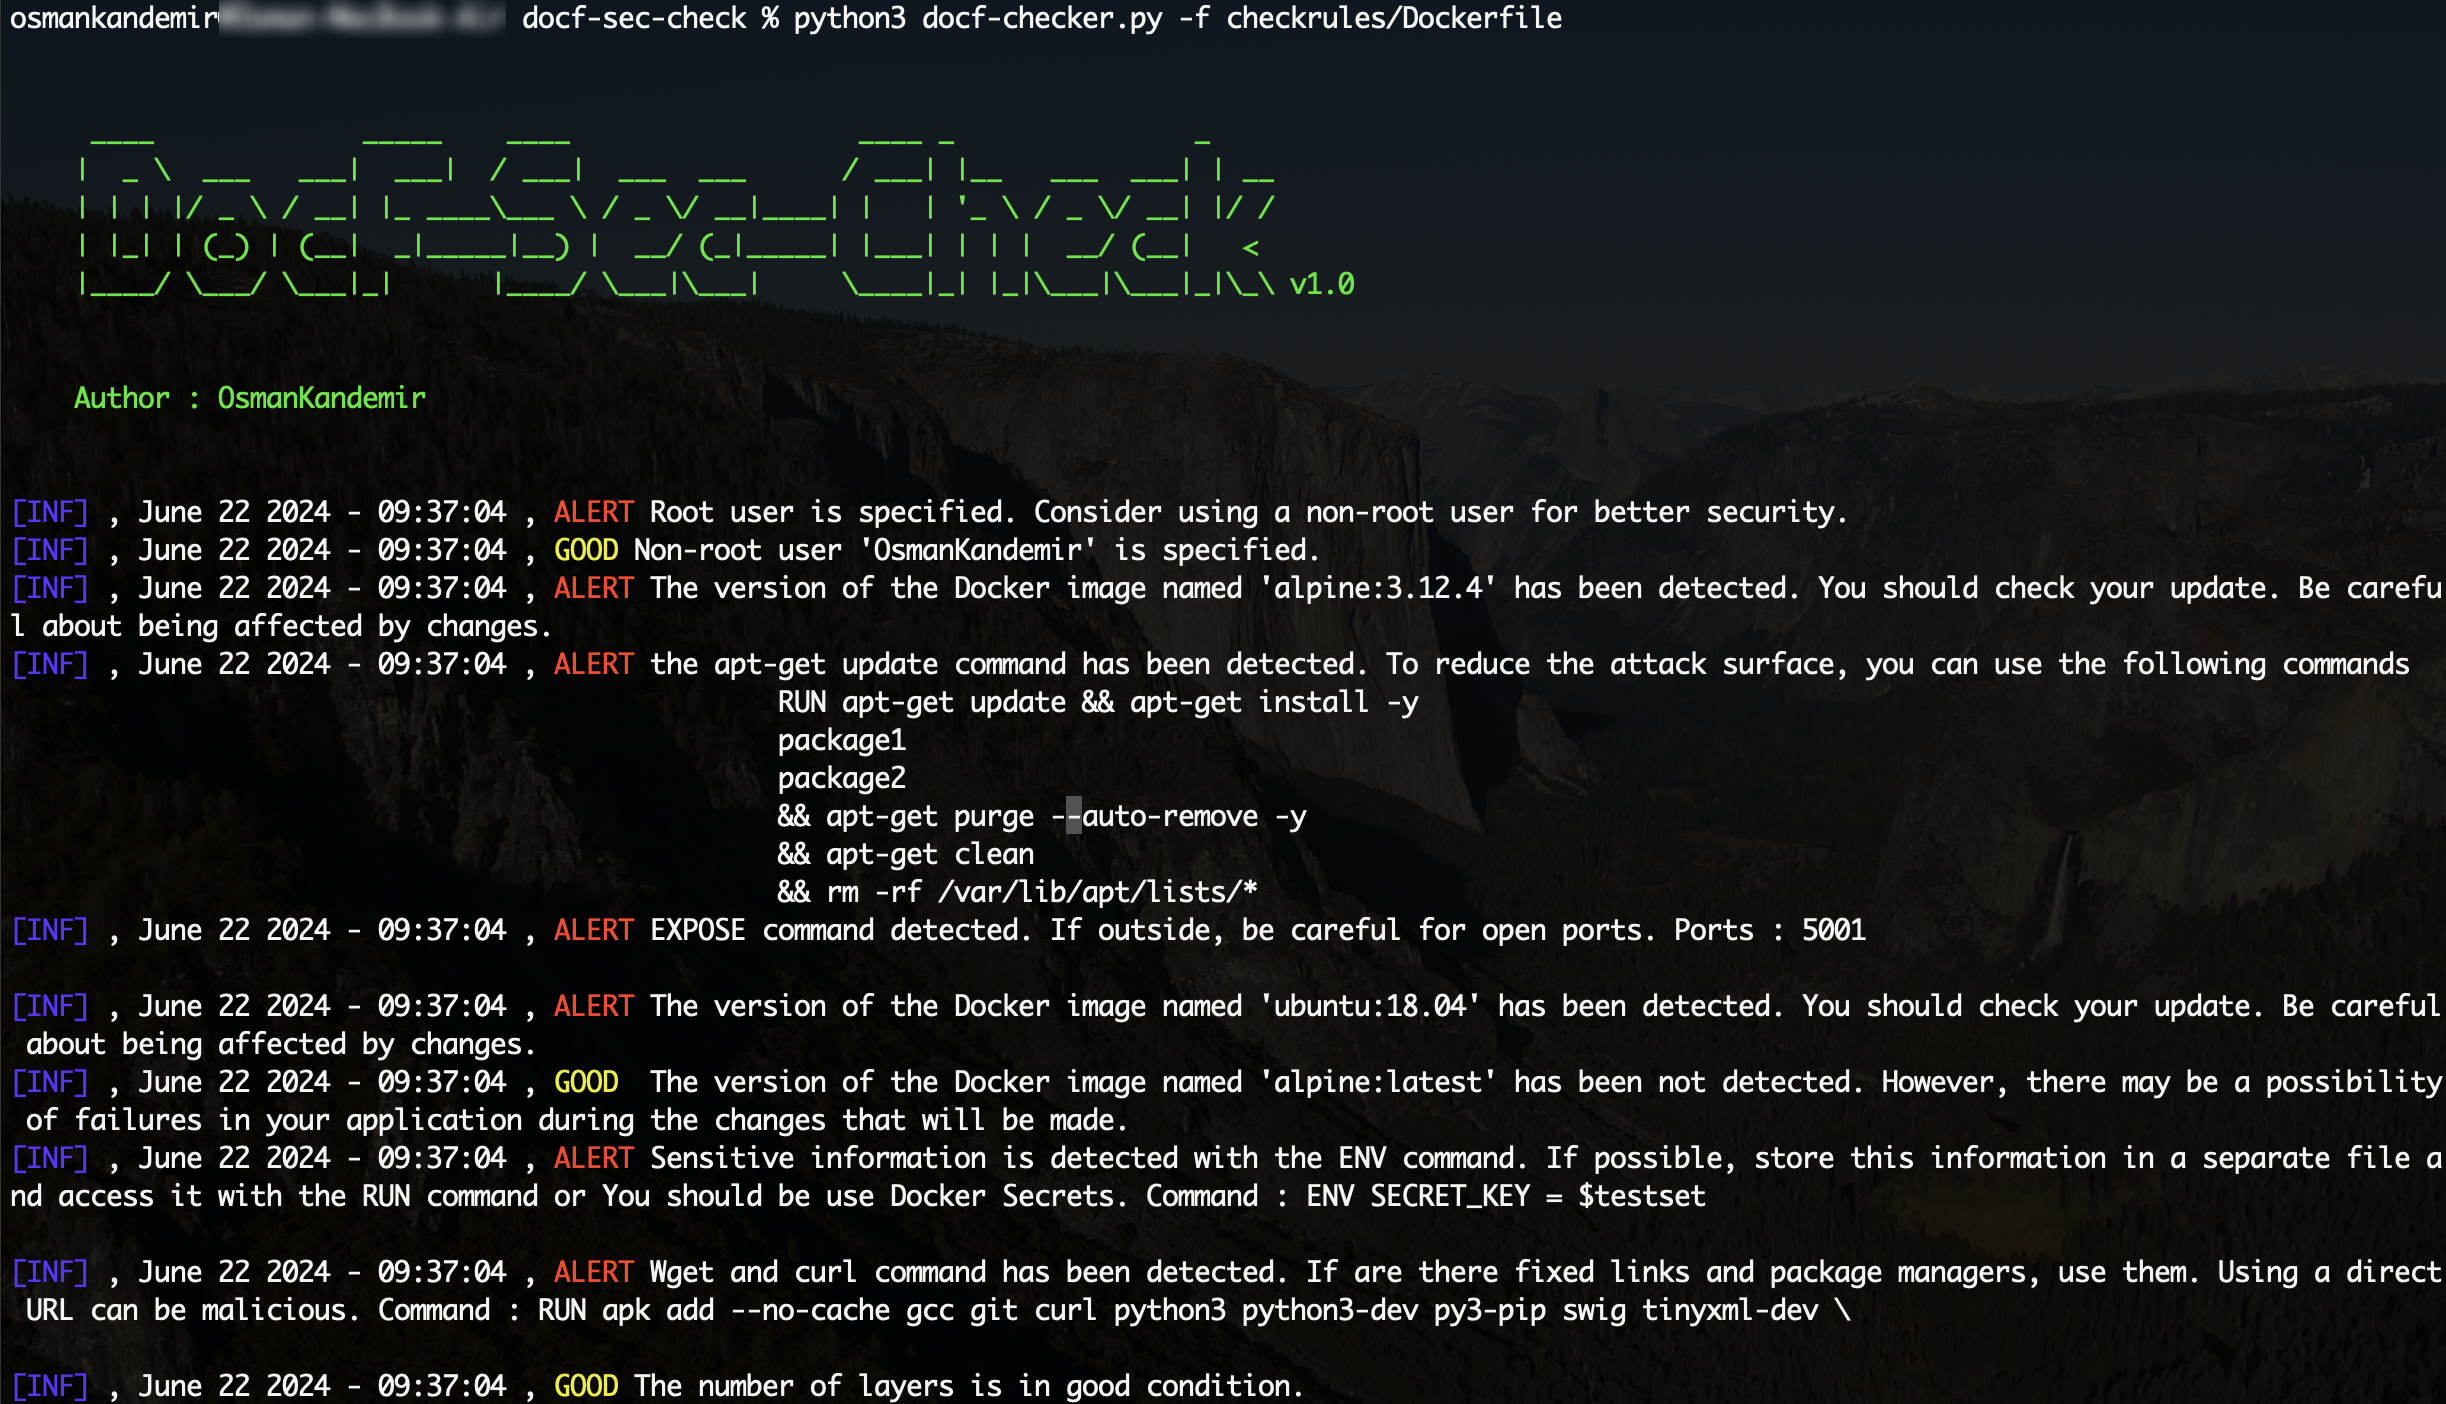 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.