
DependencyCheck
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
devsecopssupply-chain-securityvulnerability-analysis+1
dependency-check/dependencycheckOWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
 devsecopsdocs/nuclearpond
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 titus-soc/-cve-2024-3094-vulnerability-checker-fixer-public
A lightweight utility designed to detect and remediate systems affected by CVE-2024-3094, a critical vulnerability impacting [insert affected…
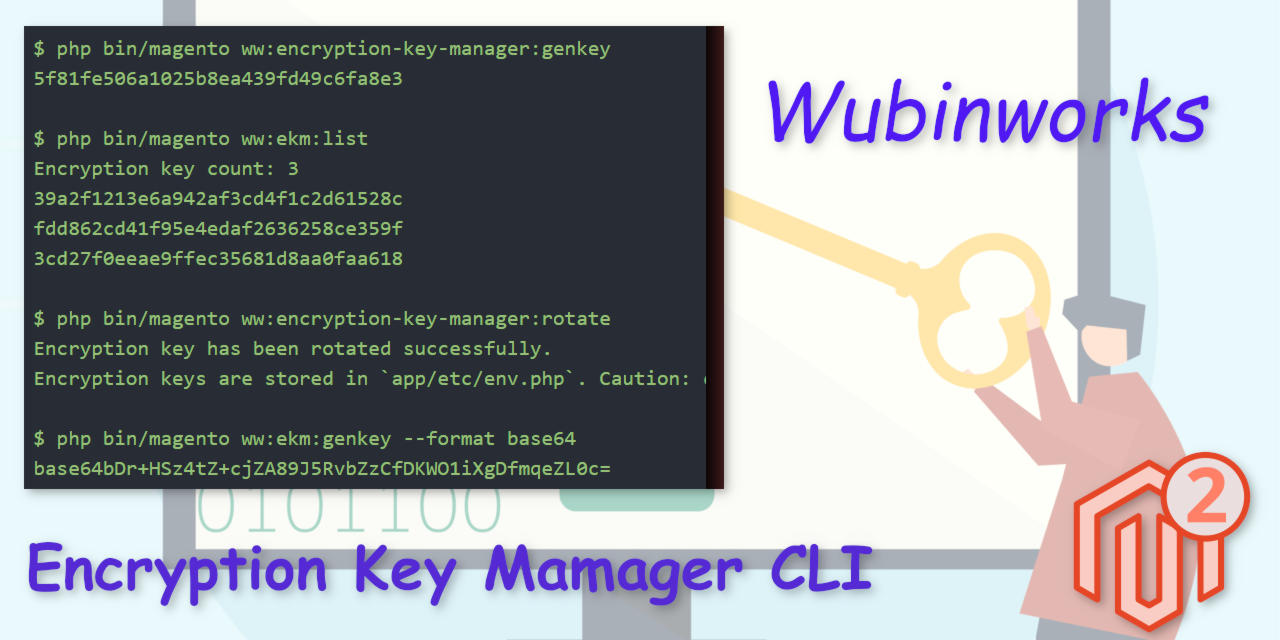 wubinworks/magento2-encryption-key-manager-cli
A utility for Magento 2 encryption key rotation and management. CVE-2024-34102(aka Cosmic Sting) victims can use it as an aftercare.
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 poshbotio/poshbot
Powershell-based bot framework
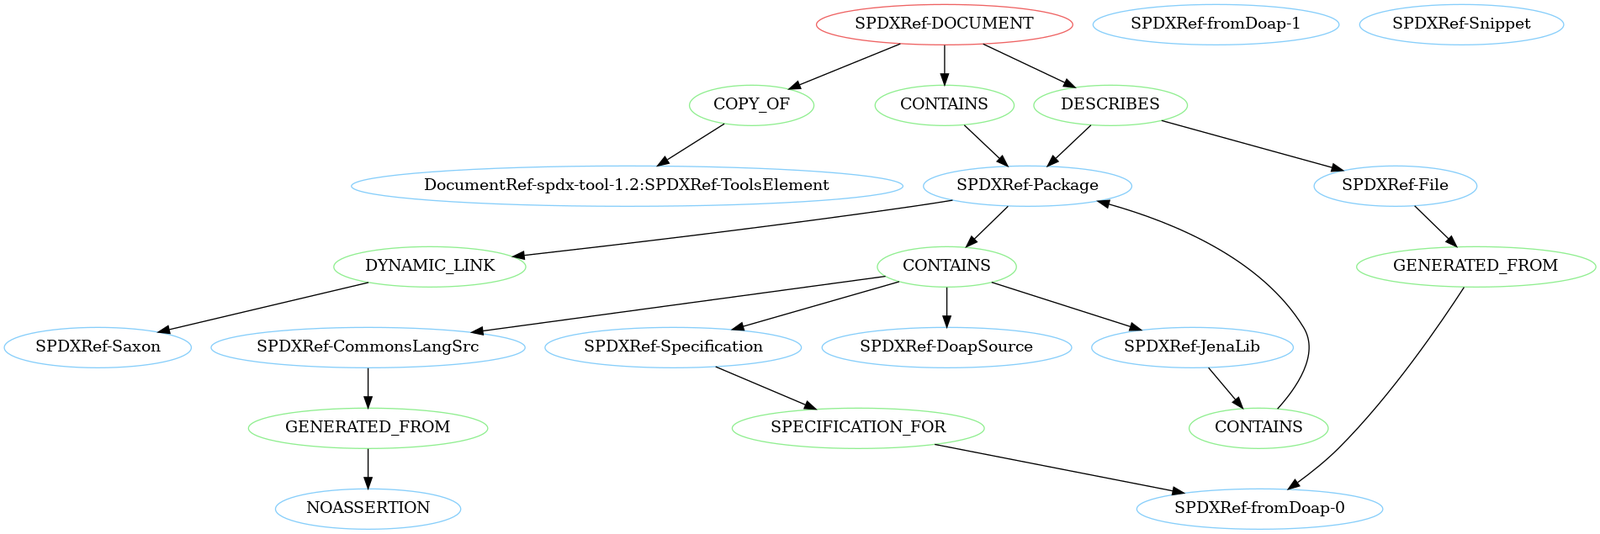 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 kevinslin/safe-npm
Safely install NPM packages
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 resery/cve-2019-17041
Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.
 shoucheng3/diffplug__goomph_cve-2022-26049_3-37-1
Gradle plugin for fast, reproducible Eclipse IDE provisioning as a build artifact, with support for OSGi, p2, and RCP builds.