

opentaint
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
ai-securityapi-securitycode-analysis+7
160
seqra/opentaintFormal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
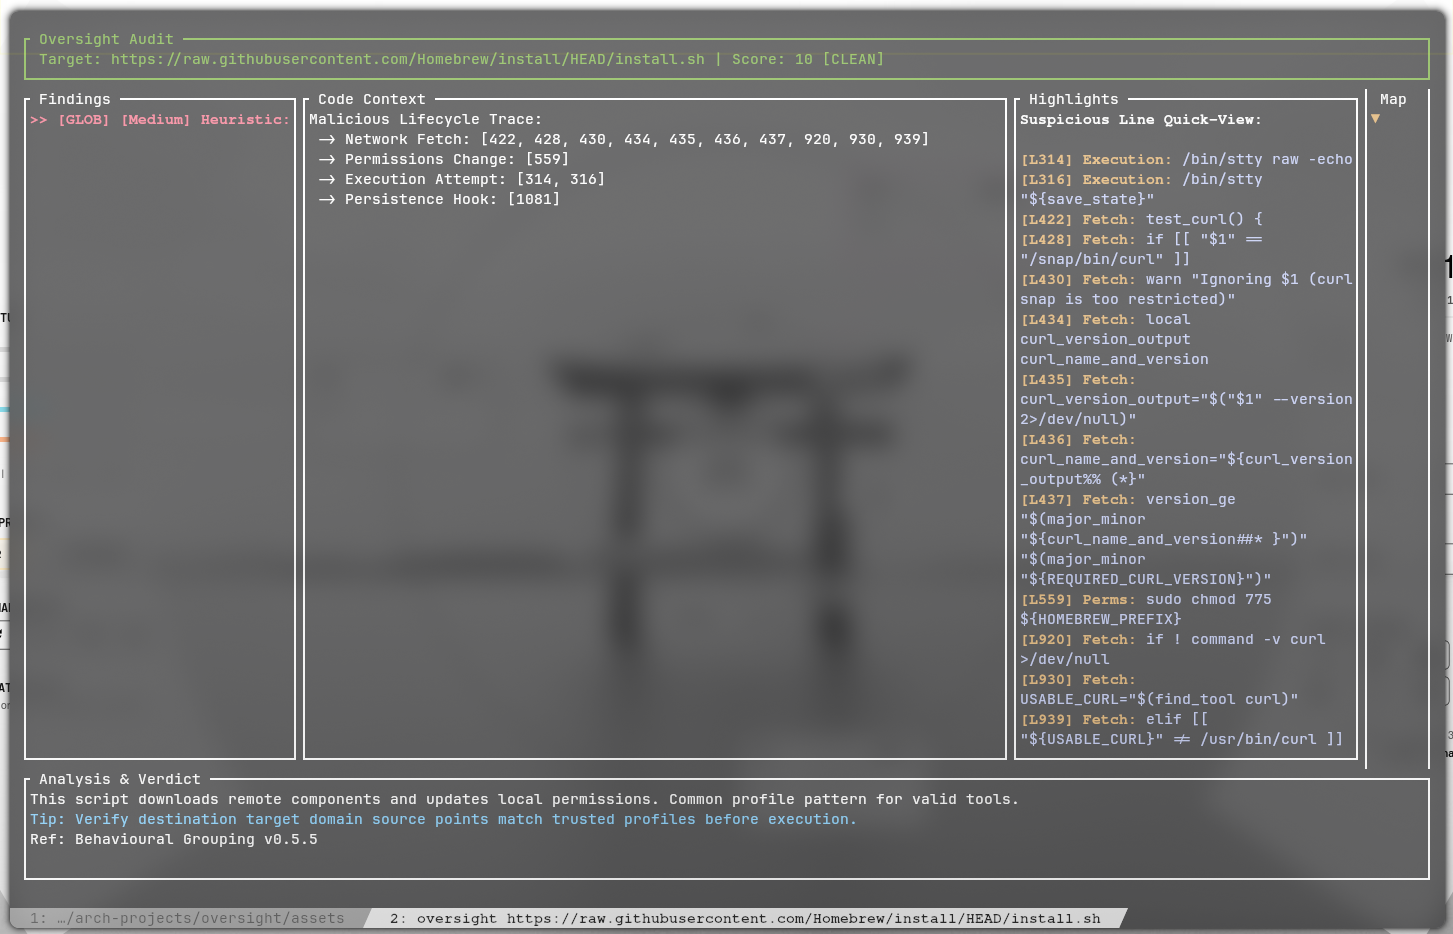 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…