oversight
 rakosn1cek/oversight
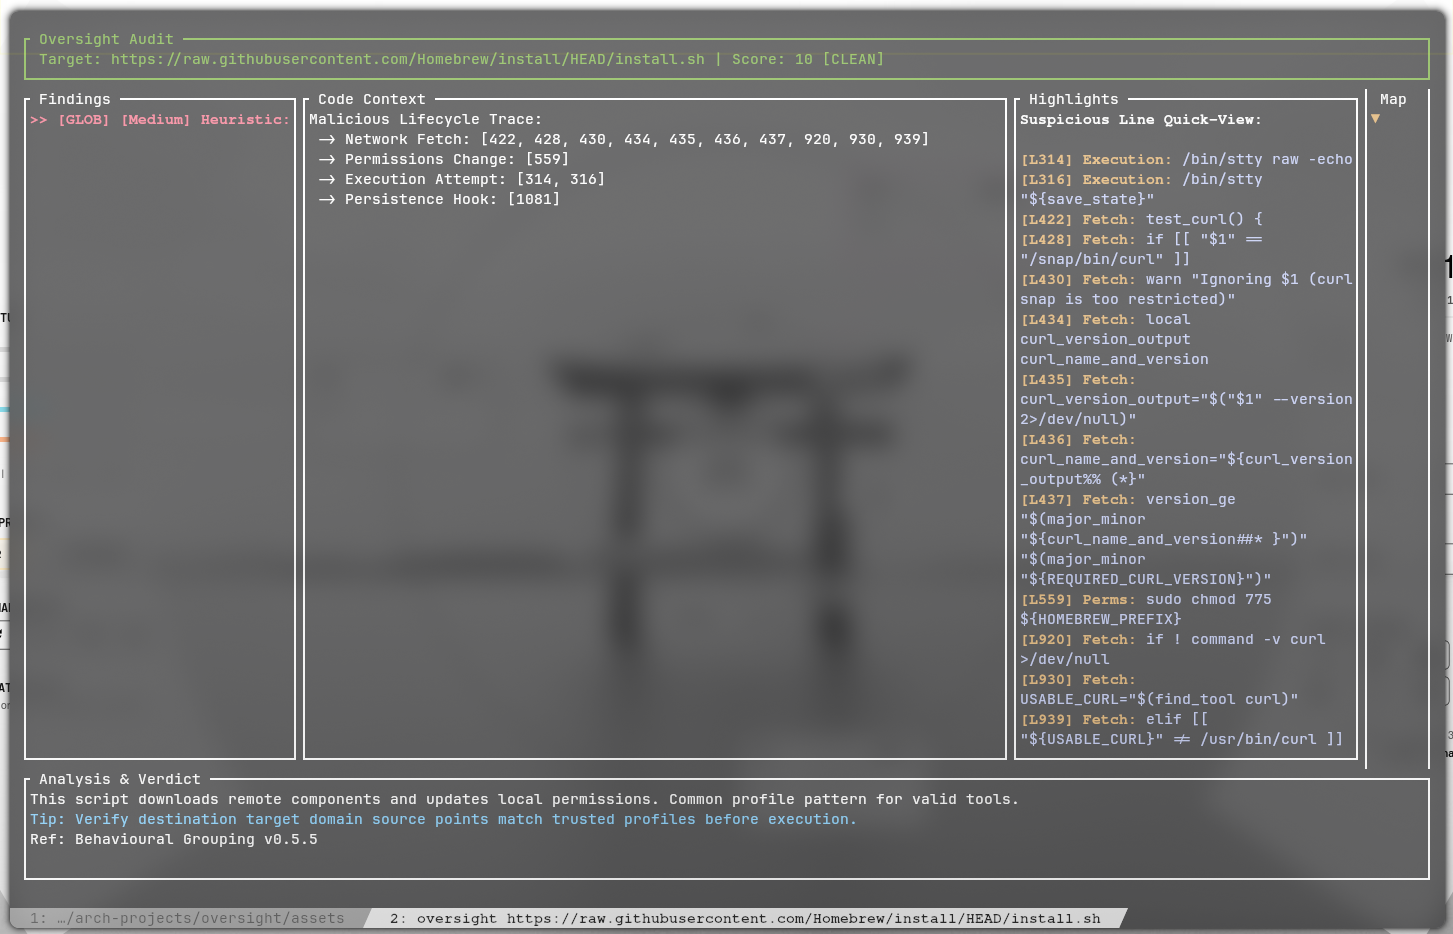
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
code-analysisdevsecopsdynamic-analysis-sandboxing+7
39
rakosn1cek/oversightA lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 rezmoss/sbomlyze
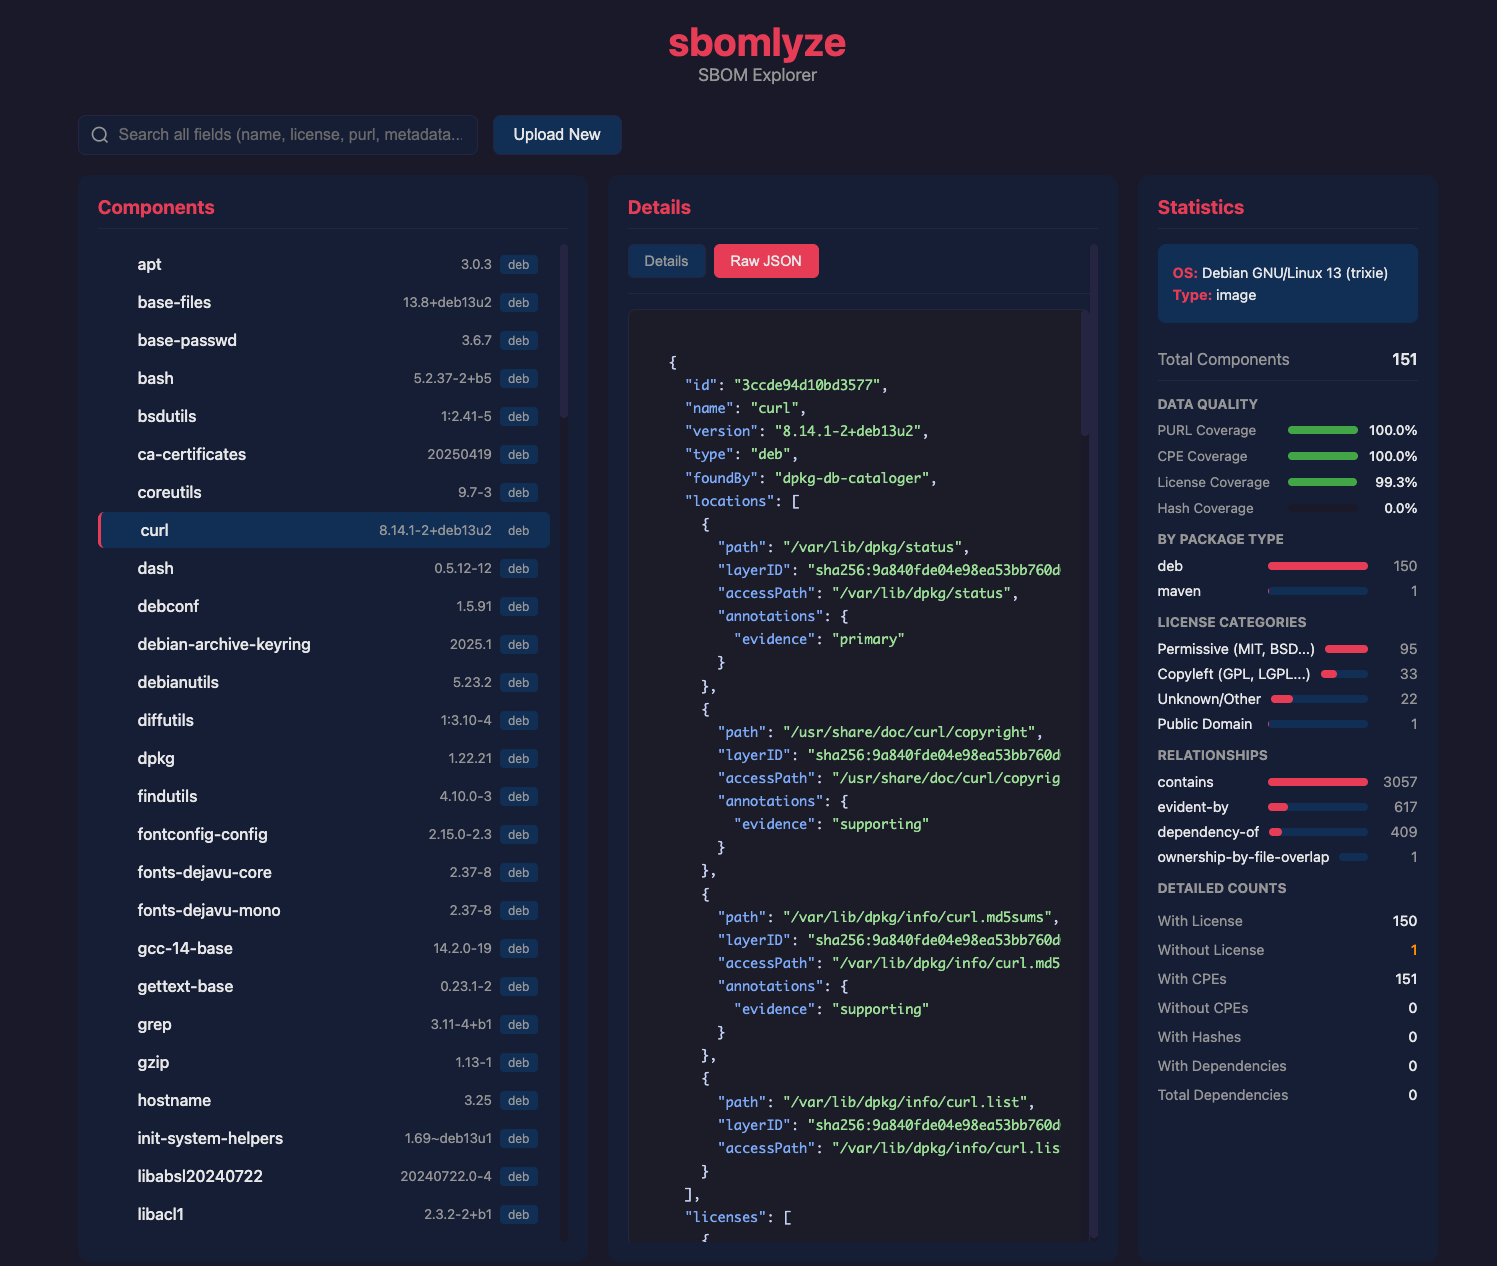
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
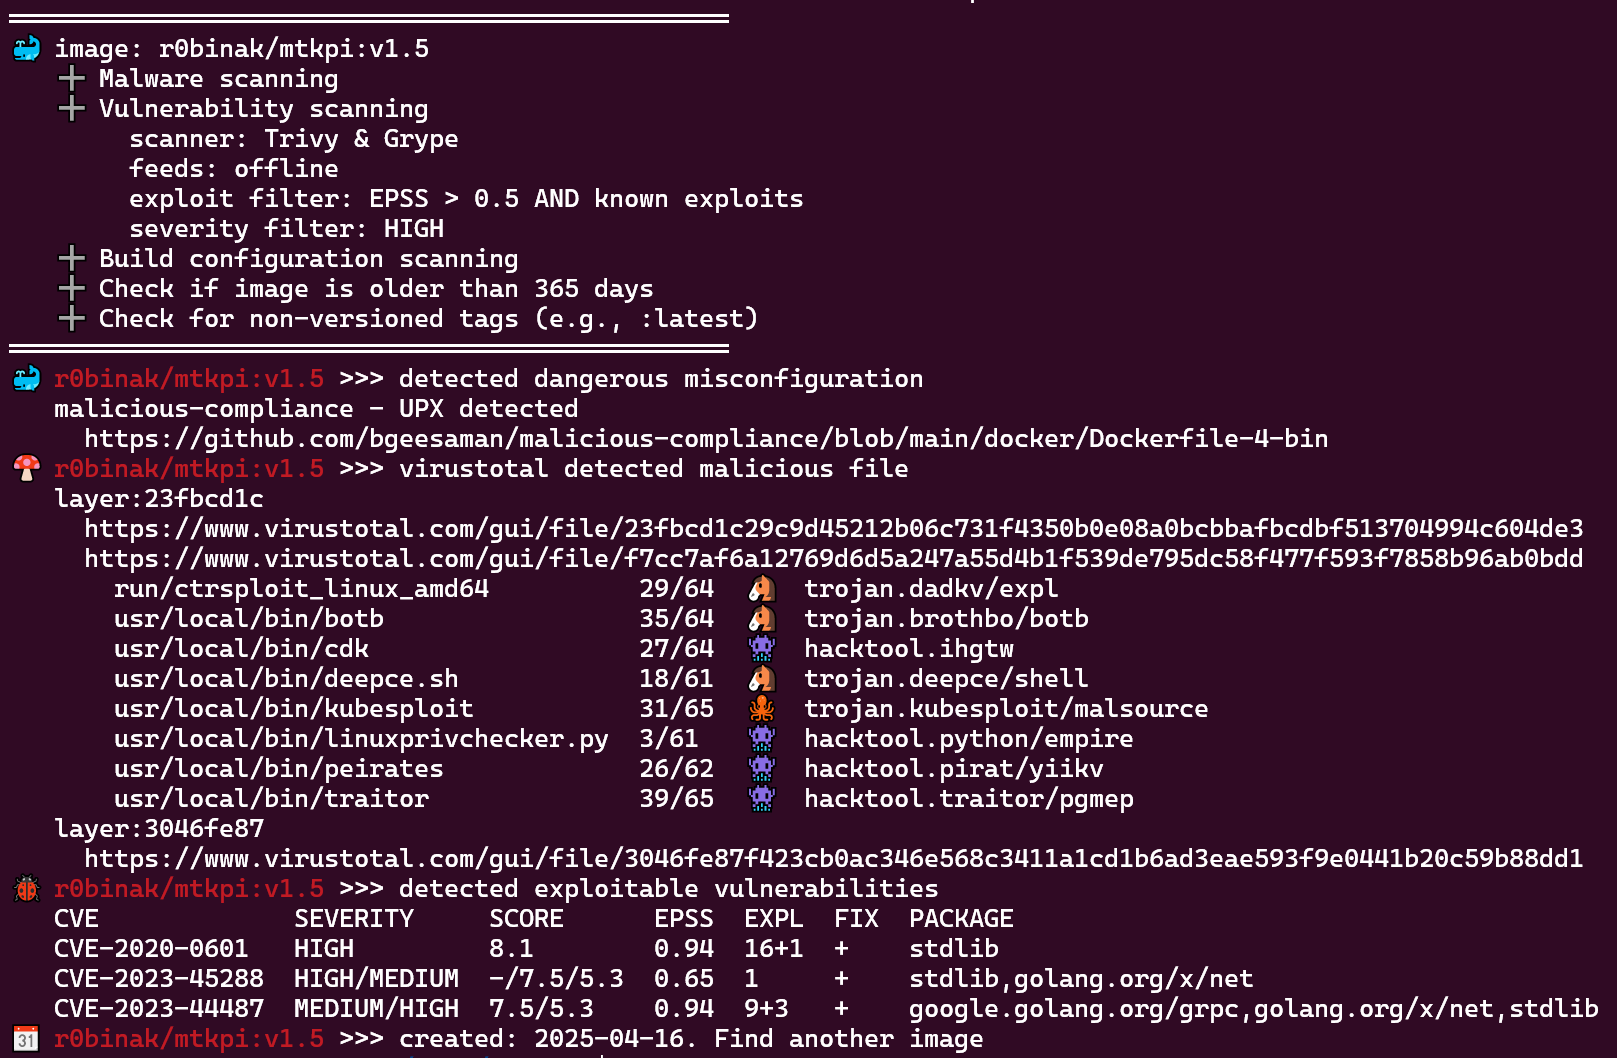 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 zihxs/check-react-rce-cve-2025-55182
Security scanner to detect CVE-2025-55182 & CVE-2025-66478 vulnerabilities in React Server Components (RSC) projects
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 amir-malek/react-cve-2025-55182
Detects and fixes CVE-2025-55182 (React2Shell) in React Server Components and Next.js apps. Scans package versions, suggests safe upgrades, and…
 didoatanasov/cve-2021-44228
Ansible playbook that applies a global JVM environment variable to mitigate the Log4j CVE-2021-44228 remote code execution vulnerability across all…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances