
dotenv-diff
 chrilleweb/dotenv-diff
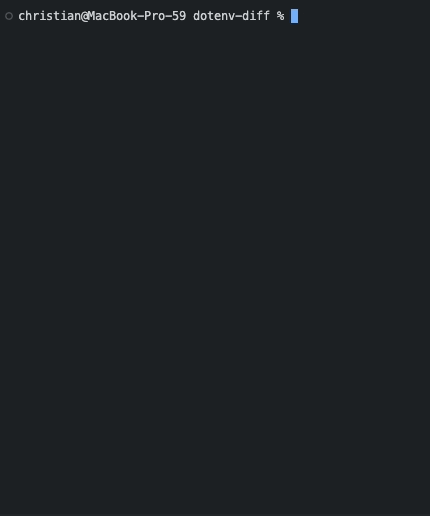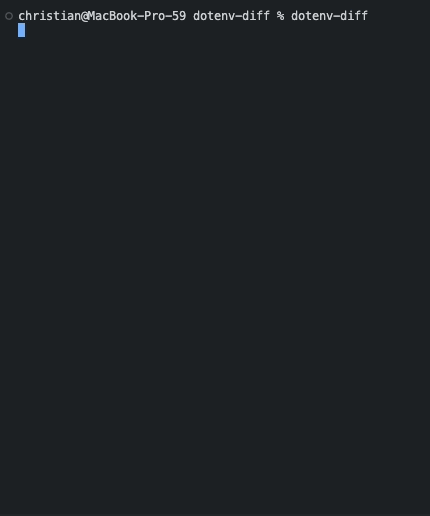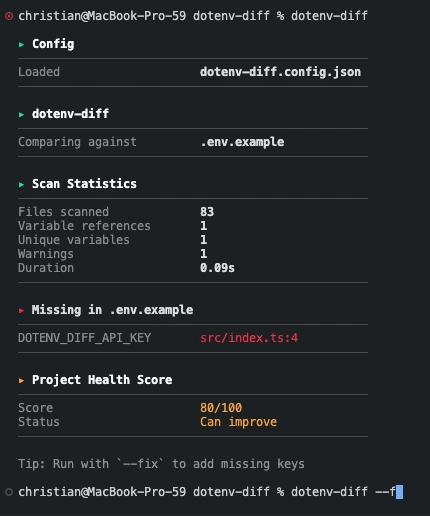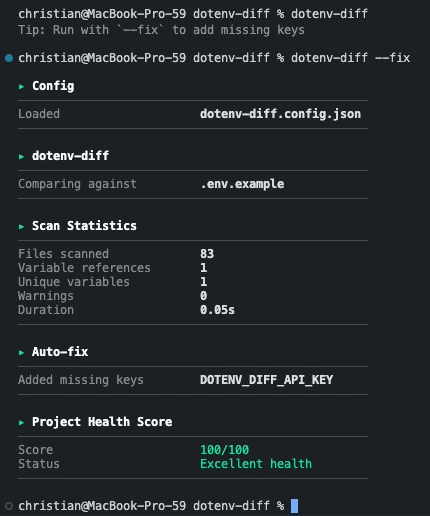
Validate environment variable usage in codebase
code-analysisconfiguration-auditingdevsecops+3
chrilleweb/dotenv-diffValidate environment variable usage in codebase
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
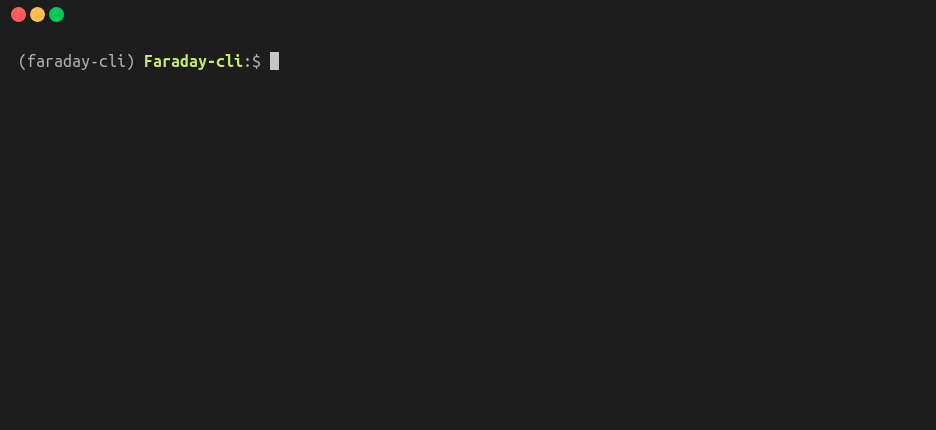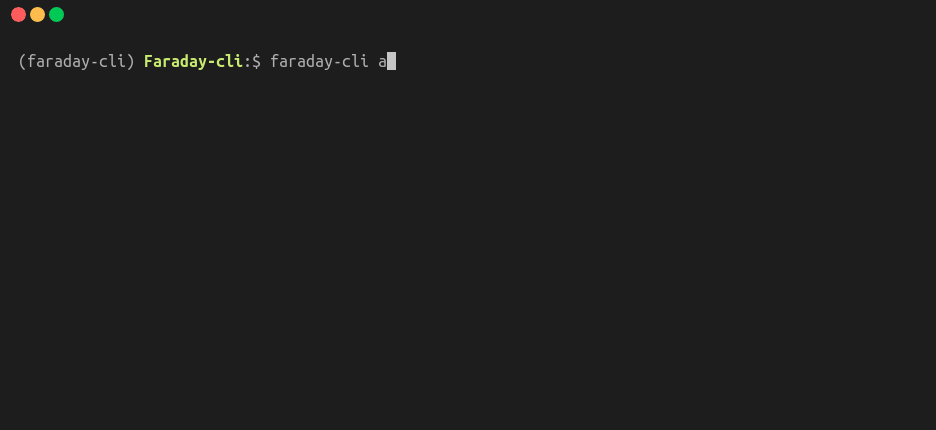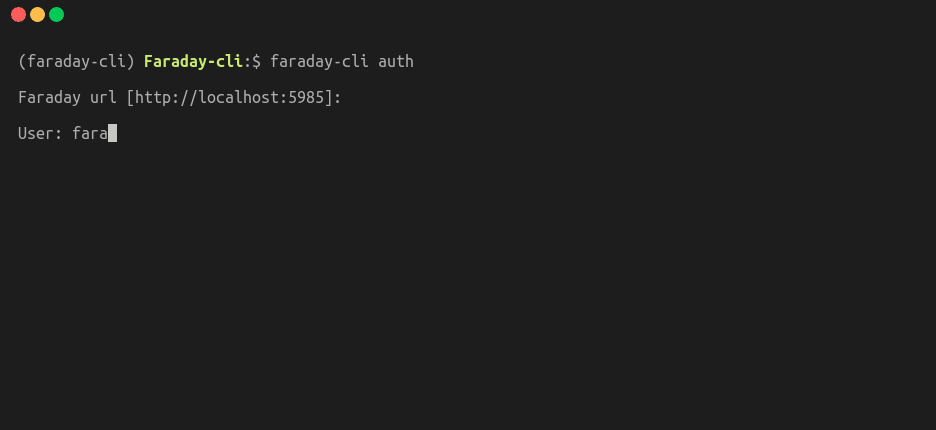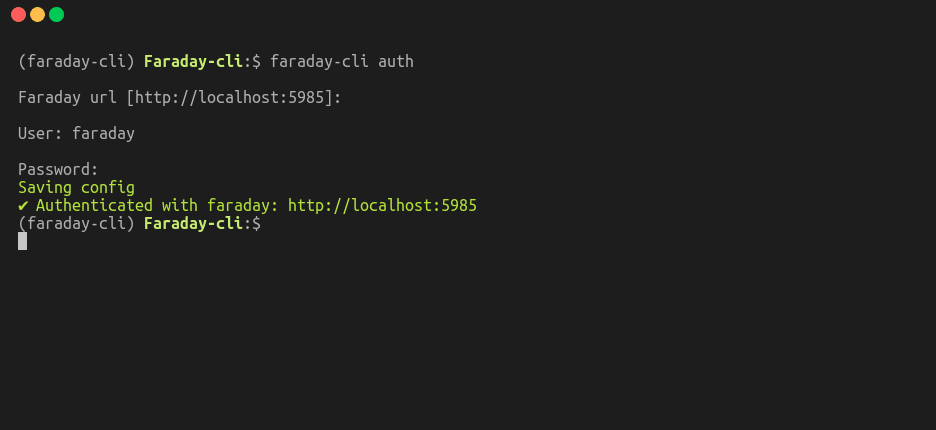 infobyte/faraday-cli
Faraday's Command Line Interface
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 securityuniversalorg/secusphere
Centralized DevSecOps platform for vulnerability management, CI/CD security integration, automated security assessment aggregation, and fostering…
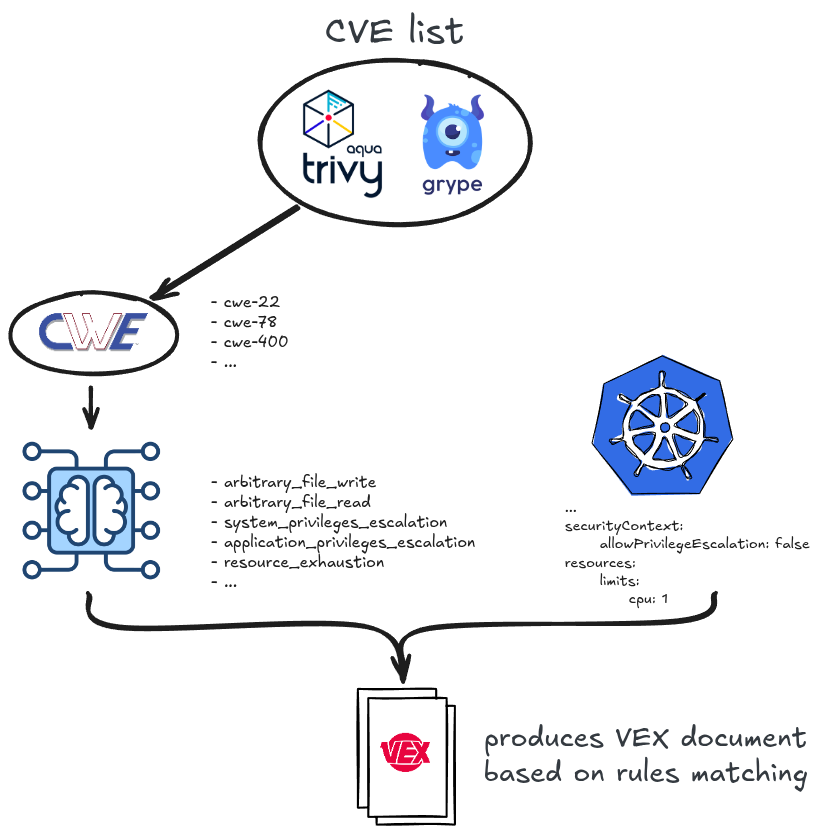 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
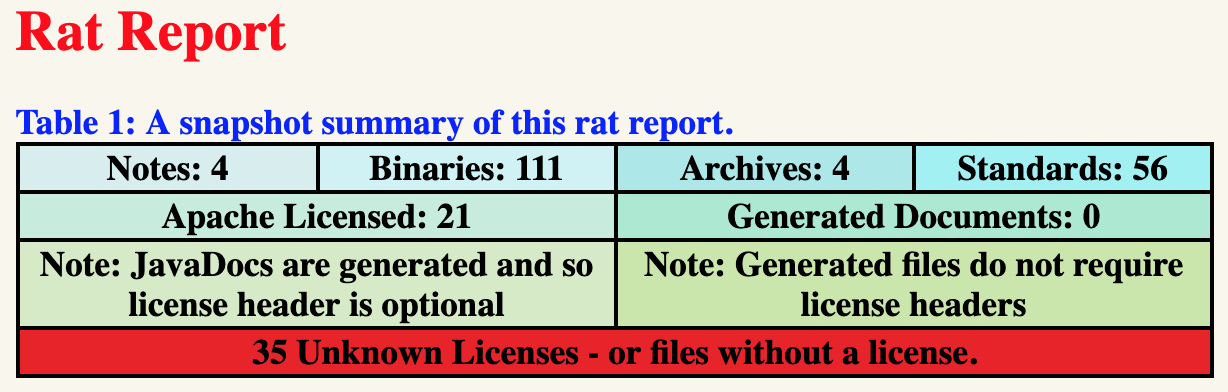 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 fran314/secrets-manager-rs
A command-line tool for securely backing up, restoring, and verifying secrets using interoperable standards like age encryption and coreutils,…