
cosign
 sigstore/cosign
Code signing and transparency for containers and binaries
authentication-authorizationcloud-securitycontainer-security+3
sigstore/cosignCode signing and transparency for containers and binaries
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 cloudquery/cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…
 dev-sec/ansible-collection-hardening
This Ansible collection provides battle tested hardening for Linux, SSH, nginx, MySQL
 microsoft/azurelinux
Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…
 fabacab/awesome-cybersecurity-blueteam
💻🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 docker/docker-bench-security
The Docker Bench for Security is a script that checks for dozens of common best-practices around deploying Docker containers in production.
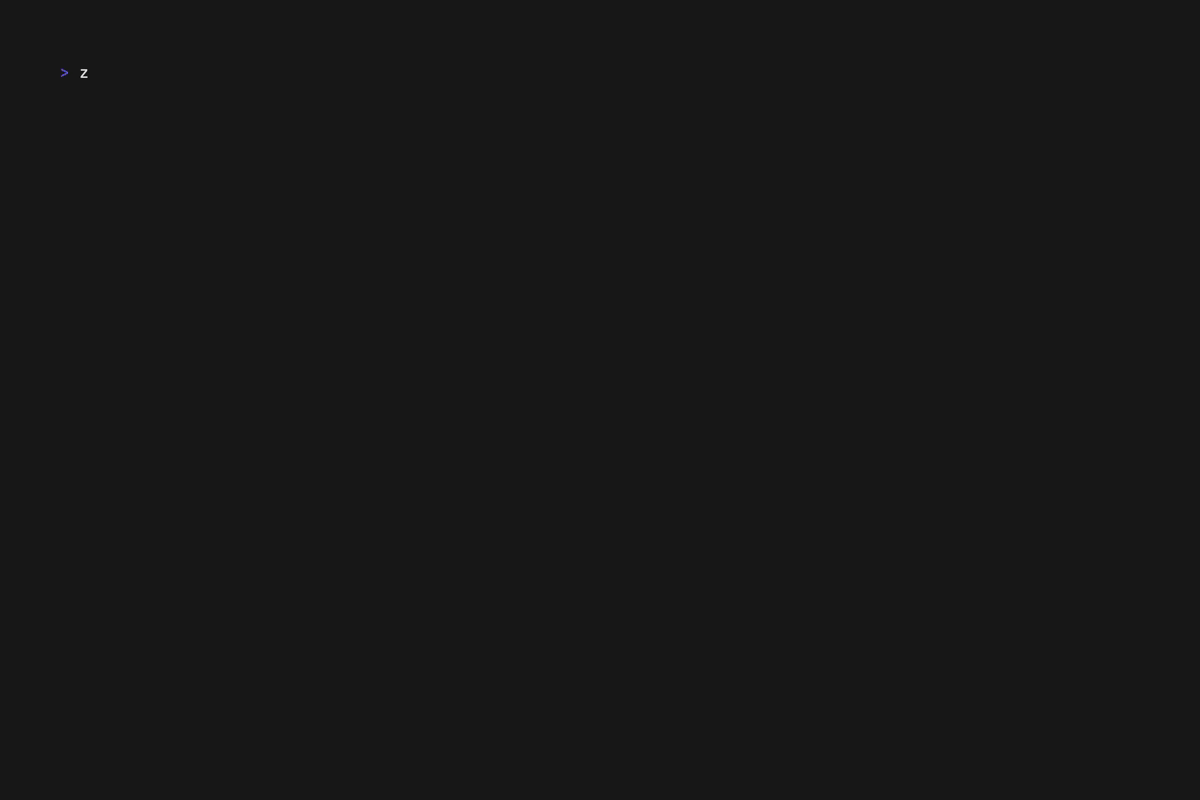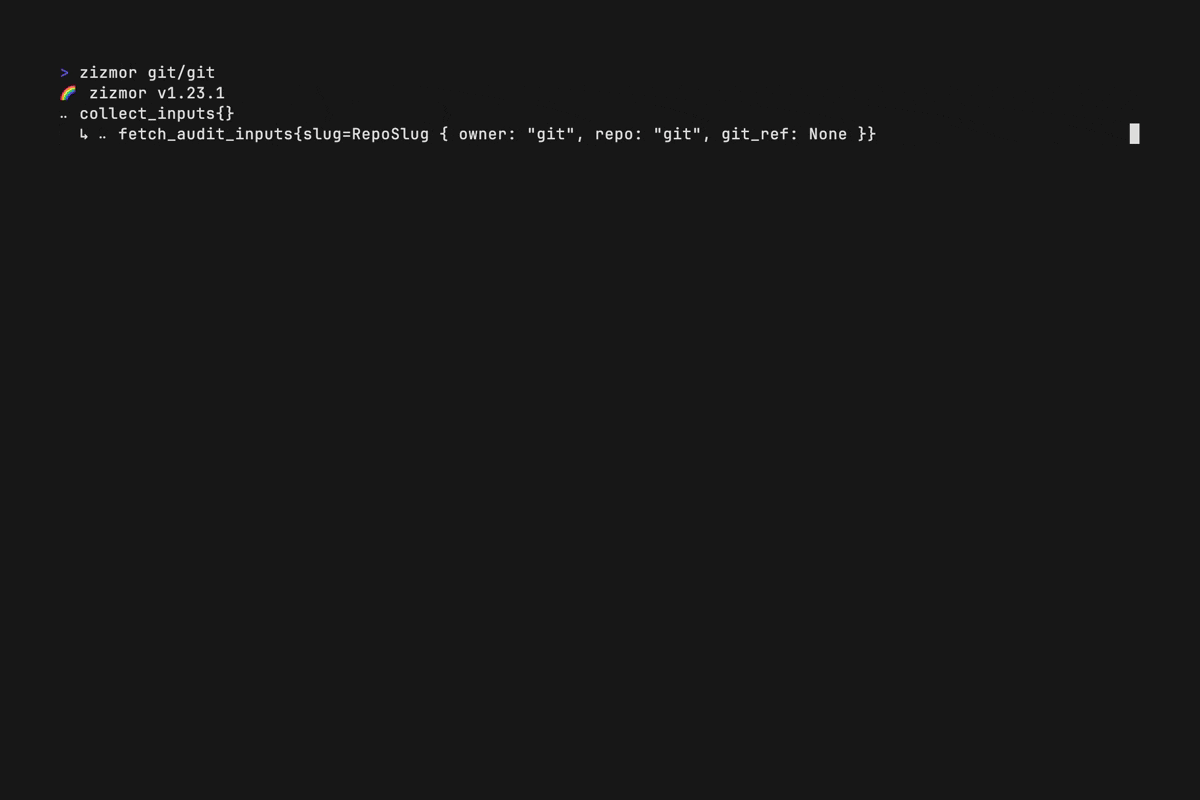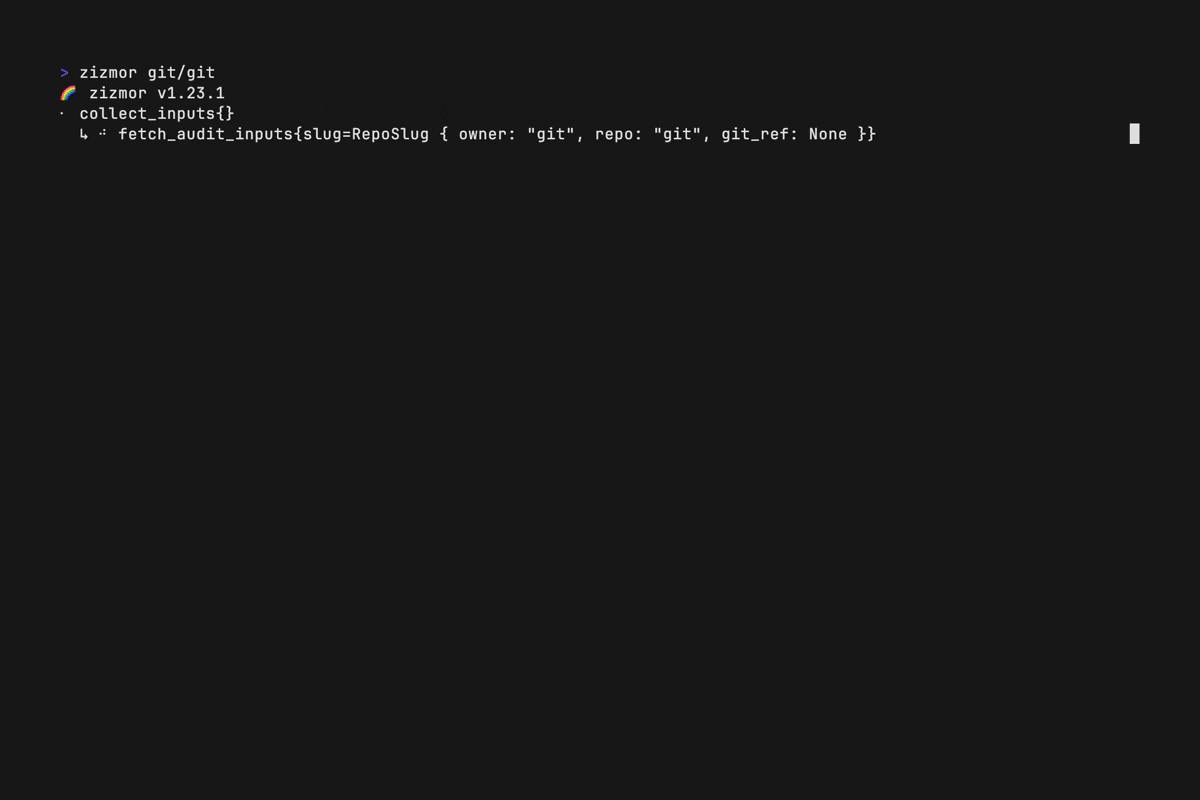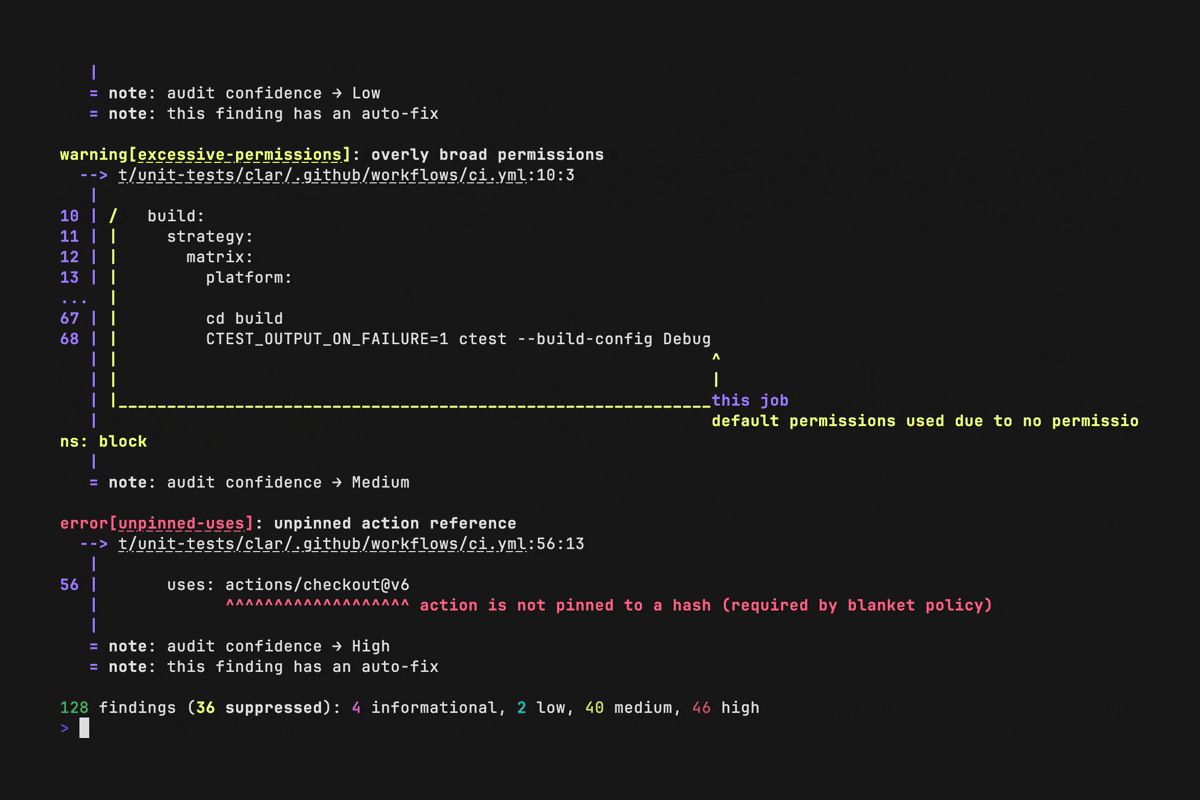 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
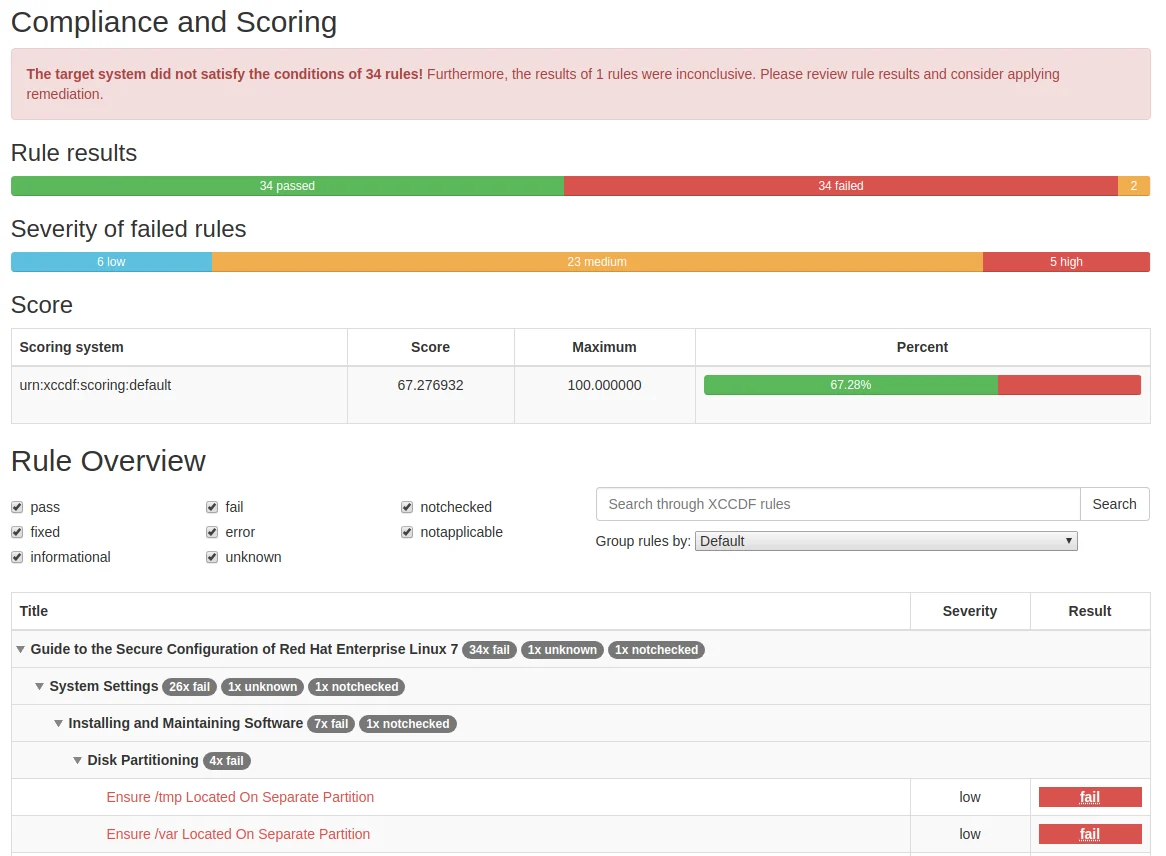 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 nolabs-ai/nono
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
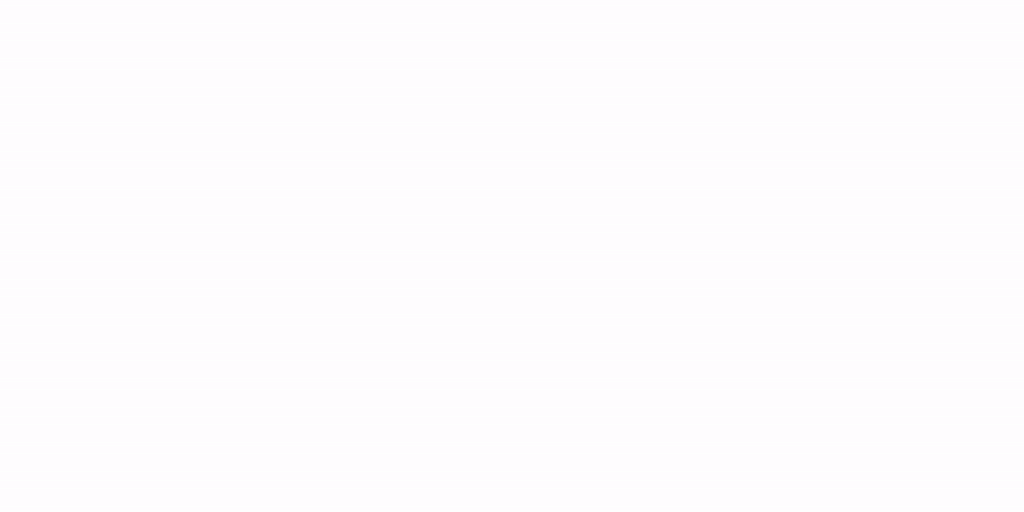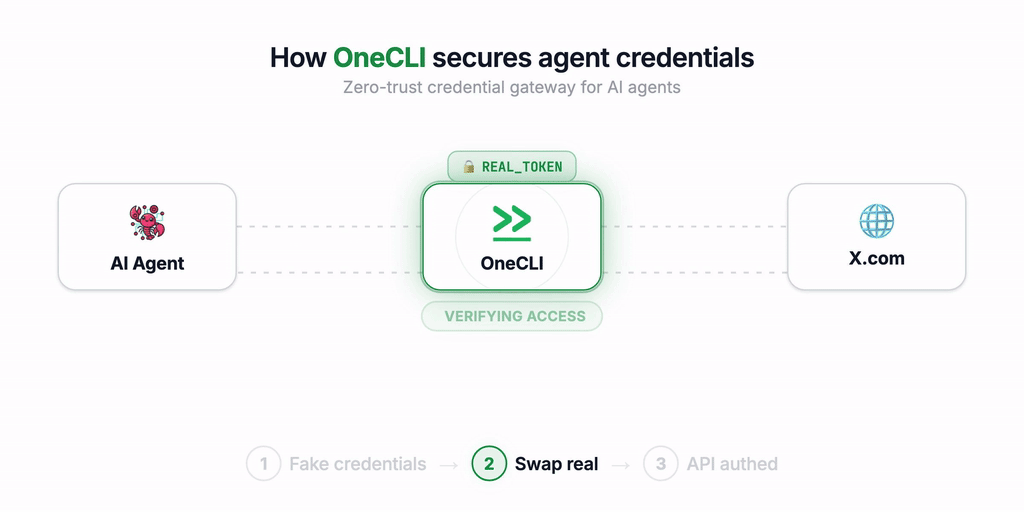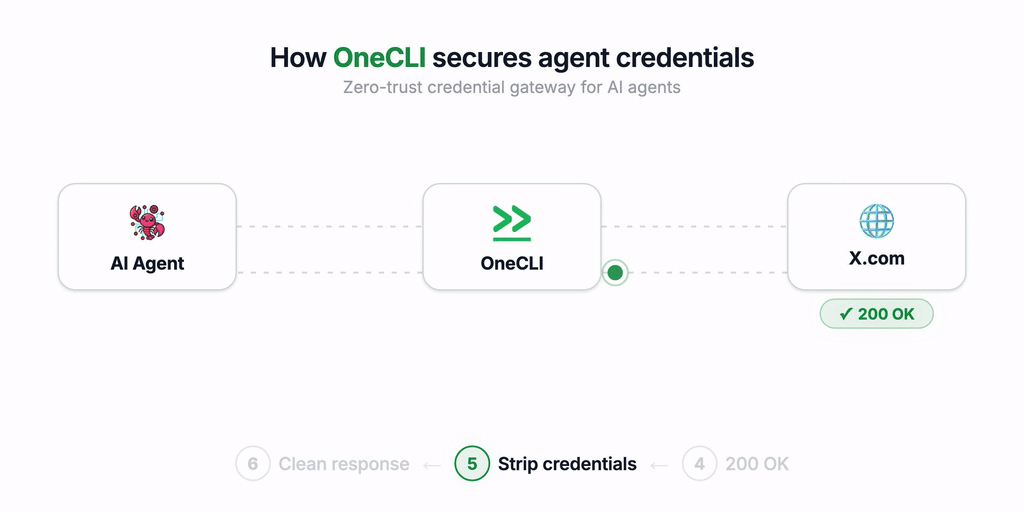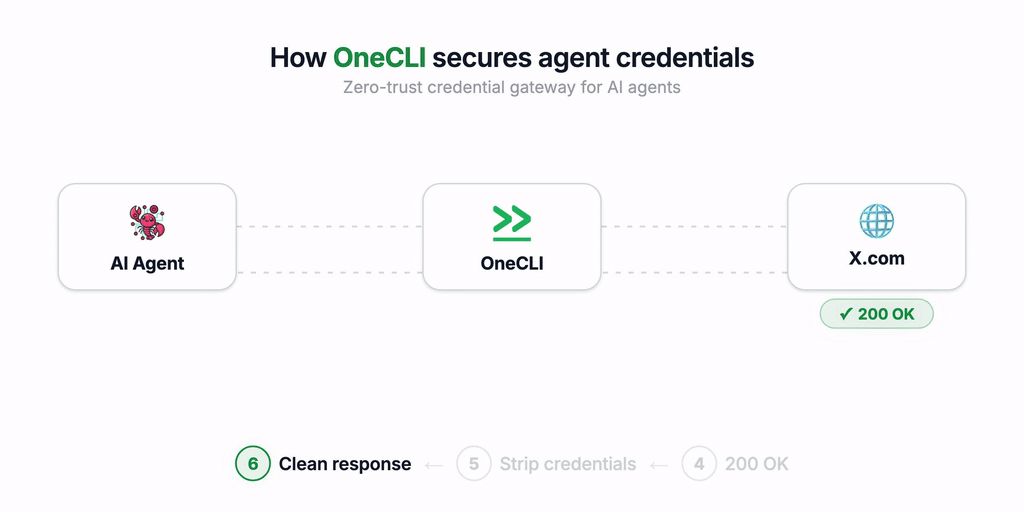 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
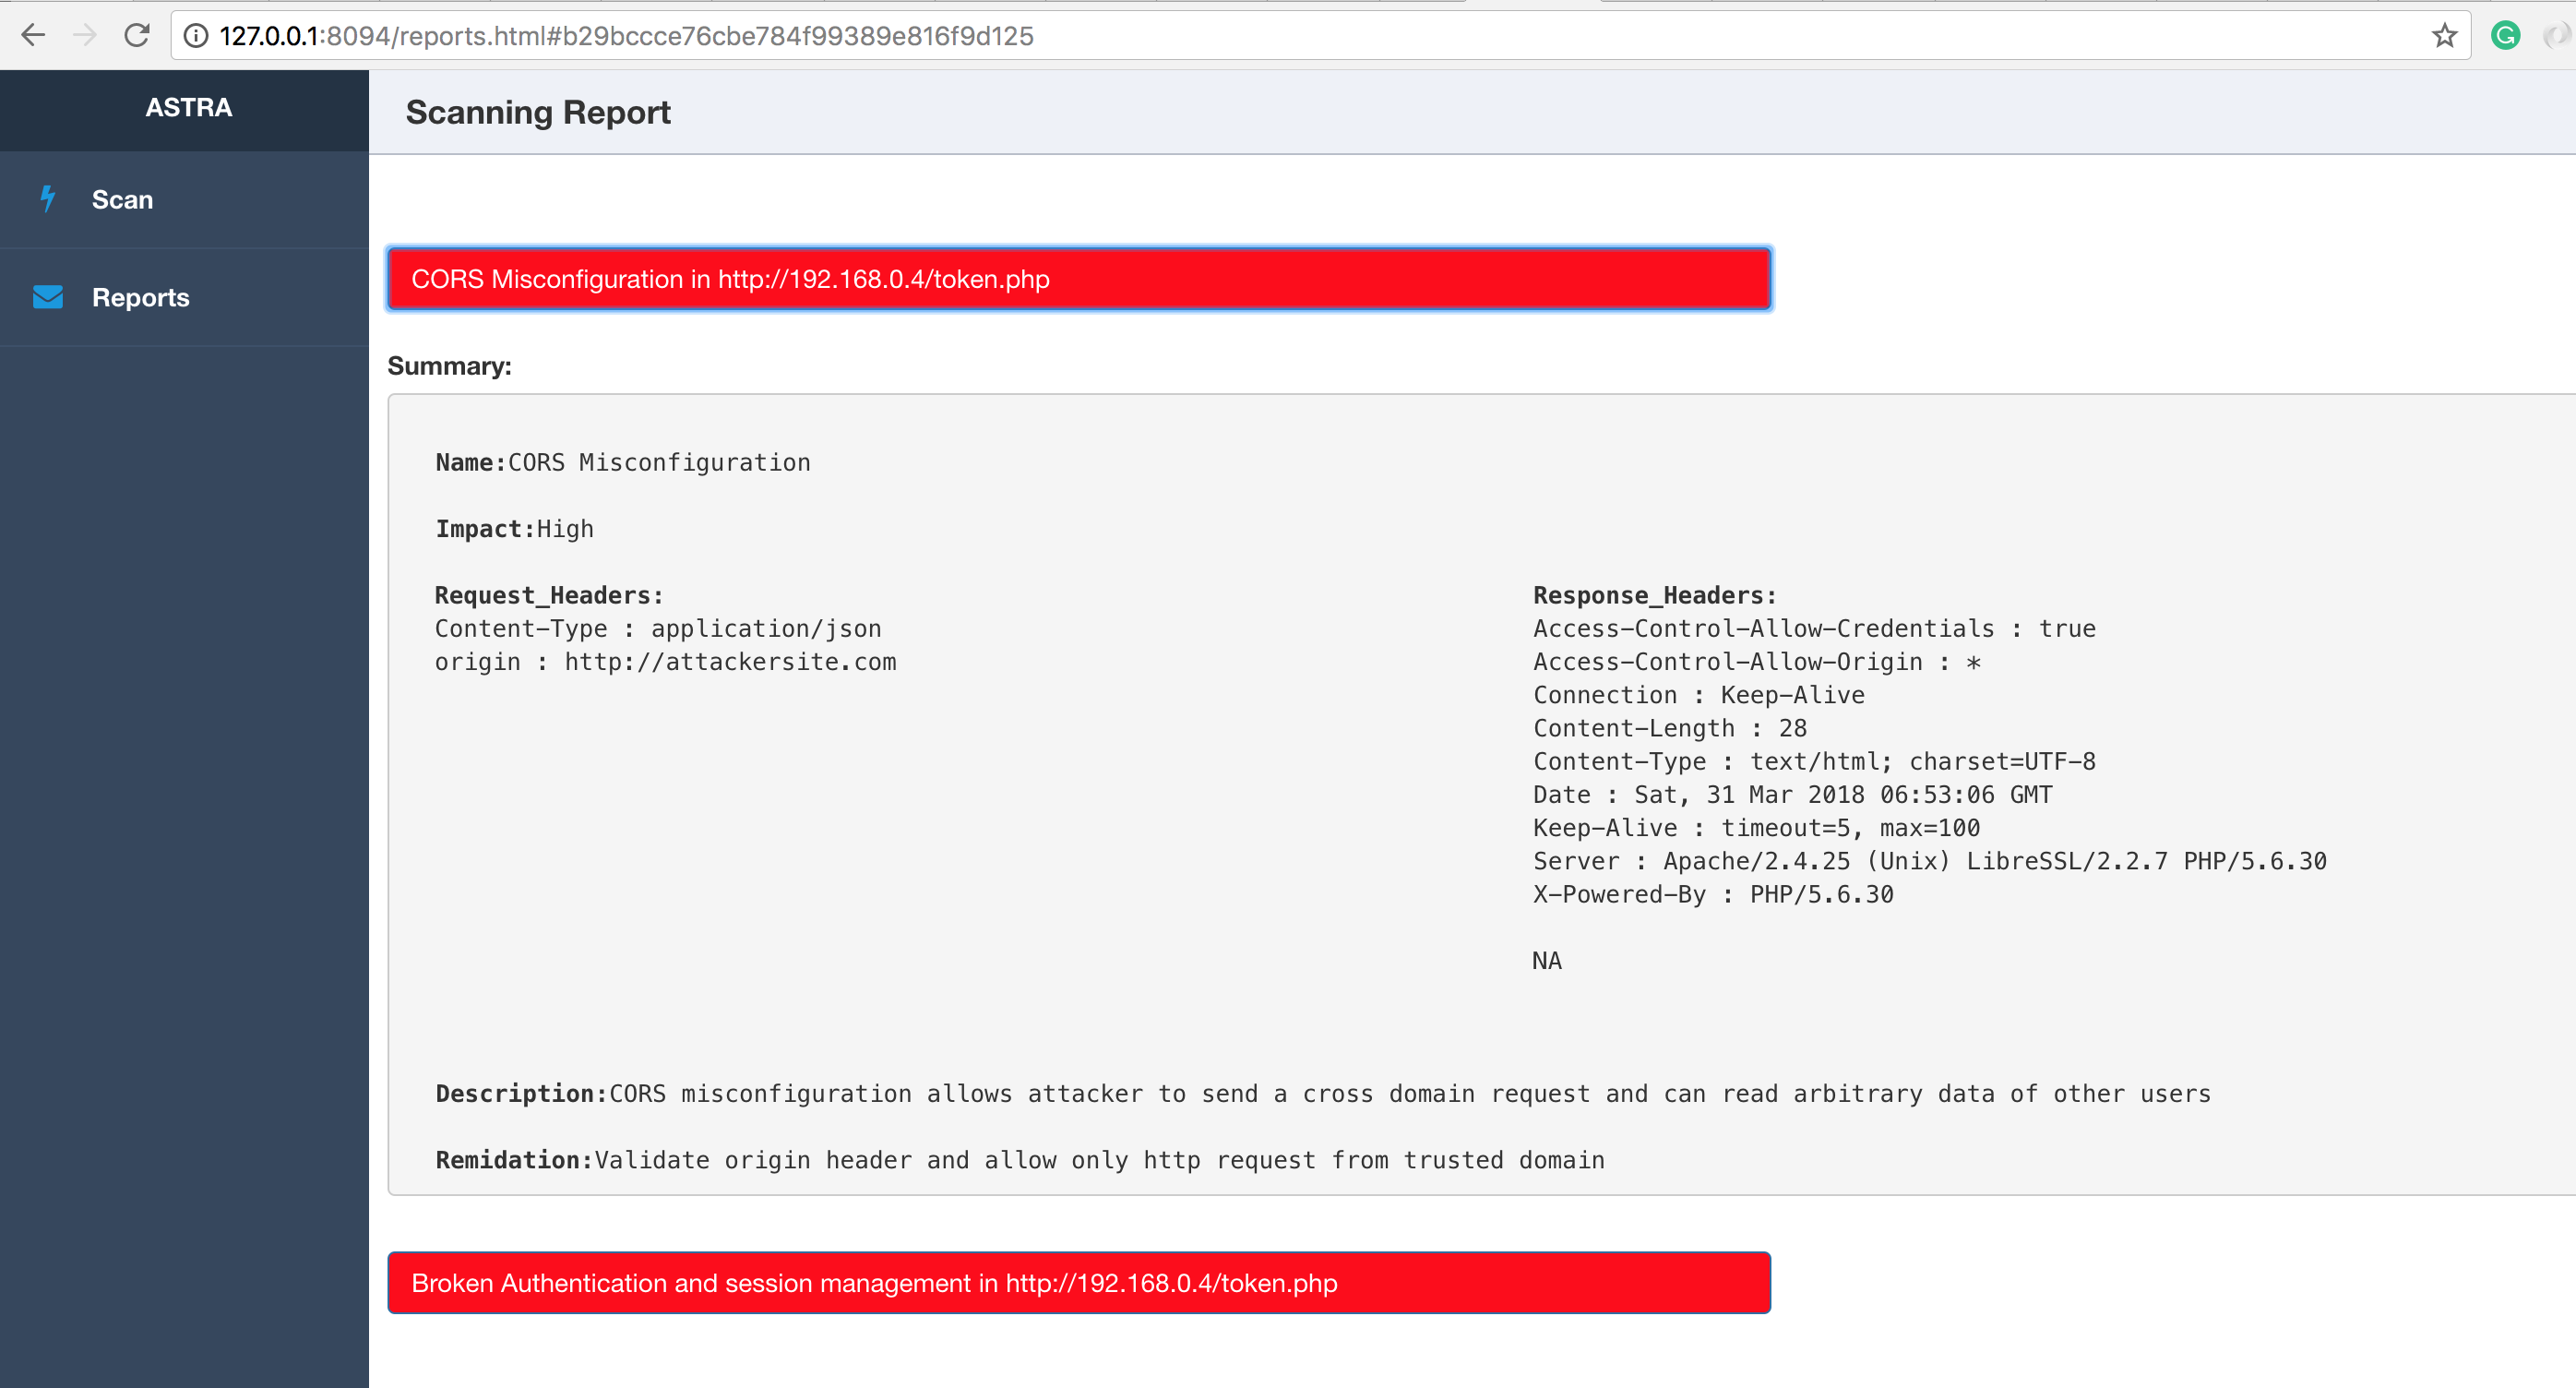 flipkart-incubator/astra
Automated Security Testing For REST API's
 alexei-led/pumba
Chaos testing, network emulation, and stress testing tool for containers