

trajan
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
cloud-securitycode-analysisconfiguration-auditing+7
195
praetorian-inc/trajanA multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
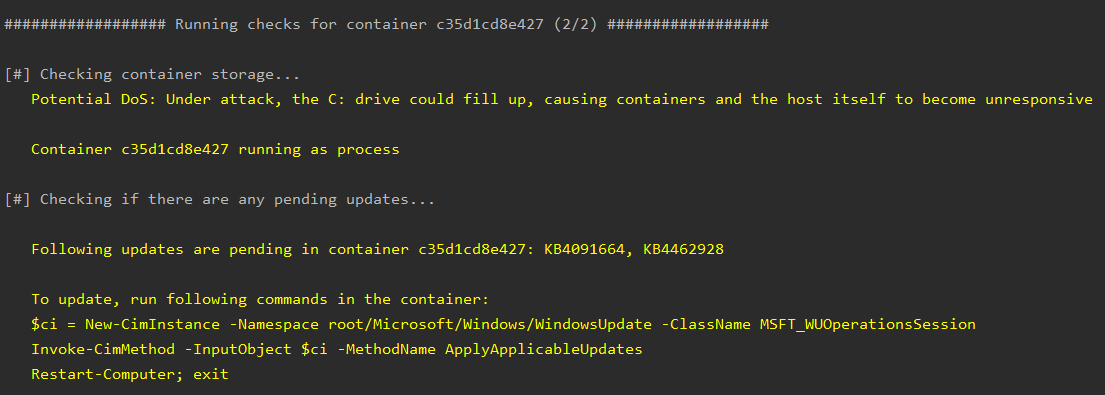 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
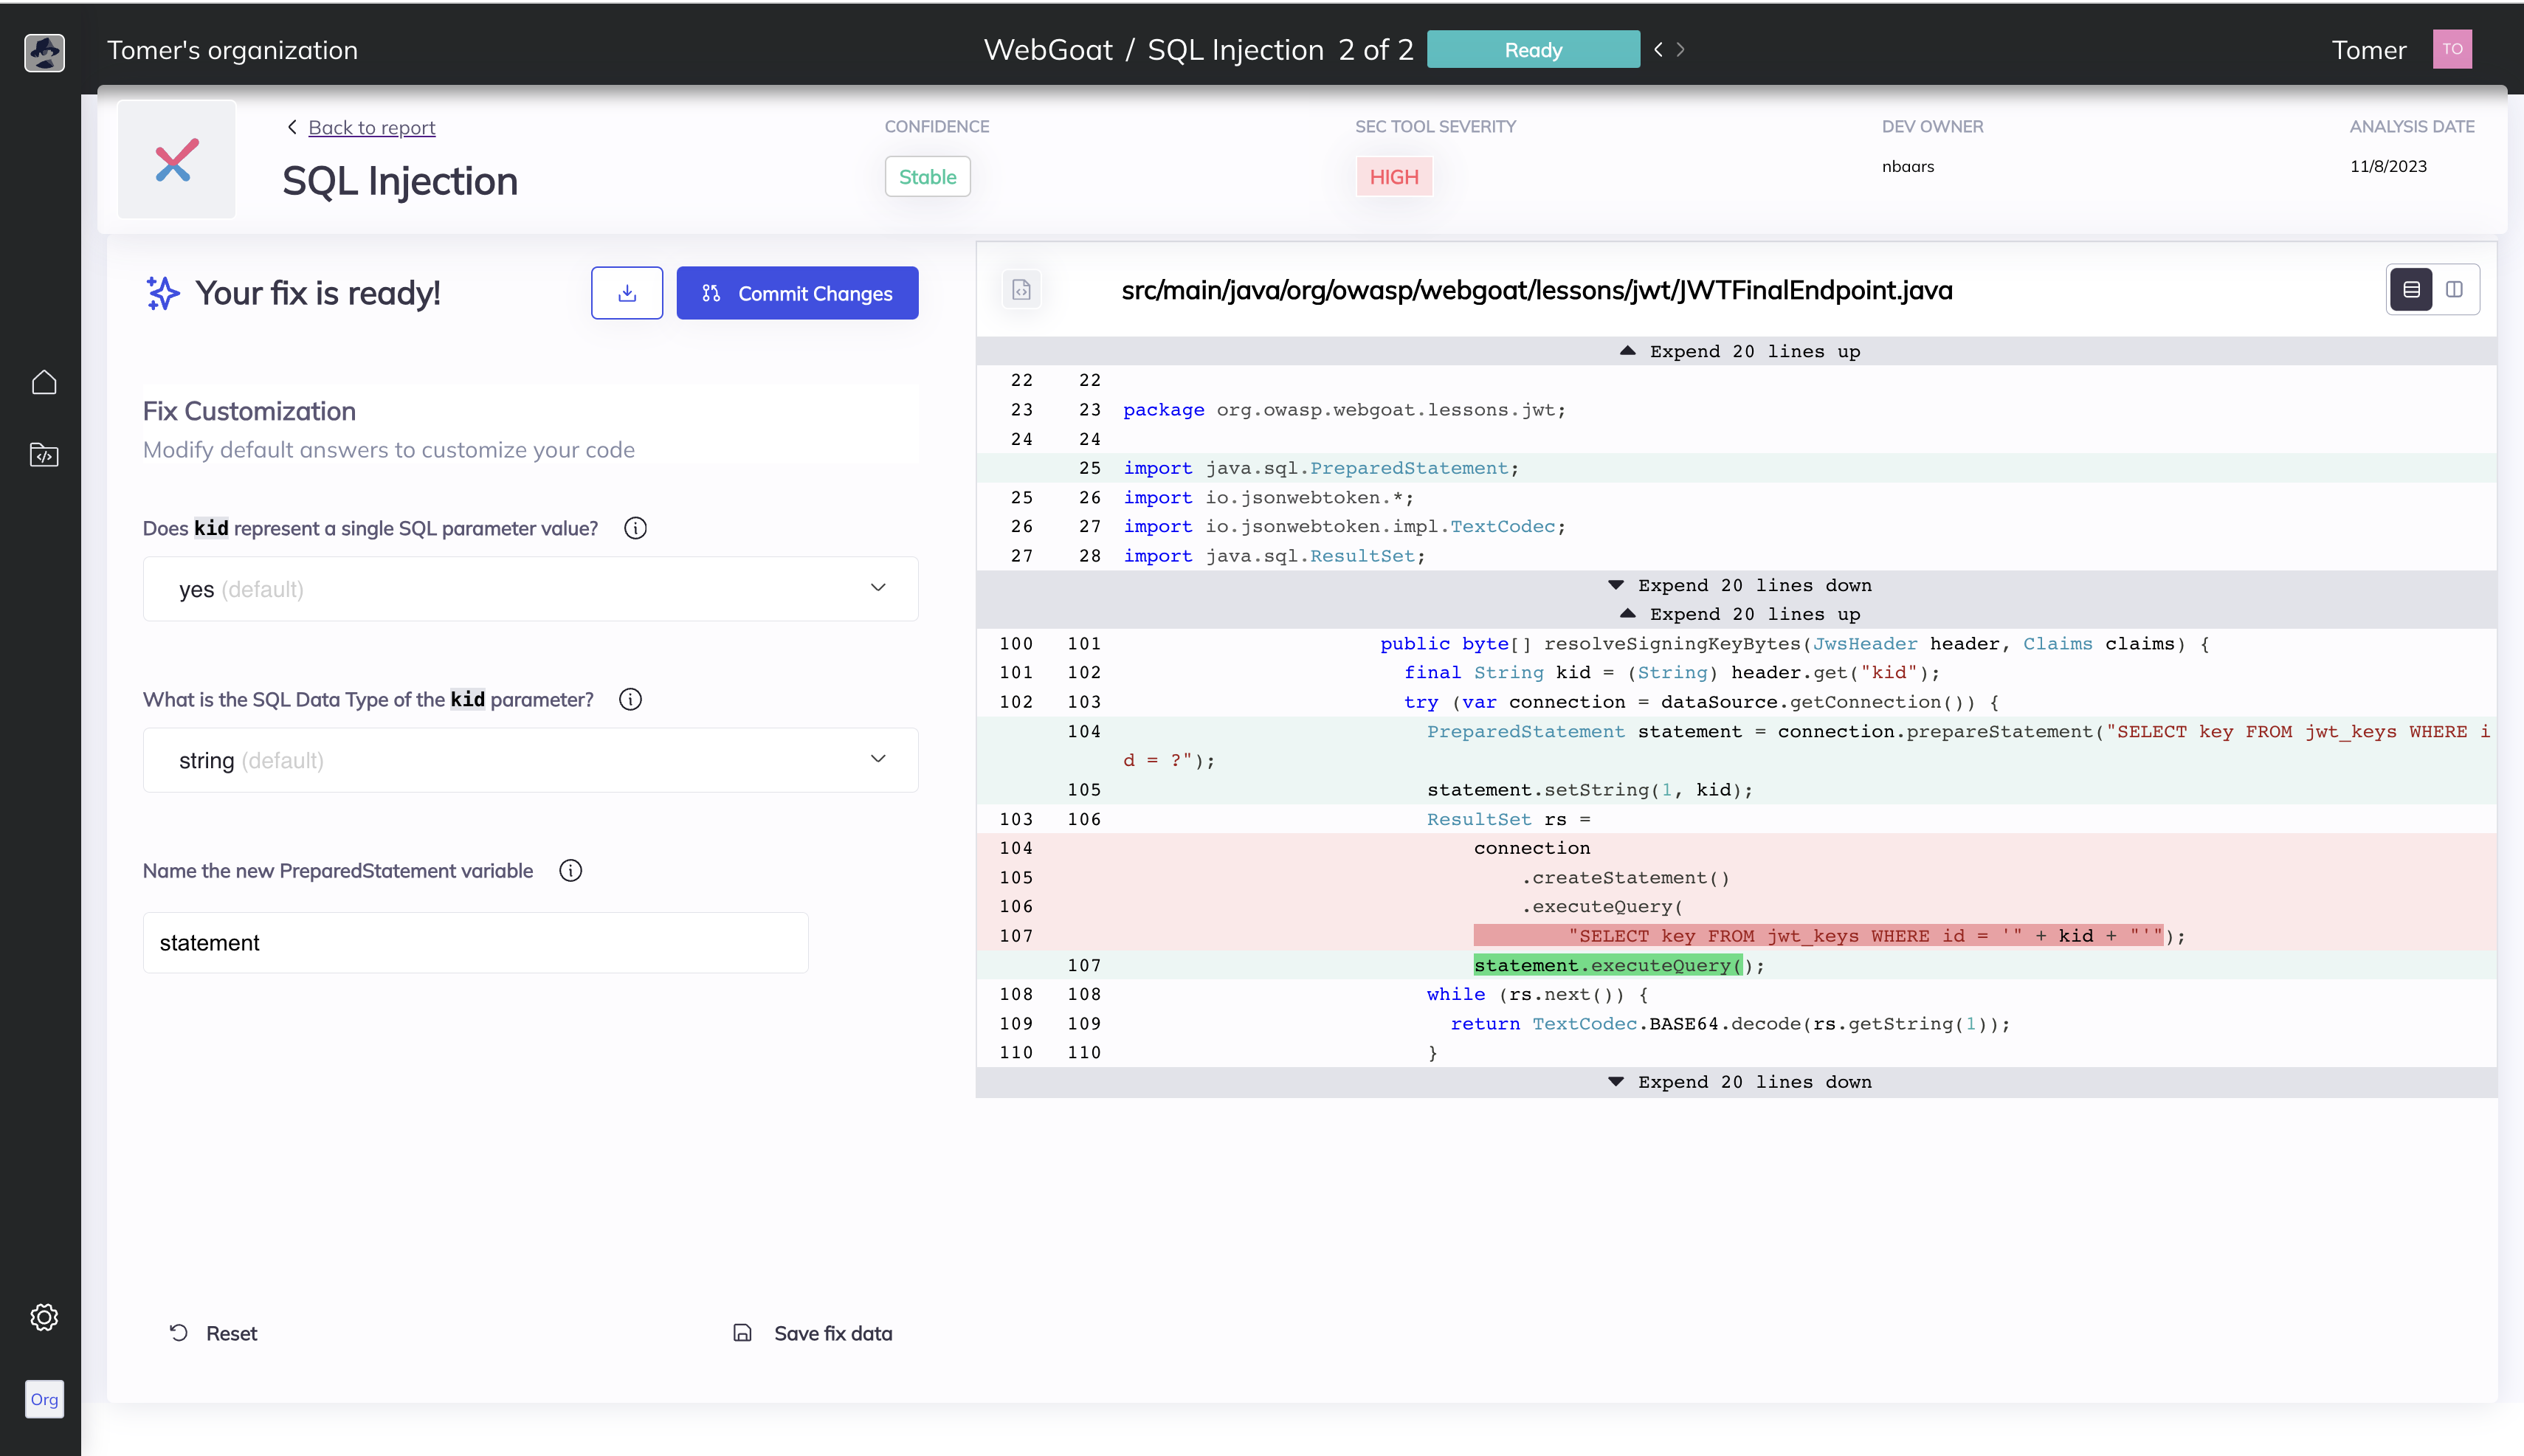 mobb-dev/bugsy
Automatic security vulnerability remediation for your code.
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 securityuniversalorg/secusphere
Centralized DevSecOps platform for vulnerability management, CI/CD security integration, automated security assessment aggregation, and fostering…
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
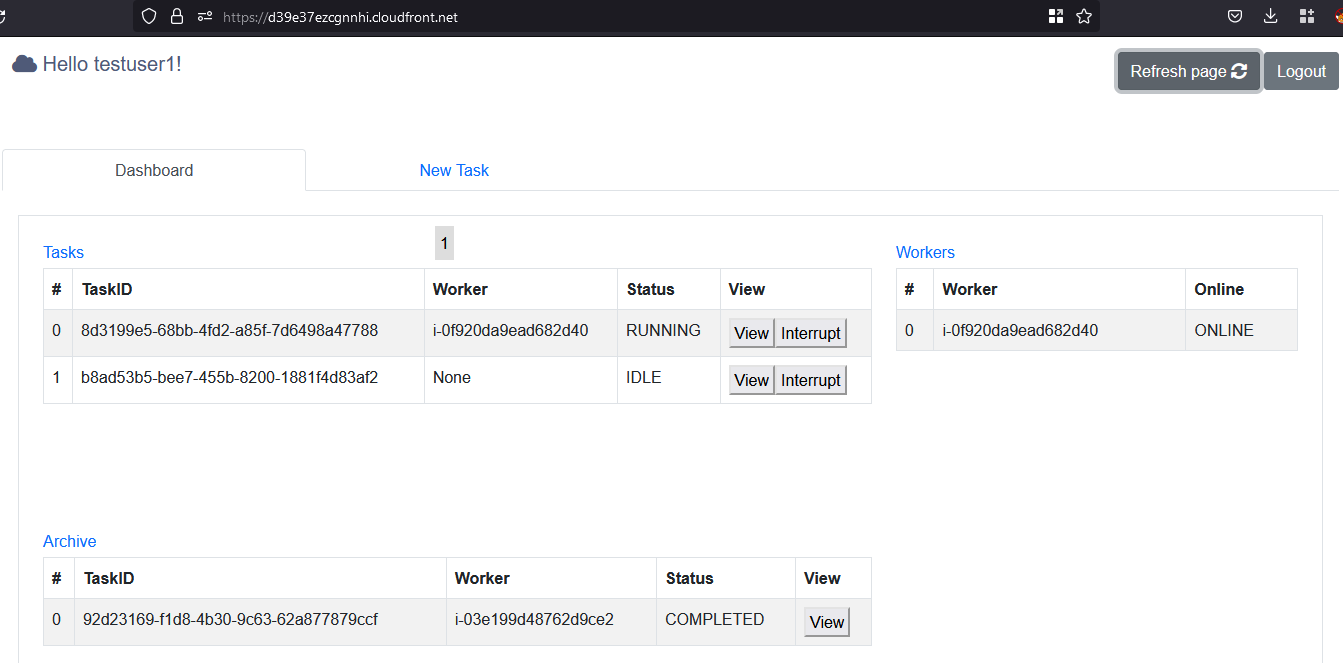 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
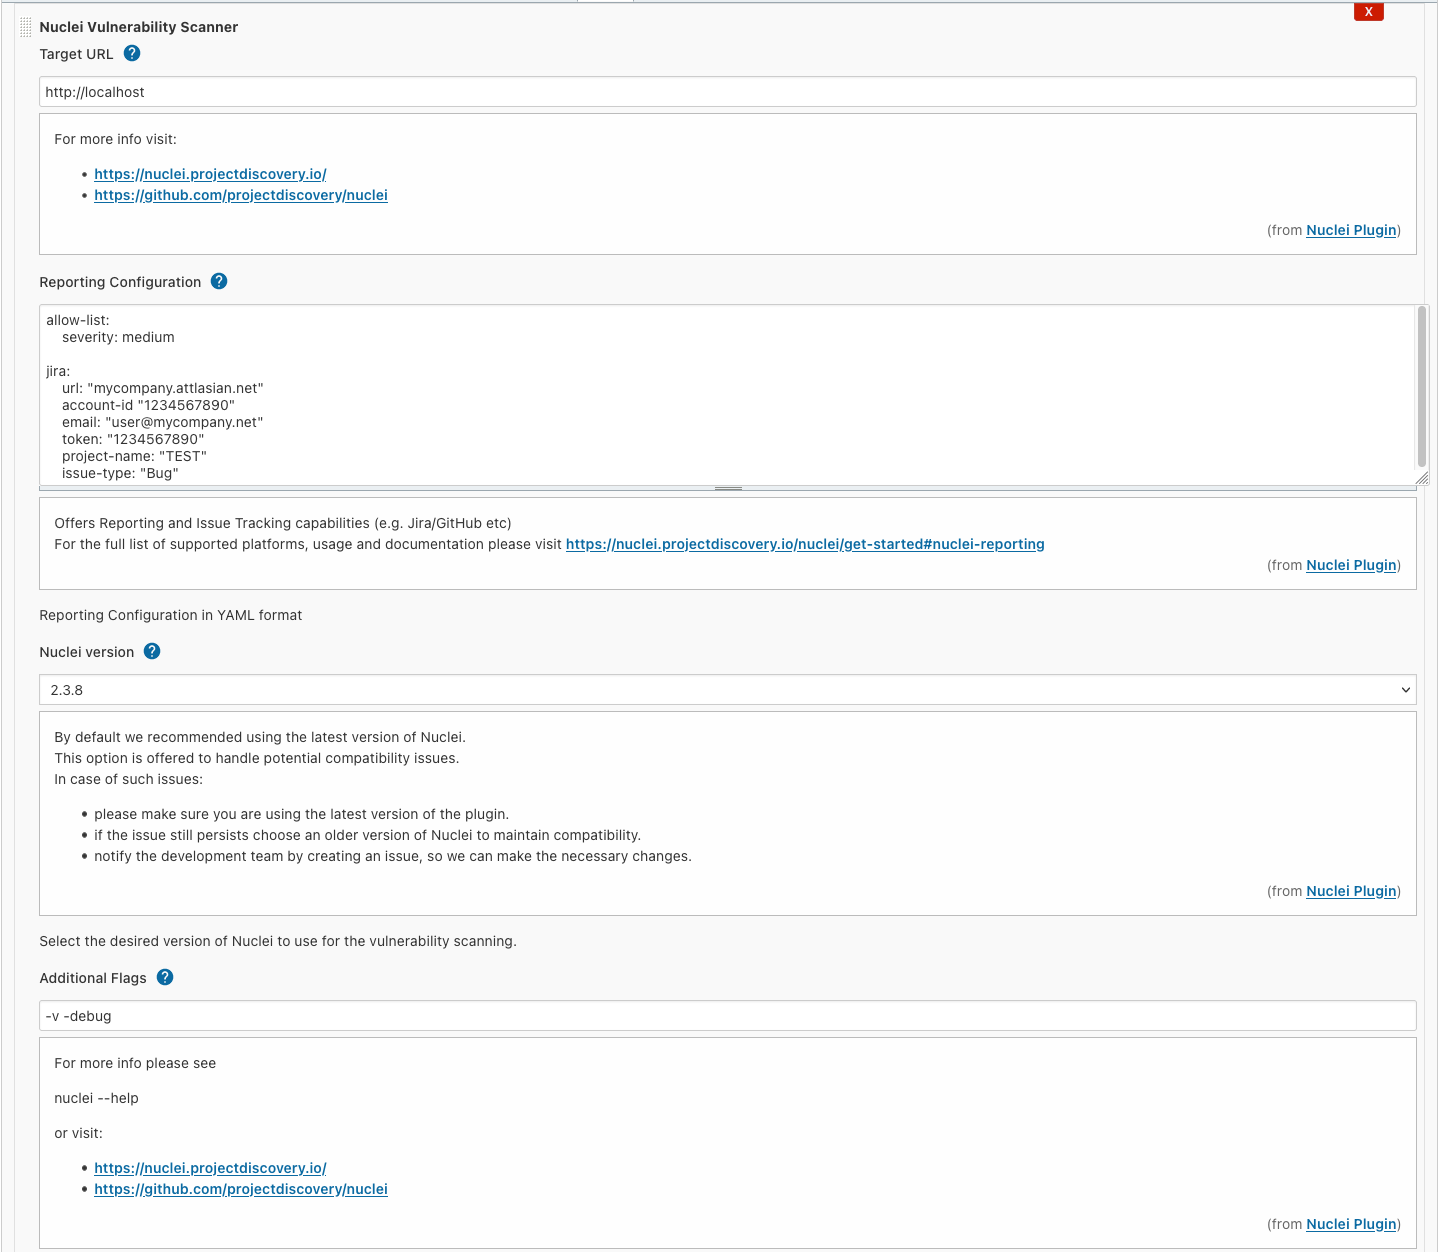 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 aaronfay/cve-2015-0235-test
Ansible playbook to check vulnerability for CVE-2015-0235
 taptap/cve-2025-59489
Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…
 abtonc/next-cve-2025-66478
Scans local projects for CVE-2025-66478 vulnerability and reports affected instances without fixing them.
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 liamromanis101/dead.letter-cve-2026-45185
Shell-based vulnerability scanner for CVE-2026-45185 (Dead.Letter) in Exim MTA. Detects use-after-free in GnuTLS builds, checks version, TLS library,…
 mikesplain/cve-2015-0235-cookbook
A chef cookbook to test the GHOST vulnerability