

owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
13
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 owasp/security-culture
OWASP Security Culture repository
 owasp/teach-appsec
OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…
 owasp/docker-security
Getting a handle on container security
 owasp/rbac
PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…
 owasp/user-security-stories
Repo to hold mapping of user-security-stories
 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
 owasp/secureml
SecureML - Securing and Watermarking AL models
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
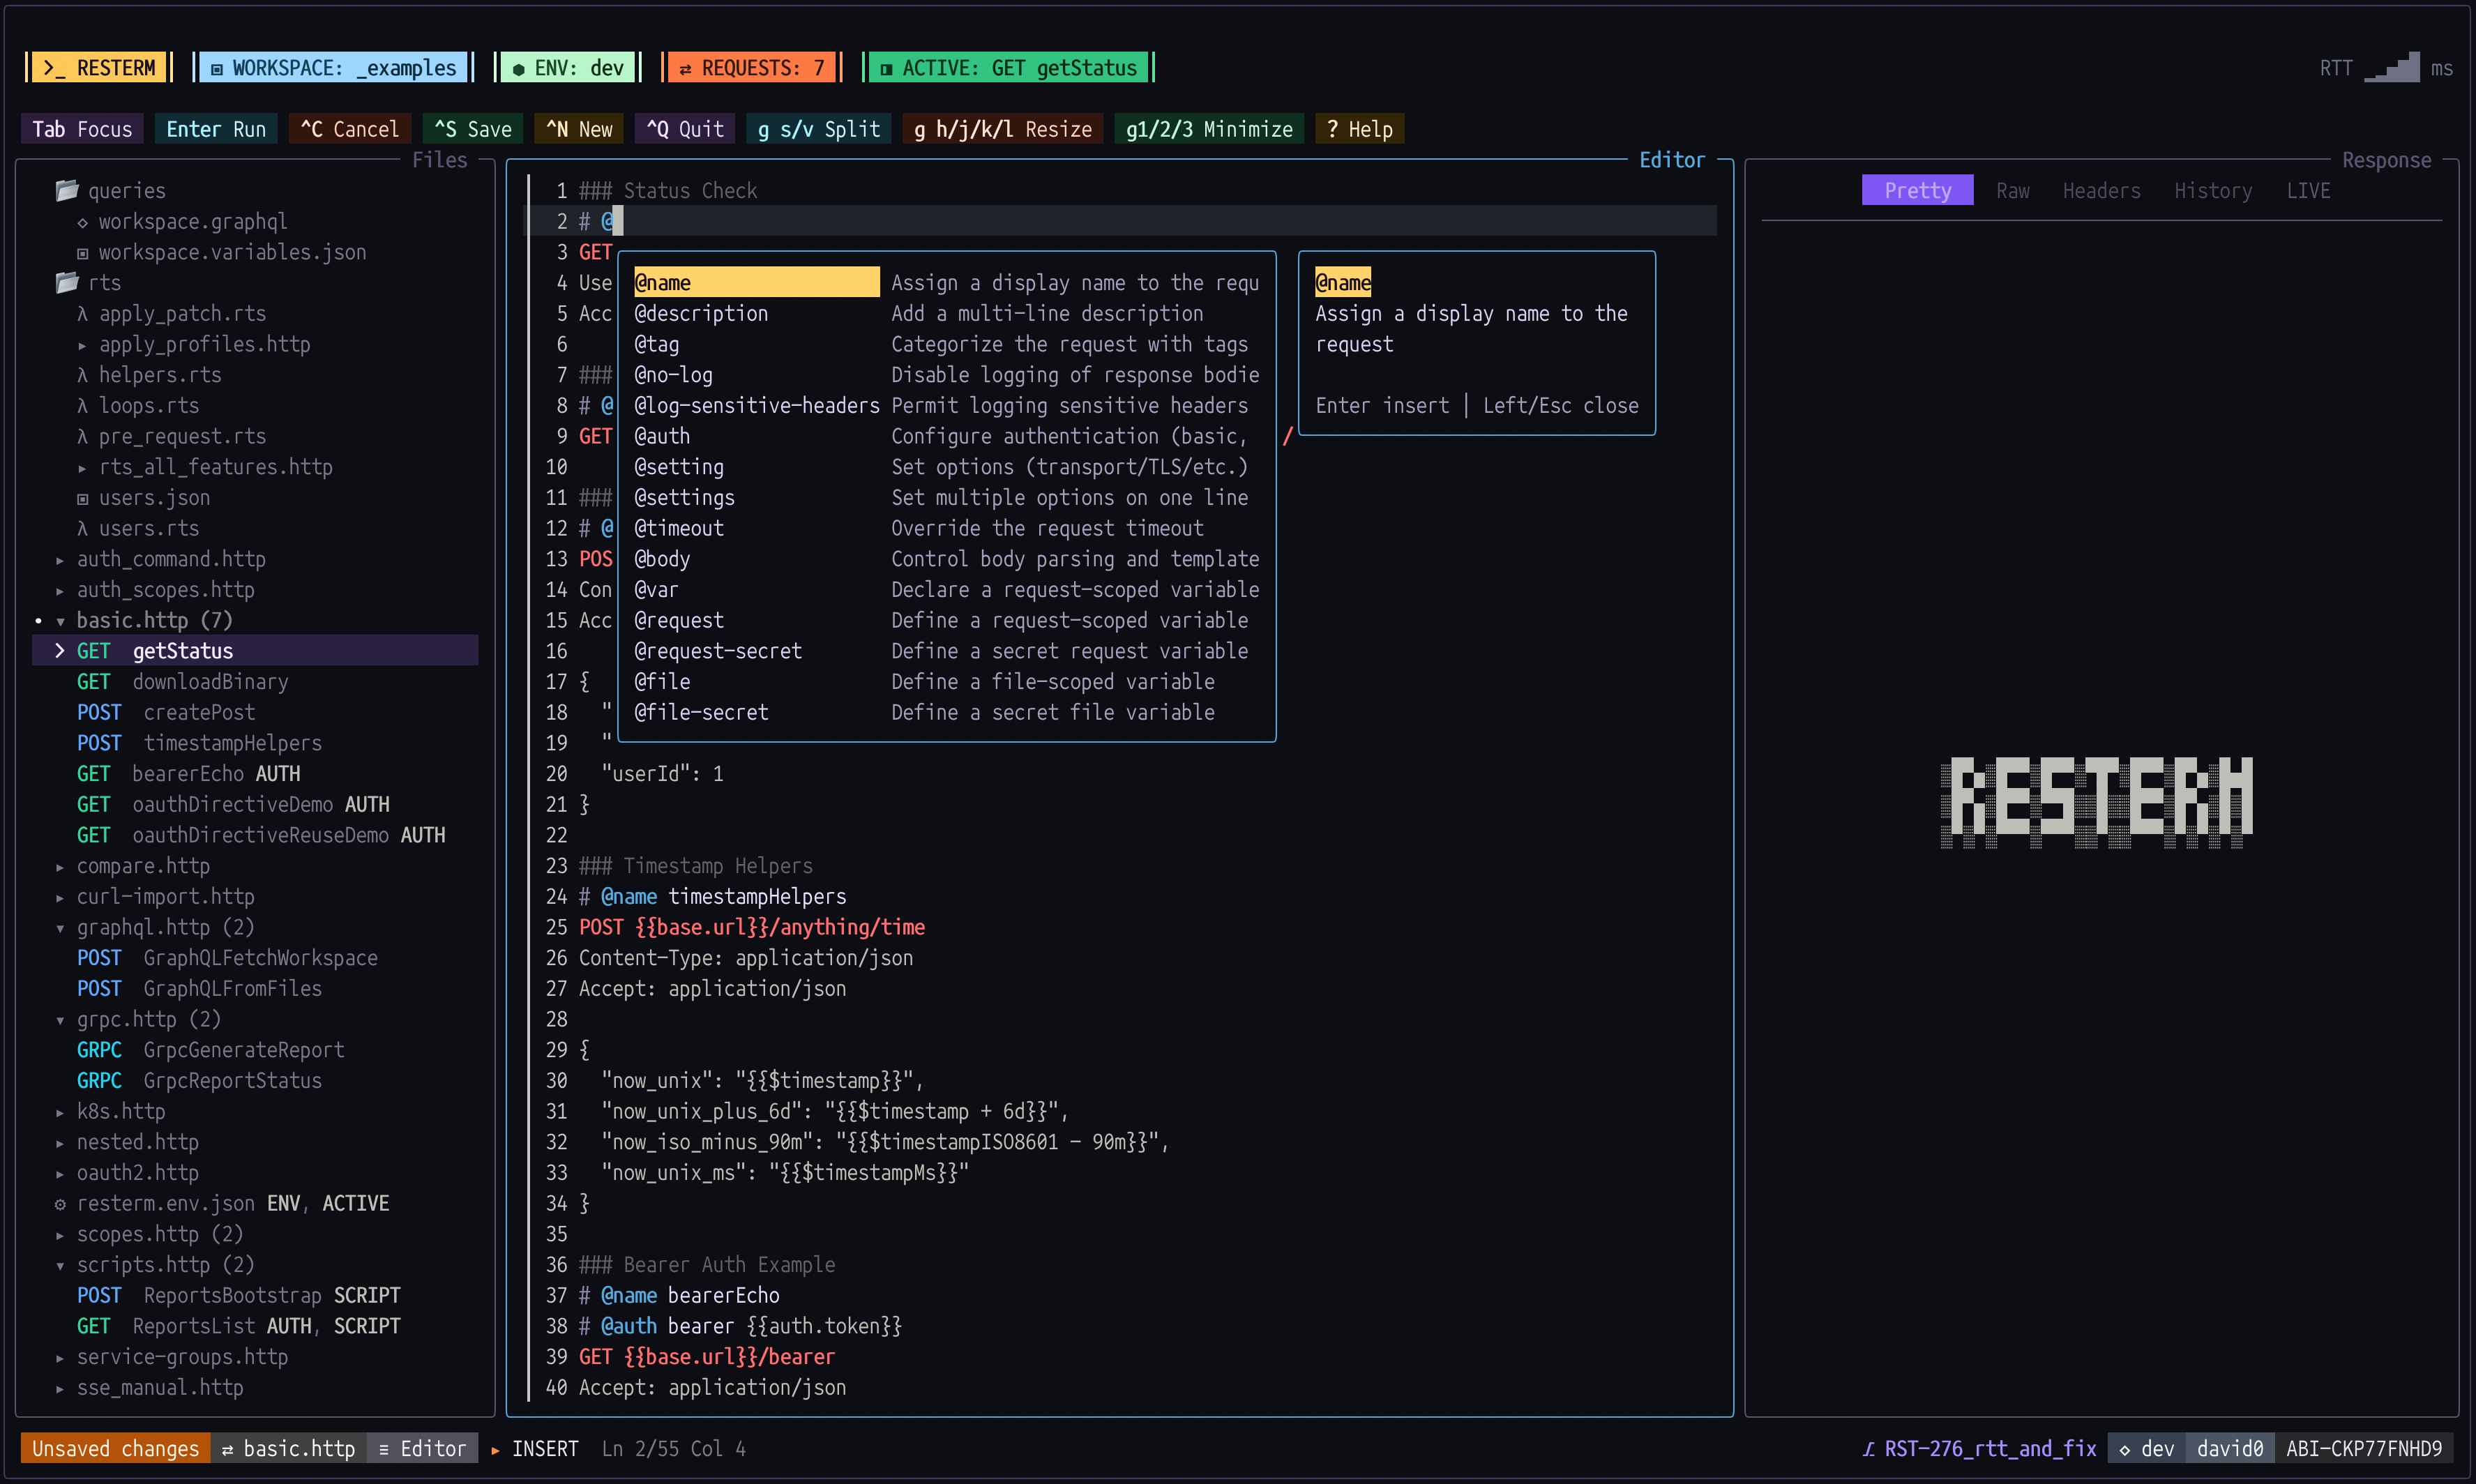 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 letsencrypt/test-certs-site
A simple server to host the valid, revoked, and expired certificates required by Section 2.2 of the CA/Browser Forum Baseline Requirements.
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.