
vuln-ejs-critical
 test-avm-714877d2df585126/vuln-ejs-critical
npm repo with ejs CVE-2022-29078 (CVSS 9.8, EPSS 32%) for Dependabot automerge testing
devsecopseducationsupply-chain-security+2
test-avm-714877d2df585126/vuln-ejs-criticalnpm repo with ejs CVE-2022-29078 (CVSS 9.8, EPSS 32%) for Dependabot automerge testing
 andypitcher/log4j_checker
Log4J checker for Apache CVE-2021-44228
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 sushant-me/agentic-workflow-injection
Reproducible vulnerable and fixed GitHub Actions fixtures for agentic workflow injection (CVE-2026-44246), with measured detector coverage and…
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 praetorian-inc/gokart
A static analysis tool for securing Go code
 pvharmo2/gha-lab-ba8e0c4217
Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
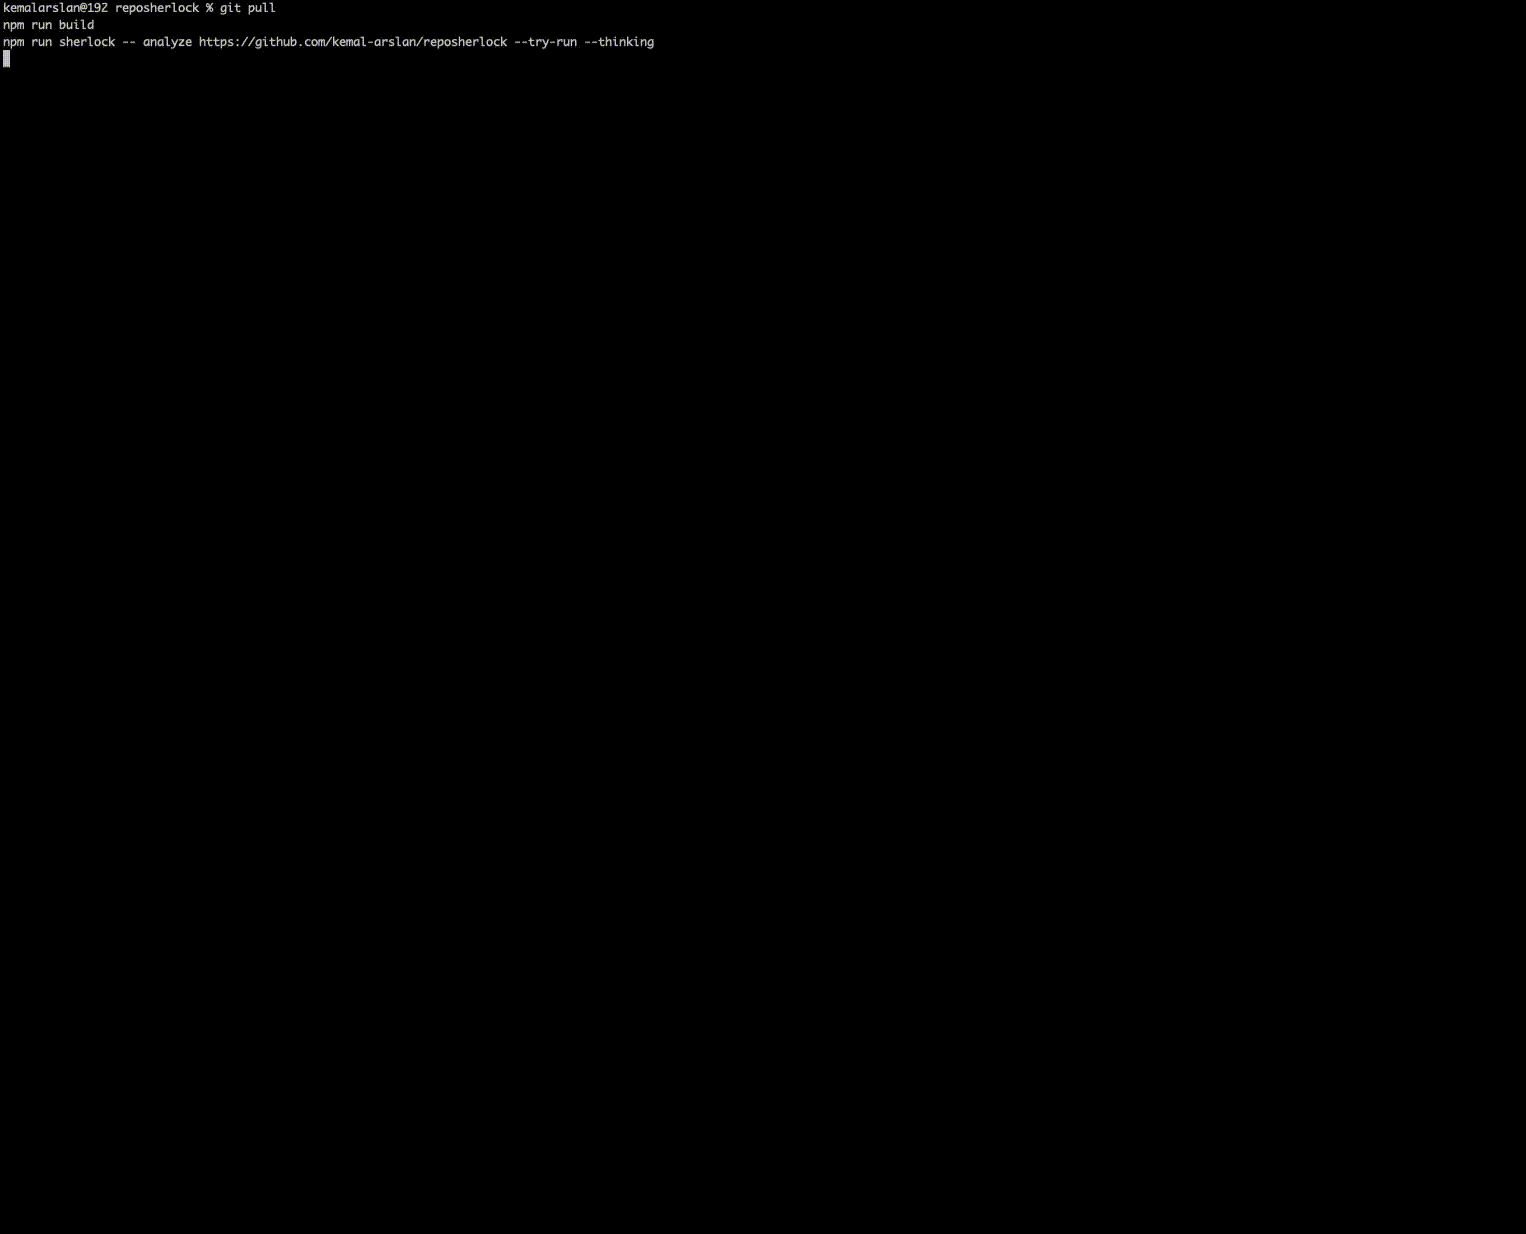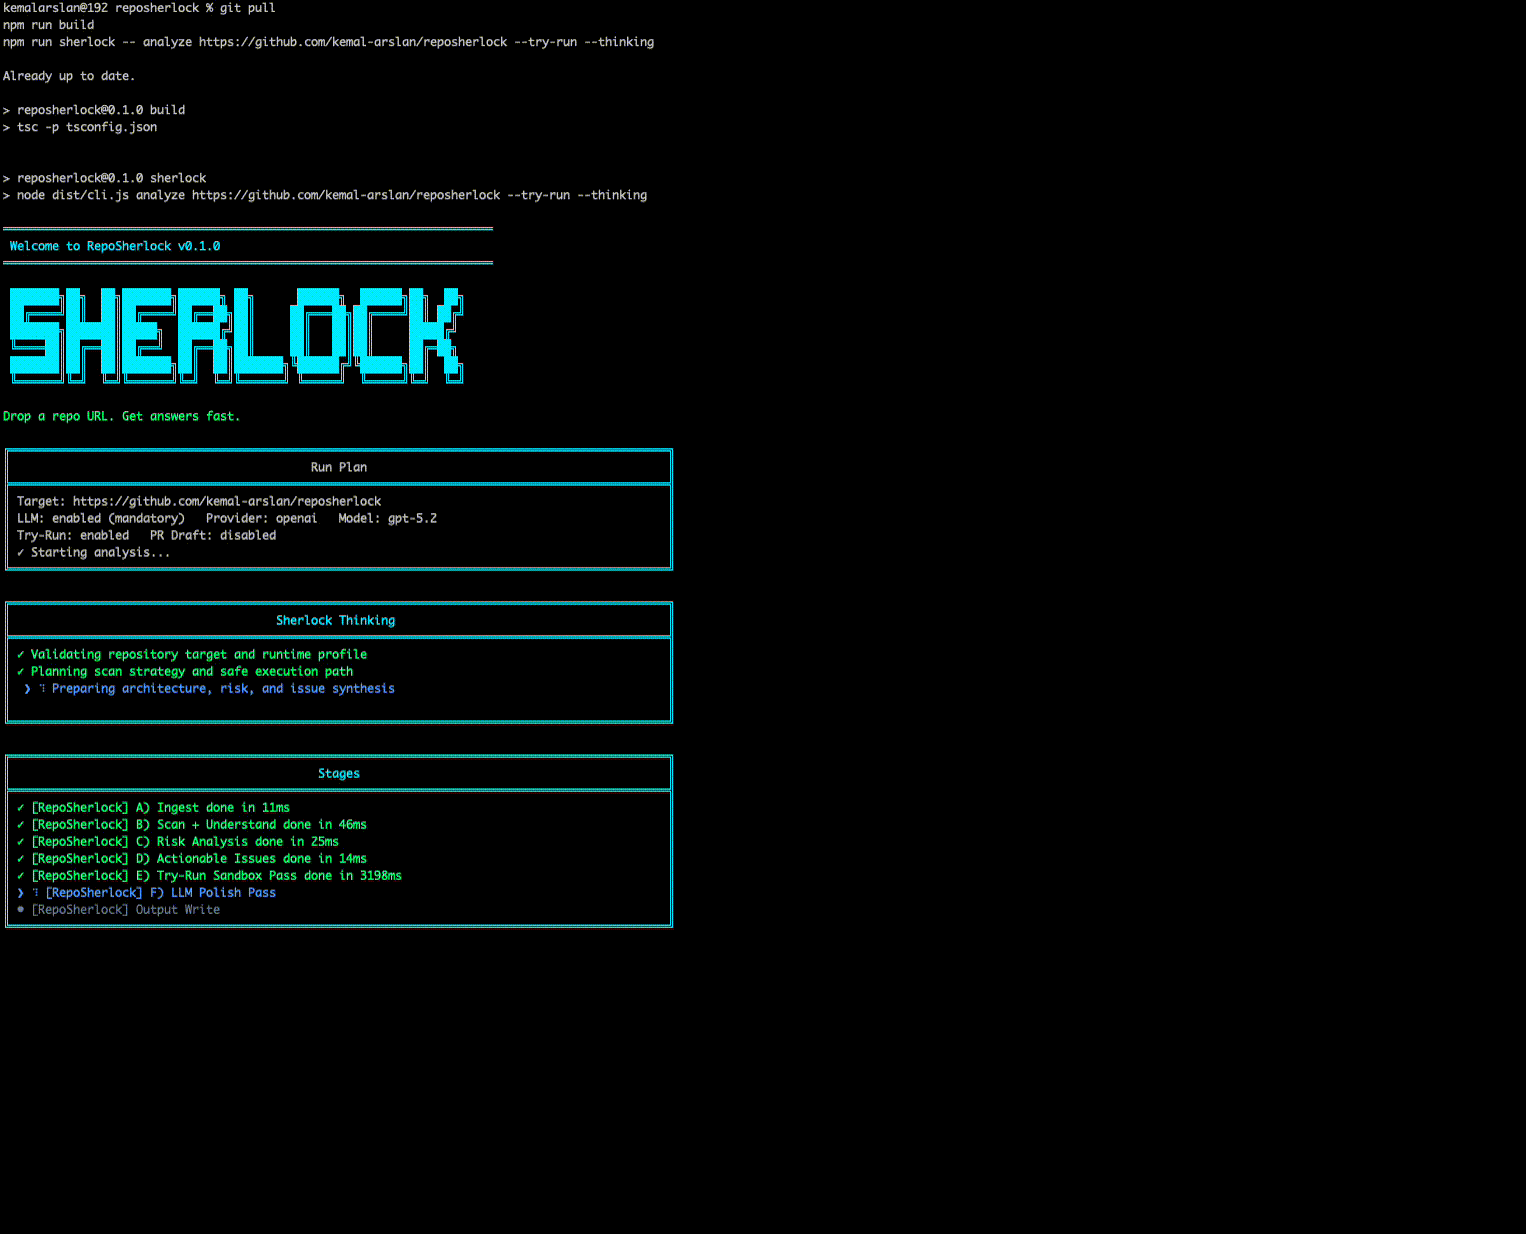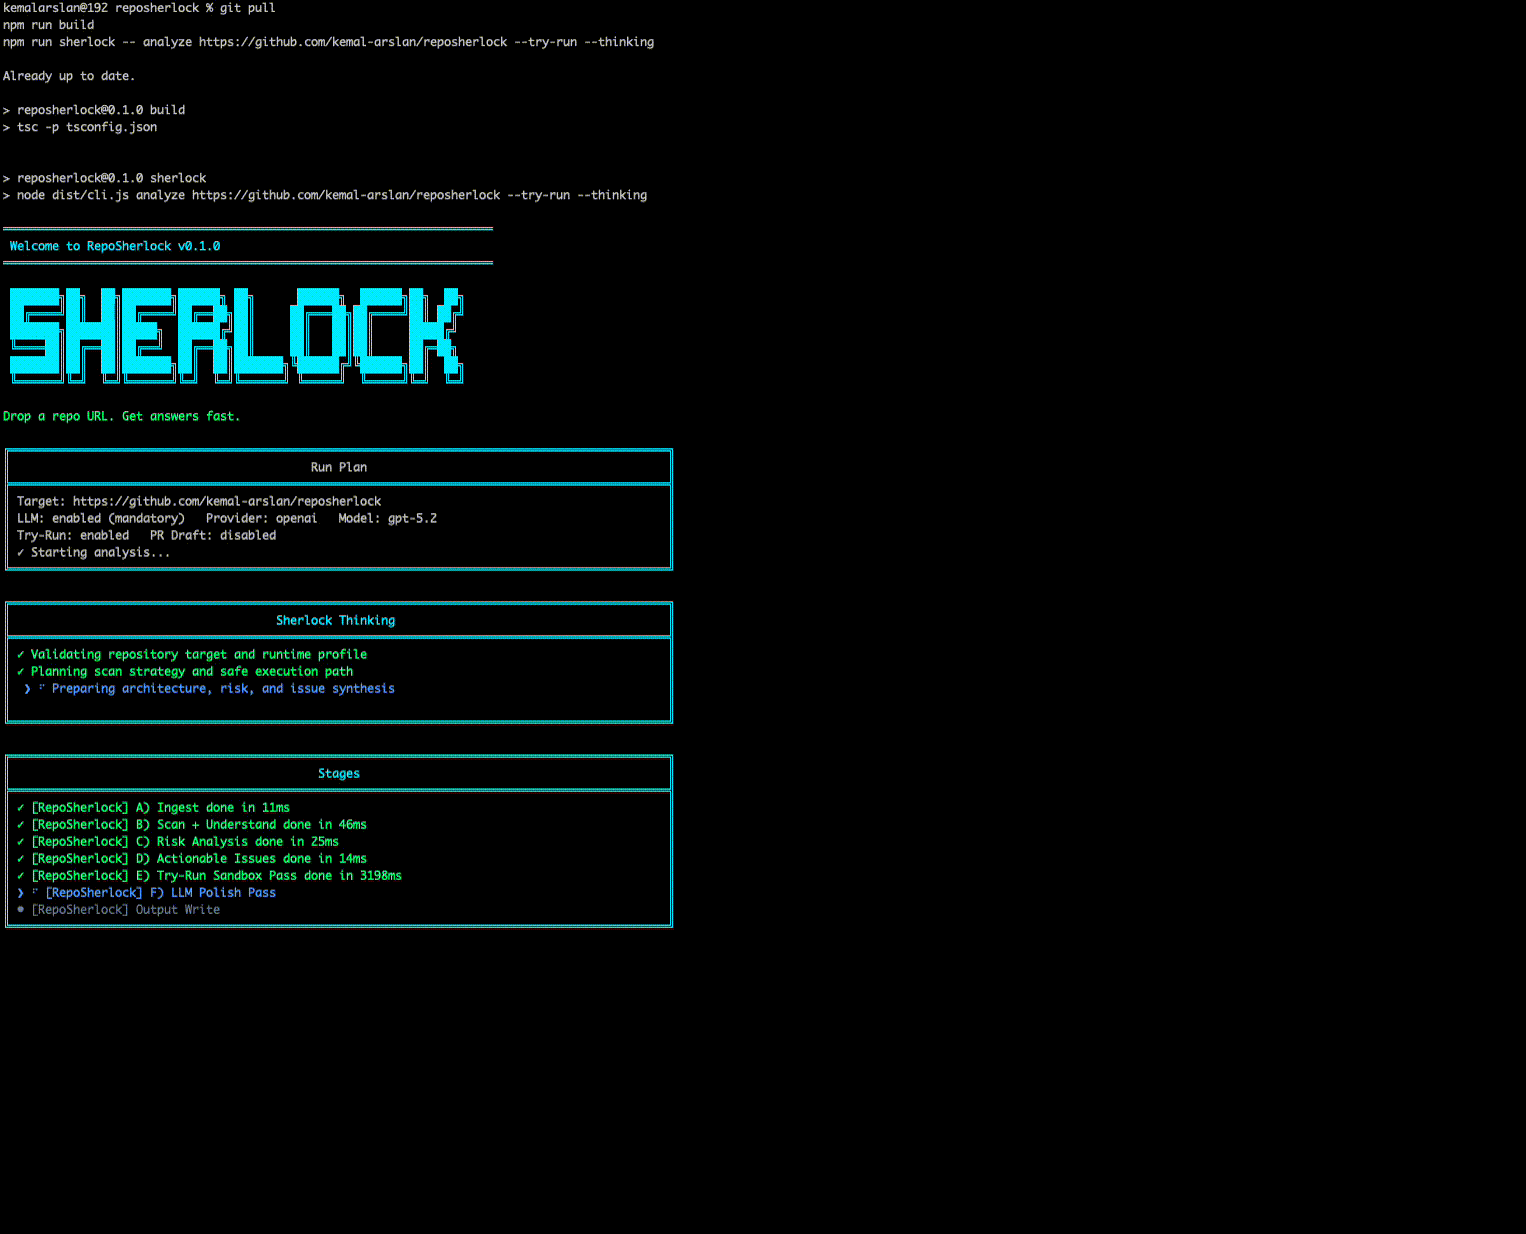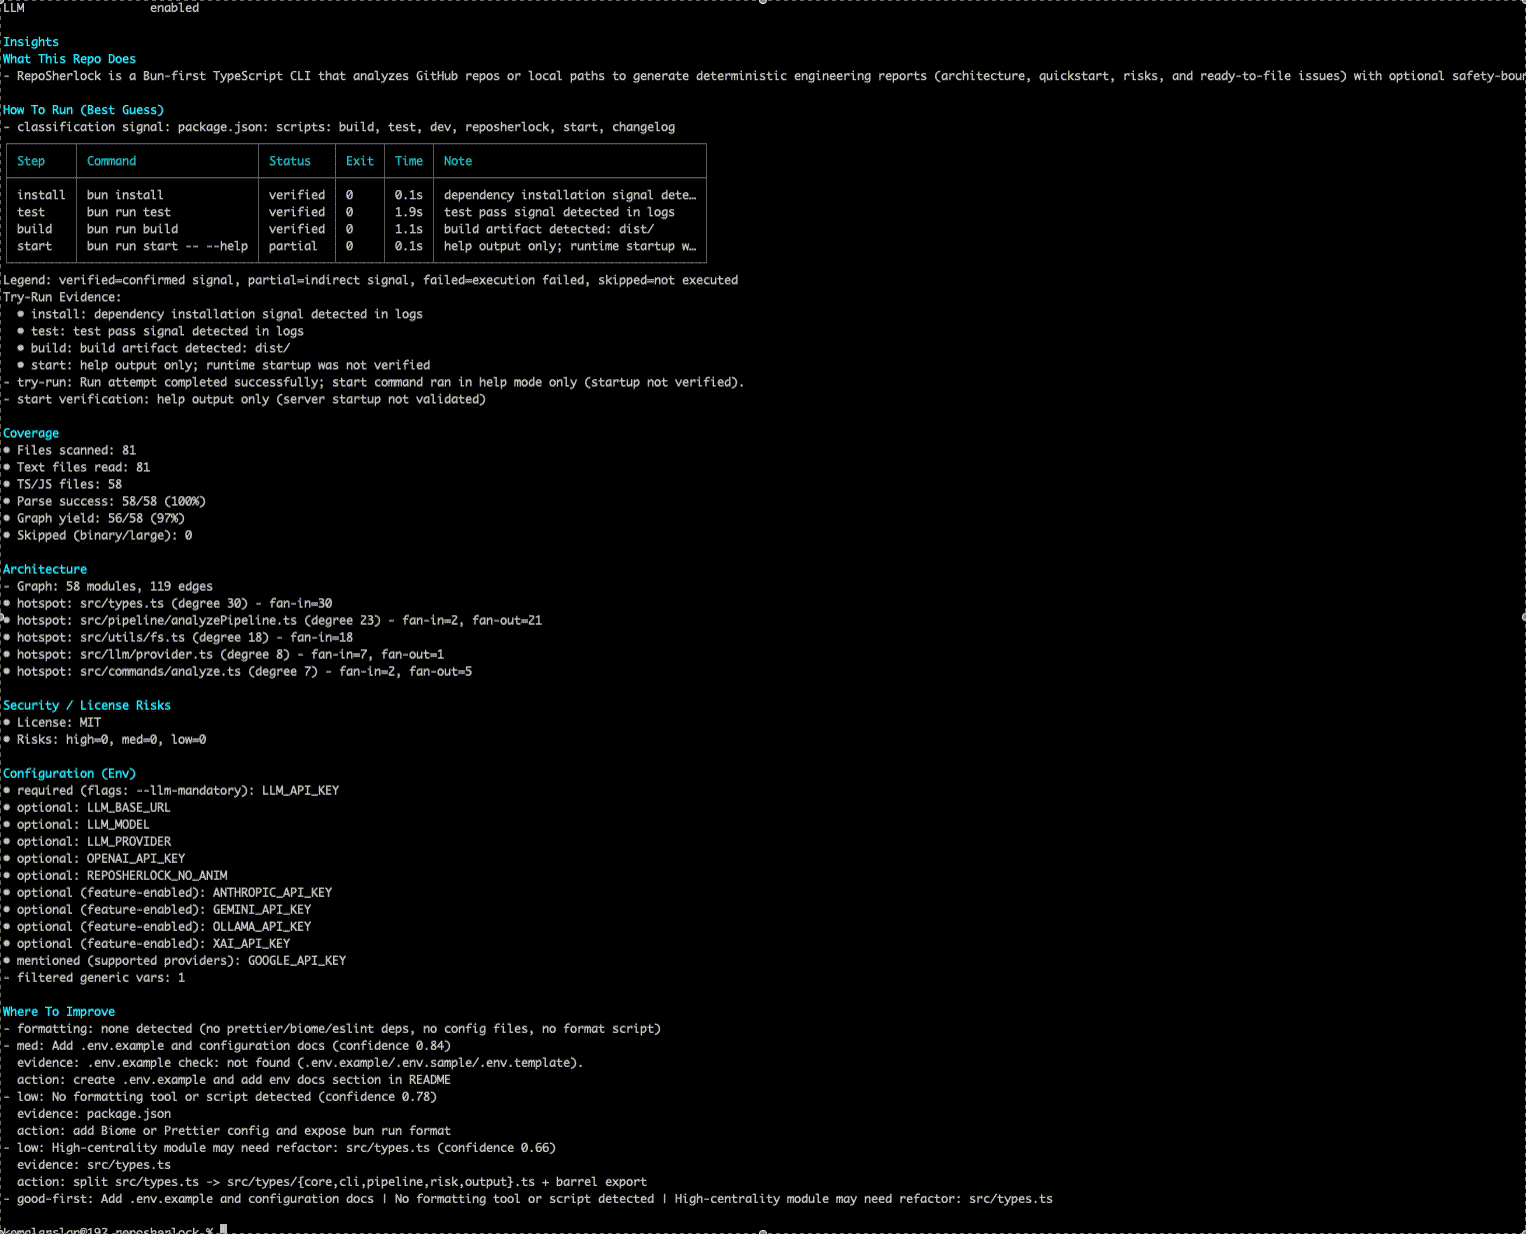 kemal-arslan/reposherlock
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 moisestapia/http-react2shell
Detection of the React Server Actions Exploit vector – CVE-2025-55182 / CVE-2025-66478
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…